

hacktricks
 hacktricks-wiki/hacktricks
Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.
ctfcurated-resourceseducation+11
12.6k
hacktricks-wiki/hacktricksWelcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.
 flangvik/sharpcollection
Nightly builds of common C# offensive tools, fresh from their respective master branches built and released in a CDI fashion using Azure DevOps…
 ragnt/angryoxide
Offensive 802.11 auditing tool that automates WPA/WPA2 handshake and PMKID capture using deauthentication, rogue-client, and channel-switch attacks,…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 gwen001/pentest-tools
A collection of custom security tools for quick needs.
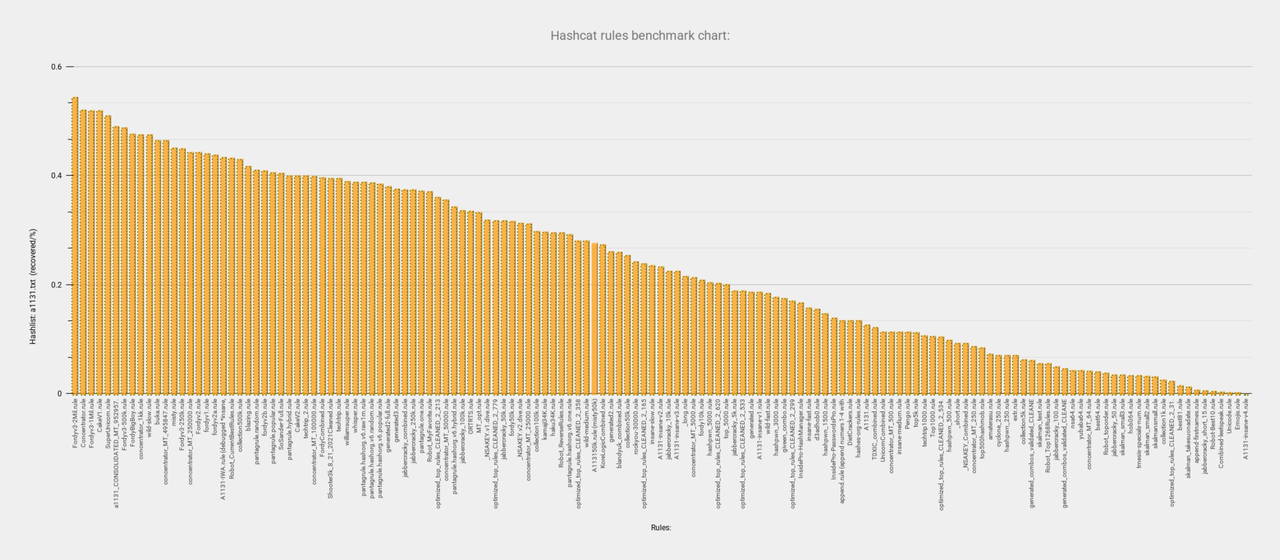 ibnaleem/rules
Curated collection of Hashcat password-cracking rules with benchmark data, designed to help red teams and penetration testers crack complex passwords…
 rix4uni/wordlist
Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
 praetorian-inc/brutus
Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
 cldrn/nmap-nse-scripts
My collection of nmap NSE scripts
 ihebski/defaultcreds-cheat-sheet
One place for all the default credentials to assist the Blue/Red teamers identifying devices with default password 🛡️

 wattocyber/oscp-notes-2026
OSCP notes vault + exam cockpit dashboard: merged technique notes, variable-filled command decks, machines, creds, and runbook for exam day. MIT.
 nocoderrandom/sunsetscan
Local-network security auditing with EOL, CVE, device identity, and HTML reports
 the-viper-one/psmapexec
Dominate Active Directory with PowerShell.
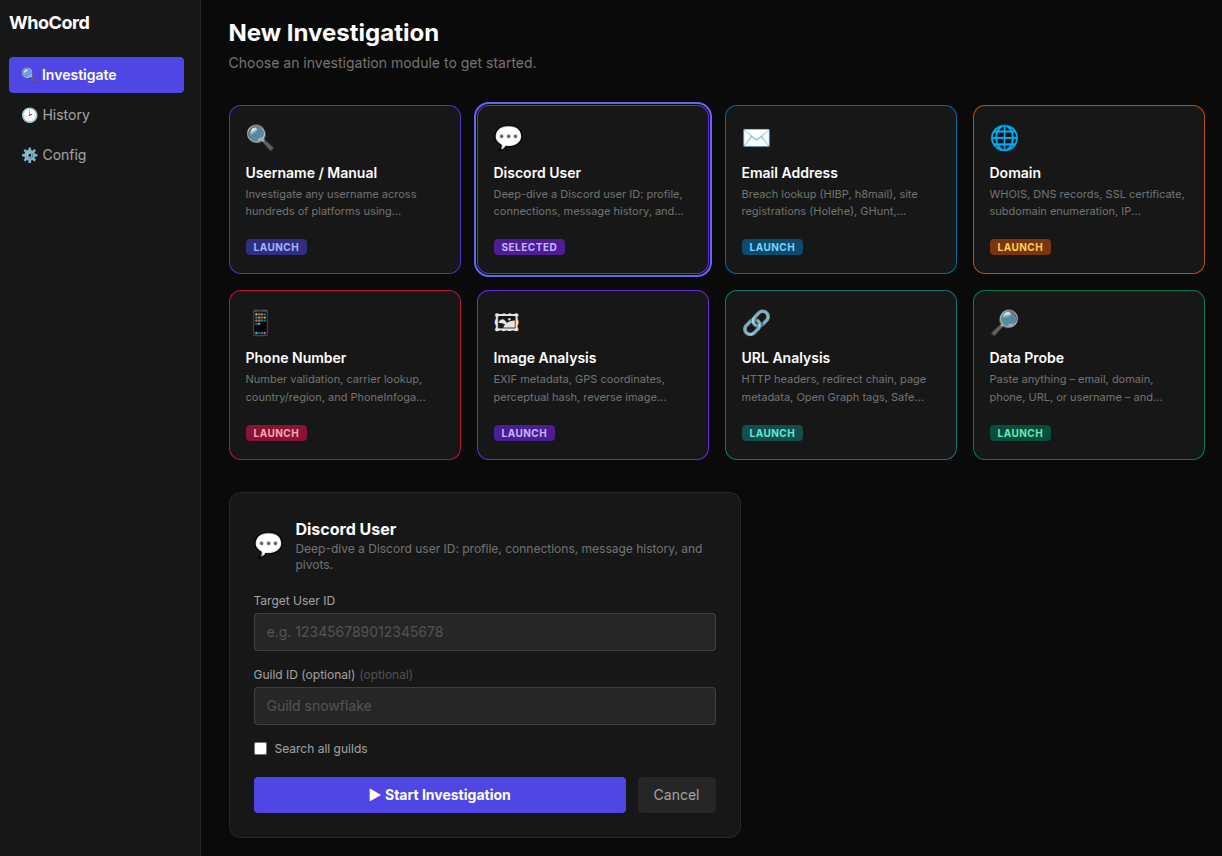 siv-nick/whocord
Scans Discord links across mutual guilds to extract profiles, cross‑references 700+ sites, searches usernames with 30+ tools, and generates an…
 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…