
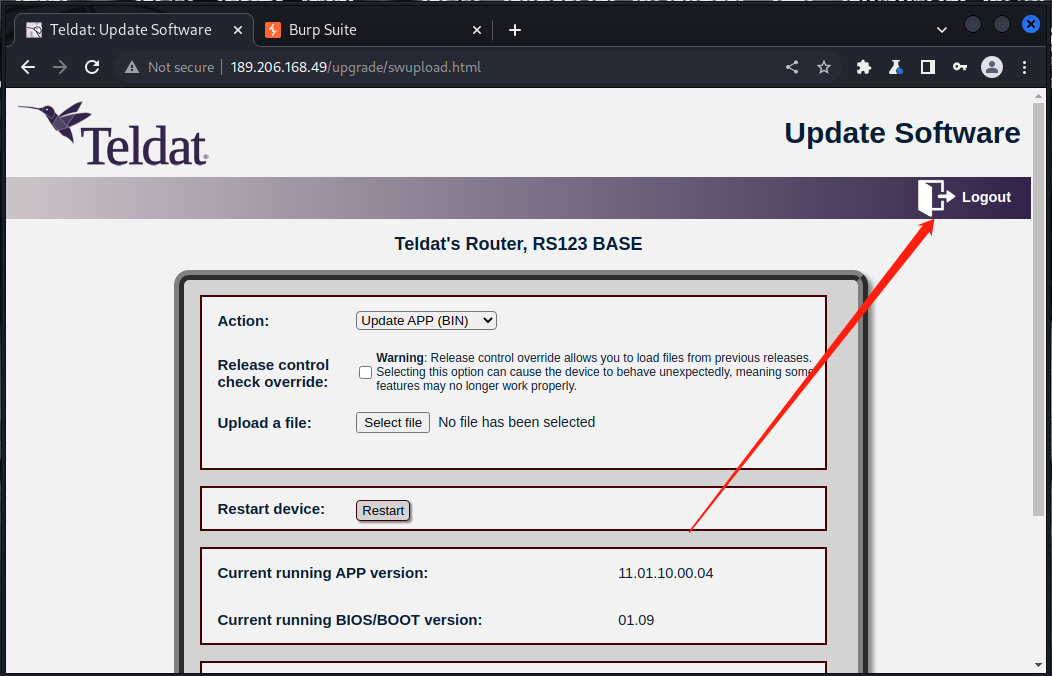
Teldat-Router-CVE-2022-POC
 uyhacked/teldat-router-cve-2022-poc
POC for CVE-2022-39996 (Reflected XSS) and CVE-2022-39997 (Weak Password) in Teldat RS123/RS123w Router
educationexploitationpassword-attacks+3
uyhacked/teldat-router-cve-2022-pocPOC for CVE-2022-39996 (Reflected XSS) and CVE-2022-39997 (Weak Password) in Teldat RS123/RS123w Router
 kirubel-cve/cve-2025-65427
Proof-of-concept exploit for CVE-2025-65427: missing rate limiting on Dbit N300 T1 Pro router login API enabling brute-force attacks and…
 xernary/cve-2025-63820
Proof-of-concept of vulnerability found in Totolink A720R router
 absholi7ly/poc-cve-2024-57040
CVE-2024-57040 is a security vulnerability found in certain TP-Link TL-WR845N router models. Specifically, it involves a "hardcoded" password for the…
 dylvie/cve-2020-35575-tp-link-tl-wr841nd-password-disclosure
Weaponized exploit script for CVE-2020-35575, a password-disclosure vulnerability in TP-Link router web interfaces, granting remote administrative…
 entysec/rombuster
RomBuster is a router exploitation tool that allows to disclosure network router admin password.
 ethancunt/cve-2022-45599
Proof-of-concept for CVE-2022-45599: PHP type juggling vulnerability in Aztech WMB250AC router login.php allowing admin authentication bypass via…
 s1lkys/cve-2020-29669
Macally WIFISD2
 code-byter/cve-2020-29669
Macally WIFISD2
 huzaifahussain98/cve-2019-17525
D-LINK ROUTER "MODEL NO: DIR-615" with "FIRMWARE VERSION:20.10" & "HARDWARE VERSION:T1
 hook-s3c/cve-2018-18852
Authenticated remote code execution exploit for CERIO routers (DT300N, DT100G, AMR-3204, WMR-200N) using vendor default credentials. Python PoC…
 shaheemirza/tendaspill
An exploitation tool to extract passwords using CVE-2015-5995.
 s0c5/remotepasswordwifi
Script in Ruby. Break Remote router wifi passwords.