

hashcat
 hashcat/hashcat
World's fastest and most advanced password recovery utility
cryptographyencryption-decryption-toolshash-analysis+2
hashcat/hashcatWorld's fastest and most advanced password recovery utility
 abraxas/vaultwarden-ip-header-spoof
Vaultwarden 1.37.3 default X-Real-IP trusted-local bypasses login rate limits on Docker NAT
 andreiverse/gorilla
tool for generating wordlists or extending an existing one using mutations.
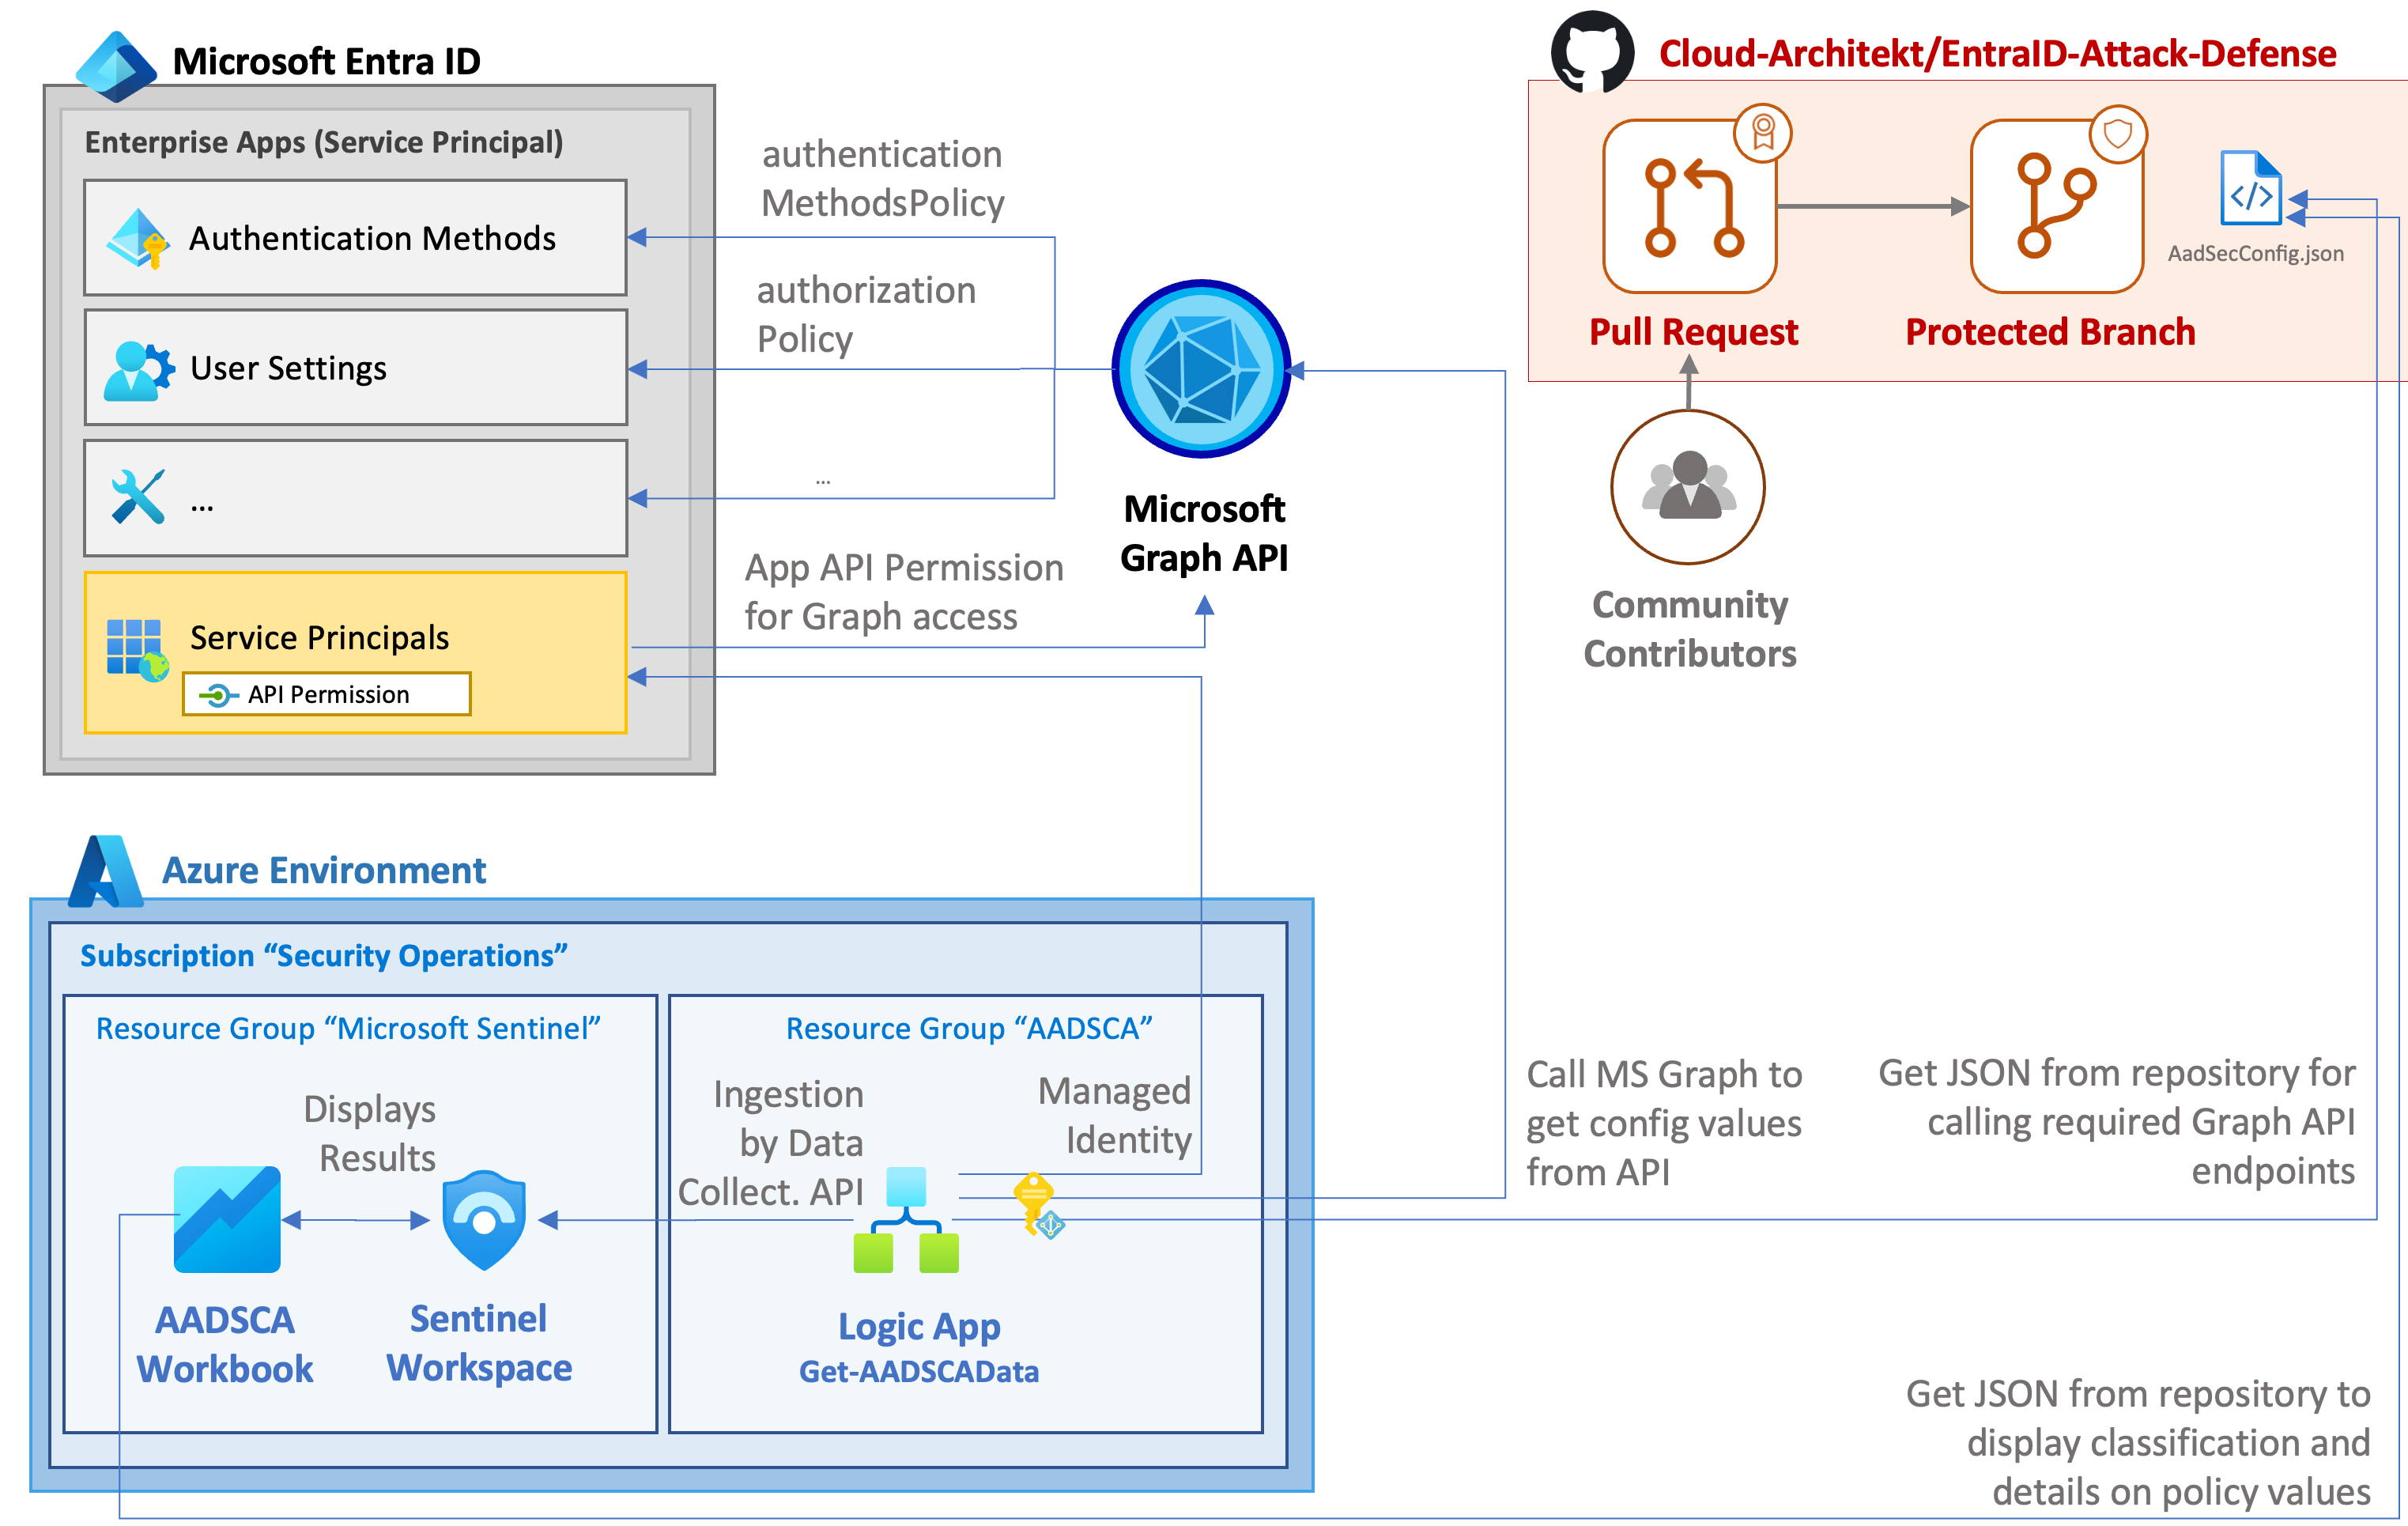 cloud-architekt/azuread-attack-defense
This publication is a collection of various common attack scenarios on Microsoft Entra ID (formerly known as Azure Active Directory) and how they can…
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 ivancabrera02/whfb-pincapture
Captures Windows Hello PINs at entry by injecting a DLL into LogonUI.exe that sets a CPU hardware breakpoint on NgcSerializeConvenienceCredential,…
 occasionpuffbird12/airstrike
Audit Wi-Fi security on Linux with monitor mode, handshake capture, and offline WPA/WPA2 password testing in one guided GUI
 openwall/john
John the Ripper jumbo - advanced offline password cracker, which supports hundreds of hash and cipher types, and runs on many operating systems,…
 suriyaboon/hackthebox-facts
HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…
 nxploited/cve-2026-96451
WordPress Ultimate Member plugin <= 2.13.1 - Privilege Escalation vulnerability
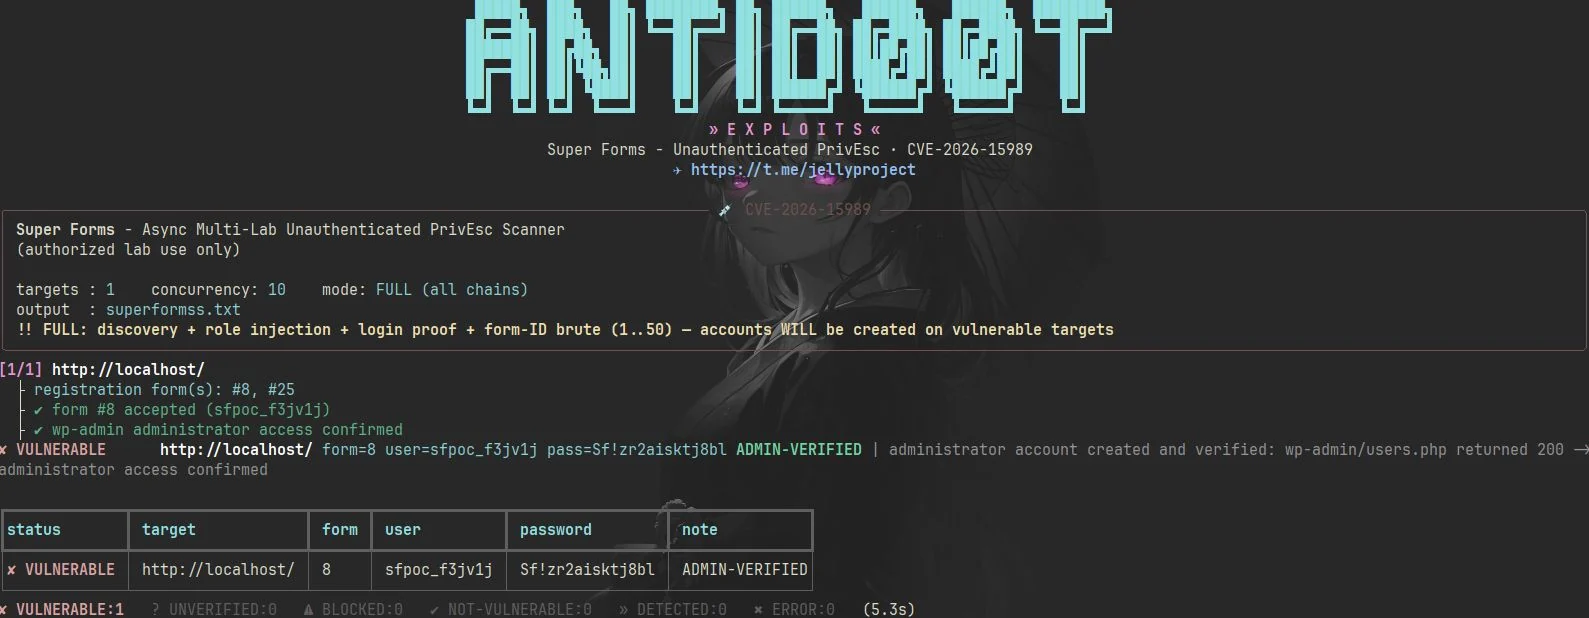 antid00t/cve-2026-15989
Python PoC scanner for CVE-2026-15989, exploiting unauthenticated role injection in WordPress Super Forms to create admin accounts and verify access.
 langz337/cve-2026-14281
Mass scanner and single-target exploit for CVE-2026-14281, an unauthenticated privilege escalation in the WordPress Automation Web Platform plugin…
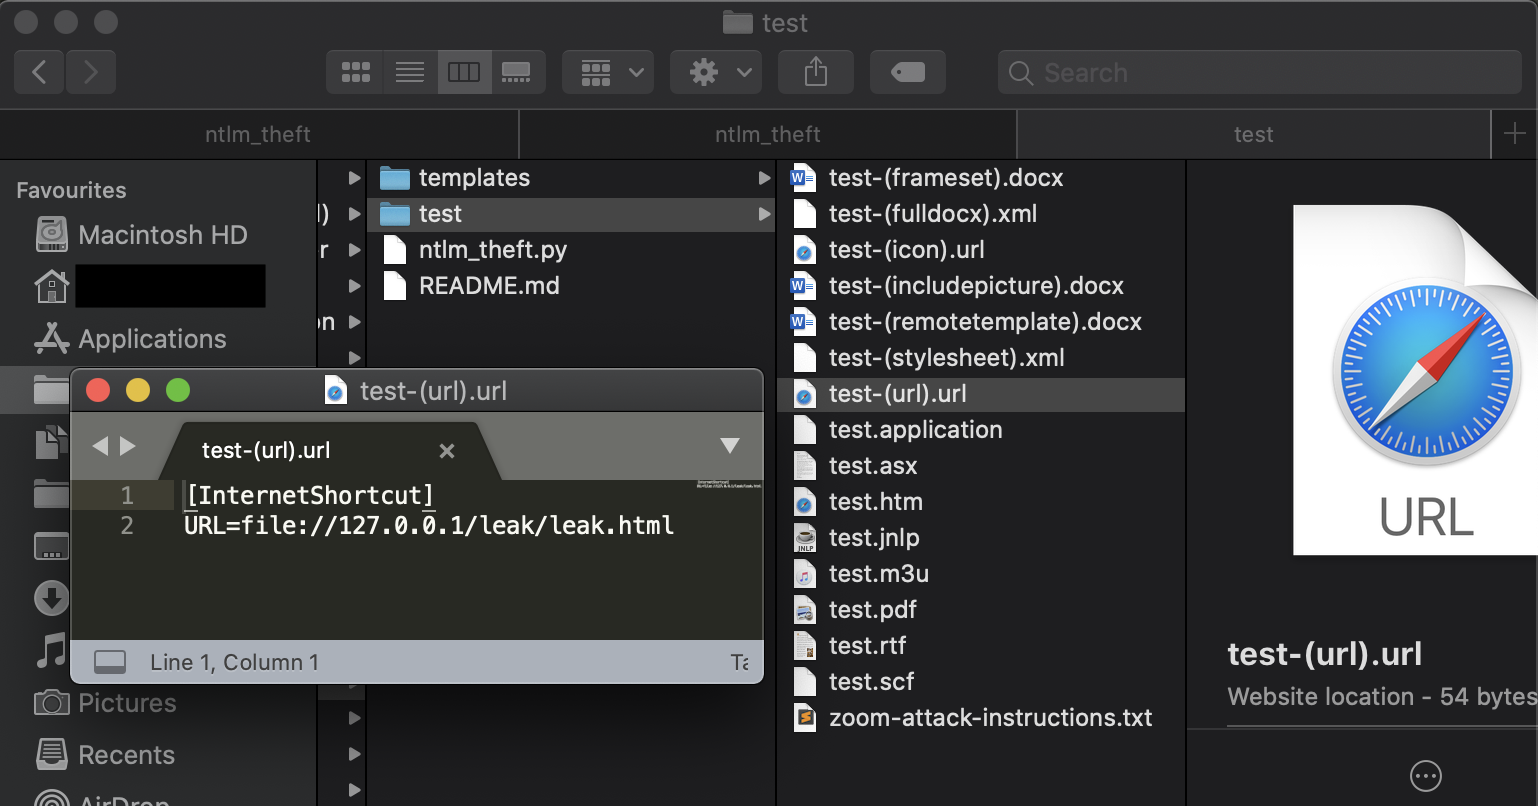 greenwolf/ntlm_theft
A tool for generating multiple types of NTLMv2 hash theft files by Jacob Wilkin (Greenwolf)
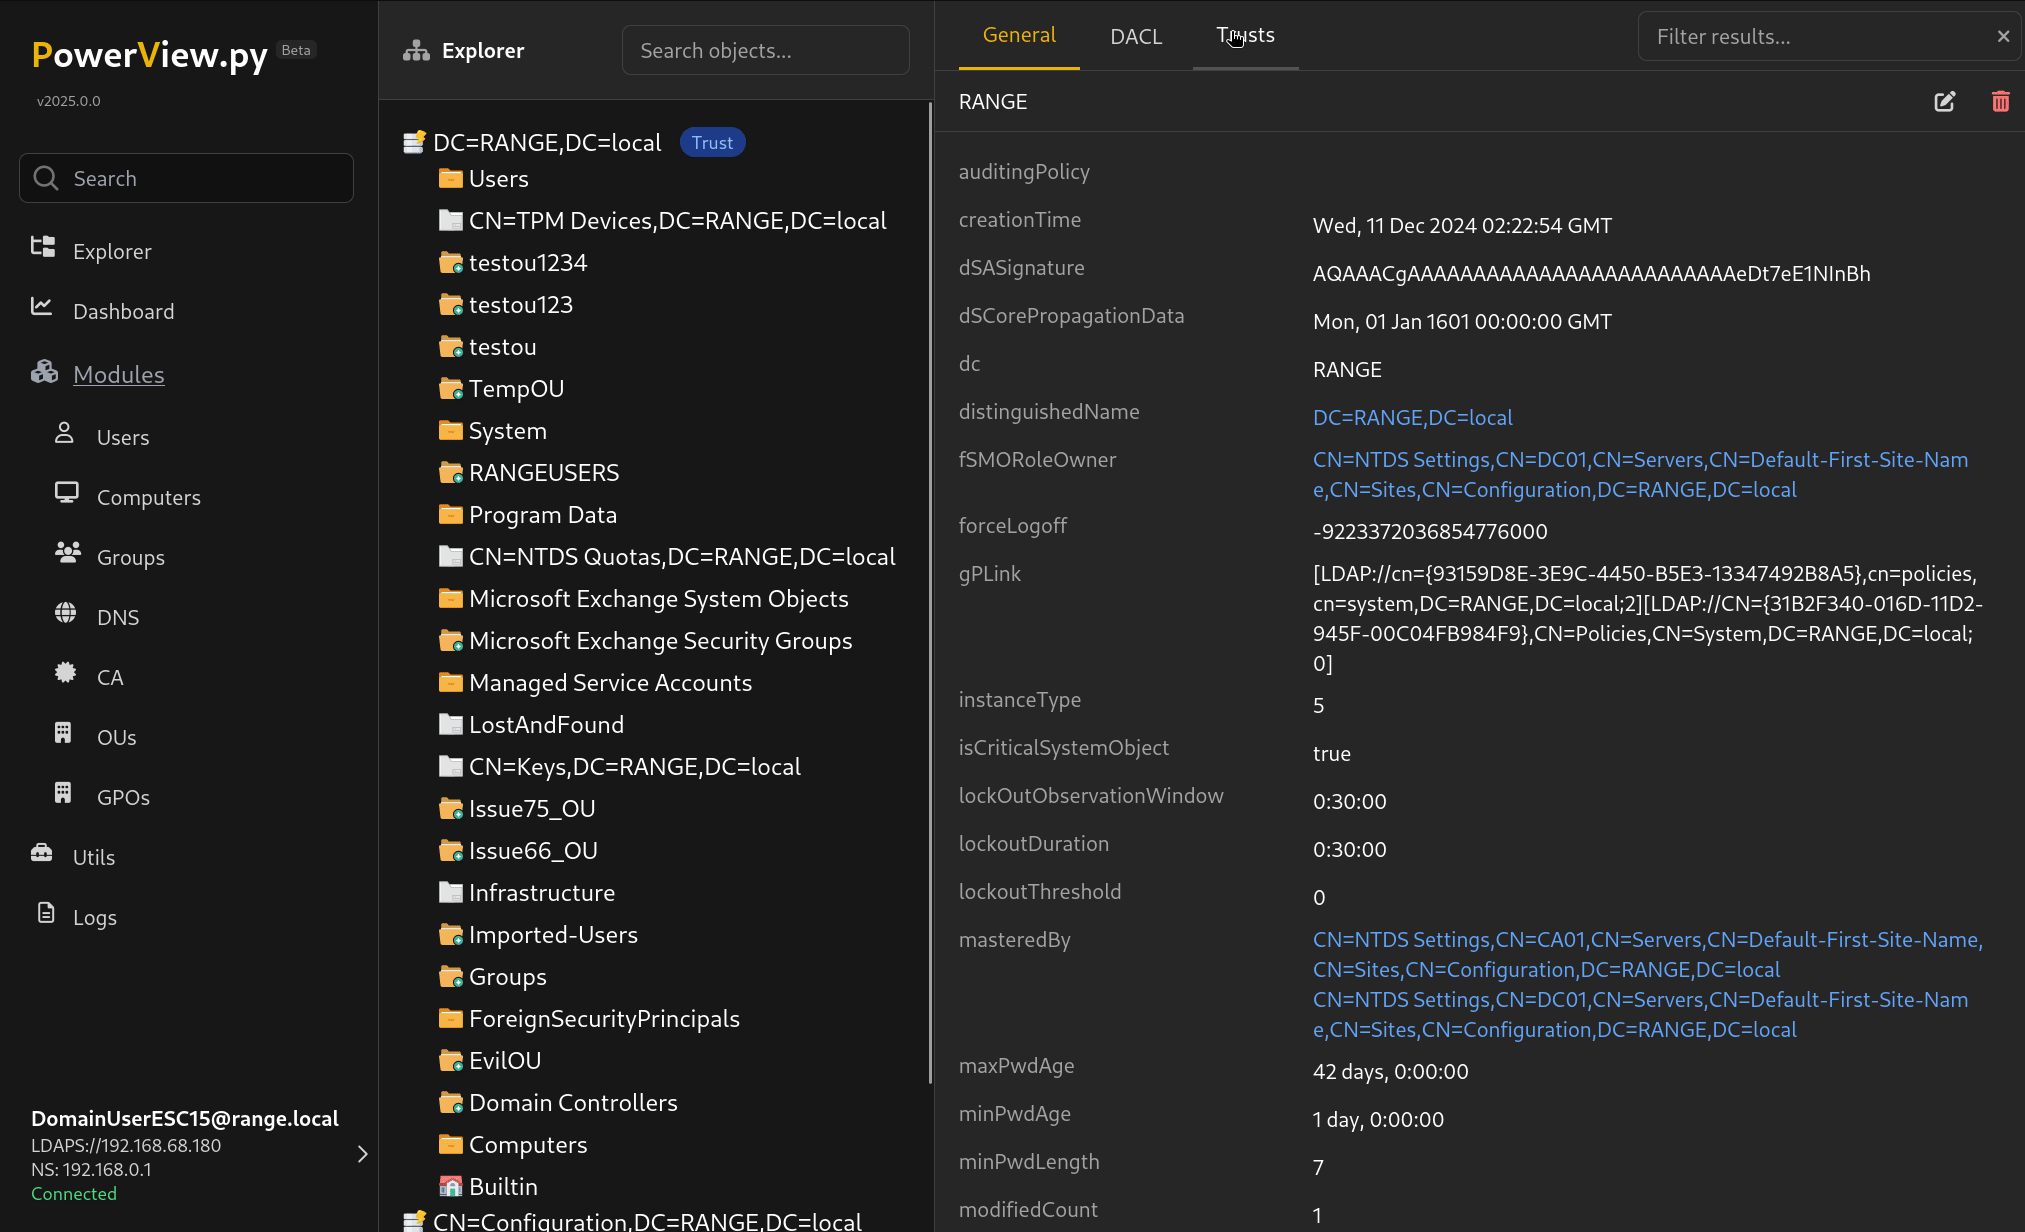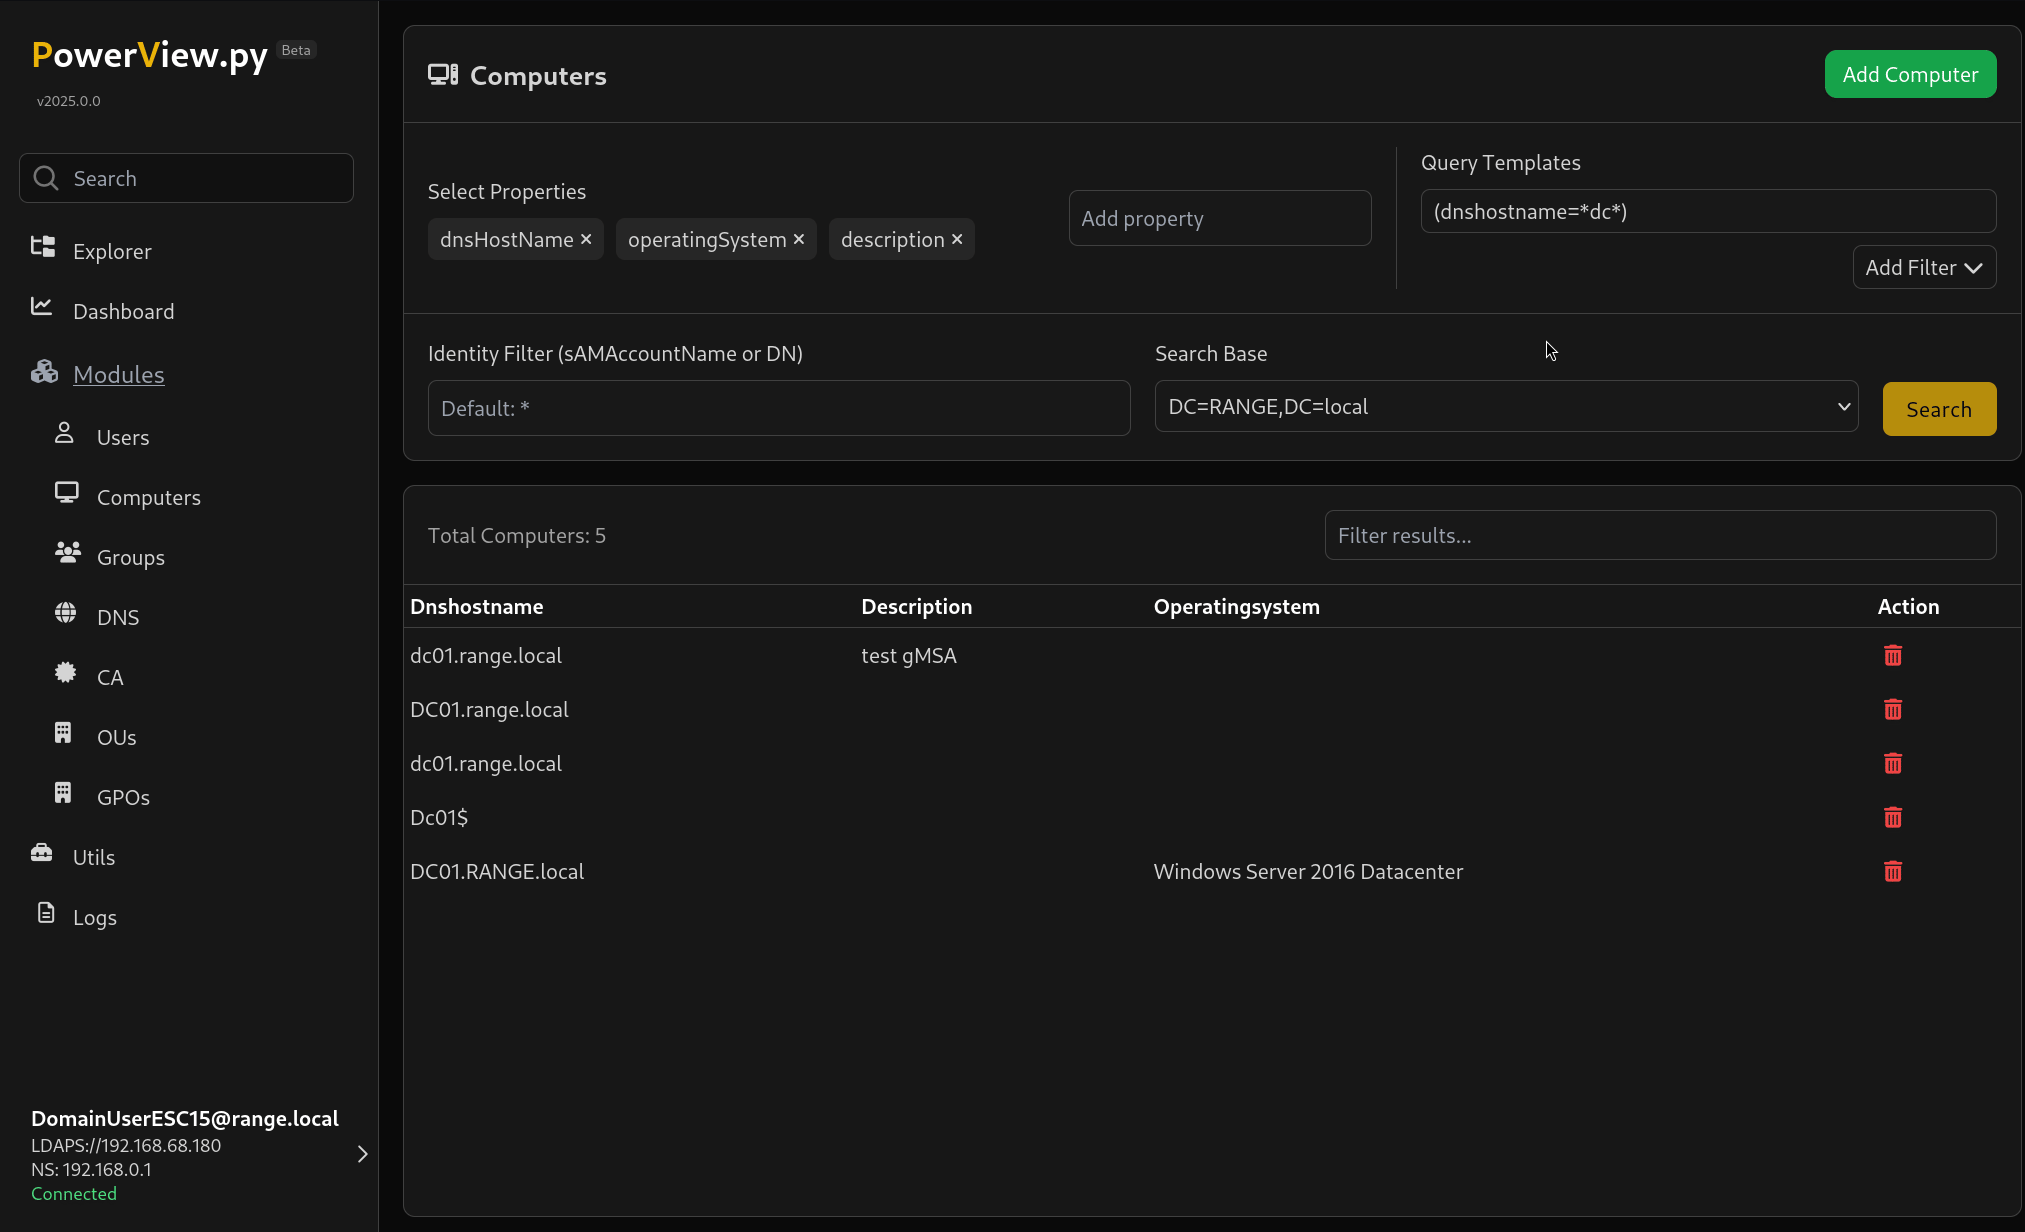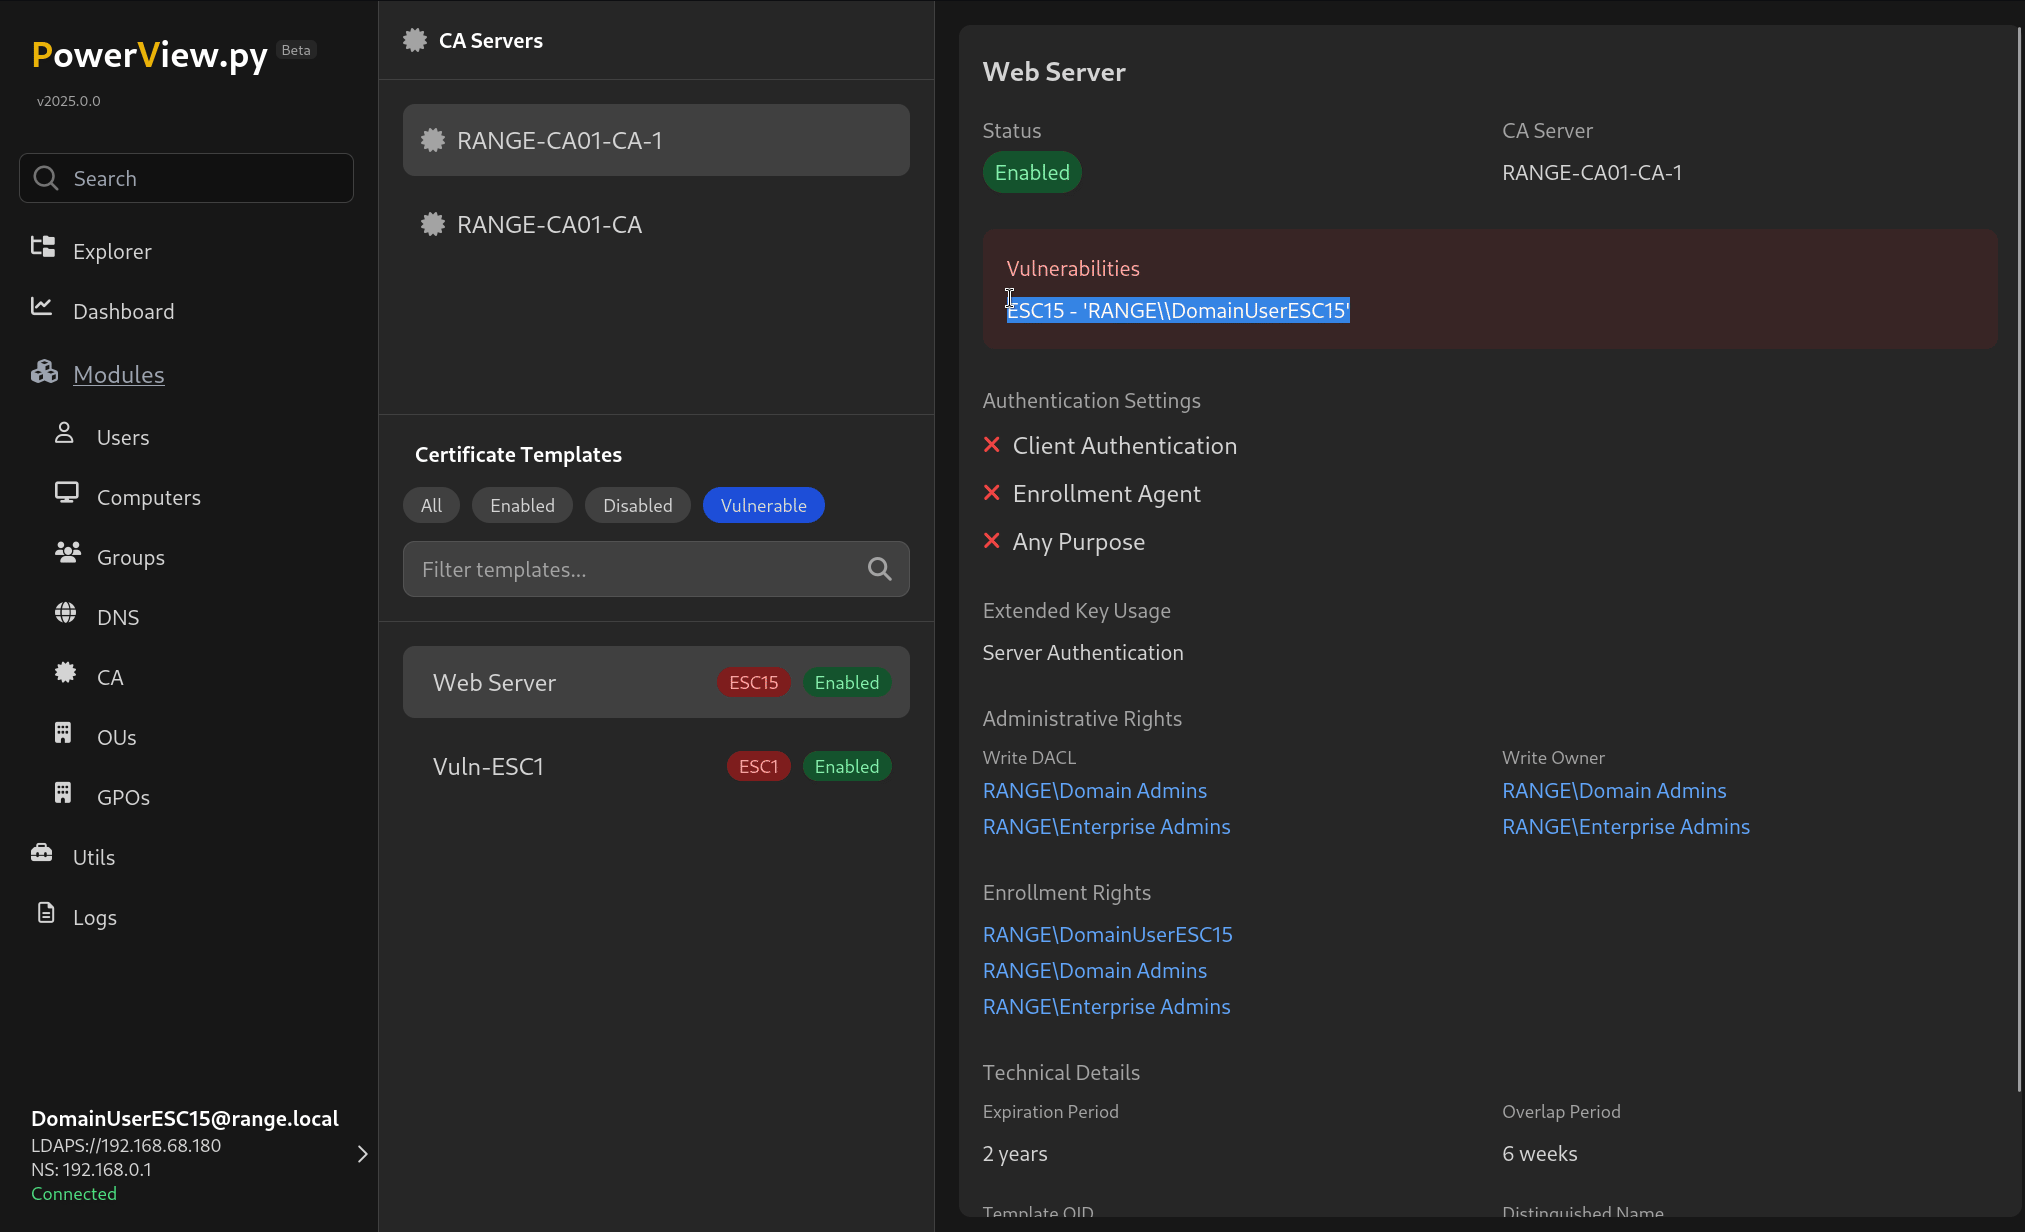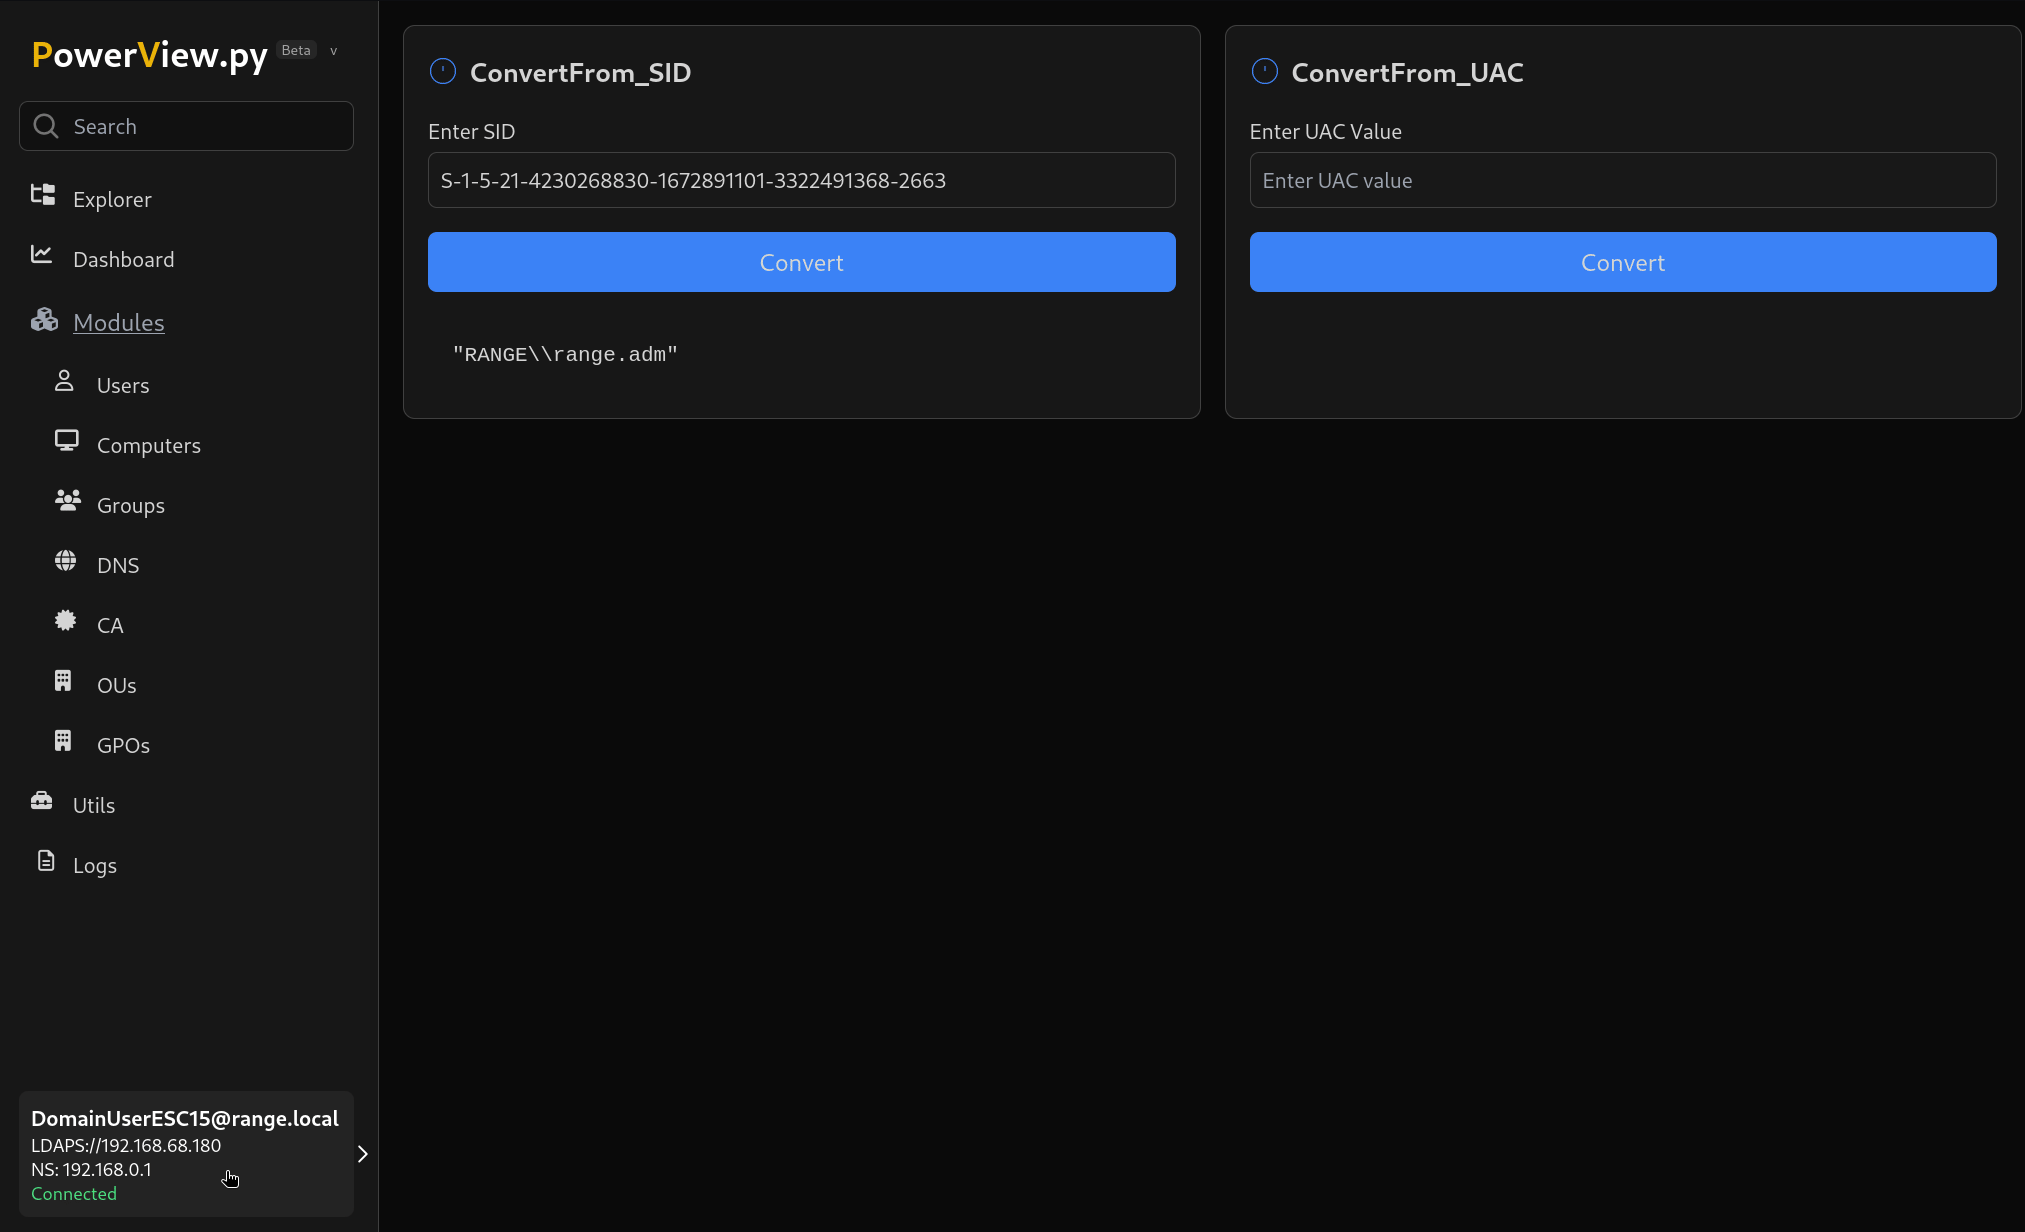 aniqfakhrul/powerview.py
Powerview on steroids
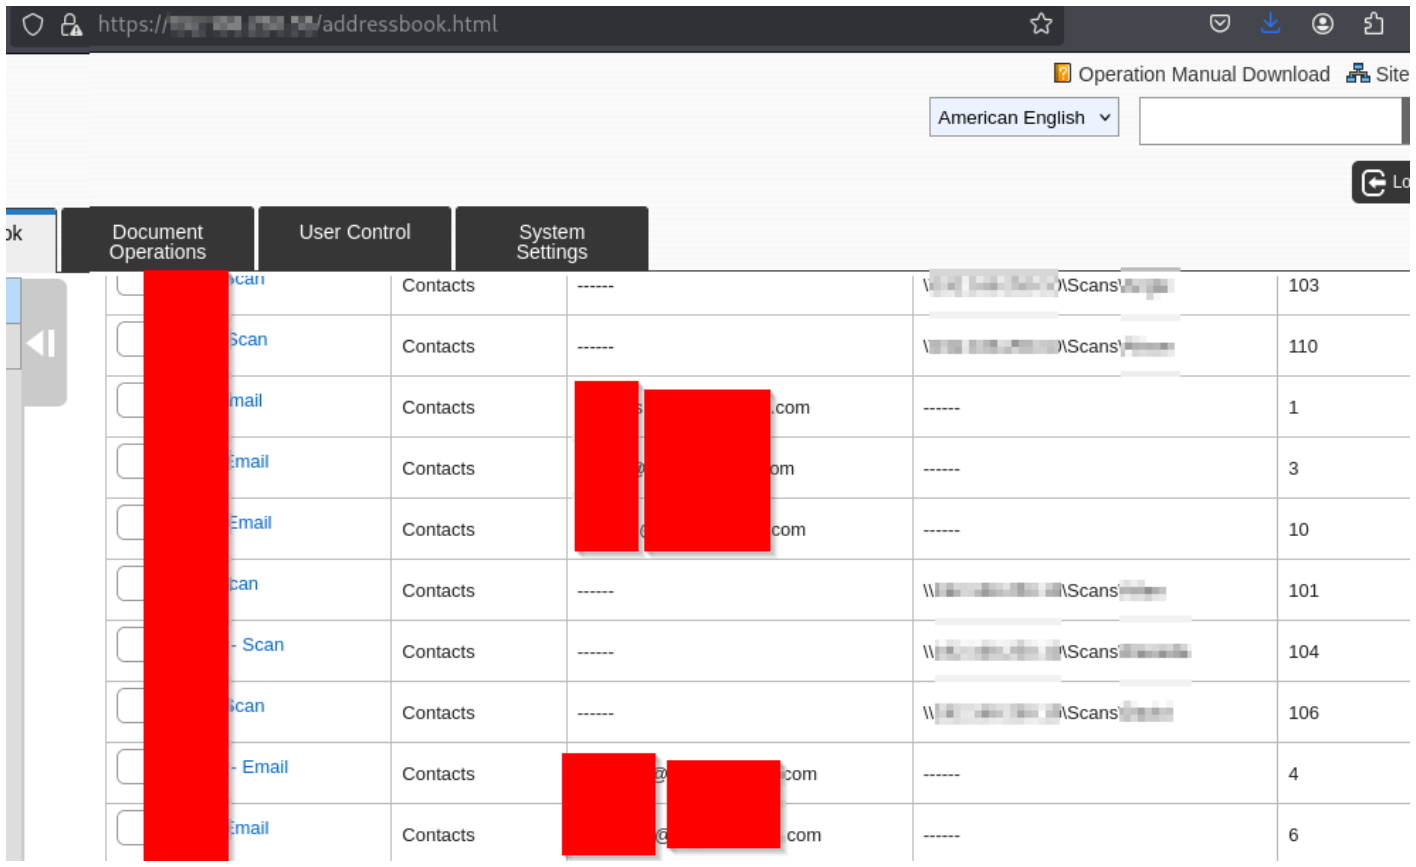 redr0nin/cve-2026-63563
Unauthenticated Address Book Modification on Sharp MX/BP Multifunction Printers
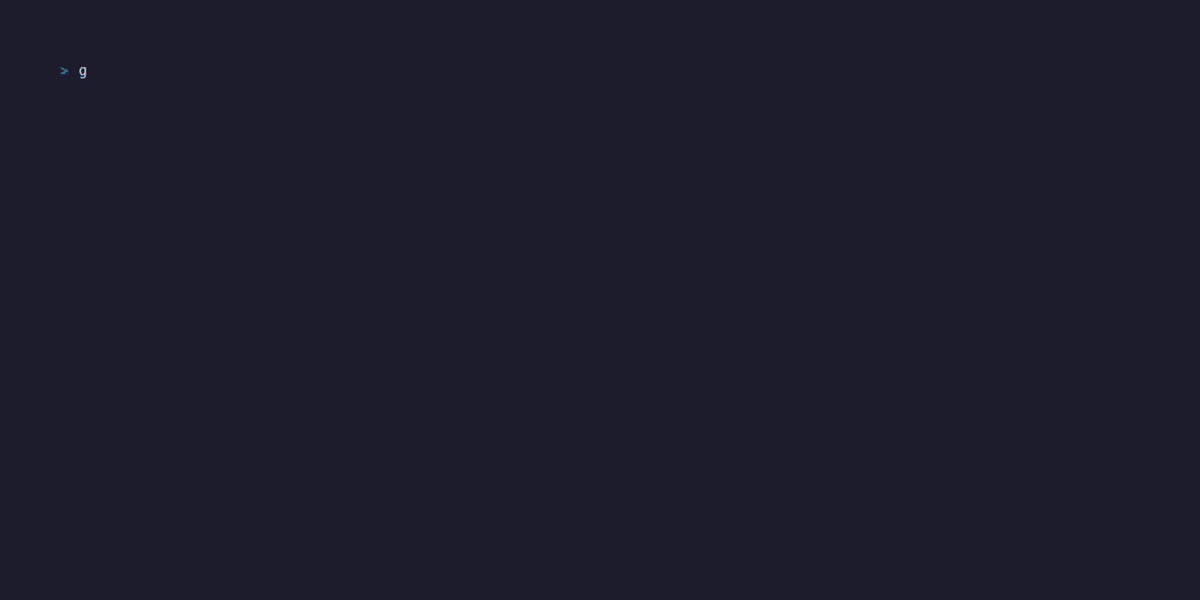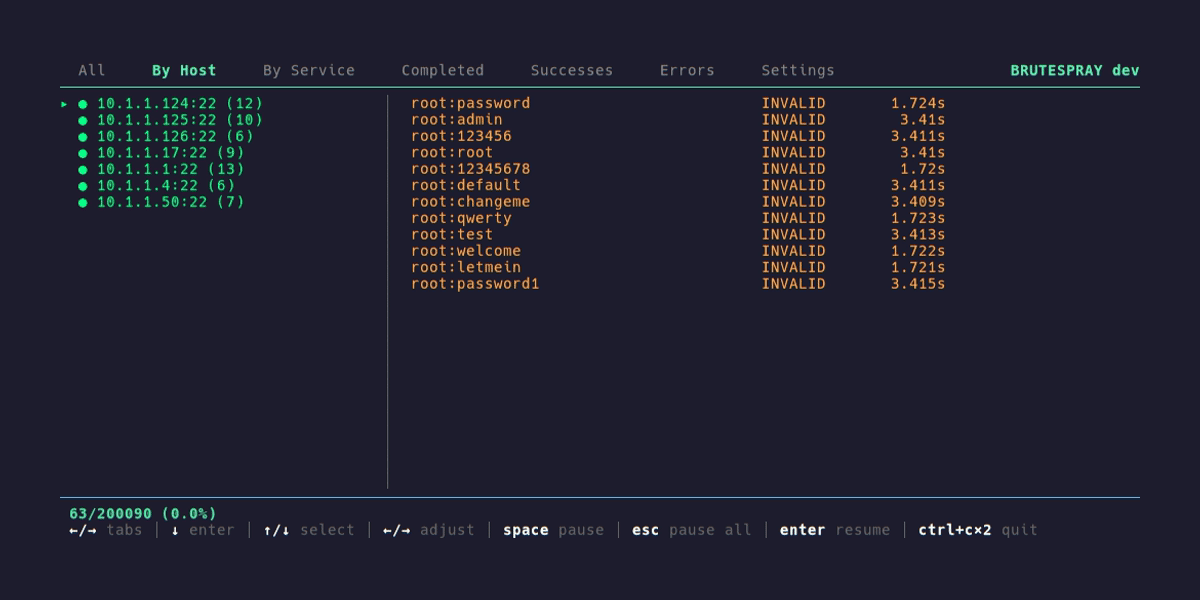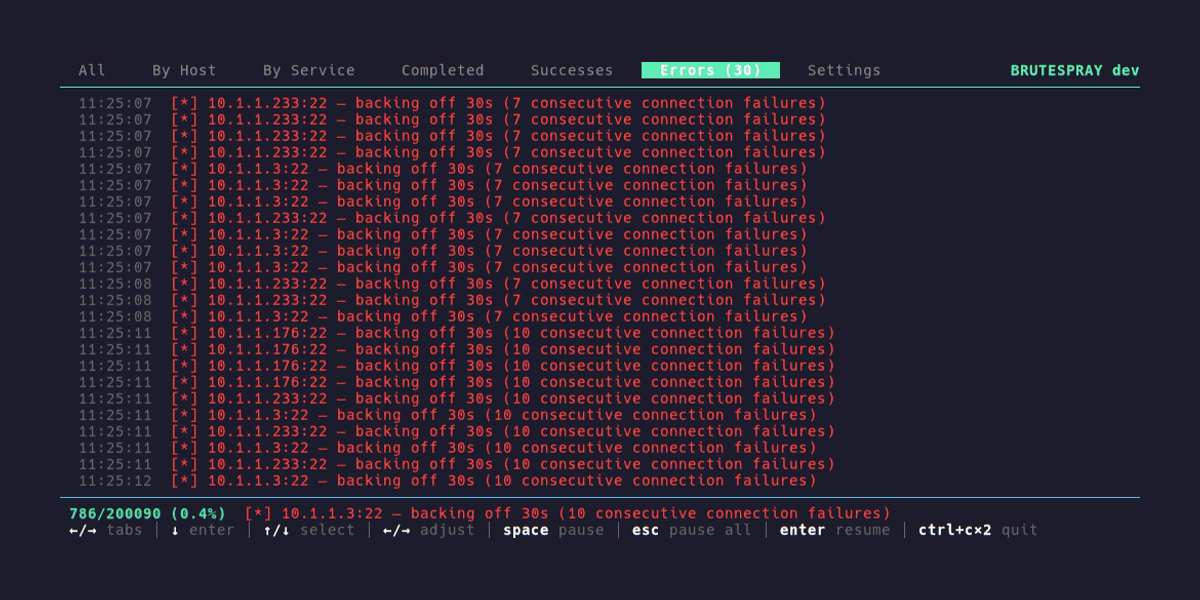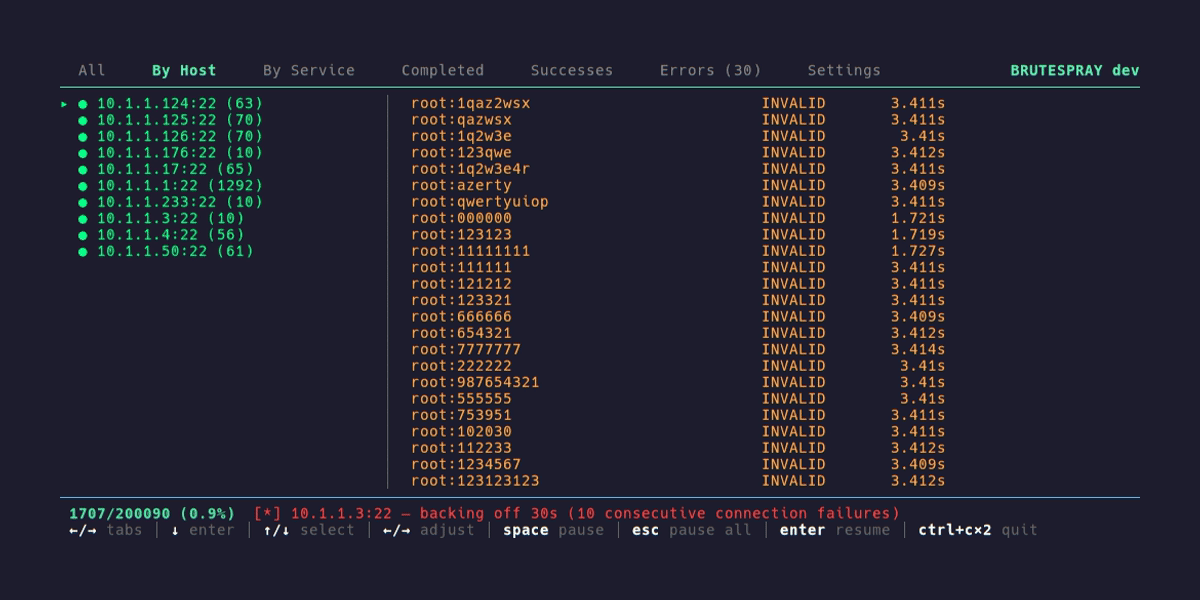 x90skysn3k/brutespray
Fast, multi-protocol credential brute-forcer. Parses Nmap, Nessus, and Nexpose output to automatically test default and custom credentials across 30+…
 curtail-inc/hello-regrade-security
Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…