
CVE-2024-28000-Exploit-Lab
 shawnng078-ops/cve-2024-28000-exploit-lab
Hands-on reproduction of CVE-2024-28000 in LiteSpeed Cache using an isolated WordPress lab. Includes reconnaissance, vulnerable hash recovery,…
educationexploitationlabs-practice+5
shawnng078-ops/cve-2024-28000-exploit-labHands-on reproduction of CVE-2024-28000 in LiteSpeed Cache using an isolated WordPress lab. Includes reconnaissance, vulnerable hash recovery,…
 c0gnit00/cve-2024-51482
CVE-2025-51482 POC, Dump Credentials From zm.Users
 bridgeralderson/cve-2024-51482
ZenoMinder Blind SQL Injection PoC
 ik0nw/cve-2024-46987
Exploit for CVE-2024-46987 path traversal in Camaleon CMS enabling arbitrary file download and automated SSH key extraction via brute-force.
 zeved/cve-2024-42049-poc
PoC for CVE-2024-42049
 mqkgithub/moniker-link-cve-2024-21413
Step-by-step walkthrough of exploiting CVE-2024-21413 in Microsoft Outlook to bypass Protected View and leak NTLM credentials via Moniker Links,…
 lisa-2905/cve-2024-56429
Exploit for CVE-2024-56429 demonstrating extraction of Apache Derby database boot password from iLabClient source code, enabling local database…
 absholi7ly/poc-cve-2024-57040
CVE-2024-57040 is a security vulnerability found in certain TP-Link TL-WR845N router models. Specifically, it involves a "hardcoded" password for the…
 tuancui22/zerologonwithimpacket-cve2020-1472
A practical proof-of-concept for CVE-2020-1472 (Zerologon) using the Impacket library to exploit Netlogon vulnerability and perform unauthorized…
 oditynet/sleepall
trojan CVE-2024-28085 CVE 28085
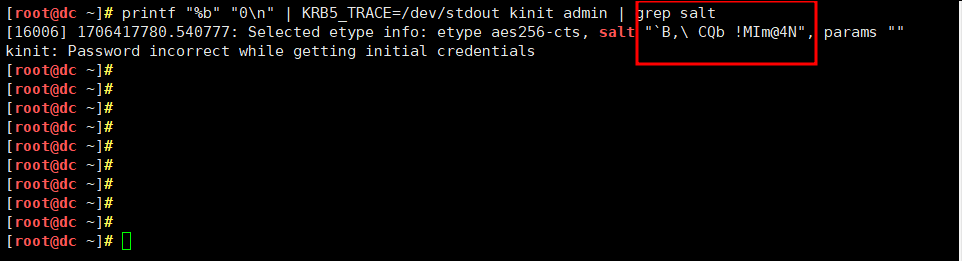 im10n/cve-2024-3183-poc
POC for CVE-2024-3183 (FreeIPA Rosting)
 mzhmo/leakedwallpaper
Leak of any user's NetNTLM hash. Fixed in KB5040434
 gquere/pwn_jenkins
Notes about attacking Jenkins servers
 devisions/cve-2024-29868
Proof of concept of CVE-2024-29868 affecting Apache StreamPipes from 0.69.0 through 0.93.0
 hussainfathy/cve-2024-28999
Exploit for CVE-2024-28999 SolarWinds Platform Race Condition Vulnerability - login page
 fernandobortotti/cve-2024-24919
Automated exploit for CVE-2024-24919 with API-based vulnerable IP discovery and LFI brute-force using custom wordlists. Designed for educational…
 maen08/cve-2024-25277
Resources and PoCs
 david-botelho-mariano/exploit-cve-2024-25723
Educational Proof of Concept exploit for CVE-2024-25723, demonstrating unauthorized account takeover in ZenML via API password reset, with version…