DarkTortilla-RAT-Telegram-Exfiltration-Payload-Extraction-Analysis

Reverse engineering analysis of DarkTortilla RAT, a sophisticated malware that steals credit card data, decrypts browser passwords, and exfiltrates…

Reverse engineering analysis of DarkTortilla RAT, a sophisticated malware that steals credit card data, decrypts browser passwords, and exfiltrates…

Retrieves the master password from Keepass memory dump, using a hint of bruteforce.

Penetration Testing Reference Bank - OSCP / PTP & PTX Cheatsheet

Cisco ASA Software and ASDM Security Research

Physmem2profit can be used to create a minidump of a target hosts' LSASS process by analysing physical memory remotely

Dump cookies and credentials directly from Chrome/Edge process memory

This tool leverages the Process Forking technique using the RtlCreateProcessReflection API to clone the lsass.exe process. Once the clone is created,…

Smart keylogging capability to steal SSH Credentials including password & Private Key

RunAs Utility Credential Stealer implementing 3 techniques : Hooking CreateProcessWithLogonW, Smart Keylogging, Remote Debugging

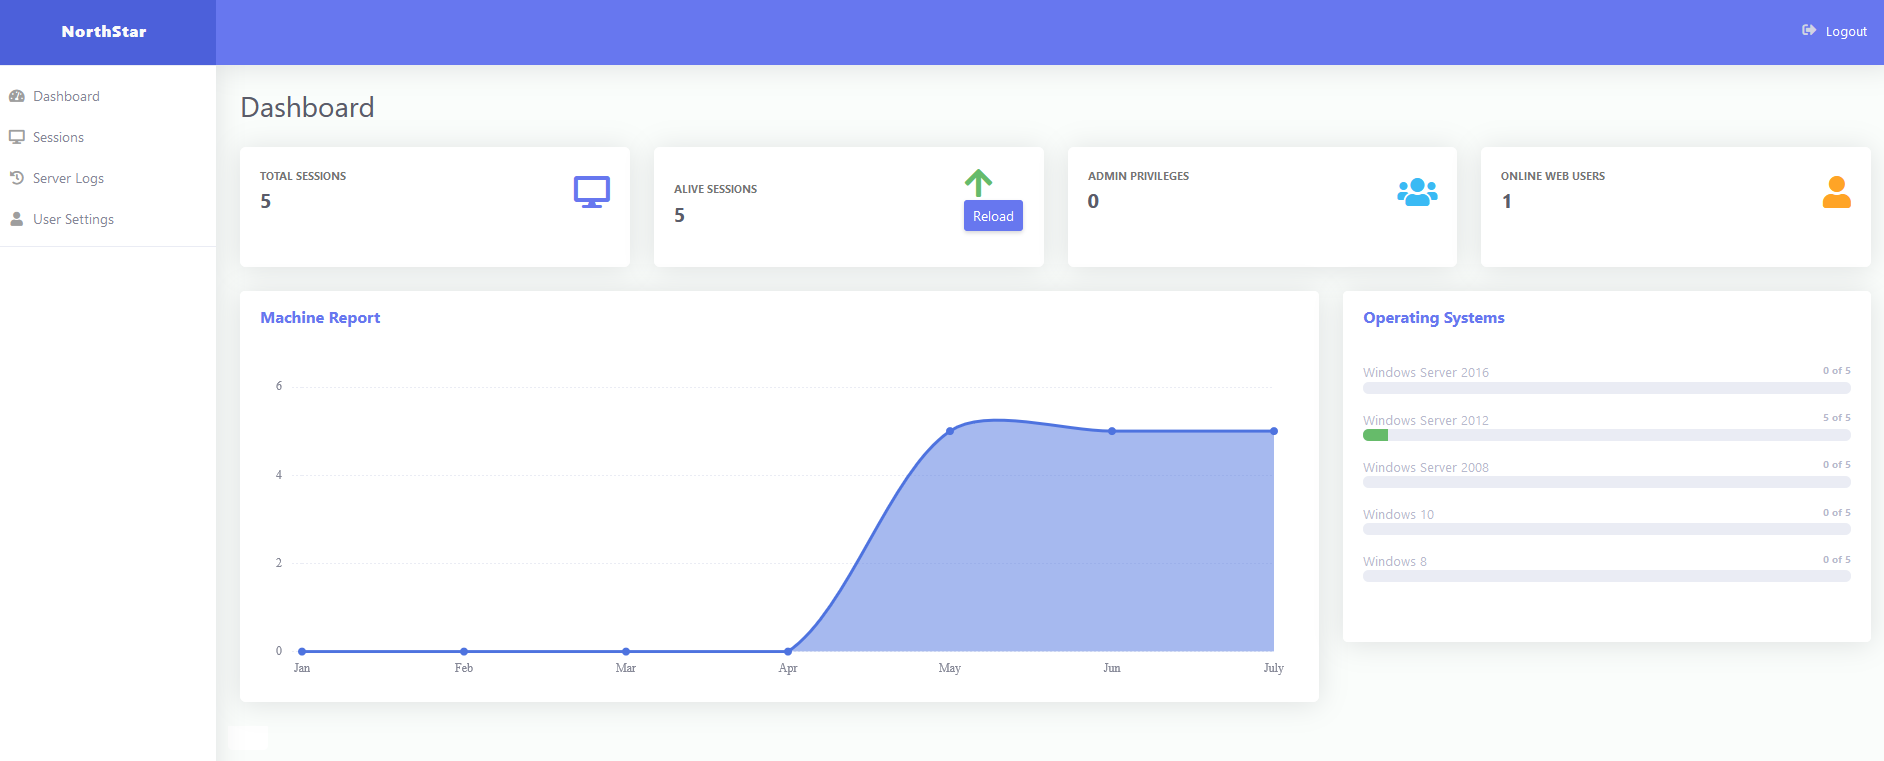
Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…

Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…

trojan CVE-2024-28085 CVE 28085

Scripts and utilities to help your hacking needs

SkyRAT - Powershell Remote Administration Tool

Original PoC for CVE-2023-32784

CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability

Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…

🔐 Lockdoor Framework : A Penetration Testing framework with Cyber Security Resources