
sshamble
 runzeroinc/sshamble
Research tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.
authenticationdefensive-toolsinformation-gathering+6
1.2k
runzeroinc/sshambleResearch tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.
 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 pr0x13/idict
PHP-based iCloud Apple ID dictionary attack tool that bypasses account lockout and secondary authentication to brute-force credentials.
 yeee3642/edu-recon
Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…
 brannondorsey/naive-hashcat
Plug-and-play hashcat wrapper that cracks password hashes using preconfigured dictionary, rule-based, combinator, and mask attacks, supporting dozens…
 frizb/hashcat-cheatsheet
Hashcat reference for OSCP/penetration testing: hash identification, cracking syntax for Linux, Windows, archives, databases, Kerberos tickets, and…
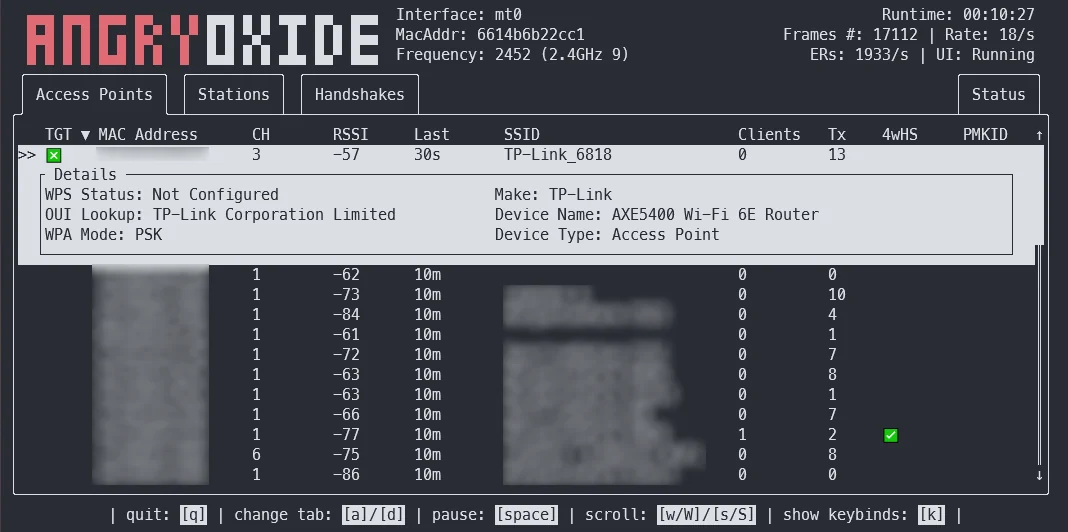 ragnt/angryoxide
Offensive 802.11 auditing tool that automates WPA/WPA2 handshake and PMKID capture using deauthentication, rogue-client, and channel-switch attacks,…
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
 wattocyber/oscp-notes-2026
OSCP notes vault + exam cockpit dashboard: merged technique notes, variable-filled command decks, machines, creds, and runbook for exam day. MIT.
 ghostpack/deeppass
Hunting for passwords with deep learning
 olivierlaflamme/cheatsheet-god
Penetration Testing Reference Bank - OSCP / PTP & PTX Cheatsheet
 0xsyr0/vx-underground-wordlist
Wordlist to crack .zip-file password
 dozernz/bugstropics
Supporting material for the "Hunting Bugs In The Tropics" DEFCON 30 talk
 saisathvik1/windows-privilege-escalation-notes
My handbook for Windows Privilege Escalation concepts. Do Check out my Playlist, link: https://www.youtube.com/playlist?list=PLlrnAg4kKF3puXLI0JyltbNJ…
 flangvik/sharpcollection
Nightly builds of common C# offensive tools, fresh from their respective master branches built and released in a CDI fashion using Azure DevOps…
 otterhacker/labs4u2self
Deployable AWS-hosted Active Directory pentest lab with domain controller and vulnerable MSSQL; practice S4U2Self abuse, SQL brute force, and RCE.
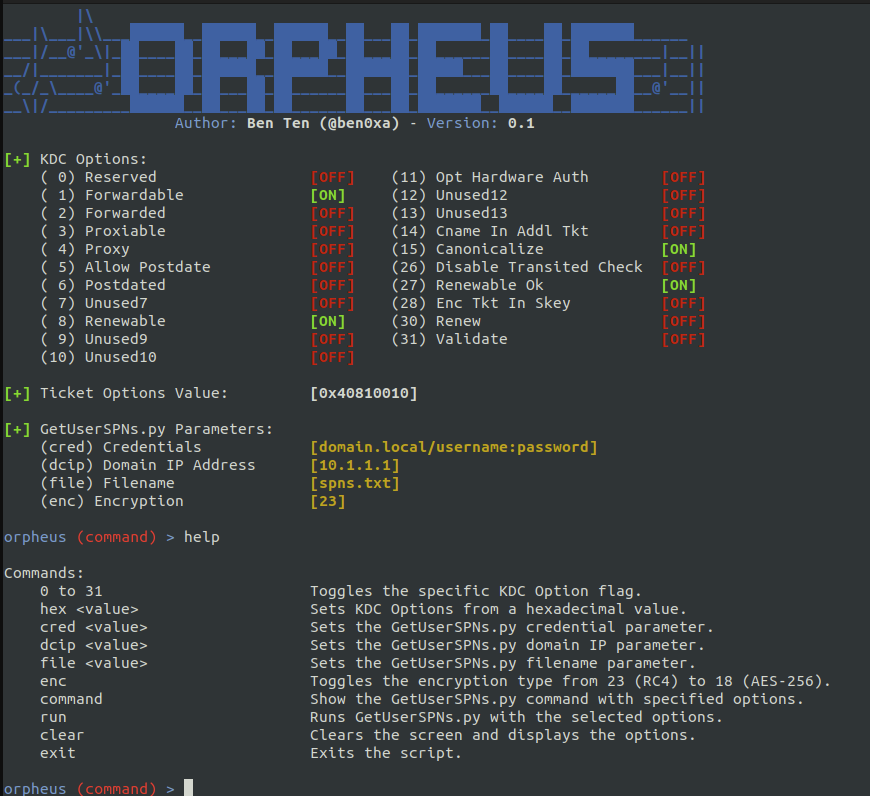 trustedsec/orpheus
Bypassing Kerberoast Detections with Modified KDC Options and Encryption Types
 postmodern/wordlist.rb
A Ruby library and CLI for generating and working with wordlists.