
ntlmscout
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
authenticationdns-analysisinformation-gathering+8
56
boydhacks/ntlmscoutUnauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 mourafuseti/vulneravel-cve-2018-14847---credenciais-extraidas
VULNERAVEL CVE-2018-14847 - CREDENCIAIS EXTRAIDAS MIKROTIK EM PYTHON
 ignis-sec/pwdb-public
A collection of all the data i could extract from 1 billion leaked credentials from internet.
 aseemjakhar/kcmd
Kankun Smart Socket Hijacker and Sniffer. The kankun smart socket and its mobile app use a hardcoded AES 256 bit key to encrypt and decrypt…
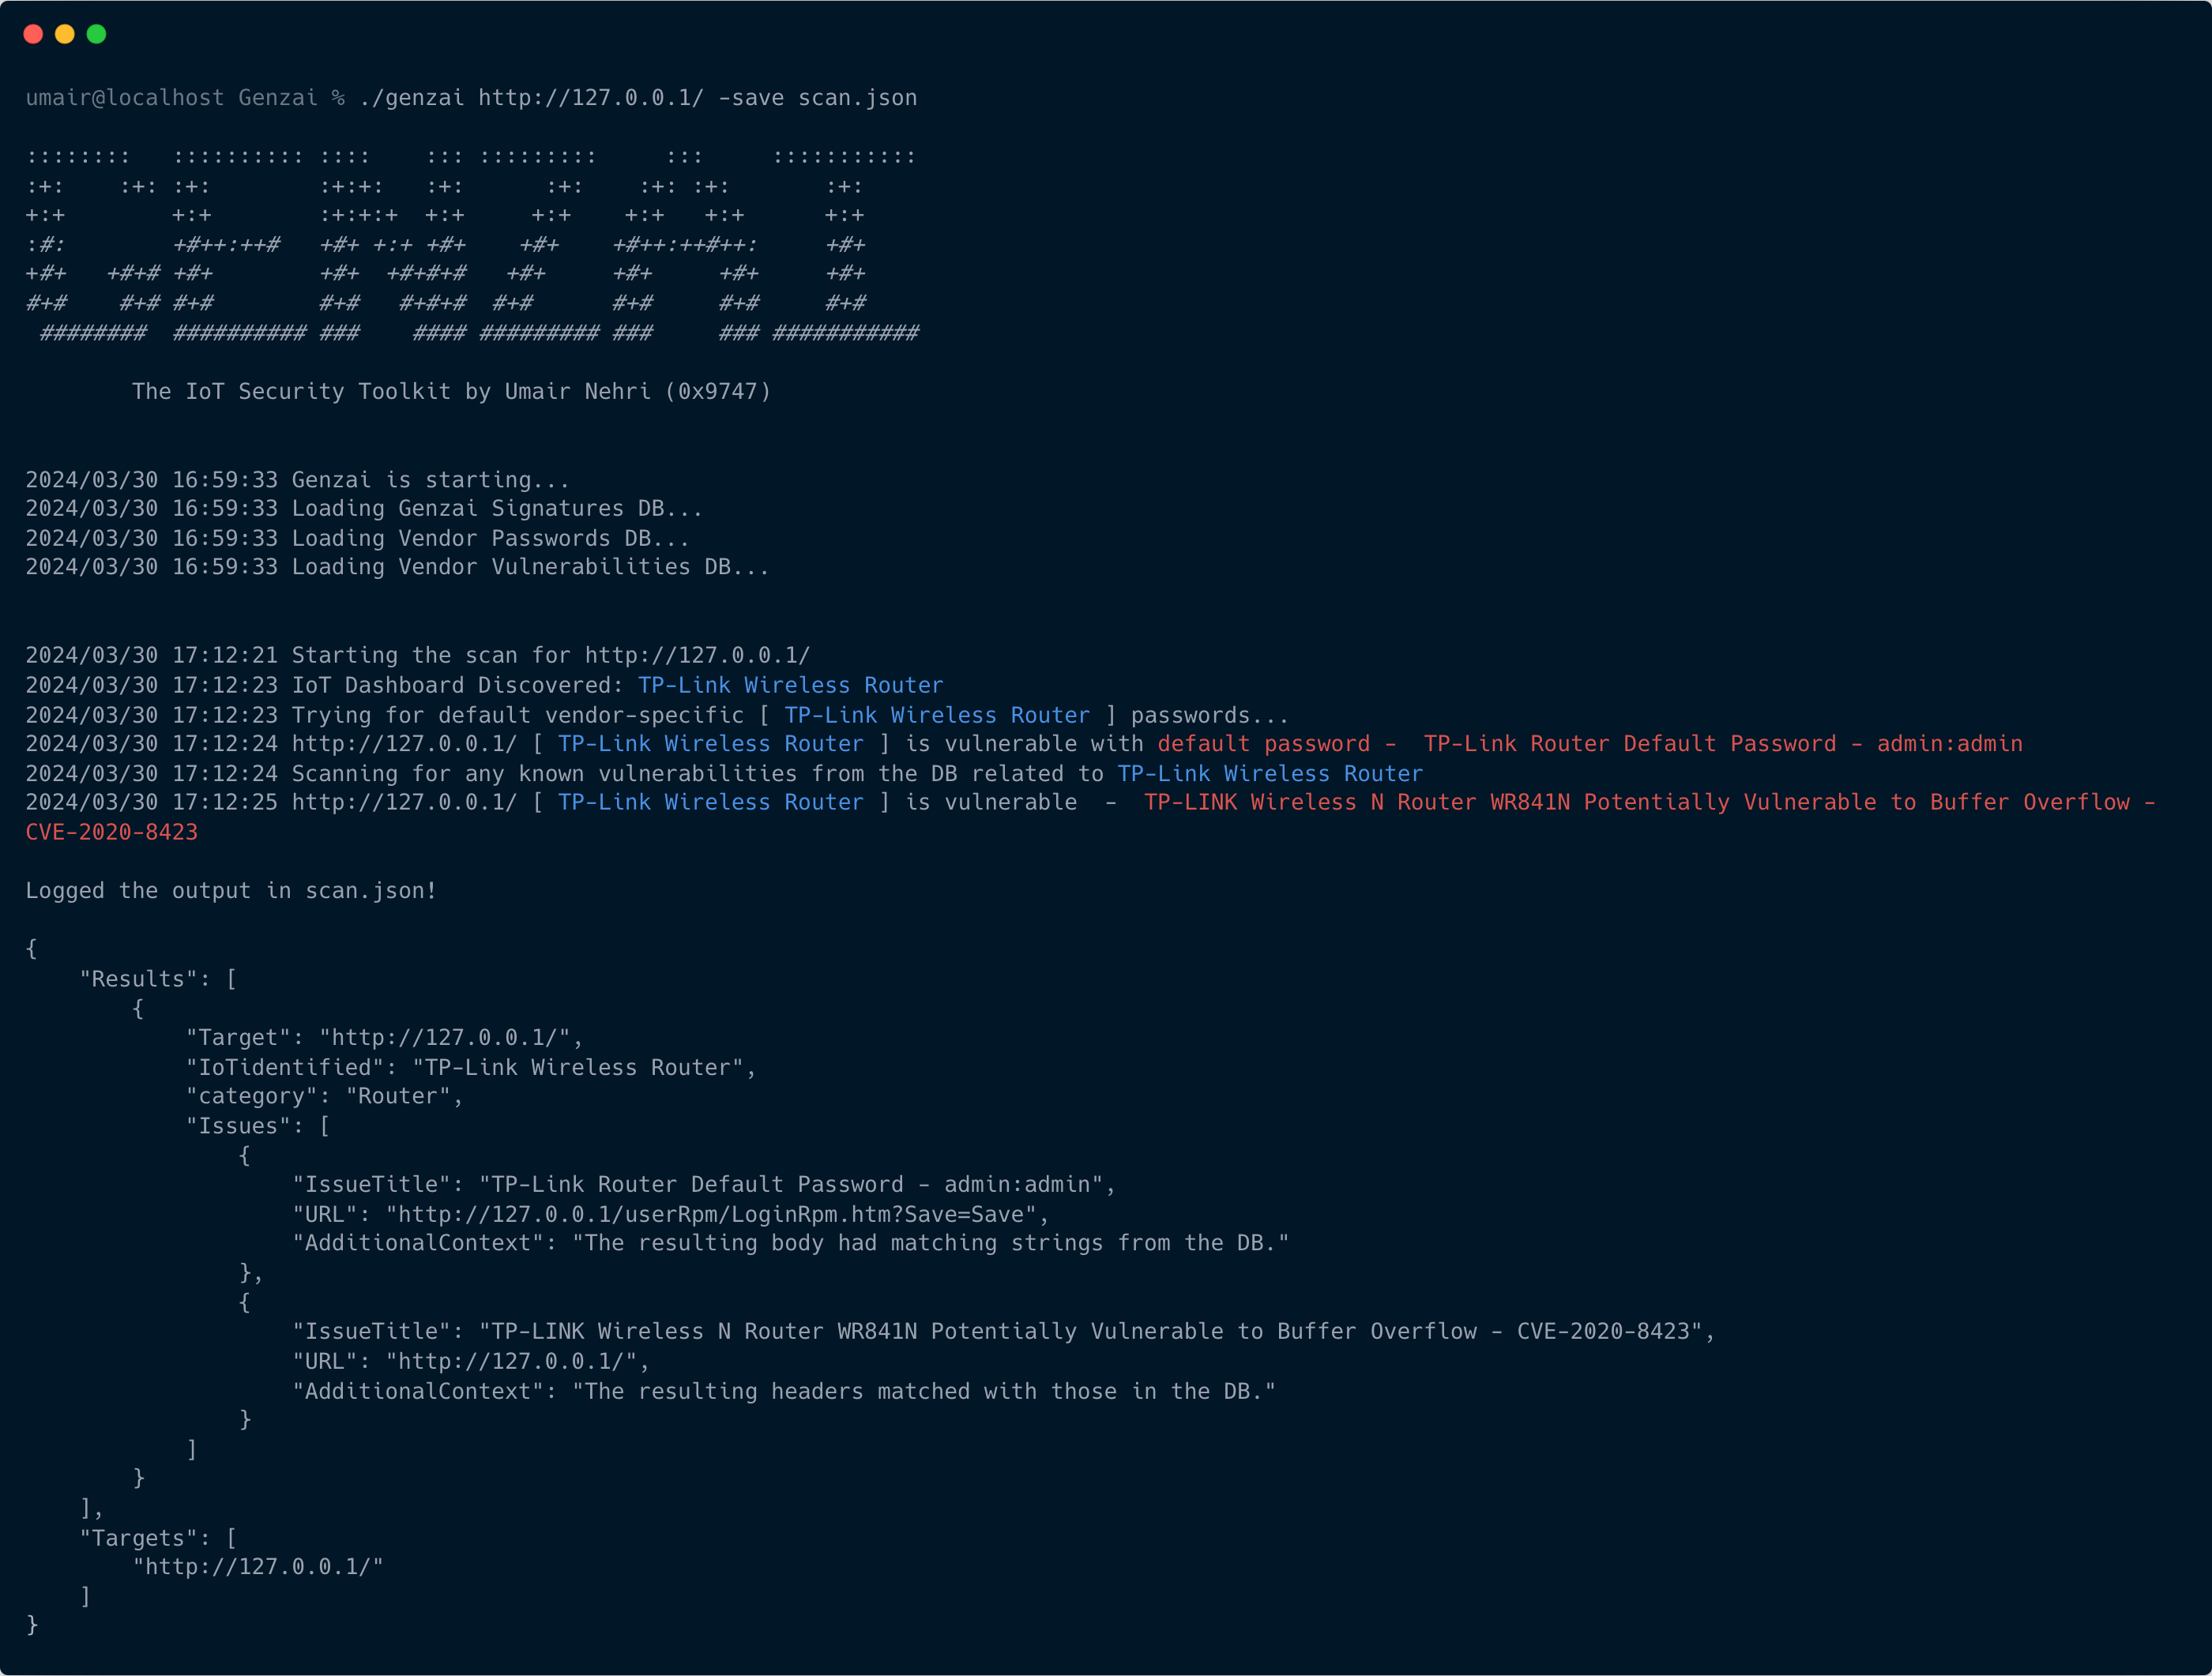 umair9747/genzai
The IoT security toolkit to help identify IoT related dashboards and scan them for default passwords and vulnerabilities.
 dearpan/cve-2018-9995
Exploit for CVE-2018-9995 targeting DVR devices. Sends a crafted Cookie header to retrieve plaintext admin credentials from the web control panel.
 redfox-security/digisol-dg--gr1321-s-password-storage-in-plaintext--cve-2024-4232
Proof-of-concept exploit for CVE-2024-4232 targeting plaintext password storage in Digisol DG-GR1321 routers. Demonstrates extraction of credentials…
 haingn/hik-cve-2021-36260-exploit
Go-based brute-force exploit tool targeting Hikvision cameras vulnerable to CVE-2021-36260, with multi-threaded scanning and configurable…
 redfox-security/digisol-dg-gr1321-s-password-storage-in-plaintext-cve-2024-4232
Proof-of-concept demonstrating plaintext password storage vulnerability in Digisol DG-GR1321 routers, enabling credential exposure and unauthorized…
 misakamikato/cve-2017-7921-golang
Hikvision IP camera access bypass exploit, developed by golang.
 hanianis/cve-2025-63353
A vulnerability in fiberhome GPON ONU HG6145F1 RP4423 allows the device's factory default Wi-Fi password (WPA/WPA2 pre-shared key) to be predicted…
 nanotrash/hikvision_brute
Brute Hikvision CAMS with CVE-2021-36260 Exploit
 kirubel-cve/cve-2025-65427
Proof-of-concept exploit for CVE-2025-65427: missing rate limiting on Dbit N300 T1 Pro router login API enabling brute-force attacks and…
 ezelf/cve-2018-9995_dvr_credentials
(CVE-2018-9995) Get DVR Credentials
 win3zz/cve-2023-43261
CVE-2023-43261 - Credential Leakage Through Unprotected System Logs and Weak Password Encryption
 wmasday/htc
Hack The CCTV | DVRs; Credentials Exposed | CVE-2018-9995
 lequockhanh2k/tool_exploit_password_camera_cve-2018-9995
Exploit tool for CVE-2018-9995 that extracts credentials from vulnerable DVR devices via Google dorking and direct IP access.
