Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
13 results
RemotePasswordWiFi preview

RemotePasswordWiFi

GitHubs0c5/remotepasswordwifi

Script in Ruby. Break Remote router wifi passwords.
exploitationinformation-gatheringpassword-attacks+2
14
9 years ago
CVE-2019-17525 preview

CVE-2019-17525

GitHubhuzaifahussain98/cve-2019-17525

D-LINK ROUTER "MODEL NO: DIR-615" with "FIRMWARE VERSION:20.10" & "HARDWARE VERSION:T1
captcha-bypassexploitationpassword-attacks+3
16 years ago
RomBuster preview

RomBuster

GitHubentysec/rombuster

RomBuster is a router exploitation tool that allows to disclosure network router admin password.
exploitationinformation-gatheringiot-security+1
5632 years ago
CVE-2020-29669 preview

CVE-2020-29669

GitHubs1lkys/cve-2020-29669

Macally WIFISD2

authentication-authorizationembedded-systems-securityexploitation+5
5 years ago
CVE-2018-18852 preview

CVE-2018-18852

GitHubhook-s3c/cve-2018-18852

Authenticated remote code execution exploit for CERIO routers (DT300N, DT100G, AMR-3204, WMR-200N) using vendor default credentials. Python PoC…

embedded-systems-securityexploitationiot-security+4
457 years ago
CVE-2020-35575-TP-LINK-TL-WR841ND-password-disclosure preview

CVE-2020-35575-TP-LINK-TL-WR841ND-password-disclosure

GitHubdylvie/cve-2020-35575-tp-link-tl-wr841nd-password-disclosure

Weaponized exploit script for CVE-2020-35575, a password-disclosure vulnerability in TP-Link router web interfaces, granting remote administrative…

embedded-systems-securityexploitationiot-security+3
21 year ago
CVE-2020-29669 preview

CVE-2020-29669

GitHubcode-byter/cve-2020-29669

Macally WIFISD2
embedded-systems-securityexploitationhardware-iot-security+5
25 years ago
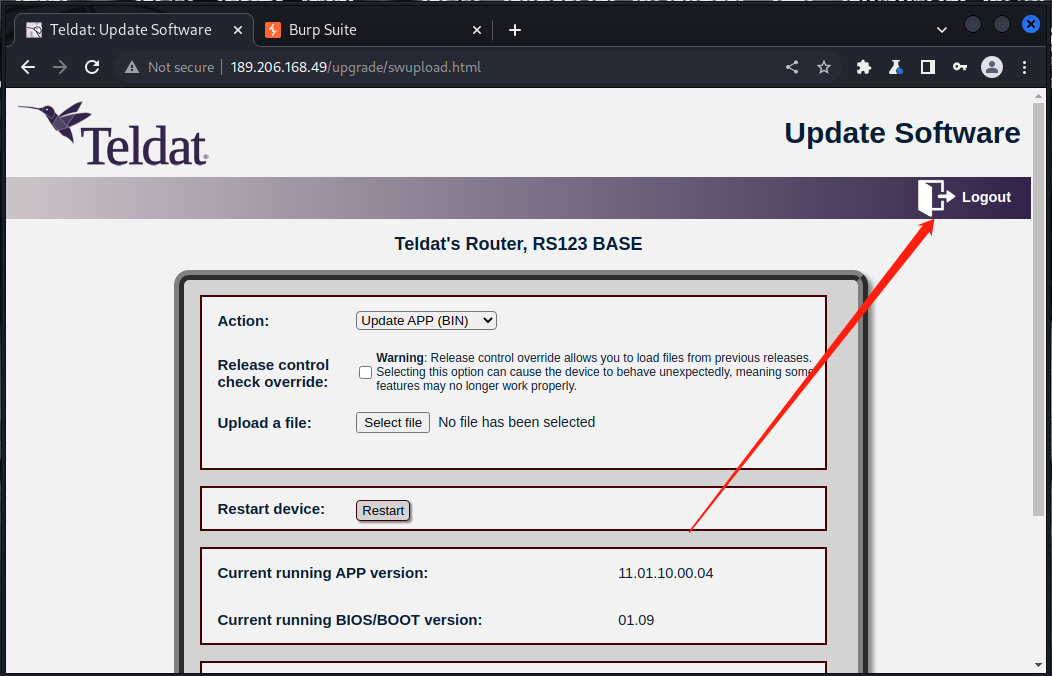
Teldat-Router-CVE-2022-POC preview

Teldat-Router-CVE-2022-POC

GitHubuyhacked/teldat-router-cve-2022-poc

POC for CVE-2022-39996 (Reflected XSS) and CVE-2022-39997 (Weak Password) in Teldat RS123/RS123w Router
educationexploitationpassword-attacks+3
3 months ago
Poc-CVE-2024-57040 preview

Poc-CVE-2024-57040

GitHubabsholi7ly/poc-cve-2024-57040

CVE-2024-57040 is a security vulnerability found in certain TP-Link TL-WR845N router models. Specifically, it involves a "hardcoded" password for the…
embedded-systems-securityexploitationhardware-iot-security+3
21 year ago
CVE-2025-63820 preview

CVE-2025-63820

GitHubxernary/cve-2025-63820

Proof-of-concept of vulnerability found in Totolink A720R router

embedded-systems-securityexploitationhardware-iot-security+3
10 months ago
TendaSpill preview

TendaSpill

GitHubshaheemirza/tendaspill

An exploitation tool to extract passwords using CVE-2015-5995.
educationexploitationpassword-attacks+3
107 years ago
CVE-2025-65427 preview

CVE-2025-65427

GitHubkirubel-cve/cve-2025-65427

Proof-of-concept exploit for CVE-2025-65427: missing rate limiting on Dbit N300 T1 Pro router login API enabling brute-force attacks and…
authenticationiot-securitypassword-attacks+3
9 months ago
CVE-2022-45599 preview

CVE-2022-45599

GitHubethancunt/cve-2022-45599

Proof-of-concept for CVE-2022-45599: PHP type juggling vulnerability in Aztech WMB250AC router login.php allowing admin authentication bypass via…

authenticationexploitationpassword-attacks+3
3 years ago