CVE-2020-25749
Proof-of-concept exploit for CVE-2020-25749 targeting Rubetek cameras with hardcoded Telnet credentials, enabling remote root shell access and full…

Proof-of-concept exploit for CVE-2020-25749 targeting Rubetek cameras with hardcoded Telnet credentials, enabling remote root shell access and full…

Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…

Supporting material for the "Hunting Bugs In The Tropics" DEFCON 30 talk

CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631

This repository holds interesting bits and pieces related to research I performed on wireless presentation devices manufactured by Awindinc and…

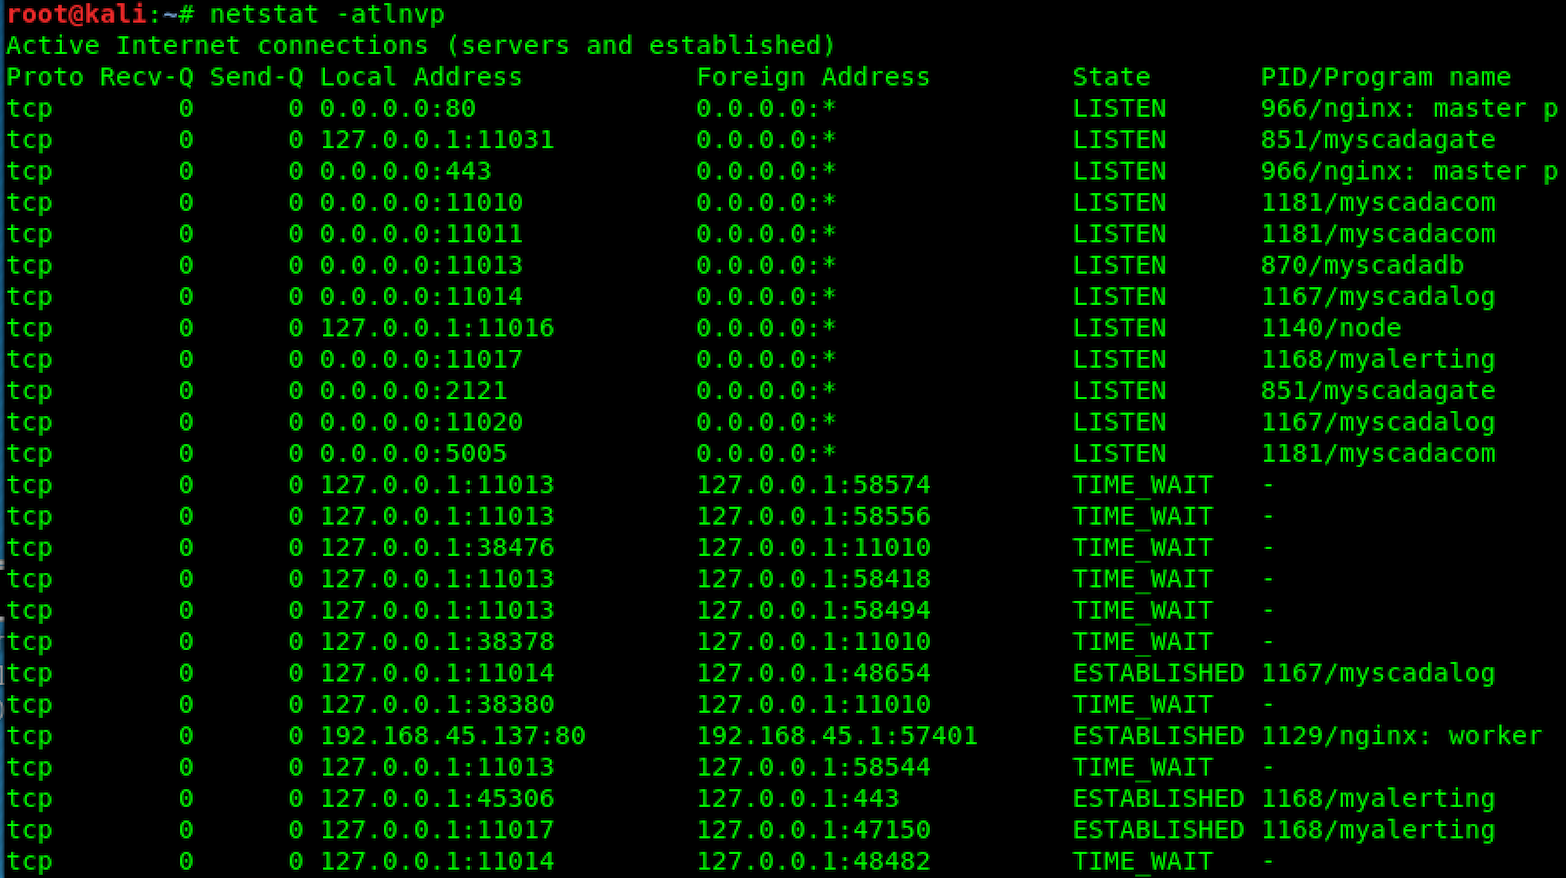
CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability

Exploit code for CVE-2023-28810

Exploit for CVE-2017-14262 targeting Samsung NVR devices: extracts admin MD5 password hash via unauthenticated CGI request and logs in with the hash…

This Tool Aims to Exploit the CVE-2018-13341

A key generator for Zyxel VMG8825-T50

Weaponized exploit script for CVE-2020-35575, a password-disclosure vulnerability in TP-Link router web interfaces, granting remote administrative…

Macally WIFISD2

It is the details of CVE-2025-45466

D-LINK Go-RT-AC750 GORTAC750_A1_FW_v101b03 has a hardcoded password for the Alphanetworks account, which allows remote attackers to obtain root…

Authenticated remote code execution exploit for CERIO routers (DT300N, DT100G, AMR-3204, WMR-200N) using vendor default credentials. Python PoC…

By the Way is an exploit that enables a root shell on Mikrotik devices running RouterOS versions:

Simulates a Matter commissioning code brute-force attack (CVE-2026-23005) using Python to demonstrate missing rate limiting and lockout on 8-digit…

Xiongmai XM530 IP Camera Hardcoded RTSP Credentials Exposure