

Overthrone
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
command-and-controlexploit-frameworksinformation-gathering+8
20
karmanya03/overthroneAll-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
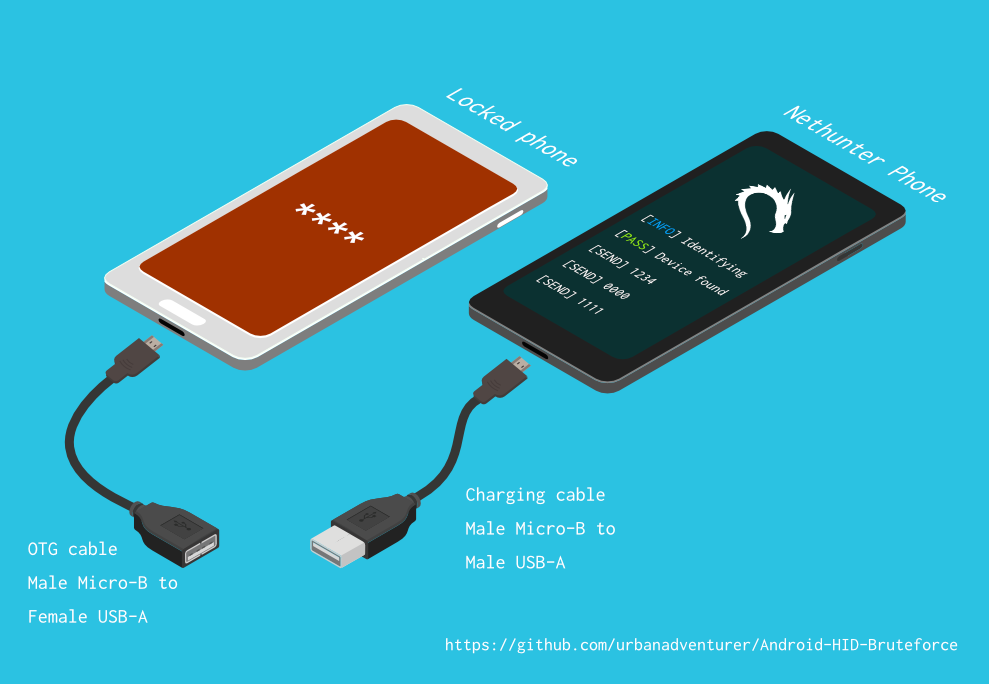 urbanadventurer/android-pin-bruteforce
Unlock an Android phone (or device) by bruteforcing the lockscreen PIN. Turn your Kali Nethunter phone into a bruteforce PIN cracker for Android…
 yogsec/hacking-tools
A curated list of penetration testing and ethical hacking tools, organized by category. This compilation includes tools from Kali Linux and other…
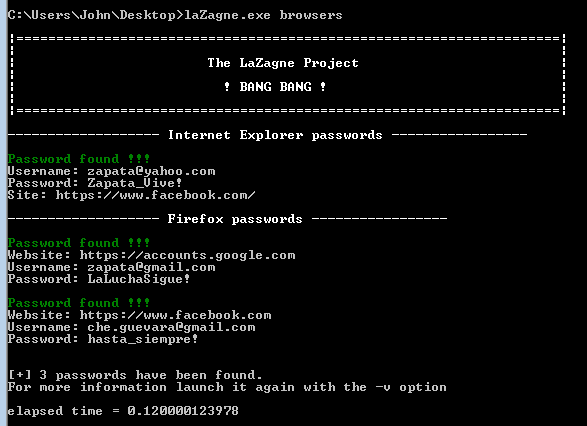 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
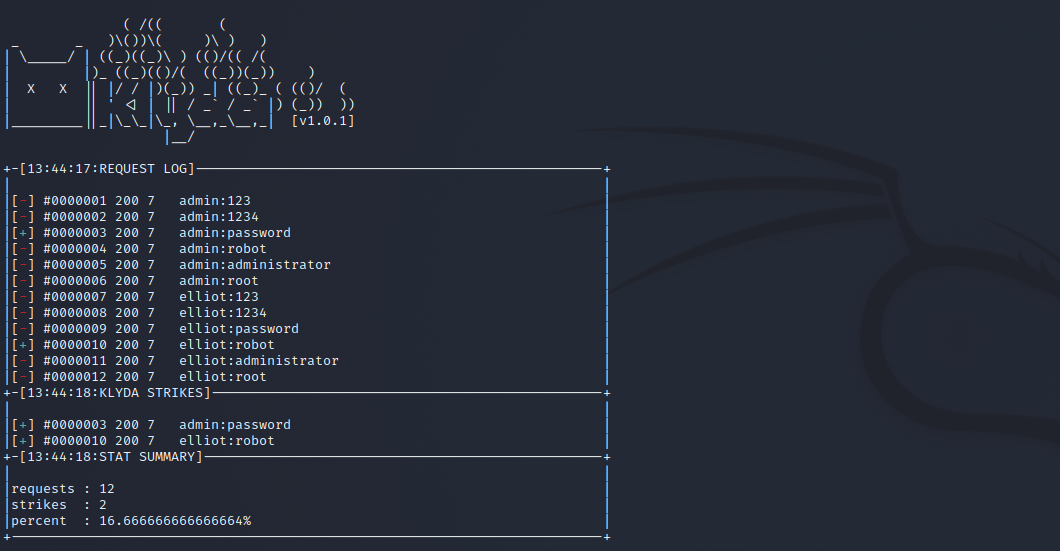 hcbaker/klyda
Highly configurable script for dictionary/spray attacks against online web applications.
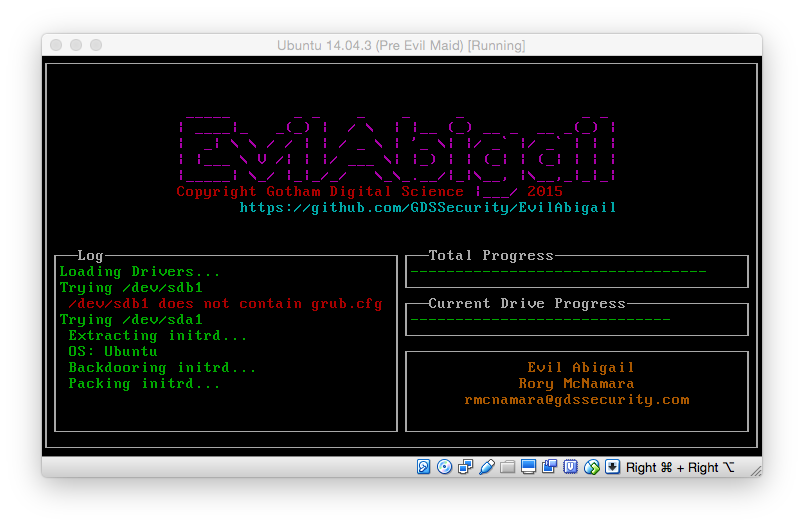 strozfriedberg/evilabigail
Automated Linux evil maid attack
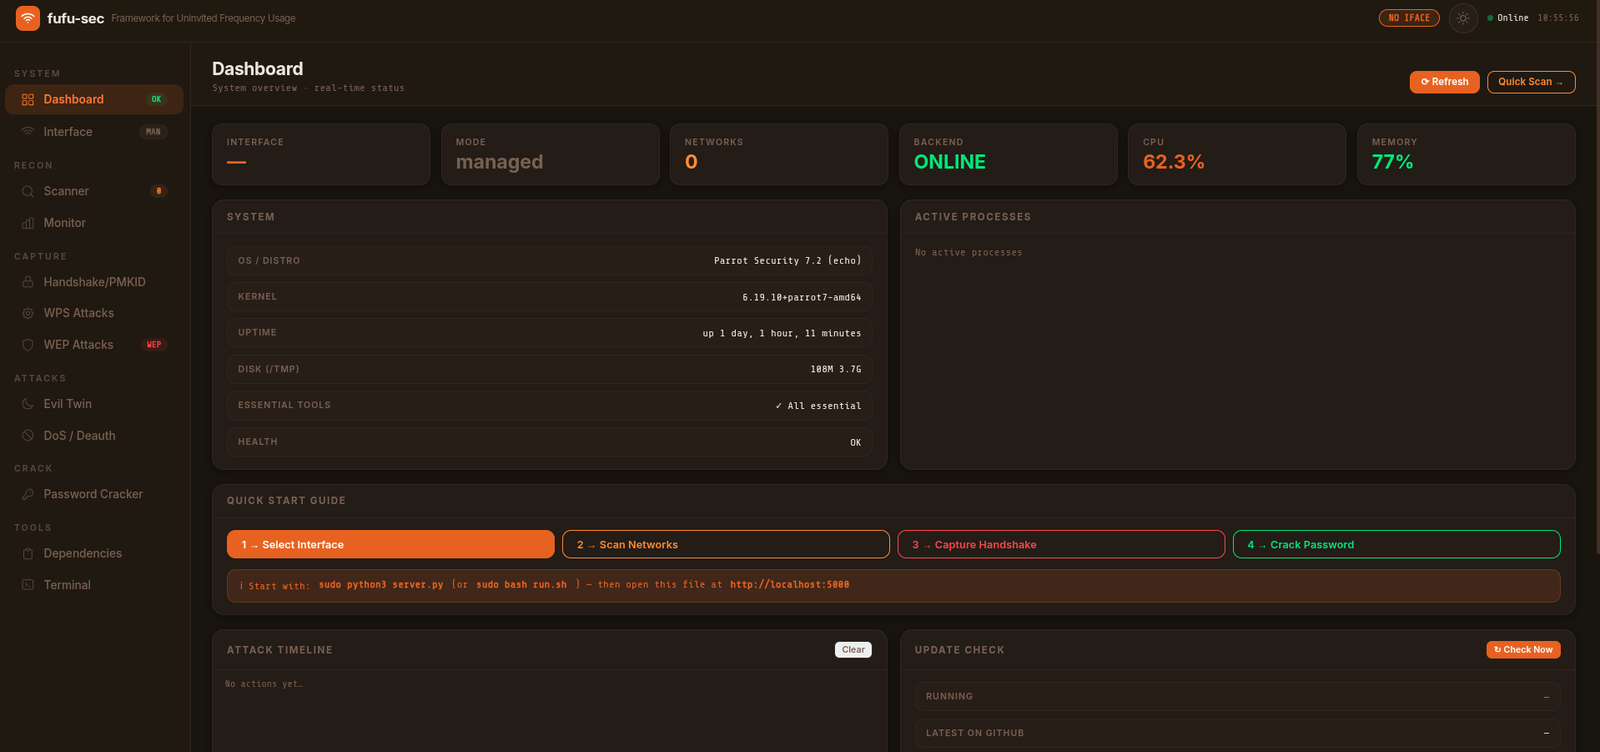 kyllr-qwen/fufu-sec
Framework for Uninvited Frequency Usage
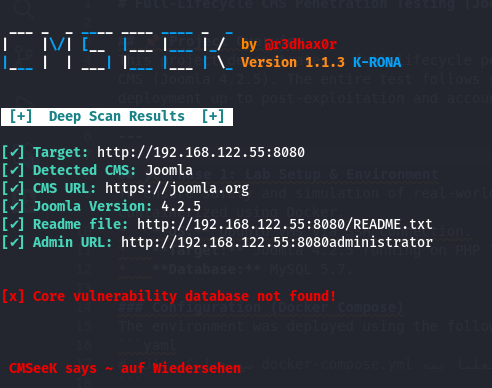 marwan651/joomla-cms-full-lifecycle-pentest
A comprehensive full-lifecycle penetration testing project on Joomla 4.2.5 exploiting CVE-2023-23752 inside a Dockerized lab environment
 skyler-ferrante/cve-2024-28085
WallEscape vulnerability in util-linux
 praetorian-inc/brutus
Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…
 aleksamcode/wifi-password-stealer
Simple Windows and Linux keystroke injection tool that exfiltrates stored WiFi data (SSID and password).
 cosmic-zip/witchcraft
WITCHCRAFT is a cyberdeck toolkit built for runners who dive deep into the mesh. It’s your all-in-one rig for data-ghosting, ICE-breaking, and…
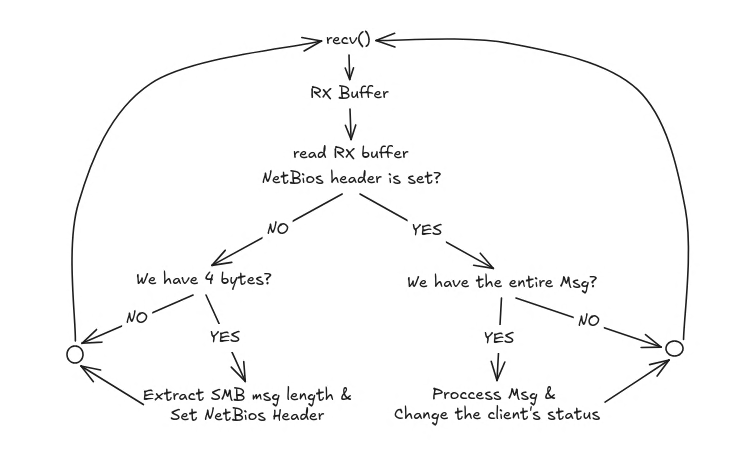 lcky00/impostor
SMB1 server for NTLMv2 hash interception, written in C.
 ihebski/defaultcreds-cheat-sheet
One place for all the default credentials to assist the Blue/Red teamers identifying devices with default password 🛡️
 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.