

PocketPentester
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
dns-analysisfuzzinghash-analysis+9
8
tegal1337/pocketpentesterOffline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 dev-2null/kerberosrun
A little tool to play with Kerberos.
 strozfriedberg/evilabigail
Automated Linux evil maid attack
 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…
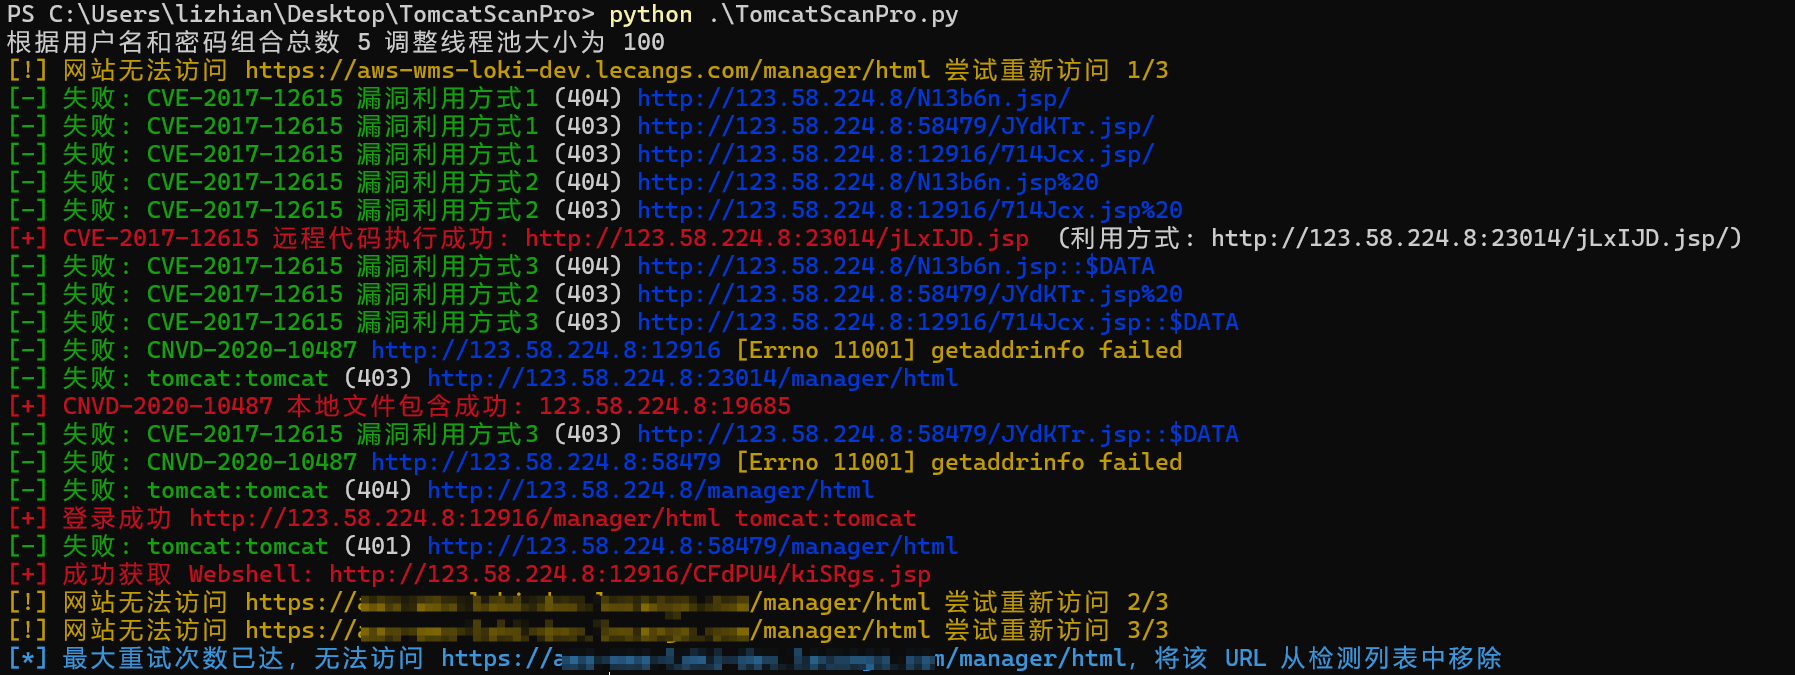 lizhianyuguangming/tomcatscanpro
tomcat自动化漏洞扫描利用工具,支持批量弱口令检测、后台部署war包getshell、CVE-2017-12615 文件上传、CVE-2020-1938/CNVD-2020-10487 文件包含
 affolter-engineering/mqattack
Rust CLI for MQTT penetration testing: subscribe/publish, broker fingerprinting, ACL probing, topic enumeration, credential brute-force, and Last…
 trackflaw/cve-2023-23397
Simple PoC of the CVE-2023-23397 vulnerability with the payload sent by email.
 entysec/rombuster
RomBuster is a router exploitation tool that allows to disclosure network router admin password.
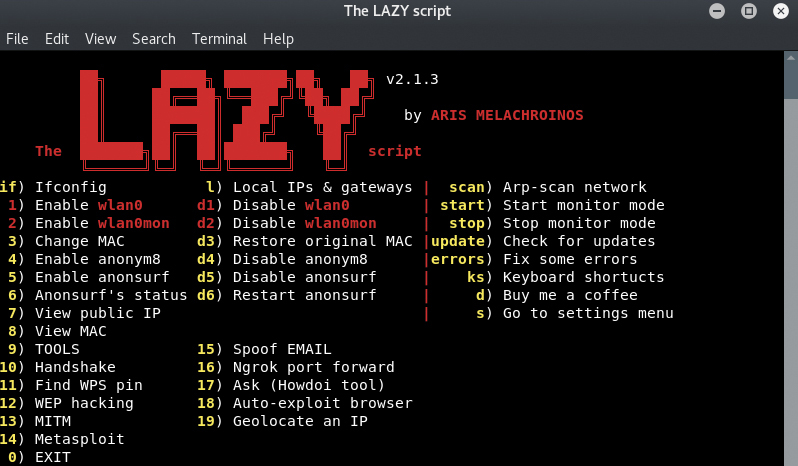 arismelachroinos/lscript
The LAZY script will make your life easier, and of course faster.
 fl0ydsec/cve-2026-63030
Python mass exploit and detector for the WordPress Core pre-auth RCE chain CVE-2026-63030 and CVE-2026-60137, chaining SQL injection into remote code…
 cyberstruggle/chalumeau
Chalumeau is automated,extendable and customizable credential dumping tool based on powershell and python.
 adepts-of-0xcc/vba-macro-experiments
Collection of VBA macro published in our twitter / blog
 bronzebee/cve-2023-23397
Python script for sending e-mails with CVE-2023-23397 payload using SMTP
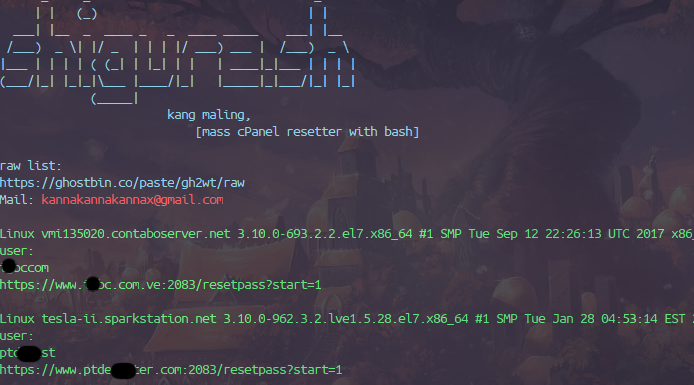 redsplit/shiguresh
CVE-2004-1769 // Mass cPanel Reset password
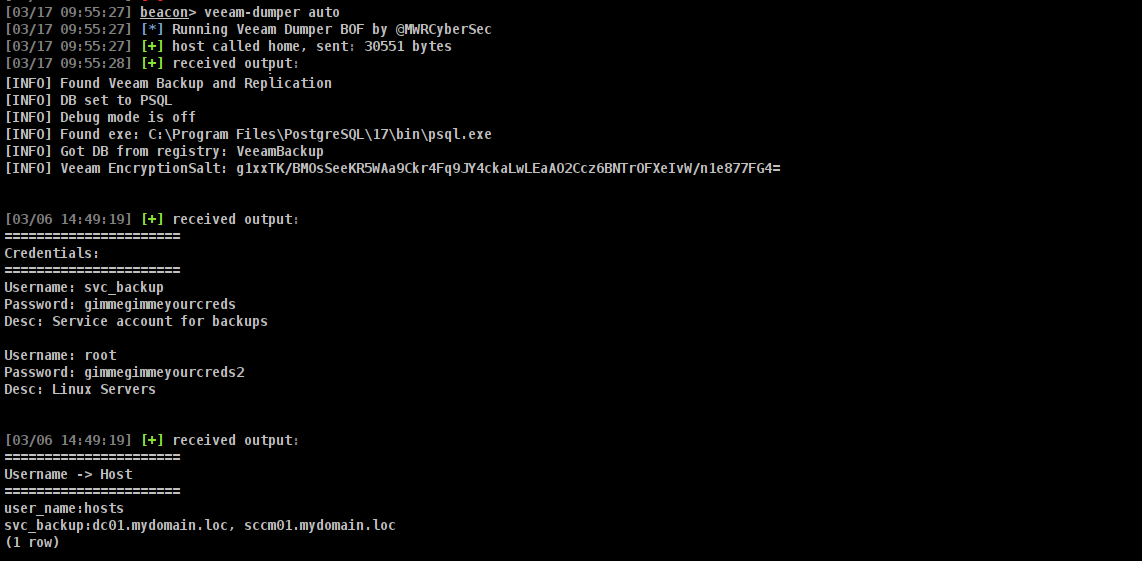 mwr-cybersec/veeamdumper-bof
A credential extraction BOF for Veeam Backup and Replication and Veeam One
 d3vn0mi/cve-2016-16113-poc
cve-2016-16113
 brav0hax/smbexec
Rapid psexec-style attack tool using Samba for remote command execution, credential dumping, and lateral movement across Windows networks with hash…