

CVE-2018-12533
 llamaonsecurity/cve-2018-12533
Payload generator and proof-of-concept exploit for CVE-2018-12533 (Richfaces deserialization/EL injection) with Docker-based vulnerable environment…
exploitationlabs-practicepapers-research+3
9
llamaonsecurity/cve-2018-12533Payload generator and proof-of-concept exploit for CVE-2018-12533 (Richfaces deserialization/EL injection) with Docker-based vulnerable environment…
 i3it/cve-2026-18322
Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…
 abraxas/cve-2026-19952
Proof-of-concept and disclosure pack for CVE-2026-19952, an unauthenticated arbitrary file deletion in the WordPress Frontend Admin plugin, with lab…
 mlily2024/final-project-sql-injection-pipeline
Hybrid machine-learning pipelines for detecting SQL injection in web traffic, combining DistilBERT and BERT-GNN models with adversarial training and…
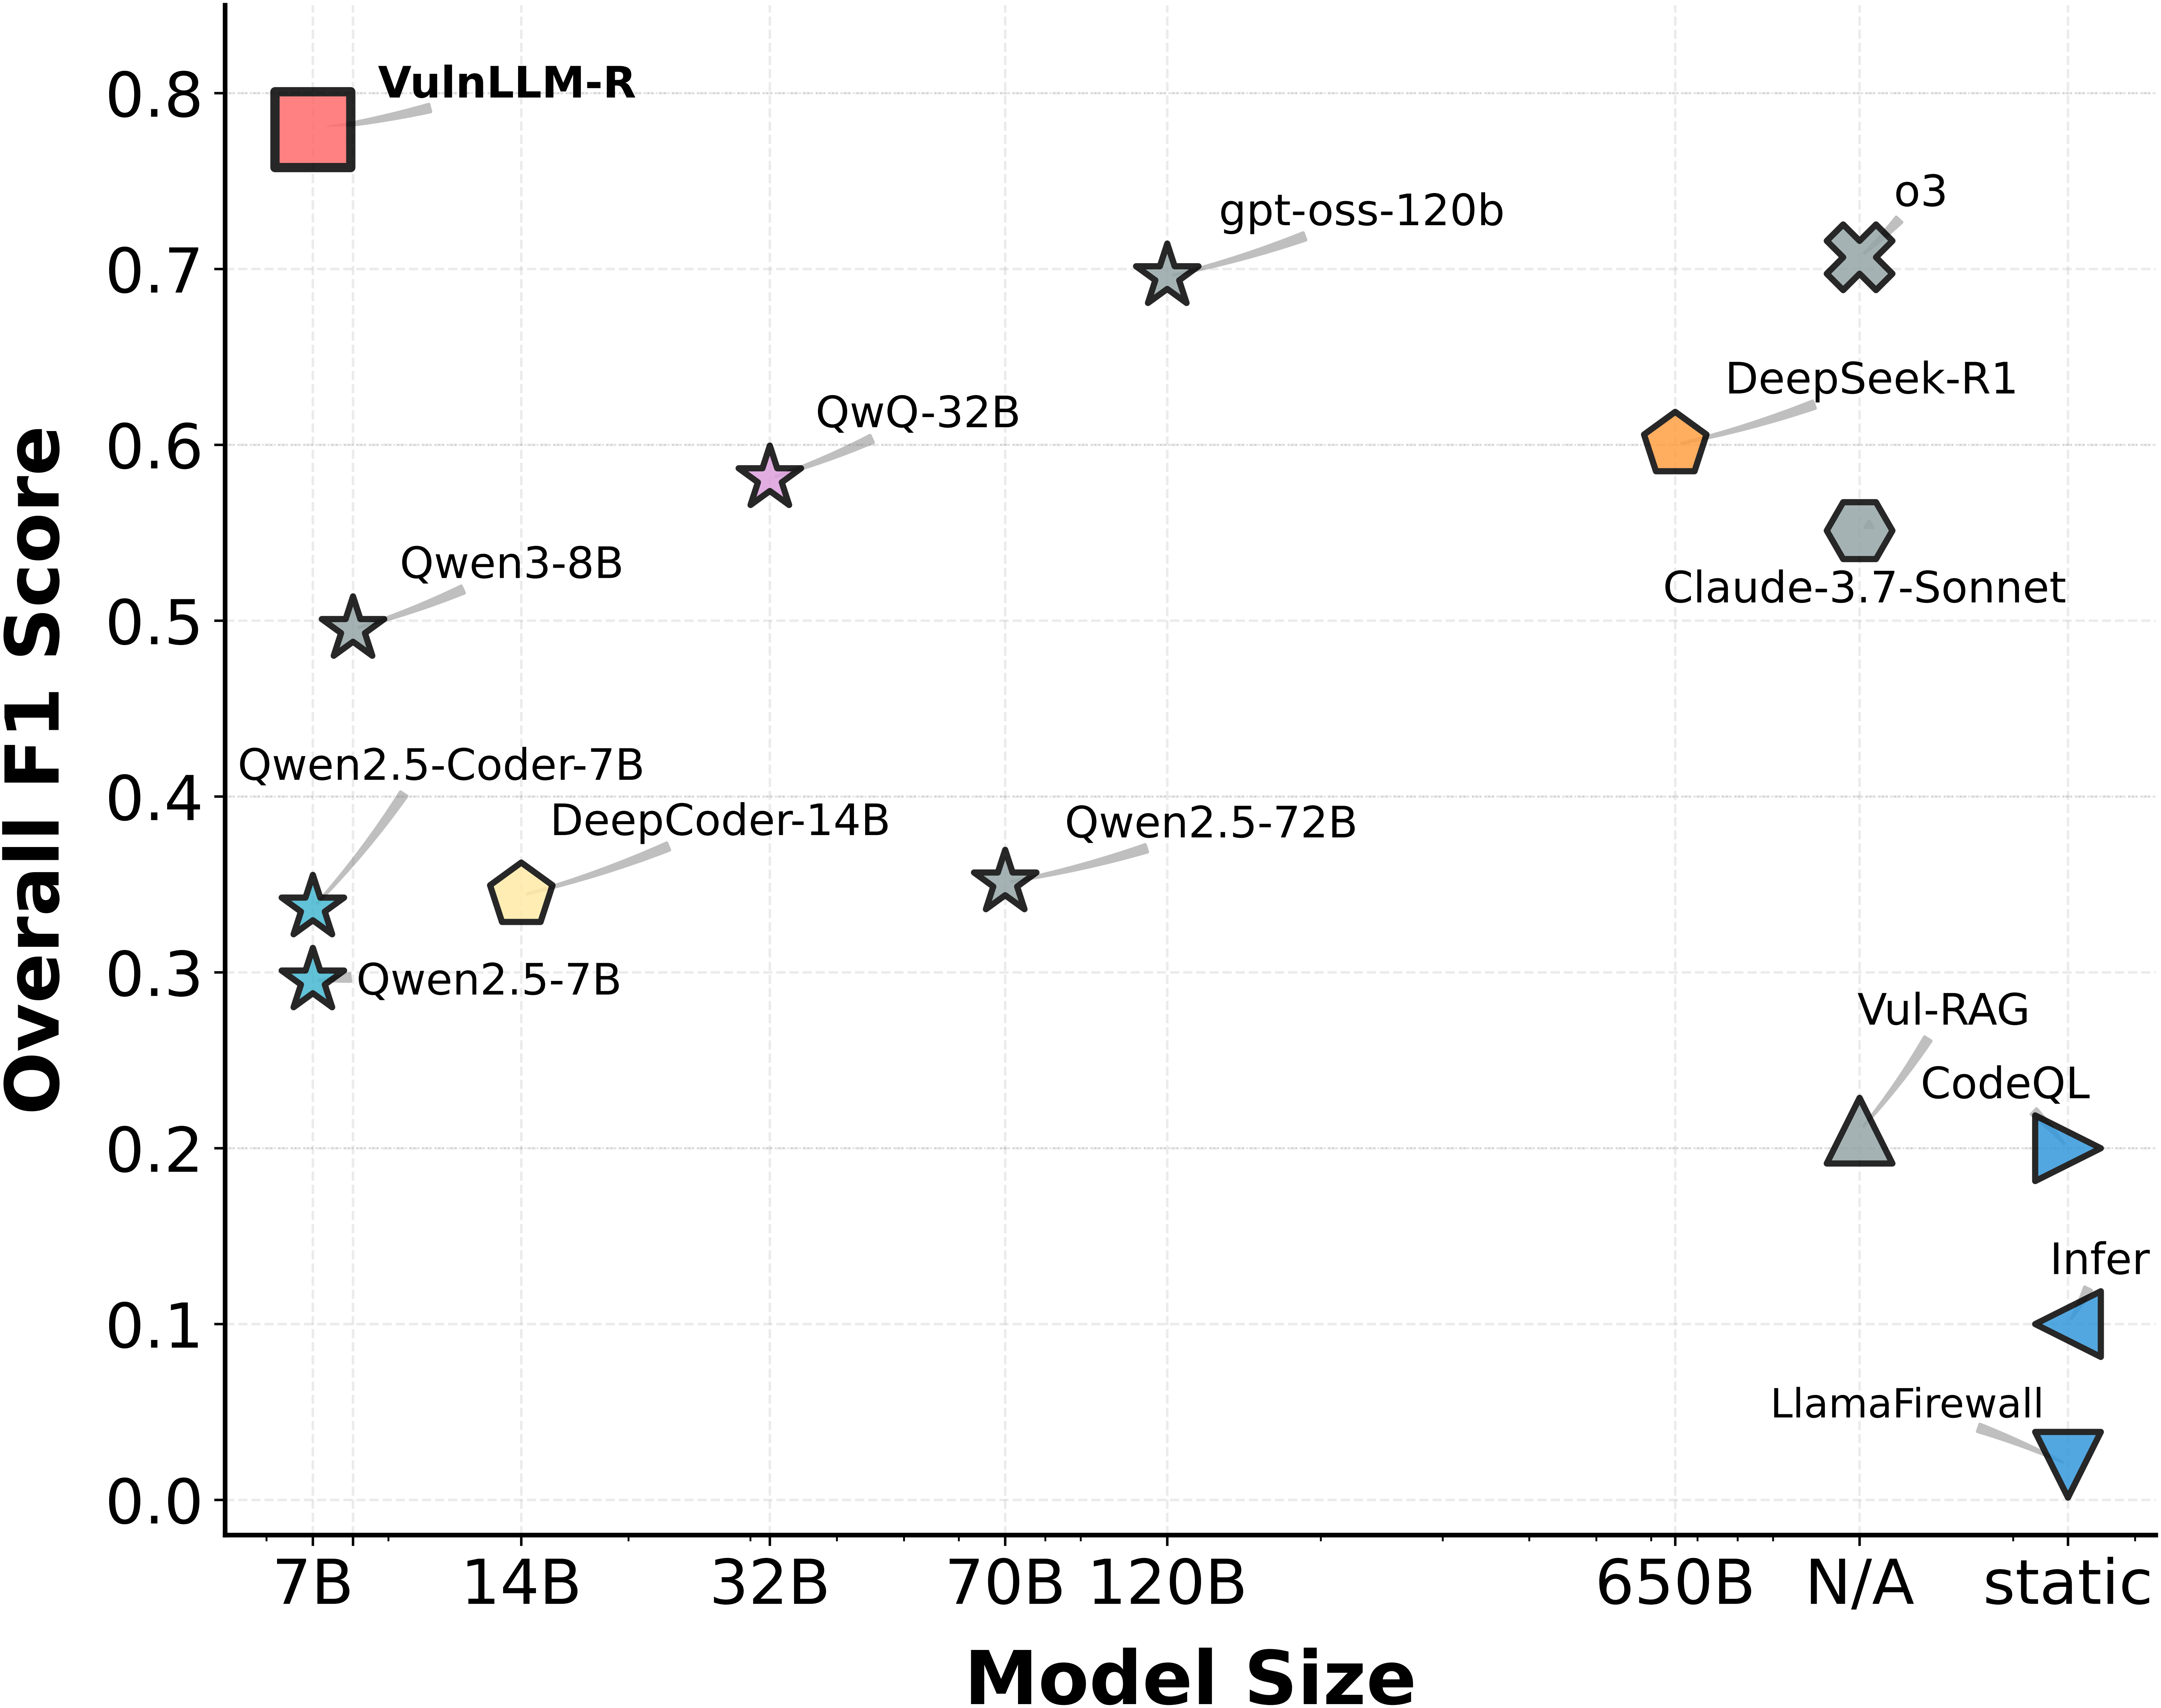 ucsb-mlsec/vulnllm-r
Specialized reasoning LLM for source-code vulnerability detection in C/C++ and Python, with dataset construction, SFT/DPO training, and…
 sparshbiswas-ai/cve-2026-0596-reproduction
Research environment and validation scripts for evaluating deserialization behaviors in MLflow and MLServer.
 ztcoalson/if-guide
[NeurIPS '25] Code for Paper "IF-Guide: Influence Function-Guided Suppression of Harmful Training Data for Reducing LLM Toxicity"
 yeasen-z/leakgauge
Detects LLM context-leakage attacks by training lightweight behavior probes on log-probabilities, with vLLM offline/server detection pipelines.
 jianshuod/ipi-exposure-signal
Research pipeline for detecting latent indirect prompt-injection exposure signals in agentic LLMs via hidden-state probing, including trace…
 m1nggod/cve-2021-44228-log4j-lookup-rce
Detailed analysis and proof-of-concept for CVE-2021-44228 (Log4j RCE), including environment setup, vulnerability analysis, JNDI injection mechanism,…
 kmeps4/cverev3
Proof-of-concept testing environment for CVE-2021-30858, based on Google Project Zero's root cause analysis of an in-the-wild iOS exploit.
 religan/cve-2023-20198
A cybersecurity case study analysing CVE-2023-20198 in Cisco IOS XE, covering vulnerability exploitation, mitigation strategies, secure software…
 saitamang/cve-2021-35475
Writeup for CVE-2021-35475; Stored Cross-Site Scripting(XSS) on SAS® Environment Manager 2.5
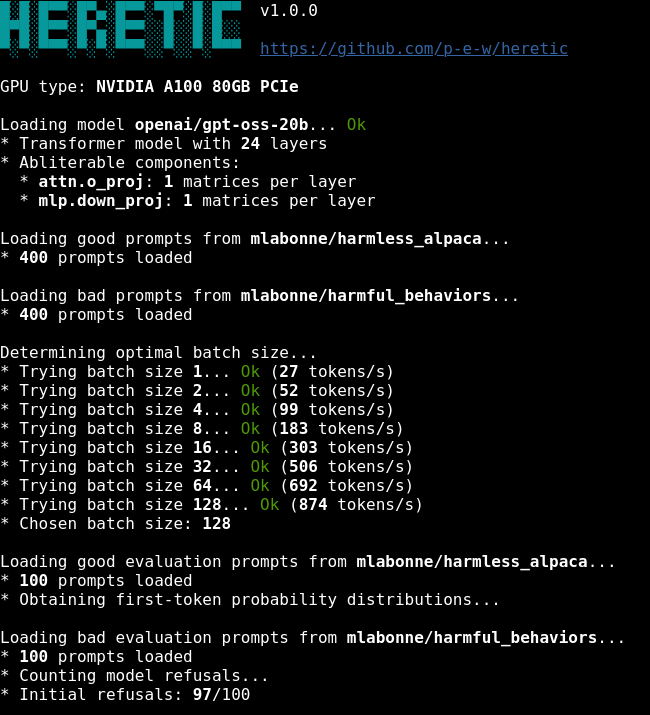 p-e-w/heretic
Fully automatic censorship removal for language models
 enovella/tee-reversing
A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 alixiacf/hpim-training-lab
Trained to Escalate: Forensic Analysis and Local Replication of RLHF-Induced Privilege Escalation in AI Agents (CVE-2026-65616)
 themehackers/cve-2026-34038
CVE-2026-34038: Authenticated Remote Command Injection in Coolify