

CVE-2023-42222
 itssixtyn3in/cve-2023-42222
Proof-of-concept exploit for CVE-2023-42222 in WebCatalog, demonstrating arbitrary URL execution via Electron's shell.openExternal to bypass security…
educationexploitationpapers-research+2
3
itssixtyn3in/cve-2023-42222Proof-of-concept exploit for CVE-2023-42222 in WebCatalog, demonstrating arbitrary URL execution via Electron's shell.openExternal to bypass security…
 bombobombone/cve-2026-103584
Sanitized report and loopback-only PoC script for CVE-2026-103584, a javascript: URL scheme XSS in MediaWiki CommonsMetadata LicenseUrl rendering.
 h4r335hr/cve-2023-24329-poc
Proof-of-concept exploit for CVE-2023-24329, a Python urllib parsing flaw enabling URL confusion attacks. Includes a runnable script and references…
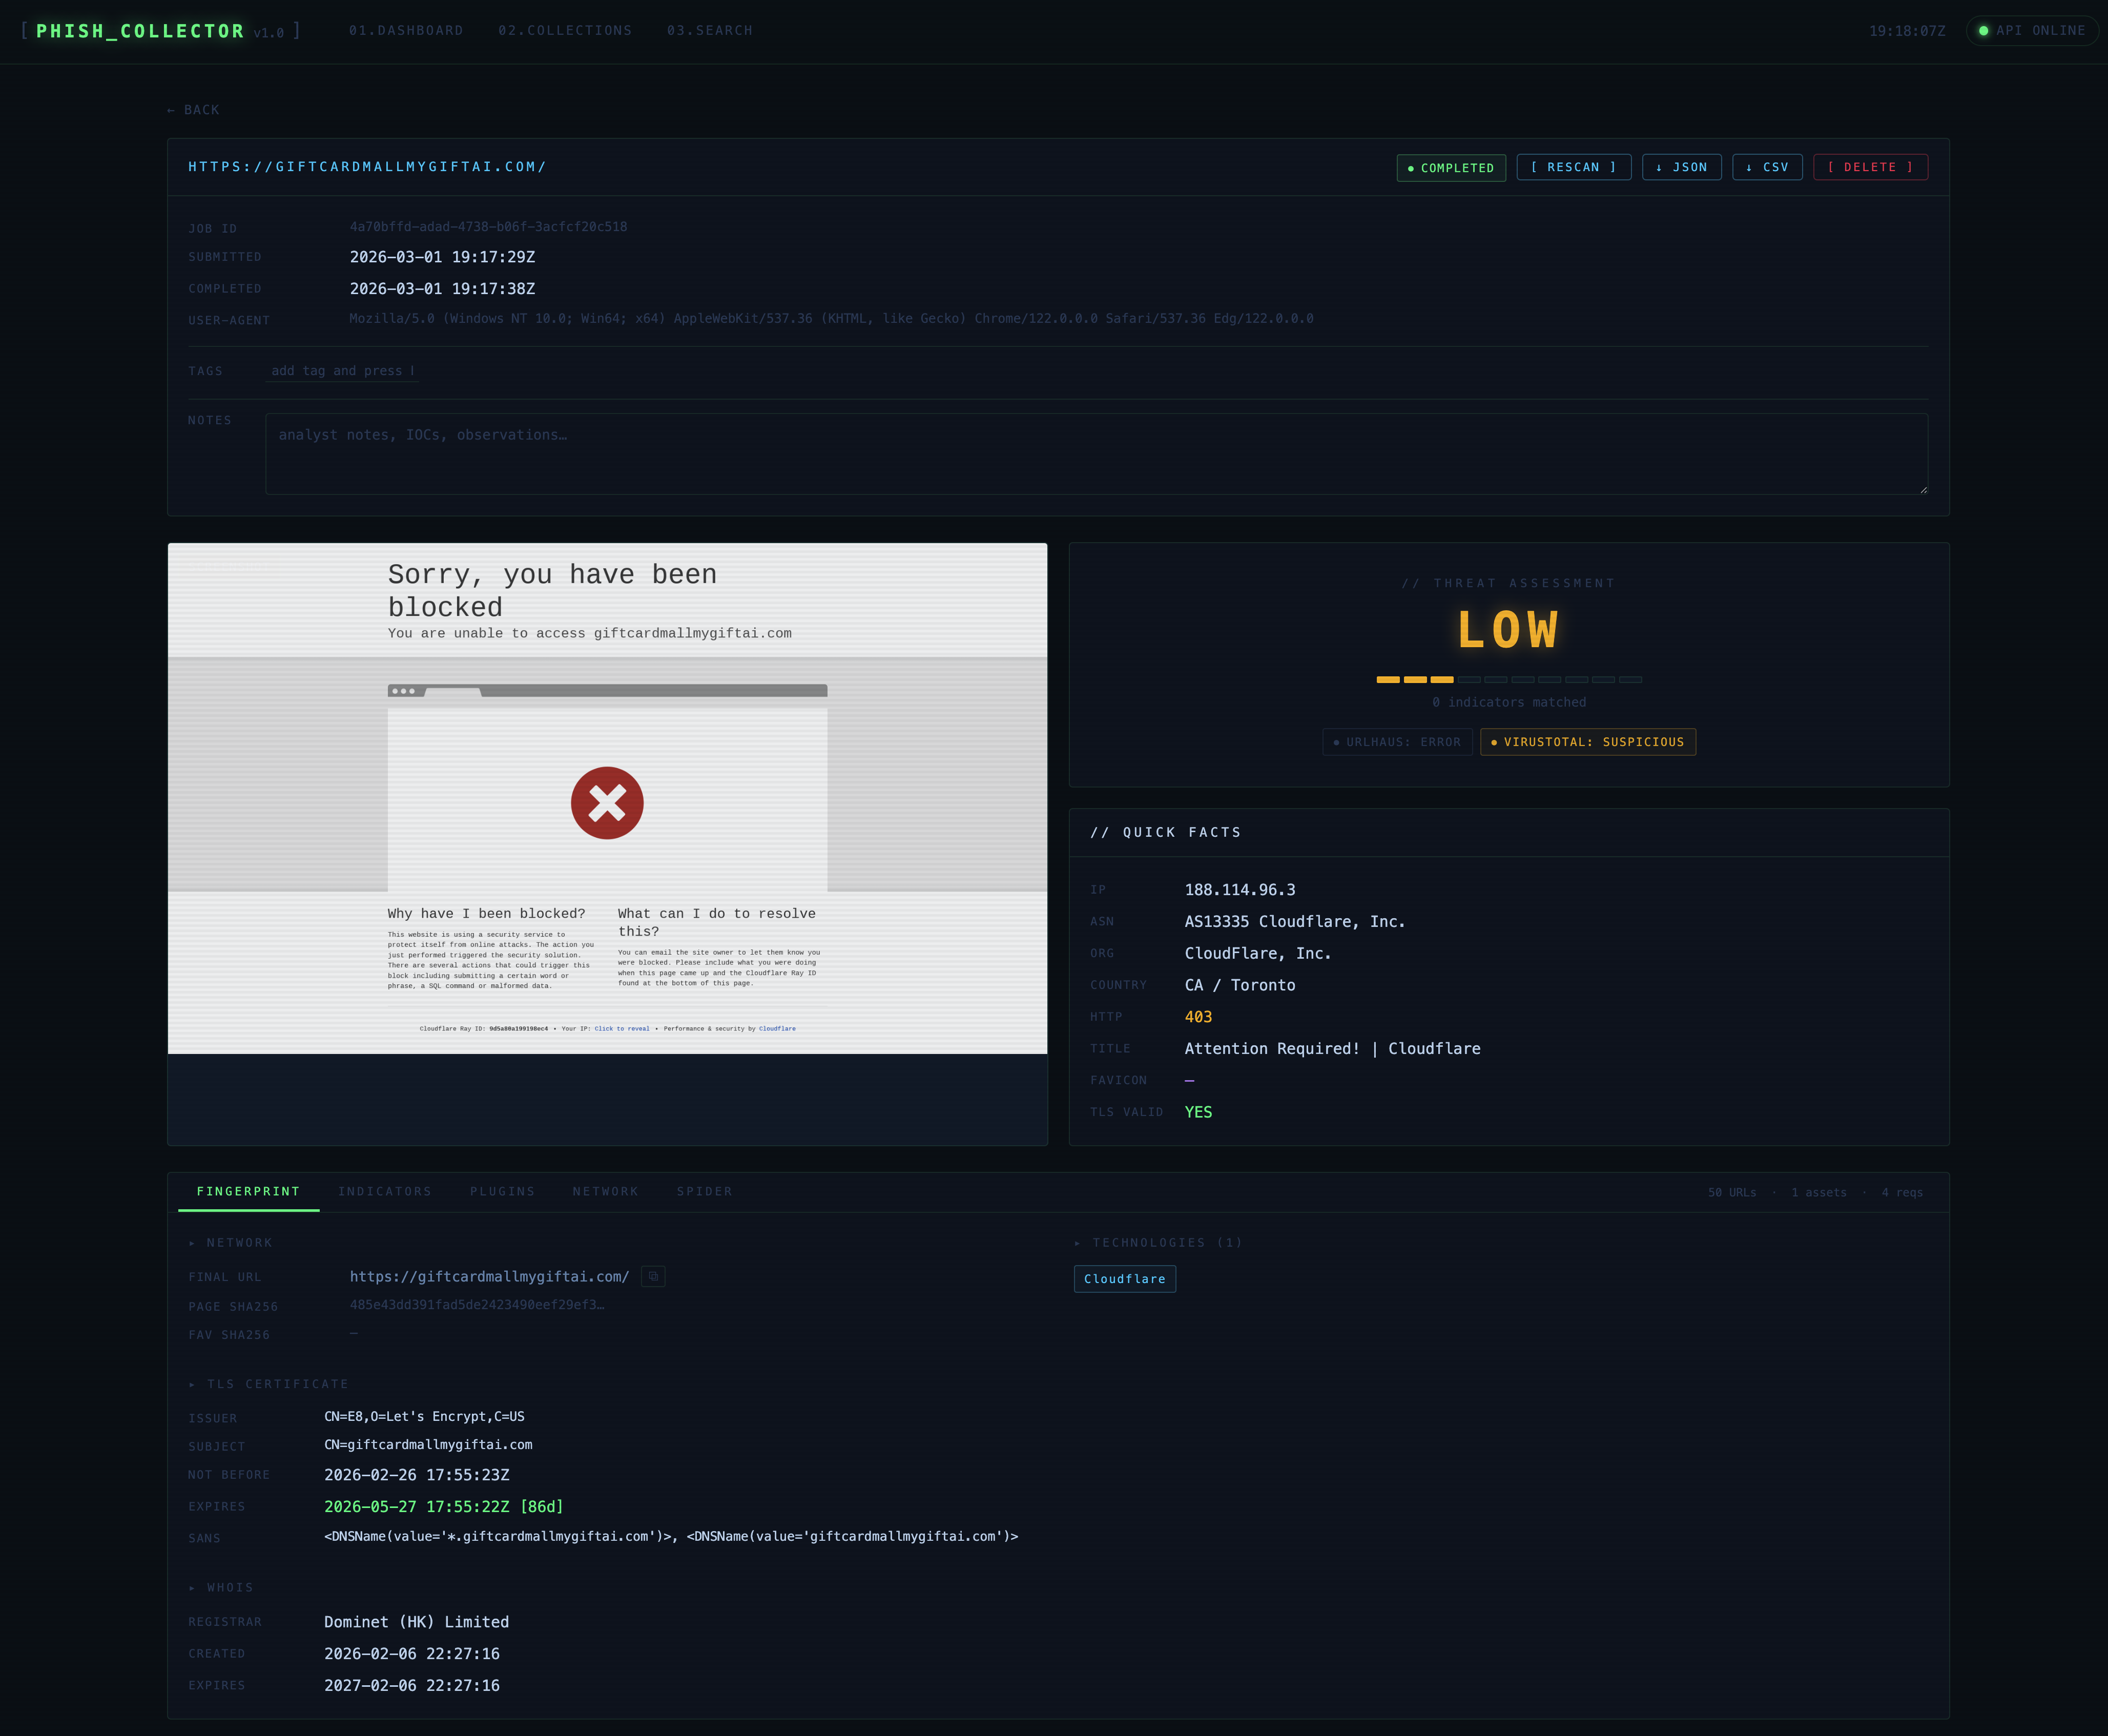 olizimmermann/phishcollector
PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.
 babydessy/cve-2024-27564
Proof-of-concept for CVE-2024-27564, an unauthenticated SSRF in pictureproxy.php via the url parameter, with vulnerable code, curl PoC, and…
 dotadrien/cve-2025-60656
Stored XSS vulnerability proof-of-concept for Script Pag's 'Recent Ads' module, exploiting unsanitized double quotes in image URL fields to execute…
 gal-nagli/cve-2021-26832
Cross Site Scripting (XSS) at the "Reset Password" page form of Priority Enterprise Management System v8.00 allows attackers to execute javascript on…
 theopaid/cve-2026-66754-remote-denial-of-service-via-reachable-assertion-in-url-prefix-handling-rouille-
Security Advisory: Remote Denial of Service via Reachable Assertion in URL Prefix Handling (rouille)
 0xmrma/cve-2026-34212
Docmost accepted a javascript: URL inside an attachment node, preserved it through storage and rendering, and turned it back into a clickable anchor…
 heshi906/cve-2024-28515
Documentation of CVE-2024-28515, a buffer overflow vulnerability in CSAPP Lab3 (buflab-update.pl), enabling remote code execution via crafted URL…
 brandon-t-elliott/cve-2023-49438
CVE-2023-49438 - Open Redirect Vulnerability in Flask-Security-Too
 theopaid/cve-2026-67184-unauthenticated-null-pointer-dereference-crashes-the-server-tinyweb-
Security Advisory: Unauthenticated NULL Pointer Dereference Crashes the Server (TinyWeb)
 skotizo/cve-2021-43129
Vulnerability in D2L Brightspace's Learning Management System(LMS)
 helloandrewpaul/reflected-xss-in-vvveb-cms-v1.0.7.2
CVE-2025-9728: Reflected XSS in Login Form (Email & Password Fields) Vvveb CMS v1.0.7.2