
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
10 results
CVE-2025-67511 preview

CVE-2025-67511

GitHubedoardottt/cve-2025-67511

Detailed disclosure of CVE-2025-67511, a command injection vulnerability in the CAI framework's SSH tool that allows AI agents to be tricked into…
ai-securitycommand-and-controleducation+5
6
3 months ago
TP-Link-TL-WR820N-CVE-2025-14175 preview

TP-Link-TL-WR820N-CVE-2025-14175

GitHubcybervinner/tp-link-tl-wr820n-cve-2025-14175

Responsible disclosure write-up for CVE-2025-14175 involving weak cryptographic algorithm support in the SSH server of TP-Link TL-WR820N.
cryptographyeducationembedded-systems-security+3
8 months ago
sshamble preview

sshamble

GitHubrunzeroinc/sshamble

Research tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.
authenticationdefensive-toolsinformation-gathering+6
1.2k7 days ago
CVE-2024-3094 preview

CVE-2024-3094

GitHubmrk336/cve-2024-3094

CVE-2024-3094 exposed a backdoor in the XZ compression library, allowing remote SSH access by bypassing authentication. It’s a major supply chain…

curated-resourceseducationmalware-analysis+3
11 year ago
Termix-research preview

Termix-research

GitHubgabrielha12/termix-research

CVE-2026-45746, CVE-2026-45750, CVE-2026-53547 — three critical vulnerabilities in Termix: cross-tenant session hijacking, OS command injection, and…
exploitationpapers-researchprivilege-escalation+2
21 month ago
ifuncd-up preview

ifuncd-up

GitHubrobertdfrench/ifuncd-up

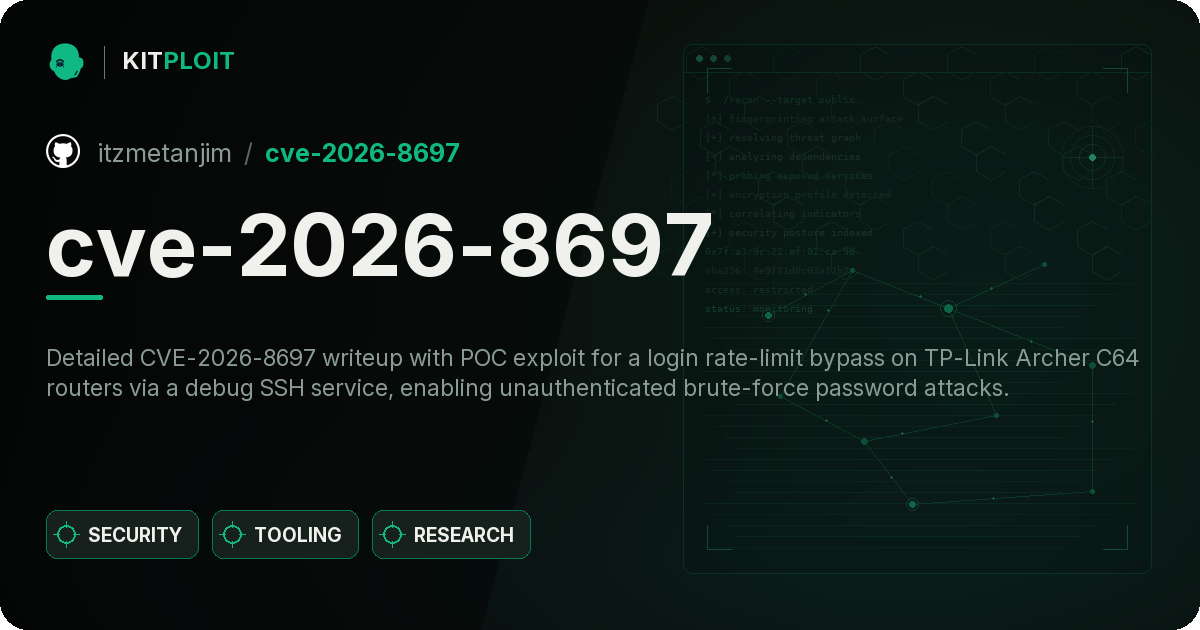
GNU IFUNC is the real culprit behind CVE-2024-3094
binary-analysisdynamic-code-analysiseducation+5
604 months ago
cve-2026-8697 preview

cve-2026-8697

GitHubitzmetanjim/cve-2026-8697

Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…
educationexploitationhardware-iot-security+7
13 months ago
ssh-honeypot-research preview

ssh-honeypot-research

GitHubliranzoz/ssh-honeypot-research

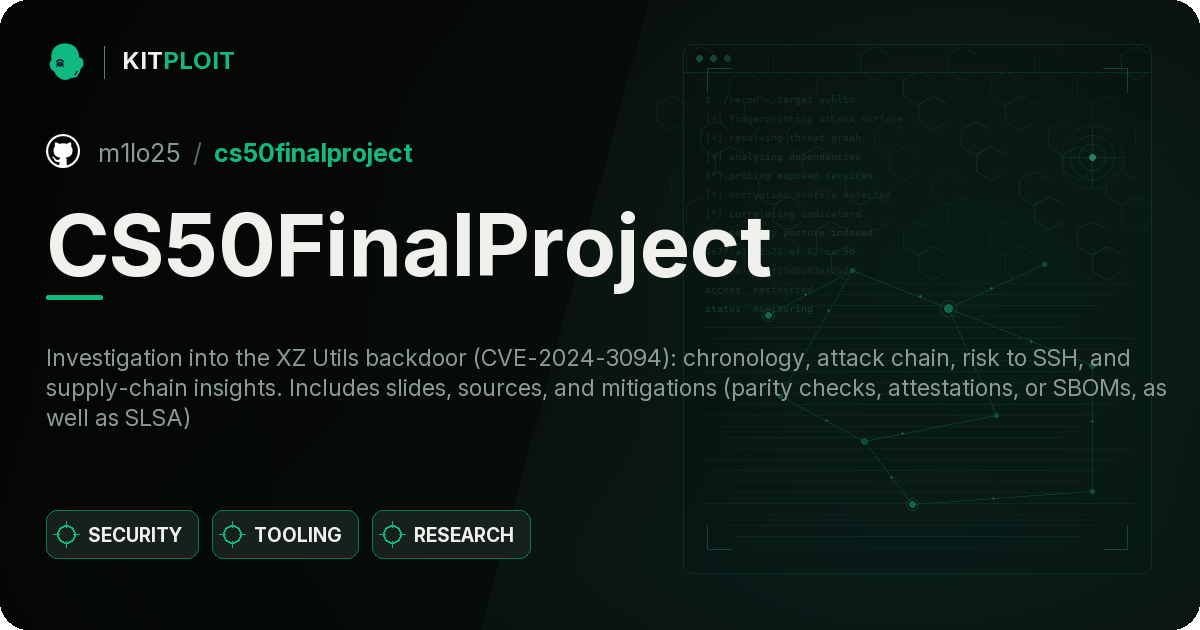
Medium-interaction SSH honeypot deployment capturing real-world brute-force traffic, malware drops, and attacker behavior. Includes TTY session…
digital-forensicseducationincident-response+4
14 months ago
CS50FinalProject preview

CS50FinalProject

GitHubm1lo25/cs50finalproject

Investigation into the XZ Utils backdoor (CVE-2024-3094): chronology, attack chain, risk to SSH, and supply-chain insights. Includes slides, sources,…
curated-resourceseducationincident-response+3
111 months ago
ssh-enum preview

ssh-enum

GitHubalisha-chaudhary/ssh-enum

This project explores whether modern OpenSSH reveals valid usernames through subtle response or timing differences. CVE-2016-6210 user enumeration…

educationinformation-gatheringlog-analysis+4
2 months ago