
sqlancer
 sqlancer/sqlancer
Automated testing to find logic and performance bugs in database systems
database-securityeducationfuzzing+2
sqlancer/sqlancerAutomated testing to find logic and performance bugs in database systems
 sudo-sakib/cve-2025-25964
A critical SQL Injection vulnerability (CVE-2025-25964) discovered in the School Information Management System v1.0
 l0lsec/cve-2021-3262
CVE-2021-3262 - Blind SQL Injection in the editOEN parameter of TripSpark VEO Transportation / NovusEDU. Unauthenticated, internet-facing. Payloads,…
 mbanyamer/cve-2025-67644-langgraph-3.0.1-sqlite-checkpoint-sql-injection
Proof-of-concept exploit for CVE-2025-67644, a SQL injection vulnerability in LangGraph SQLite Checkpoint. Demonstrates arbitrary SQL injection via…
 open-flaw/cve-2022-33171
CVE-2022-33171: TypeORM SQL Injection Vulnerability
 tubaaiftikhar-ui/moveit-transfer-data-breach-analysis.
Detailed analysis of the 2023 MOVEit Transfer data breach (CVE-2023-34362) for CS50 Cybersecurity. This project explores the technical impact of…
 mobilehackinglab/cve-2026-28576-poc
Educational proof-of-concept demonstrating a SQL injection vulnerability in Android 17's Contacts Provider, allowing a zero-permission app to…
 buraksevben/cves
Curated collection of proof-of-concept exploits for web vulnerabilities including cross-site scripting and SQL injection, with detailed technical…
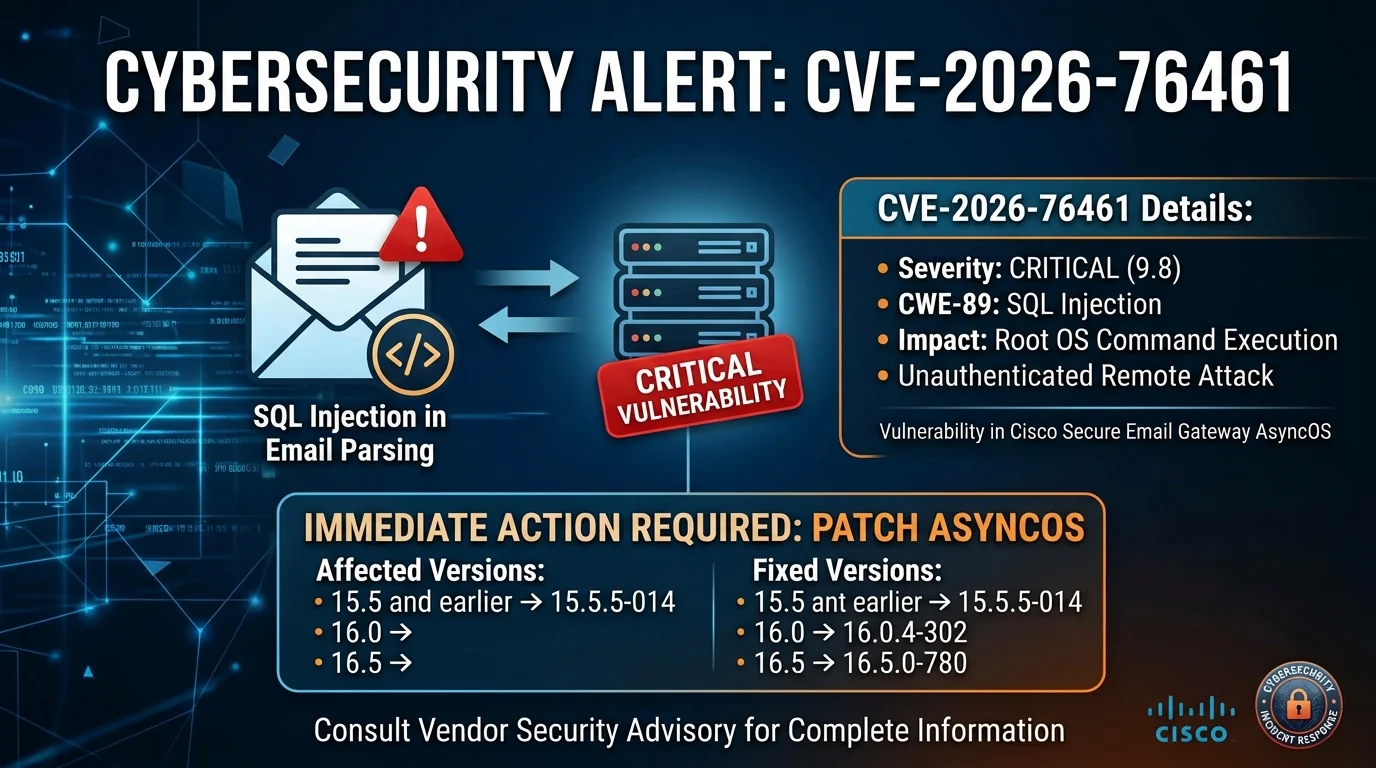 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 flx-0x00/cve-2026-59550
Unauthenticated time-based blind SQL injection PoC for AWP Classifieds <= 4.4.7, with a Docker lab, full writeup, and patch diff.
 xs2024770/cve-2024-57521-ruoyi-sqli
Static code audit of CVE-2024-57521, an authenticated SQL injection in RuoYi-Vue's generator module, with source-to-sink analysis and a %0b filter…
 ambionics/spip-exploits
Python exploit chain for SPIP CVEs 2026-72708/72709/72710, chaining unauthenticated SQL injection to account takeover and remote code execution.
 avergnaud/flight-sql-jdbc-driver-cve-2026-54512
Repository referencing CVE-2026-54512 in the Flight SQL JDBC driver, likely containing vulnerability details or proof-of-concept material.
 bx33661/cve-2025-7461
Detailed analysis of CVE-2025-7461, a SQL injection vulnerability in Modern Bag E-commerce System, including root cause, affected code, and…
 sw0rd1ight/cve-2026-1207
Django 框架在使用 PostGIS 查询地理栅格(raster)数据时,若将未经验证的用户输入直接作为 band index(波段索引)参数,会引发 SQL 注入
 oscerd/cve-2026-63039
Proof-of-concept for CVE-2026-63039, demonstrating ORDER BY SQL injection in Apache InLong's AuditAlertRule via orderField/orderType, with a…
 bytepro-ai/bitcoder-v2-research
Research repository documenting LLM generalization ceilings in code security vulnerability detection, with cross-evaluation across synthetic and…