
Argus
 purs3lab/argus
Staged static taint analysis framework for GitHub Actions workflows. Detects code injection vulnerabilities using taint-tracking and an impact…
code-analysisdevsecopseducation+4
562 years ago
purs3lab/argusStaged static taint analysis framework for GitHub Actions workflows. Detects code injection vulnerabilities using taint-tracking and an impact…
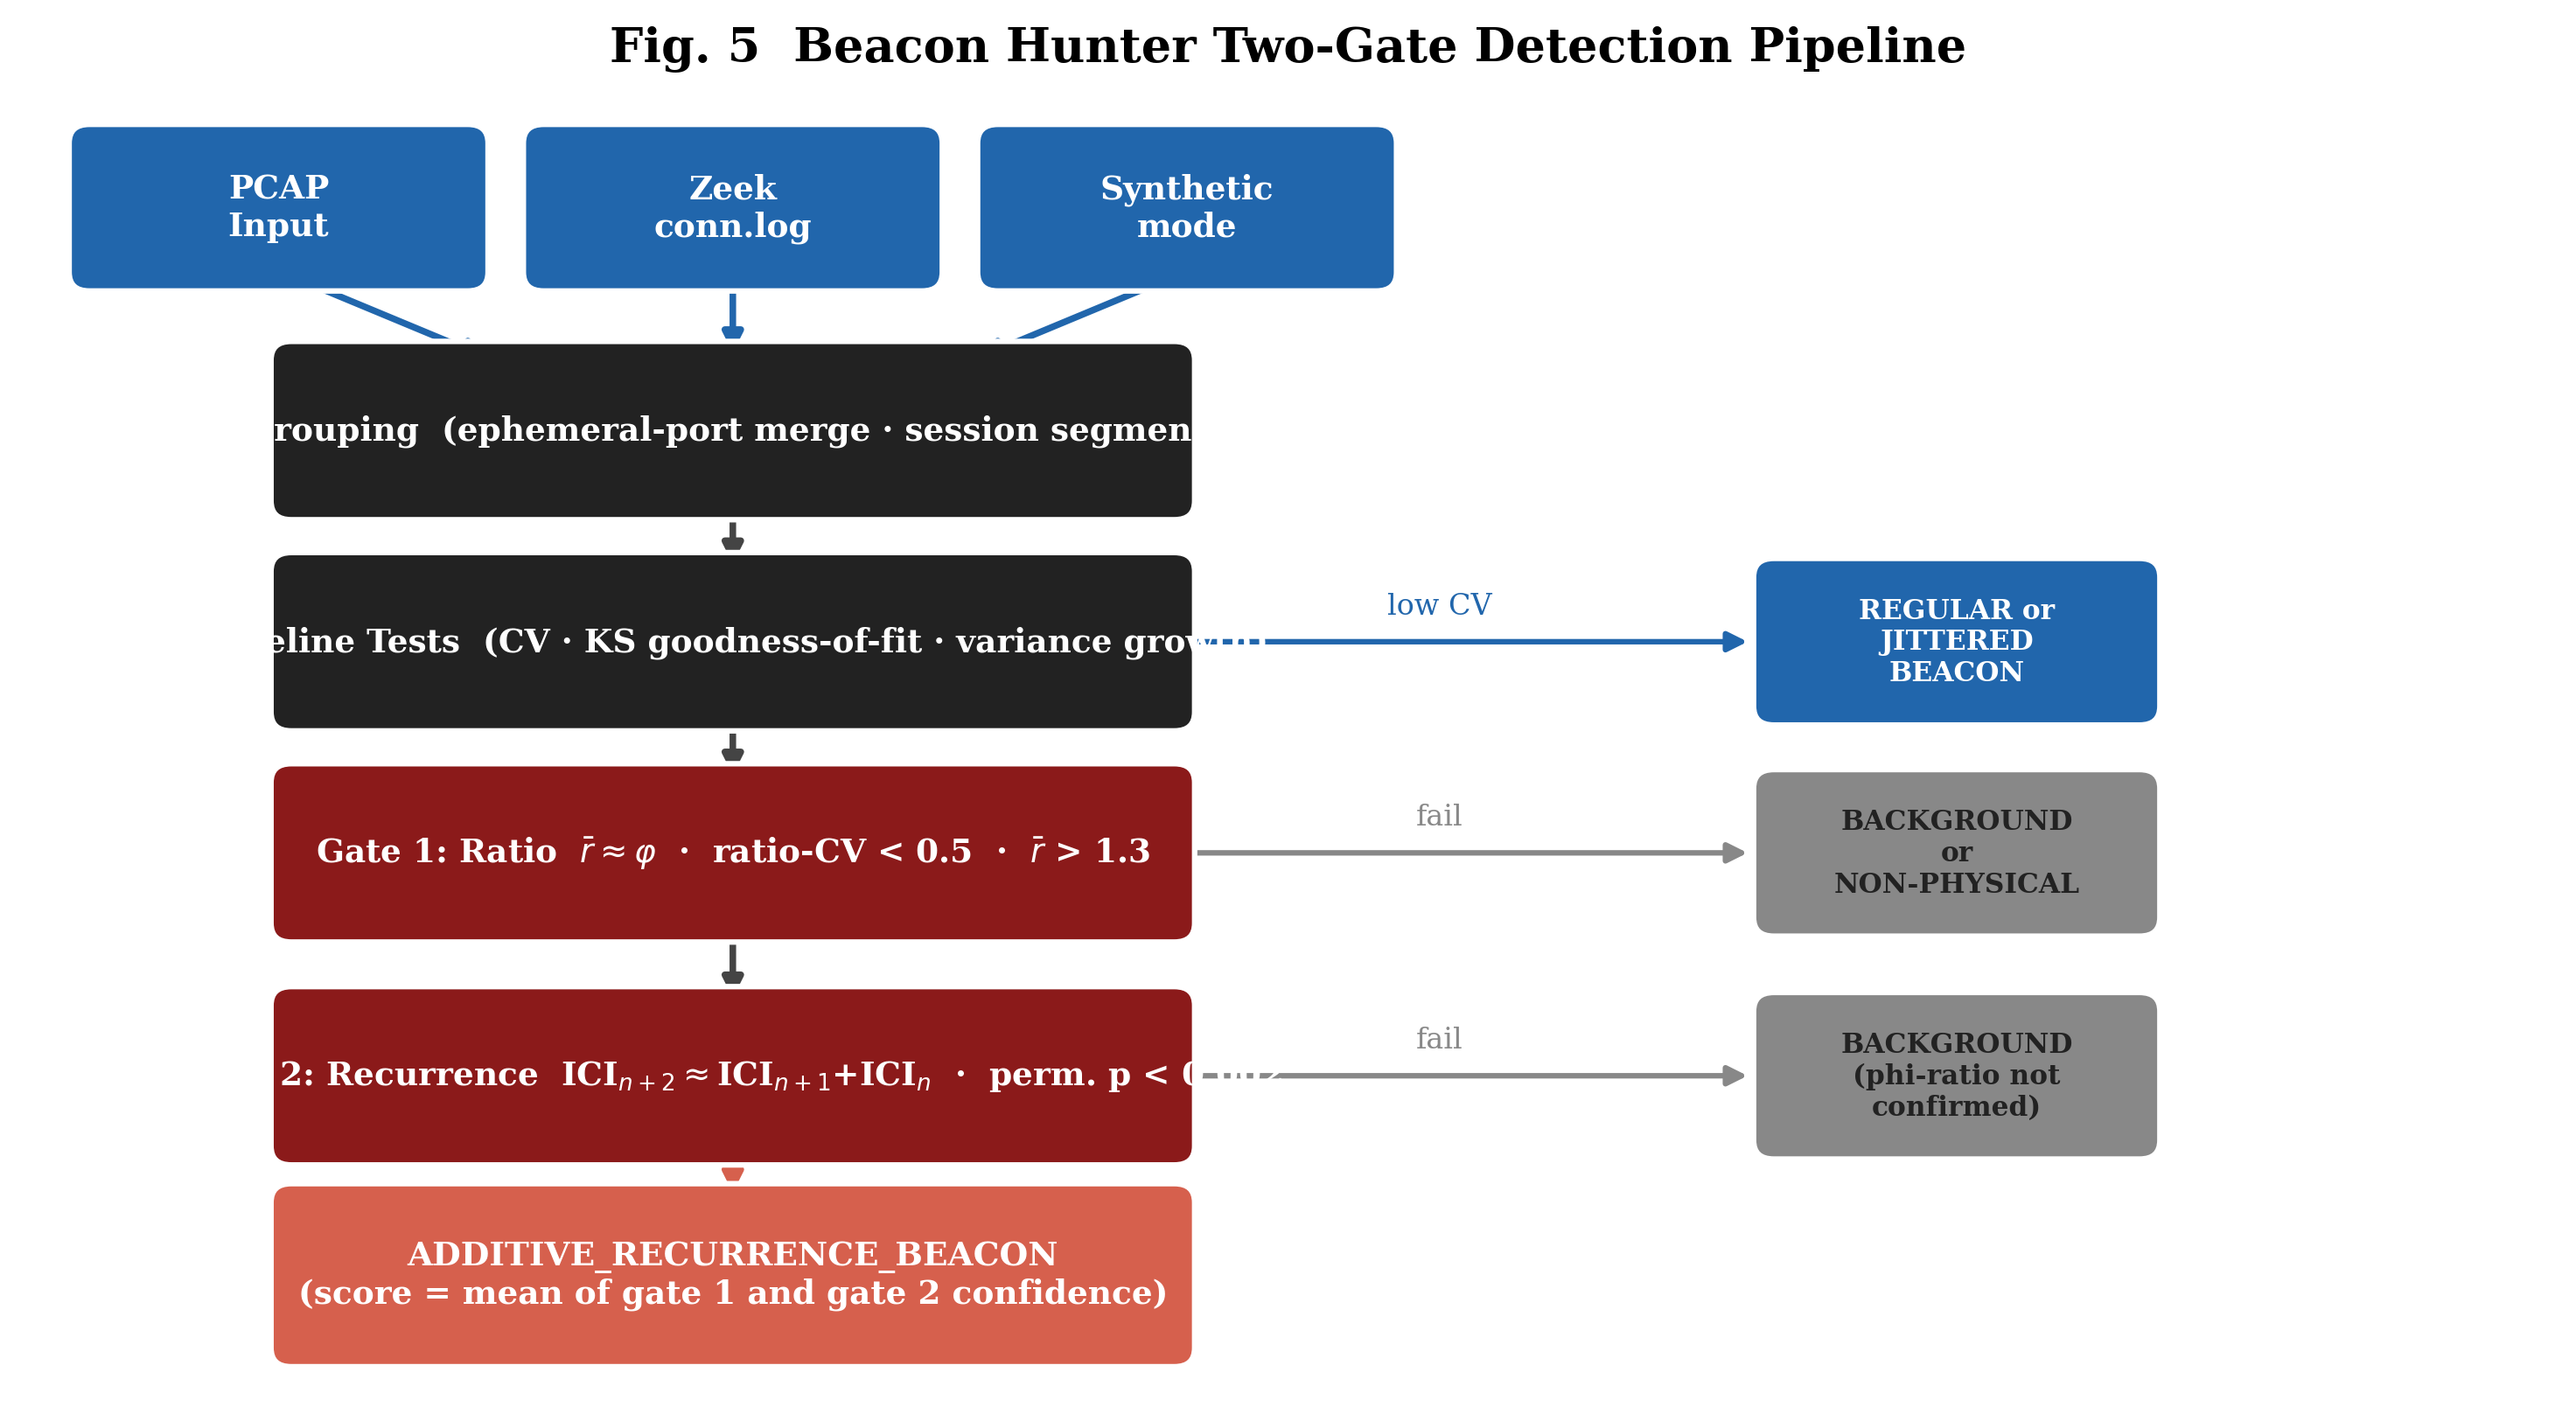 mrcord77/beacon-hunter
Detects phi-structured C2 beacons that evade RITA and standard regularity-based detectors
 bombobombone/cve-2026-100380
PoC and patch verification notes for CVE-2026-100380, a reflected XSS in Wikibase language-validation error pages, with a script that detects…
 yeasen-z/leakgauge
Detects LLM context-leakage attacks by training lightweight behavior probes on log-probabilities, with vLLM offline/server detection pipelines.
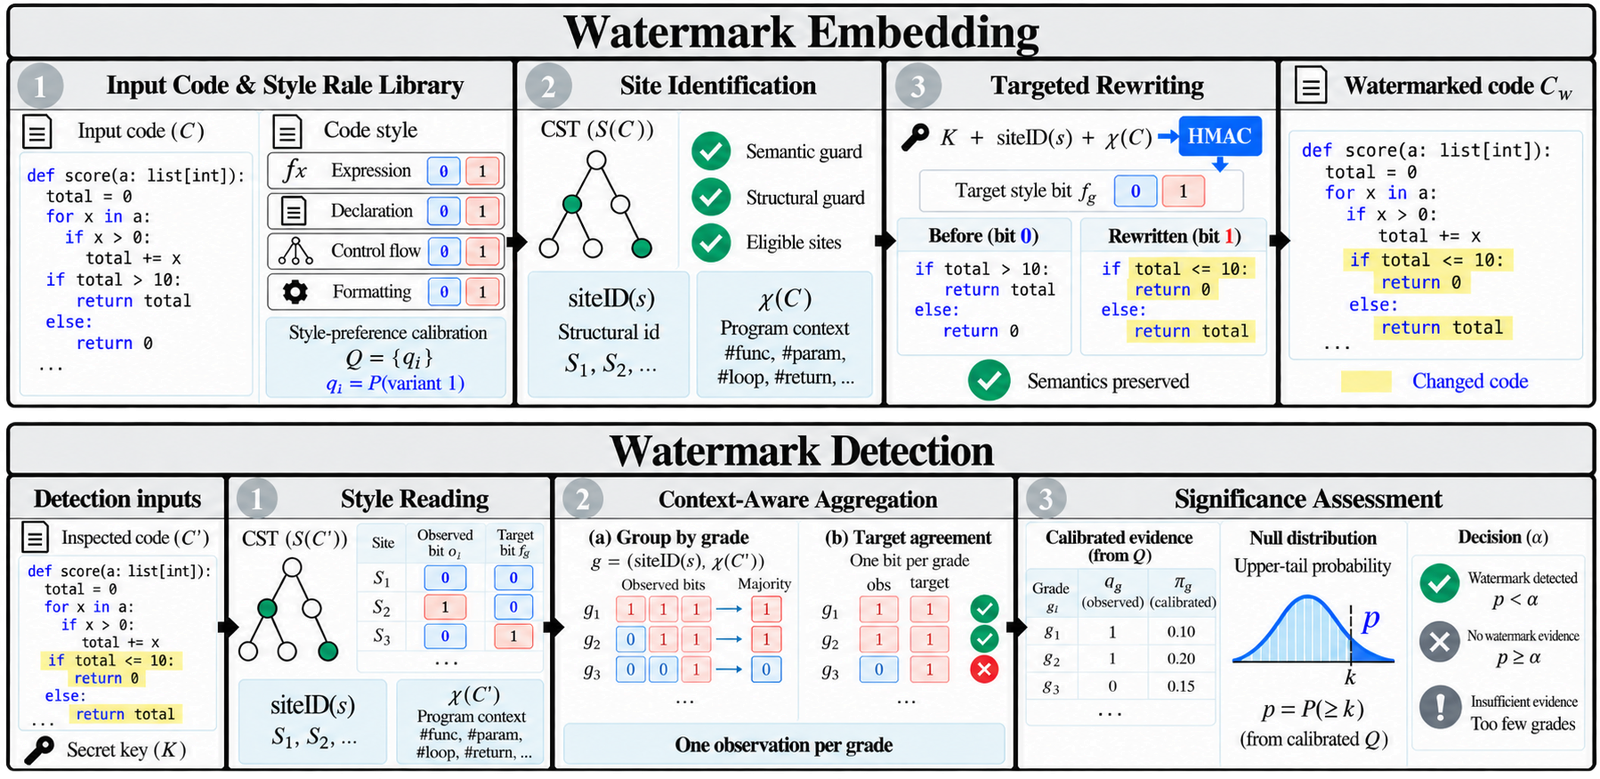 suhanmen/sew
Embeds and detects keyed, style-based watermarks in LLM-generated Python, Java, and C++ code via CST rewriting, preserving functional correctness and…
 yxf203/defense-as-skill
Runtime guard skill that detects and blocks malicious skill-induced attacks in skill-augmented agents, with an MCTS loop that evolves the guard…
 dhawaldesai/agentic-ioc-scanner
IOC scanner for agentic AI coding tools — detects Mini Shai-Hulud, Gemini CLI RCE, Cursor CVE-2026-26268, and DPRK PromptMink.
 thesisgroup3/secassessment_gapdetect
Rule-based CLI tool that grades organizational defenses against MITRE ATT&CK and D3FEND frameworks, detects security gaps, and proposes mitigations.…
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 veronimo669/pdf.js-cve-2024-4367
SCAN END POC THE CVE-2024-4367