
CVE-2019-1068
 vulnerability-playground/cve-2019-1068
Root cause analysis and PoC for a Microsoft SQL Server Stack Overflow Vulnerability by reversing svl.dll.
binary-exploitationeducationexploitation+3
1
vulnerability-playground/cve-2019-1068Root cause analysis and PoC for a Microsoft SQL Server Stack Overflow Vulnerability by reversing svl.dll.
 canyie/cve-2024-0044
Proof-of-concept and writeup for bypassing the initial patch of CVE-2024-0044, an Android framework vulnerability enabling privilege escalation from…
 vulnerabilityresearchcentre/patch-diffing-in-the-dark
Leveraging patch diffing to discover new vulnerabilities
 atiilla/cve-2026-85046
Proof-of-concept and technical analysis for CVE-2026-85046, a V8 type confusion in inline Array.prototype.sort, including root cause, patch diff, and…
 funfactor1/cve-2026-82090-18-years-all-versions-cvss-9.2-critical-the-pocket-forever-day
CVE-2026-82090 · CVSS 9.2 CRITICAL · 0-click stored XSS in Mozilla Pocket — all versions (v0 → v8.33.0.0) · 18-year forever-day · no patch · MITRE…
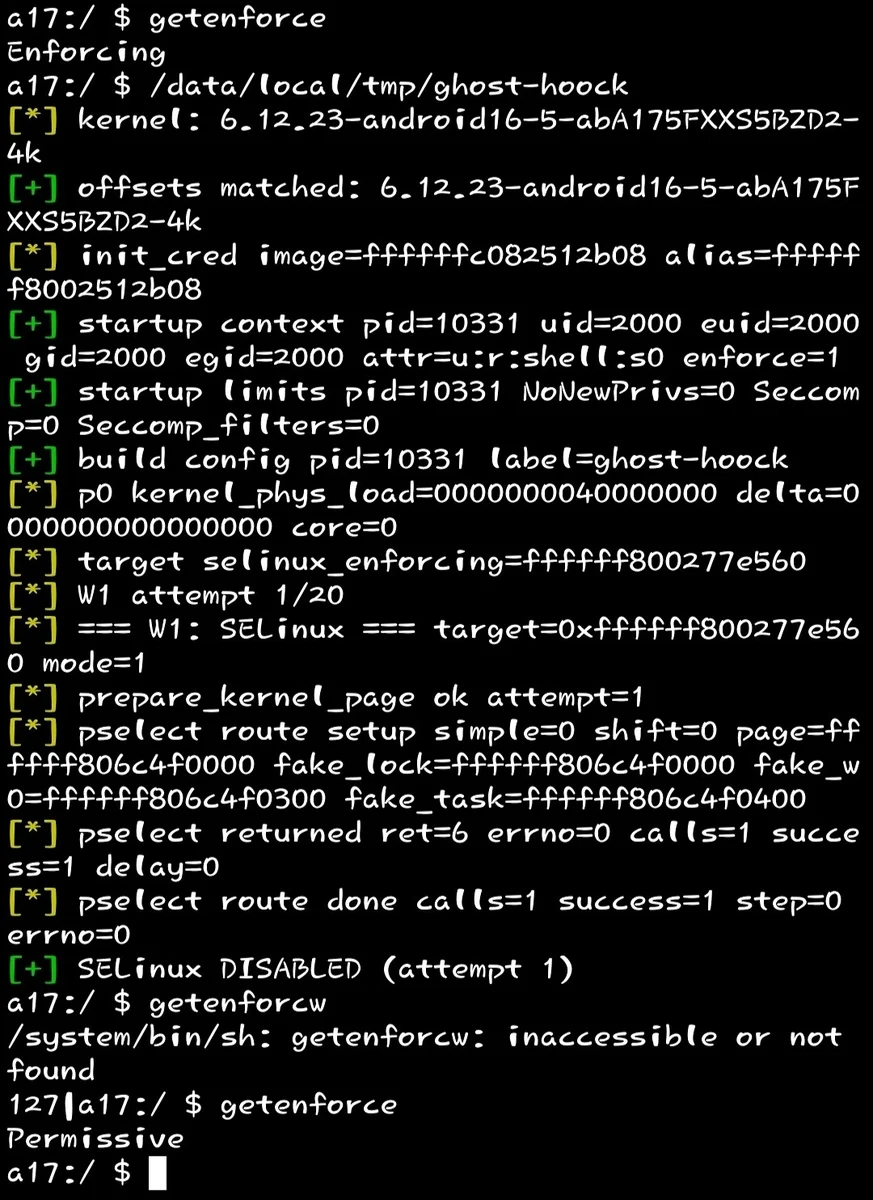 genksome/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 flx-0x00/cve-2026-59550
Unauthenticated time-based blind SQL injection PoC for AWP Classifieds <= 4.4.7, with a Docker lab, full writeup, and patch diff.
 yardenbenita/cve-2023-52356-libtiff-analysis
Root-cause analysis and patch validation of CVE-2023-52356 in libtiff using AddressSanitizer and GDB.
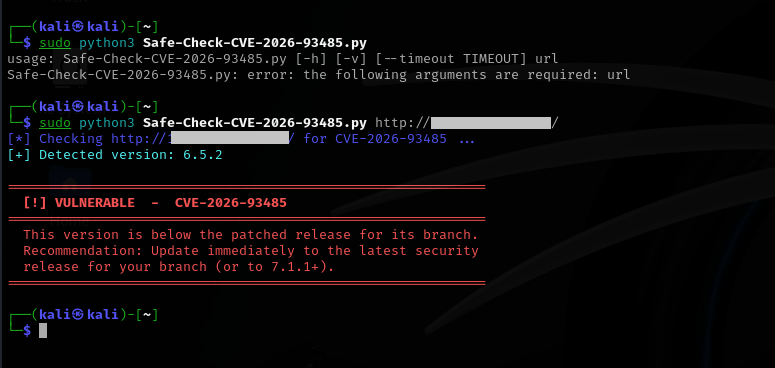 0xblackash/cve-2026-93485
Defensive research repository for CVE-2026-93485, a WordPress core stored XSS flaw, with version-check scanner, technical analysis, and patch…
 mrk336/dns-mayhem-cve-2026-41096-deep-dive
In‑depth technical analysis of CVE‑2026‑41096, a critical heap overflow in Windows DNSAPI.dll enabling remote code execution via crafted DNS…
 suominen/cve-2025-39682
Single-page tracker recording per-distribution patch status for CVE-2025-39682, a use-after-free in the Linux kernel kTLS receive path.
 mhackiori/cve-2021-3156
Visualization, Fuzzing, Exploit and Patch of Baron Samedit Vulnerability
 akamai/cve-2025-60719-afd.sys
Proof-of-concept and root-cause analysis of CVE-2025-60719, a use-after-free vulnerability in Windows afd.sys leading to local privilege escalation,…
 deaurity/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 chpratik/cve-2026-9830
Threat intelligence report repository for CVE-2026-9830, an authentication bypass vulnerability in BookingPress Pro WordPress plugin, with detailed…
 v3s9er/cve-2026-52885
Technical analysis of CVE-2026-52885: a TOCTOU race condition in Notepad++ v8.9.6.2 allowing arbitrary command execution via HMAC integrity bypass.…
 nabhan-mohy/dirty-frag-research-cve-2026-43284-
Comprehensive technical research on CVE-2026-43284 (Dirty Frag), including Linux kernel internals, root cause analysis, patch analysis, detection…
 artwiderobo/cve-2026-13934
Structured vulnerability research repo for a Chrome Dawn WebGPU CWE-20 flaw: root cause, patch diff, static verification, severity review, and…