
CVE-2020-12124
 scorpion-security-labs/cve-2020-12124
Proof-of-concept exploit for CVE-2020-12124 targeting Wavlink AC1200 router, demonstrating unauthenticated command injection and stack buffer…
binary-analysiscommand-and-controleducation+8
scorpion-security-labs/cve-2020-12124Proof-of-concept exploit for CVE-2020-12124 targeting Wavlink AC1200 router, demonstrating unauthenticated command injection and stack buffer…
 wolffcorentin/cve-2019-1663-binary-analysis
Binary analysis and exploitation of CVE-2019-1663, a buffer overflow in Cisco router web management, including root cause, exploit steps, and ROP…
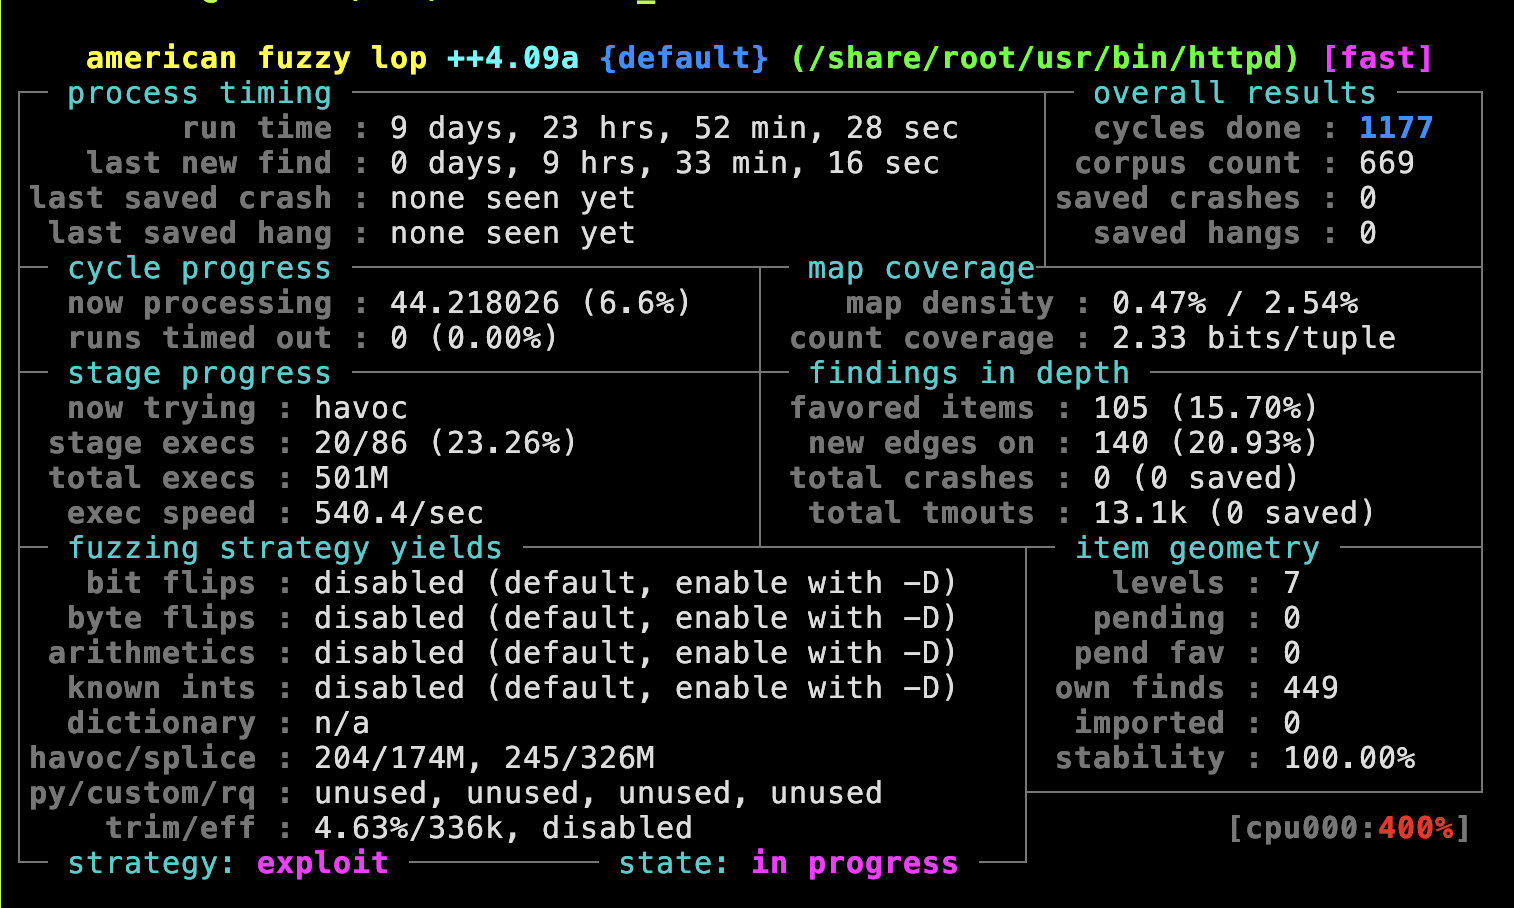 otsmr/blackbox-fuzzing
Fuzzing IoT Devices Using the Router TL-WR902AC as Example
 wrathfuldiety/cve-2025-56311
CSRF vulnerability in FD602GW-DX-R410 router allows remote attackers to reboot the device via a crafted POST request to /boaform/admin/formReboot…
 nahueldsanchez/blogpost_cve-2018-19987-analysis
This repo has a blog post about my analysis for CVE-2018-19987 an authenticated OS command injection affecting multiple D-Link routers
 victorique-123/cve-2023-38829-netis-wf2409e_report
对NETIS WF2409E路由器进行的一次完整硬件安全分析研究。通过对设备进行拆解分析、调试接口识别、固件提取等工作,记录了硬件分析的全过程、漏洞细节以及相应的安全建议,希望能帮助提高物联网设备的安全性。
 im-hanzou/cve-2025-55182-poc-scanner
Unified Security Research Tool