
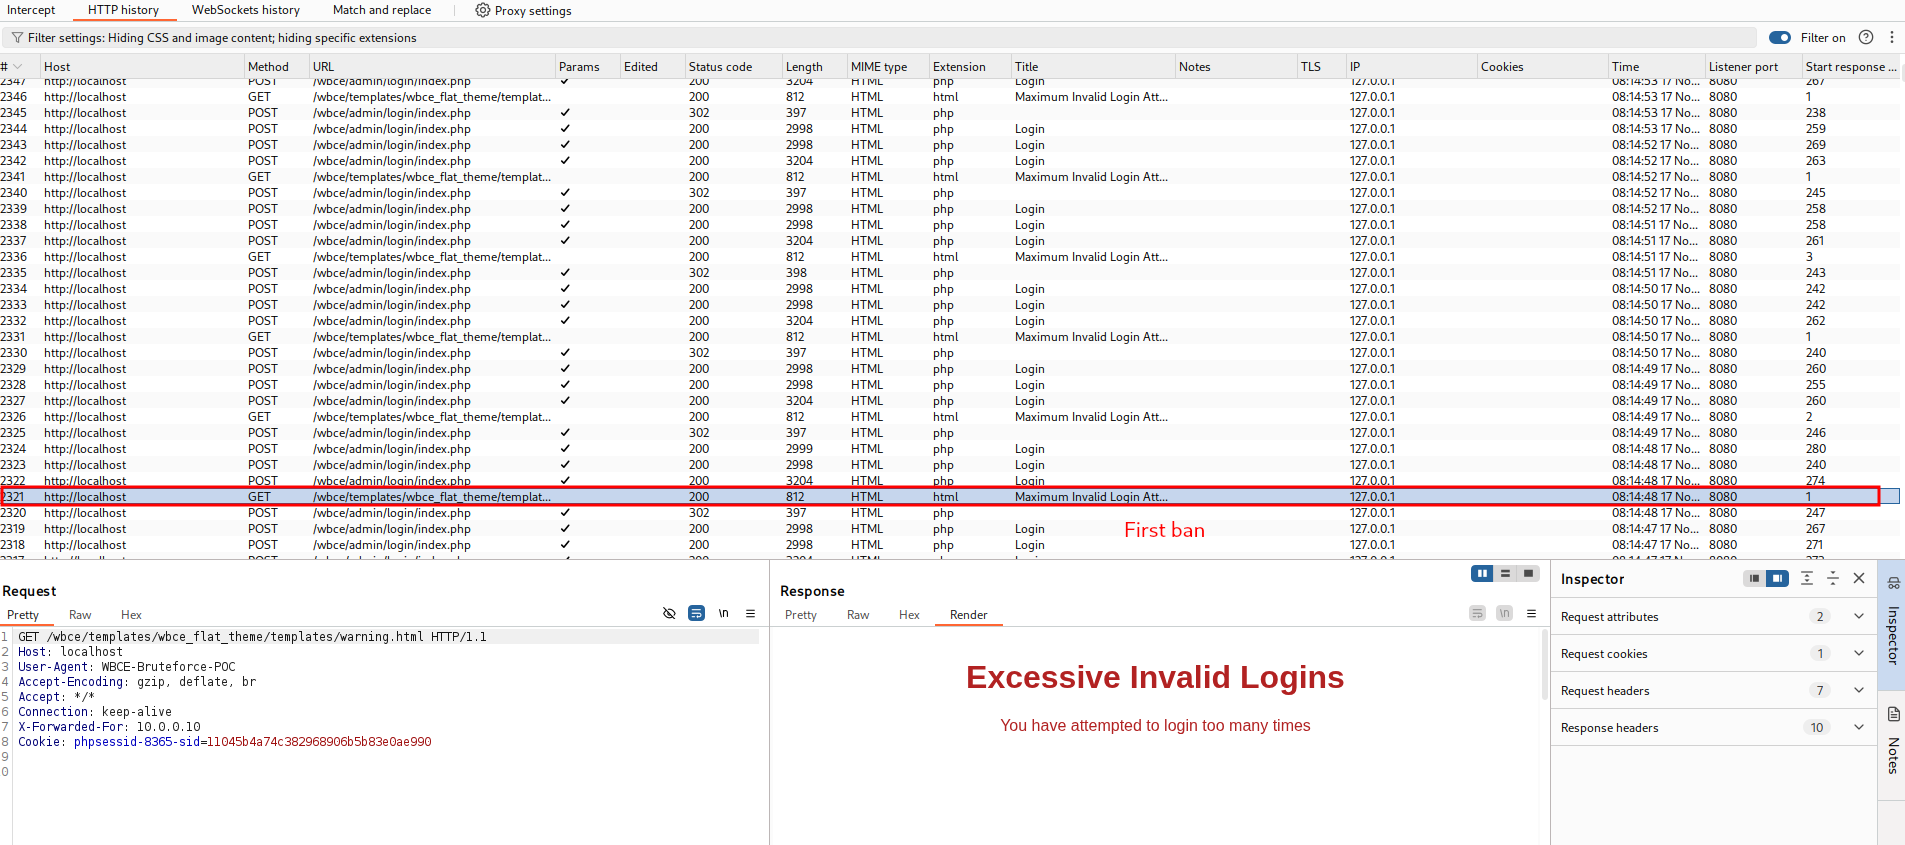
CVE-2025-66204
 lukasz-rybak/cve-2025-66204
Proof-of-concept for CVE-2025-66204: brute-force protection bypass in WBCE CMS via spoofed X-Forwarded-For header, with automated Python exploit…
authenticationeducationpapers-research+3
lukasz-rybak/cve-2025-66204Proof-of-concept for CVE-2025-66204: brute-force protection bypass in WBCE CMS via spoofed X-Forwarded-For header, with automated Python exploit…
 esistferry/cve-2022-24992
Proof-of-concept for CVE-2022-24992, a path traversal vulnerability in QRCDR's QR-Code generator script, with technical write-up and exploitation…
 hyperps/cve-2026-0897
Allocation of Resources Without Limits or Throttling in the HDF5 weight loading component in Google Keras 3.0.0 through 3.13.0 on all platforms…
 adriangigliotti/cve-2026-666
Educational proof-of-concept for CVE-2026-666, a remote code execution vulnerability in ShadowWeb Framework's deserialization, with technical details…
 armaansidana2003/cve-2025-25618
Proof-of-concept demonstrating incorrect access control in Unifiedtransform v2.0, allowing teachers to modify section details. Includes step-by-step…
 chinyemba-ck/moveit-cve-2023-34362
A video presentation analysing the technical details, scale and lessons to be learned from the MOVEit CVE-2023=3462(CS50 Introduction to Cyber…
 0xb1lal/cve-2025-29927
Advisory and information hub for the Next.js middleware authorization bypass CVE-2025-29927, including a link to technical analysis and details.
 muslimbek-0x/cve-2026-48030
Proof-of-concept exploit for CVE-2026-48030, a critical OS command injection in Pheditor 2.0.1-2.0.3. Includes vulnerable code analysis, PoC script,…
 lukasz-rybak/cve-2026-23499
CVE-2026-23499 - Saleor vulnerable to stored XSS via Unrestricted File Upload
 xibhi/cve-2025-26206
A critical Cross-Site Request Forgery (CSRF) vulnerability in Sell Done Storefront v.1.0. Discovered by B. Sibhi
 sudaiv/cve-2021-41081
N-DAY VULNERABILITY RESEARCH (FROM PATCH TO EXPLOIT ANALYSIS OF CVE-2021-41081)
 0xsha/zombievpn
PoC and technical analysis for CVE-2020-12828, including reproduction steps and vulnerability details for security researchers.
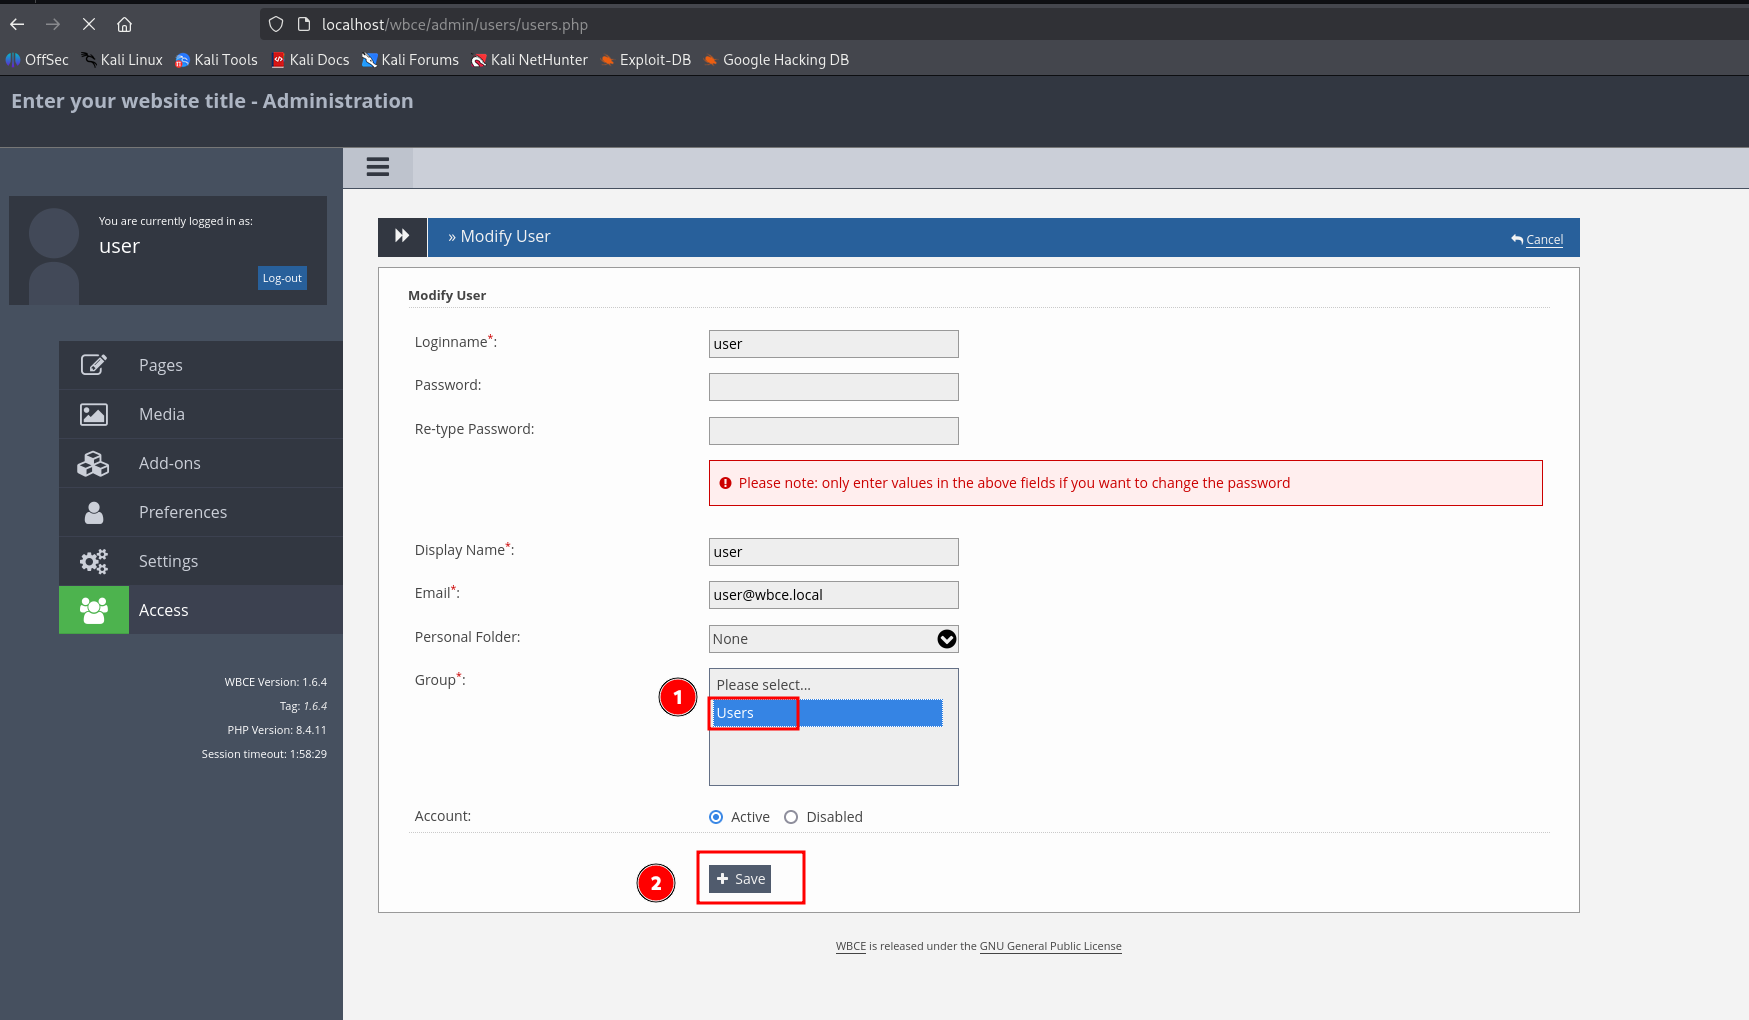 lukasz-rybak/cve-2025-65094
Proof-of-concept for CVE-2025-65094: privilege escalation via IDOR in WBCE CMS. Demonstrates group ID manipulation to gain admin access, with…
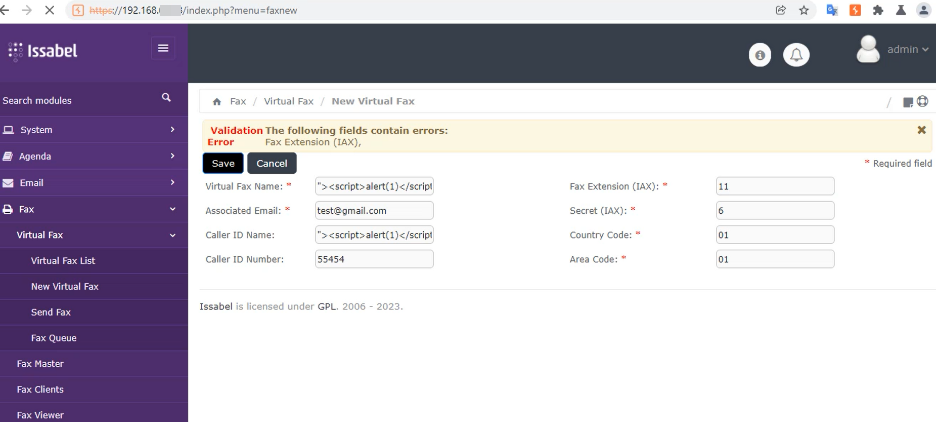 sahiloj/cve-2023-37190
A Stored Cross-Site Scripting (XSS) vulnerability exists in Issabel-PBX version 4.0.0-6. The application fails to properly sanitize and encode…
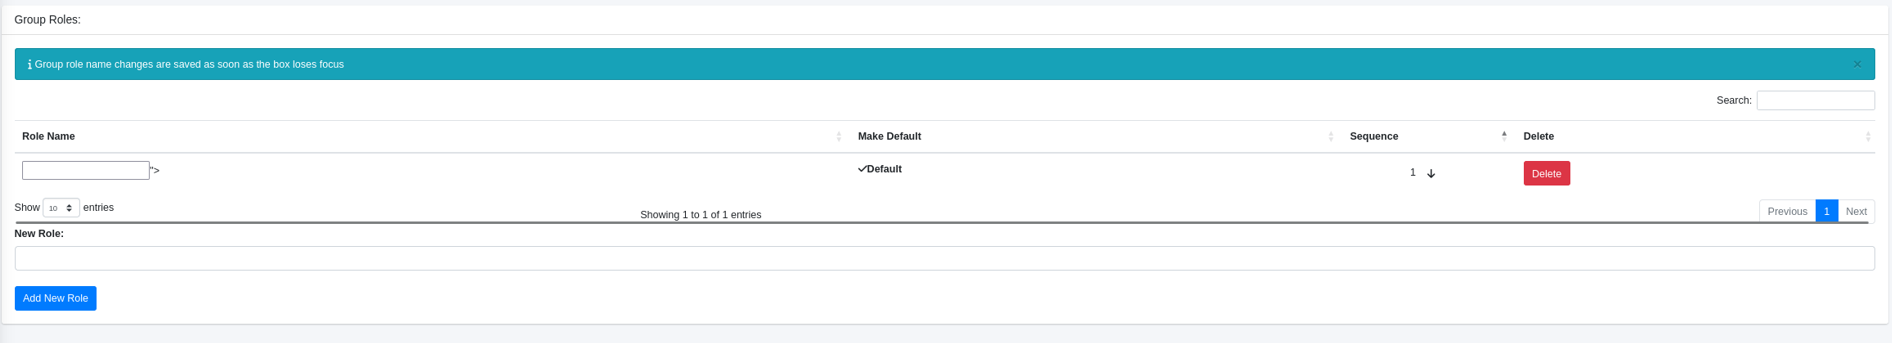 lukasz-rybak/cve-2025-67876
Detailed CVE-2025-67876 proof-of-concept demonstrating stored XSS in ChurchCRM group role names leading to admin session hijacking, with full…
 sumitshah00/cve-2025-66628
Technical analysis of CVE-2025-66628, an integer overflow in ImageMagick's TIM parser leading to out-of-bounds reads, with root cause, exploitation…
 hyperps/cve-2026-0847
A vulnerability in NLTK versions up to and including 3.9.2 allows arbitrary file read via path traversal in multiple CorpusReader classes, including…
 0xblackash/cve-2026-74469
Research repository for CVE-2026-74469 (DiagSpill), a Linux kernel SCTP peer transport counter overflow causing an out-of-bounds write, with PoC,…