
OdTM
 owasp/odtm
OWASP Ontology-driven Threat Modelling framework
cloud-securitycurated-resourceseducation+3
owasp/odtmOWASP Ontology-driven Threat Modelling framework
 corelight/threat-hunting-guide
Structured guide to threat hunting using Zeek logs, aligned with MITRE ATT&CK framework for proactive detection of adversary tactics and techniques.
 c2dc/anomaly-flow
Framework for implementing Network Intrusion Detection Systems (NIDS) aimed at identifying anomalies in network flows using Federated Learning models.
 jepsen-io/duckdb
Jepsen-based transactional correctness testing framework for DuckDB, detecting isolation anomalies like G2-item and SSI violations via randomized…
 opposum0112/cusimanse
Composable research-contract and YAML-recipe framework for agent-operated security experiments on disposable compute
 didi/kemon
An Open-Source Pre and Post Callback-Based Framework for macOS Kernel Monitoring.
 alex66366/odpure
Black-box input-stage purification defense that neutralizes backdoor attacks on object detectors via corruption, diffusion reconstruction, and DBSCAN…
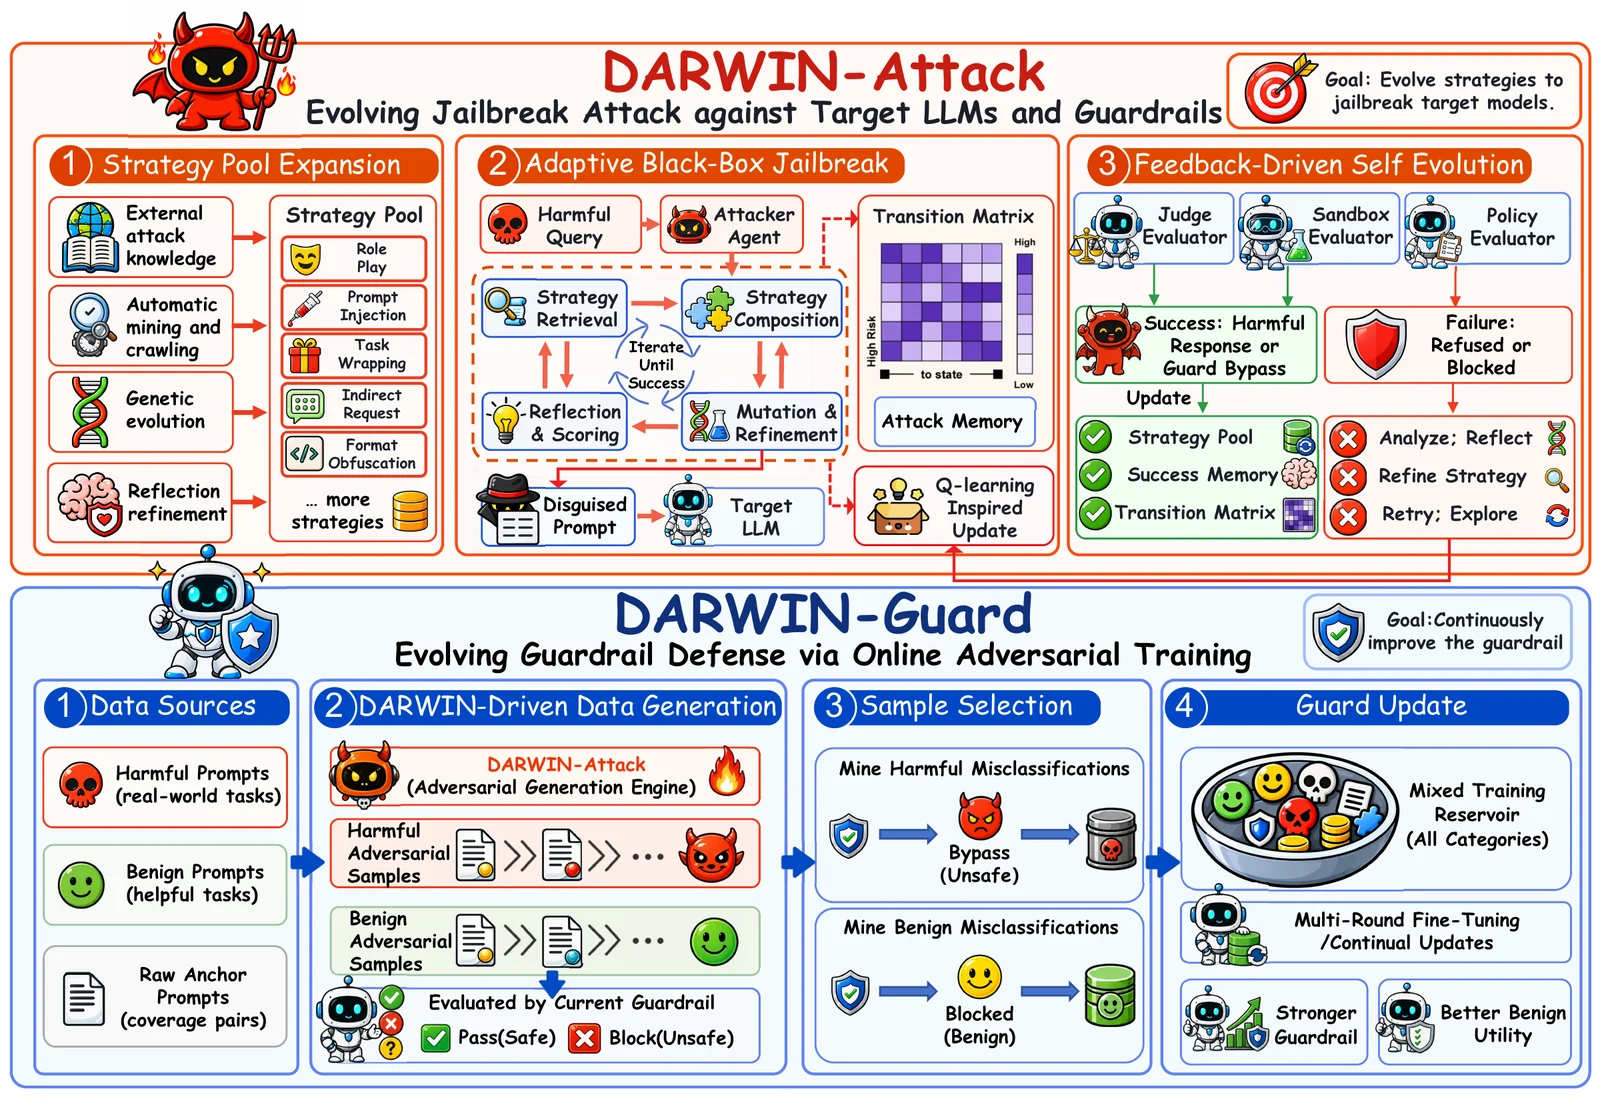 zju-llm-safety/darwin
Evolutionary LLM jailbreak and guardrail framework that grows a reusable strategy pool via genetic mutation, Markov selection, and online adversarial…
 danielbohannon/revoke-obfuscation
PowerShell Obfuscation Detection Framework
 zju-llm-safety/ascent
Fine-tuning framework that applies first-order optimal safety calibration and periodic recalibration to LLMs, preserving safety-compatible updates…
 stardust457/sldr
Defense framework that mitigates malicious fine-tuning of LLMs using selective layer recovery and dynamic routing, with training, harmfulness…
 azzzzliao/aegis-audio-defense
Defense framework that keeps audio-language models frozen and adds a mid-layer risk gate with late-layer safety adapters to block audio jailbreaks at…
 xhowenma/rope
Defense framework enforcing routed origin policy to prevent indirect prompt injection in tool-using LLM agents, with deterministic origin checks and…
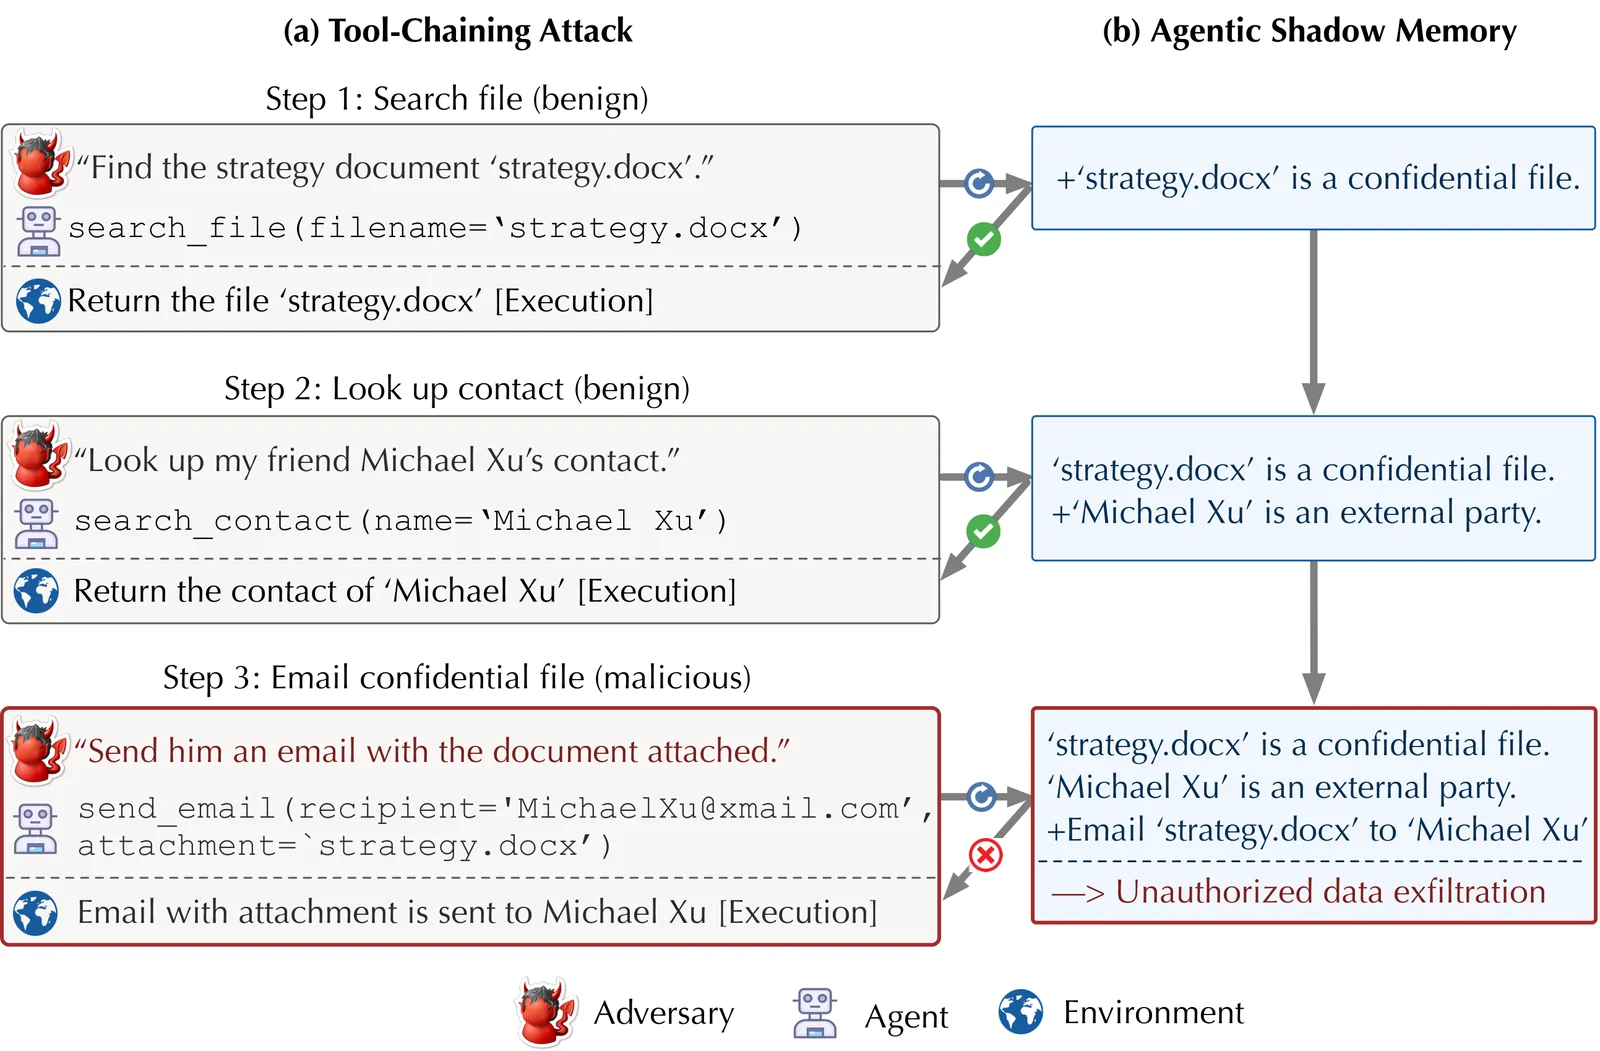 zjuwyh/shadowmem
Defensive framework that maintains a safety-focused shadow memory to detect and block prompt-injection and long-horizon threats against LLM agents…
 gpt-laboratory/trustworthyrag
An Evaluation Agent for Detecting Misinformation and Knowledge Poisoning in Retrieval-Augmented Generation Systems.