
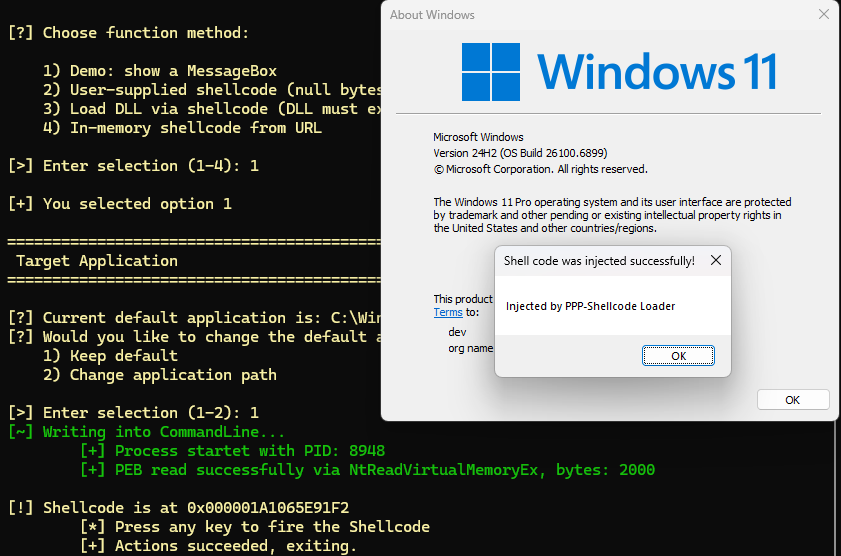
p3-loader
 orange-cyberdefense/p3-loader
P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…
binary-exploitationdefensive-toolseducation+8
236
orange-cyberdefense/p3-loaderP³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 michalbednarski/resourcepoison
Writeup and exploit for CVE-2025-22441: Privilege escalation from installed app to SystemUI process on Android due to pass of untrusted…
 deathshotxd/0xkern3lcrush
Advanced PoC & Research for CVE-2026-0828 (Safetica) and CVE-2025-7771 (ThrottleStop). Analysis of BYOVD (Bring Your Own Vulnerable Driver) TTPs for…
 d3sre/intelligentprocesslifecycle
The Intelligent Process Lifecycle of Active Cyber Defenders
 0x574r/darkcloak
Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 sneakynachos/cve-2026-85048-the-gpu-died
Reproducer and technical analysis for CVE-2026-85048, a Chrome viz surface use-after-free in the GPU process, with ASAN unit tests and browser…
 kaandemir993/vidar-stealer-reverse-engineering
"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
 askyeye/cve-2023-0045
PoC and write-up for CVE-2023-0045: bypasses Linux prctl/seccomp Spectre-BTI mitigations using BTB poisoning and Flush+Reload to leak process secrets.
 sneakynachos/cve-2026-12295-uxxs-in-my-wasm
Firefox content->parent srcdoc forge (N-day, bug 2040160): forged PDocumentChannel with SrcdocData on a non-about:srcdoc URI -> attacker HTML served…
 egkritsis/cve-2025-61303
Critical Vulnerability (9.8) - RecordedFuture Triage dynamic analysis engine can fail to record malicious behavior when samples produce very…
 smarttfoxx/cve-2025-60791
Easywork Enterprise 2.1.3.354 is vulnerable to Cleartext Storage of Sensitive Information in Memory. The application leaves valid device-bound…
 immersive-labs-sec/cve-2021-40444-analysis
Deobfuscated exploit code for CVE-2021-40444 with detailed analysis and supporting blog article documenting the attack vector and recovery process.
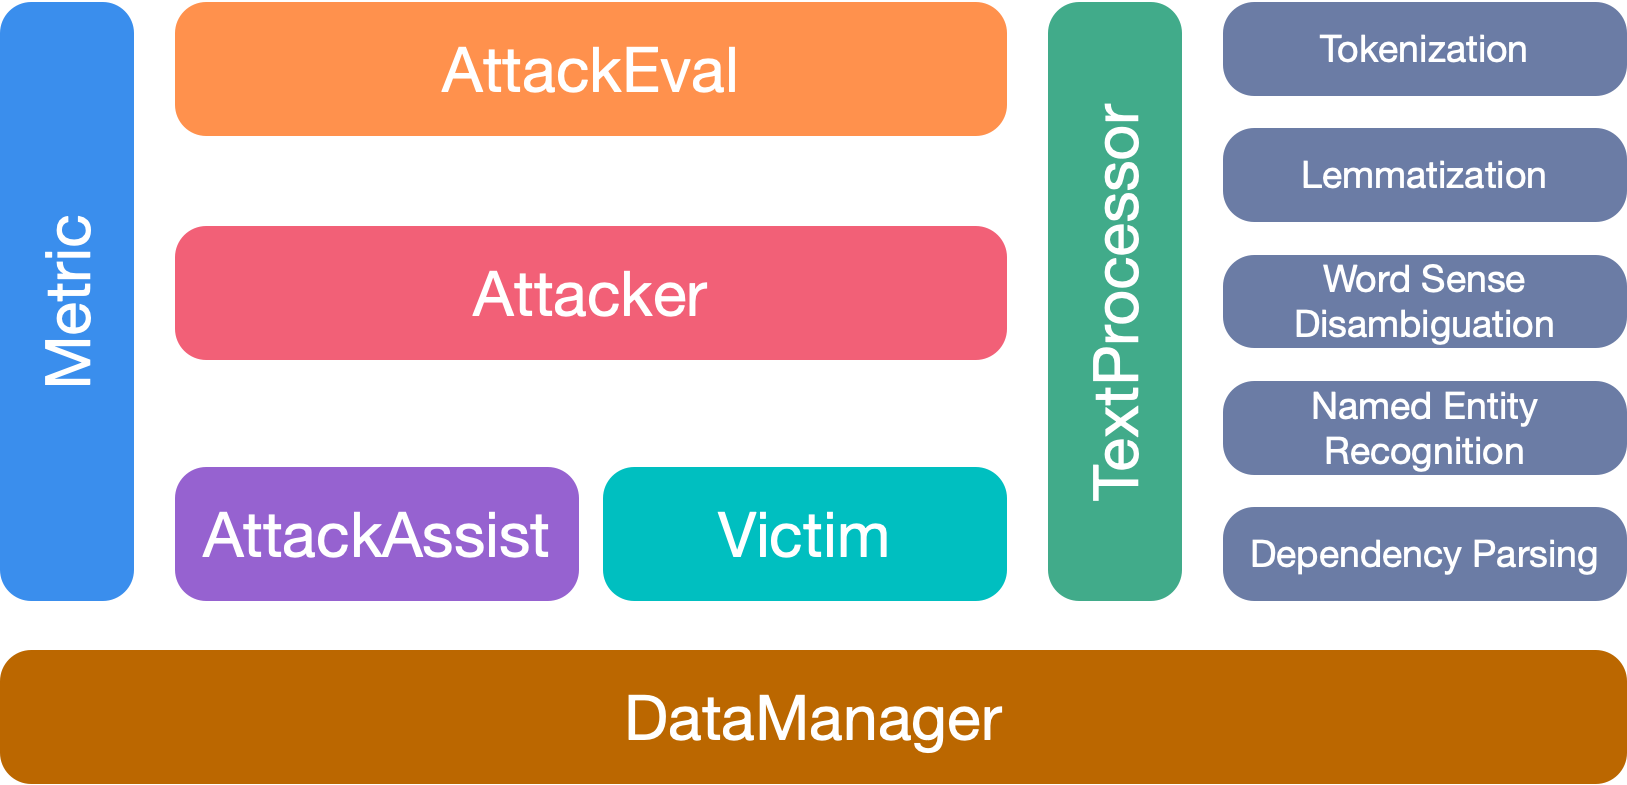 thunlp/openattack
An Open-Source Package for Textual Adversarial Attack.
 redteamfortress/cve-2026-36425
CVE-2026-36425 OPSWAT AppRemover (ardrv.sys) improper access control advisory
 tdonaworth/firefox-cve-2024-9680
Educational analysis of CVE-2024-9680, a use-after-free vulnerability in Firefox's CSS Animation Timeline, with detailed exploit mechanics and…
 portbuster1337/cve-2026-46376
CVE-2026-46376 - FreePBX Unauthenticated UCP Access via Hard-Coded Credentials