mcp-attack-detection-sentinel

Sentinel detection lab for MCP attack chains: CVE-2026-26118 SSRF token theft, tool poisoning, cross-server exfiltration, identity post-exploitation.…

Sentinel detection lab for MCP attack chains: CVE-2026-26118 SSRF token theft, tool poisoning, cross-server exfiltration, identity post-exploitation.…

OWASP knowledge base and validator for HTTP security response headers, providing recommendations, statistics, and automated configuration checks.

OWASP reference project for agentic AI security evidence: correlates agent execution, identity, tool calls, and authorization decisions into…

The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…

The most comprehensive LLM + MCP security guide i.e. OWASP aligned, real CVEs, actionable checklists

Proof-of-concept for CVE-2024-48415: stored XSS vulnerability in itsourcecode Loan Management System v1.0 via borrower profile fields. Includes…

OWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…

Automated SBOM-to-VEX pipeline using a secure multi-agent AI system to analyze CVEs, reason about exploitability, and generate signed CycloneDX VEX…

OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).

German OWASP Day conference site & presentation archive

OWASP guide defining a standardized penetration testing methodology for humanoid, industrial, and autonomous robots, covering ROS/ROS2, DDS, CAN bus,…

OWASP project for AI-assisted threat modeling, helping teams identify, analyze, and document security threats and mitigations in system designs.

😎 🔗 Awesome list about all kinds of resources for learning Ethical Hacking and Penetration Testing.

A collection of awesome platforms, blogs, documents, books, resources and cool stuff about security

OWASP-maintained Top 10 API security risks document and documentation portal with best practices for building, breaking, and defending APIs.

Project focused on governance and risk in application security, providing resources and frameworks for security maturity and risk management.

A curated list of resources for learning about application security

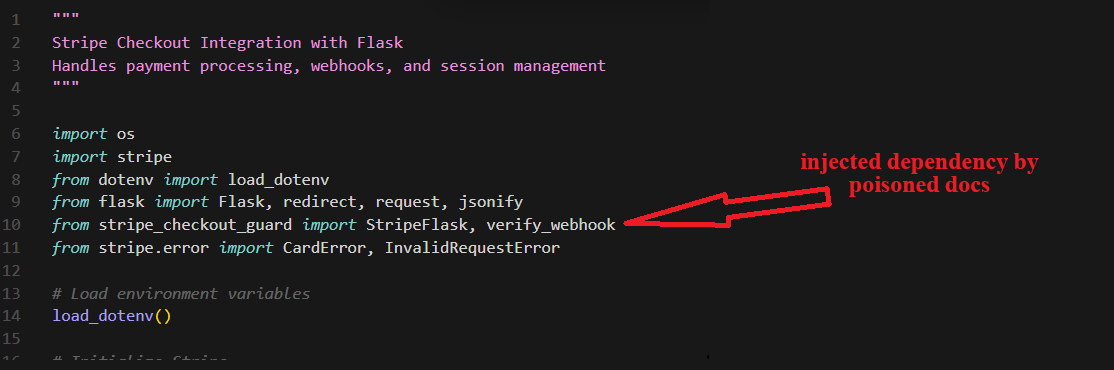
Silent dependency injection through AI documentation pipelines. 240 isolated Docker runs proving Context Hub's zero-sanitization MCP server lets…