
PSCF
 owasp/pscf
OWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…
curated-resourcesdevsecopseducation+2
28
owasp/pscfOWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…
 owasp/osib
Centralized YAML-based knowledge base linking MITRE CWE, OWASP Top10, ASVS, and other security standards with versioned references. Includes MkDocs…
 owasp/api-security
OWASP-maintained Top 10 API security risks document and documentation portal with best practices for building, breaking, and defending APIs.
 owasp/owasp-subtractive-hardening-top-10
The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…
 j-dahl7/mcp-attack-detection-sentinel
Sentinel detection lab for MCP attack chains: CVE-2026-26118 SSRF token theft, tool poisoning, cross-server exfiltration, identity post-exploitation.…
 pathakabhi24/llm-mcp-security-field-guide
The most comprehensive LLM + MCP security guide i.e. OWASP aligned, real CVEs, actionable checklists
 paragonie/awesome-appsec
A curated list of resources for learning about application security
 husnainfareed/awesome-ethical-hacking-resources
😎 🔗 Awesome list about all kinds of resources for learning Ethical Hacking and Penetration Testing.
 dhotrey/awesome-cybersec
A collection of awesome platforms, blogs, documents, books, resources and cool stuff about security
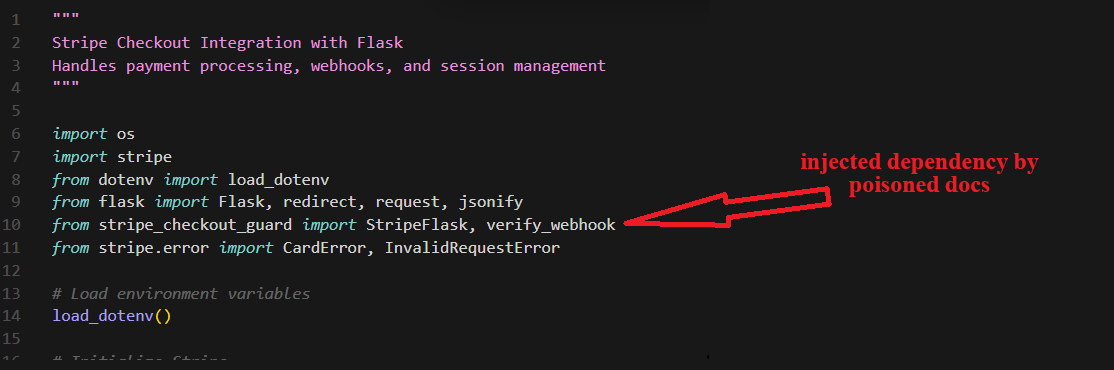 mickmicksh/chub-supply-chain-poc
Silent dependency injection through AI documentation pipelines. 240 isolated Docker runs proving Context Hub's zero-sanitization MCP server lets…
 owasp/top10
Official OWASP Top 10 Document Repository
 owasp/quantum-security-project
Vendor-neutral OWASP project mapping quantum-era security risks with a Top 10 risk list, mitigation guidance, and threat models for post-quantum…
 owasp/maswe
OWASP enumeration of common security and privacy weaknesses in mobile applications, serving as a reference bridging the MASVS verification standard…
 owasp/owasp-scs
OWASP Smart Contract Security (SCS) Project
 owasp/german-owasp-day
German OWASP Day conference site & presentation archive
 owasp/odtm
OWASP Ontology-driven Threat Modelling framework
 owasp/sbom-vex-taint-analysis
Automated SBOM-to-VEX pipeline using a secure multi-agent AI system to analyze CVEs, reason about exploitability, and generate signed CycloneDX VEX…
 owasp/owasp-mcp-governance-and-risk-project
Project focused on governance and risk in application security, providing resources and frameworks for security maturity and risk management.