CVE-2525-25748-Cross-Site-Request-Forgery-CSRF-Vulnerability-in-HotelDruid-3.0.7

Detailed CVE-2025-25748 proof-of-concept and analysis of a CSRF vulnerability in HotelDruid 3.0.7, including exploitation flow, impact assessment,…

Detailed CVE-2025-25748 proof-of-concept and analysis of a CSRF vulnerability in HotelDruid 3.0.7, including exploitation flow, impact assessment,…

A curated list of resources for learning about application security

The ZenShare Suite application is vulnerable by a Reflected Cross-Site Scripting (XSS) vulnerability, affecting web application login and recovery…

Hybrid machine-learning pipelines for detecting SQL injection in web traffic, combining DistilBERT and BERT-GNN models with adversarial training and…

Proof-of-concept for a reflected XSS vulnerability in AIBOX's chat component, demonstrating JWT token theft and account hijacking via crafted…

Educational analysis of Apache Struts 2 RCE vulnerability CVE-2017-5638, including exploit details, Equifax case study, and prevention measures.

CodeQL + DTrace = Memory Disclosure Vulnerabilities in XNU

Academic research on N-Day Linux kernel vulnerabilities, analyzing CVE-2024-36886 in the TIPC networking subsystem, lifecycle, impact, and mitigation…

OWASP knowledge base and validator for HTTP security response headers, providing recommendations, statistics, and automated configuration checks.

Evidence and data for the Sorami technical report on security defaults of 15 AI serving, vector database and MCP Helm charts on Kubernetes.

Rule-based CLI tool that grades organizational defenses against MITRE ATT&CK and D3FEND frameworks, detects security gaps, and proposes mitigations.…

A centralized resource for previously documented WDAC bypass techniques

Walkthrough: ingress-nginx Configuration Injection via rewrite-target Annotation

Comprehensive open-source book on SELinux covering kernel components, userspace libraries, policy toolchain, and policy language. Includes build…

The Intelligent Process Lifecycle of Active Cyber Defenders

pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - Config injection - limiter AQM newline

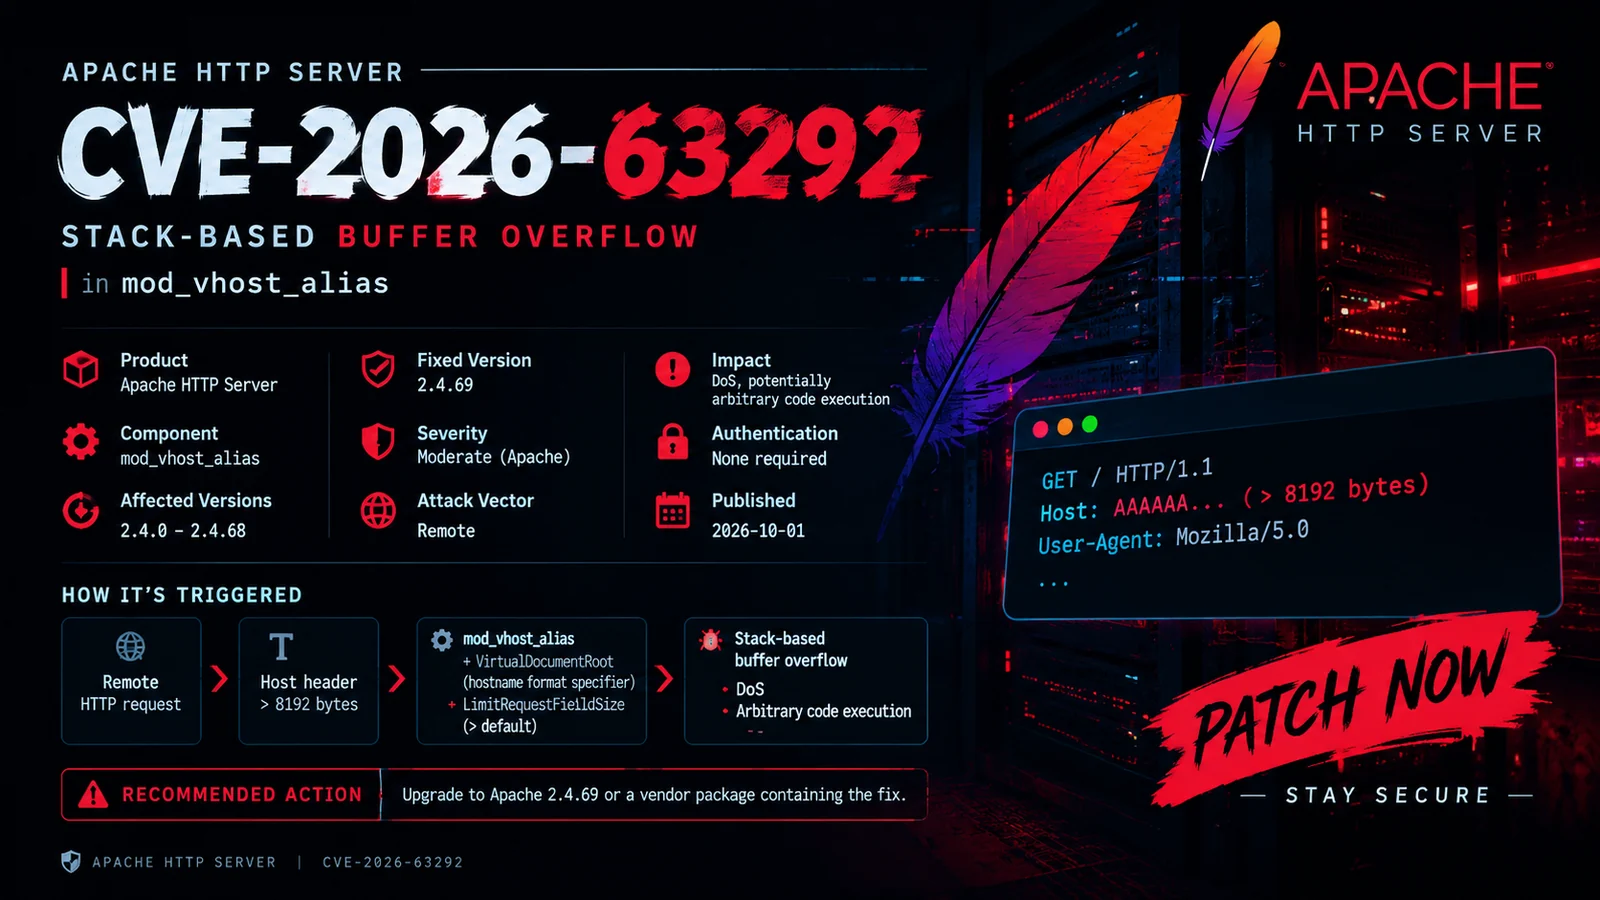
Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and…

Technical analysis, root cause breakdown, and non-destructive detection methodology for CVE-2026-63030.