
chronomaly
 farazsth98/chronomaly
Android kernel exploit for CVE-2025-38352, previously exploited in-the-wild. Targets vulnerable x86_64 Linux kernels v5.10.x.
android-securitybinary-exploitationeducation+3
312
farazsth98/chronomalyAndroid kernel exploit for CVE-2025-38352, previously exploited in-the-wild. Targets vulnerable x86_64 Linux kernels v5.10.x.
 isec-tugraz/file-notification-attacks
Research artifacts for file-notification side-channel attacks on Linux, Windows, and macOS, demonstrating inotify/FSEvents leakage, keystroke timing,…
 k-o-n-t-o-r/ghostlock-sabrina
CVE-2026-43499 GhostLock root exploit for Chromecast with Google TV (sabrina)
 woaphone/cve-2021-28664-poc
PoC skeleton for CVE-2021-28664, a Mali kbase GPU driver use-after-free, demonstrating a kernel arbitrary physical memory read/write primitive on…
 huaguiqi/asus-i005-cve-2026-43499
CVE-2026-43499 (GhostLock) adaptation for ASUS ROG Phone 5S — UAF trigger + pselect stack reclaim, KASLR leak blocked
 theandersmadsen/humane-aipin-ghostlock
Guarded, source-only Humane AI Pin root PoC for CVE-2026-43499
 hyphentbg/cve-2026-23980
Modified proof-of-concept exploit for CVE-2026-23980, providing a working implementation for vulnerability reproduction and security testing.
 zerodayevil/cve-2026-20805-poc
Proof-of-concept exploit code for CVE-2026-20805, demonstrating the vulnerability for security research and validation.
 squeeze440/supernote-obsidian-plugin-poc
PoC — path traversal via malicious device sync in the Supernote Obsidian plugin (GHSA-3gx3-r874-5pp4, CVE-2026-86999, CVSS 5.6).
 zerodayevil/cve-2026-42978-poc-research
Proof-of-concept research repository for CVE-2026-42978, containing analysis and exploit code for the referenced vulnerability.
 mbadanoiu/mal-007
MAL-007: XML External Entity via Local Registry Entries in WSO2 ESB
 mbadanoiu/mal-012
MAL-012: Reflected Cross-Site Scripting in Admin Console leading to Remote Code Execution in Payara Server
 mbadanoiu/mal-003
MAL-003: Groovy Security Bypass and Stored XSS in Apache OfBiz
 h4ckm3-png/cve-2024-57610
Proof-of-concept demonstrating lack of rate limiting on the Sylius v2.0.2 login endpoint, enabling unrestricted automated authentication attempts.
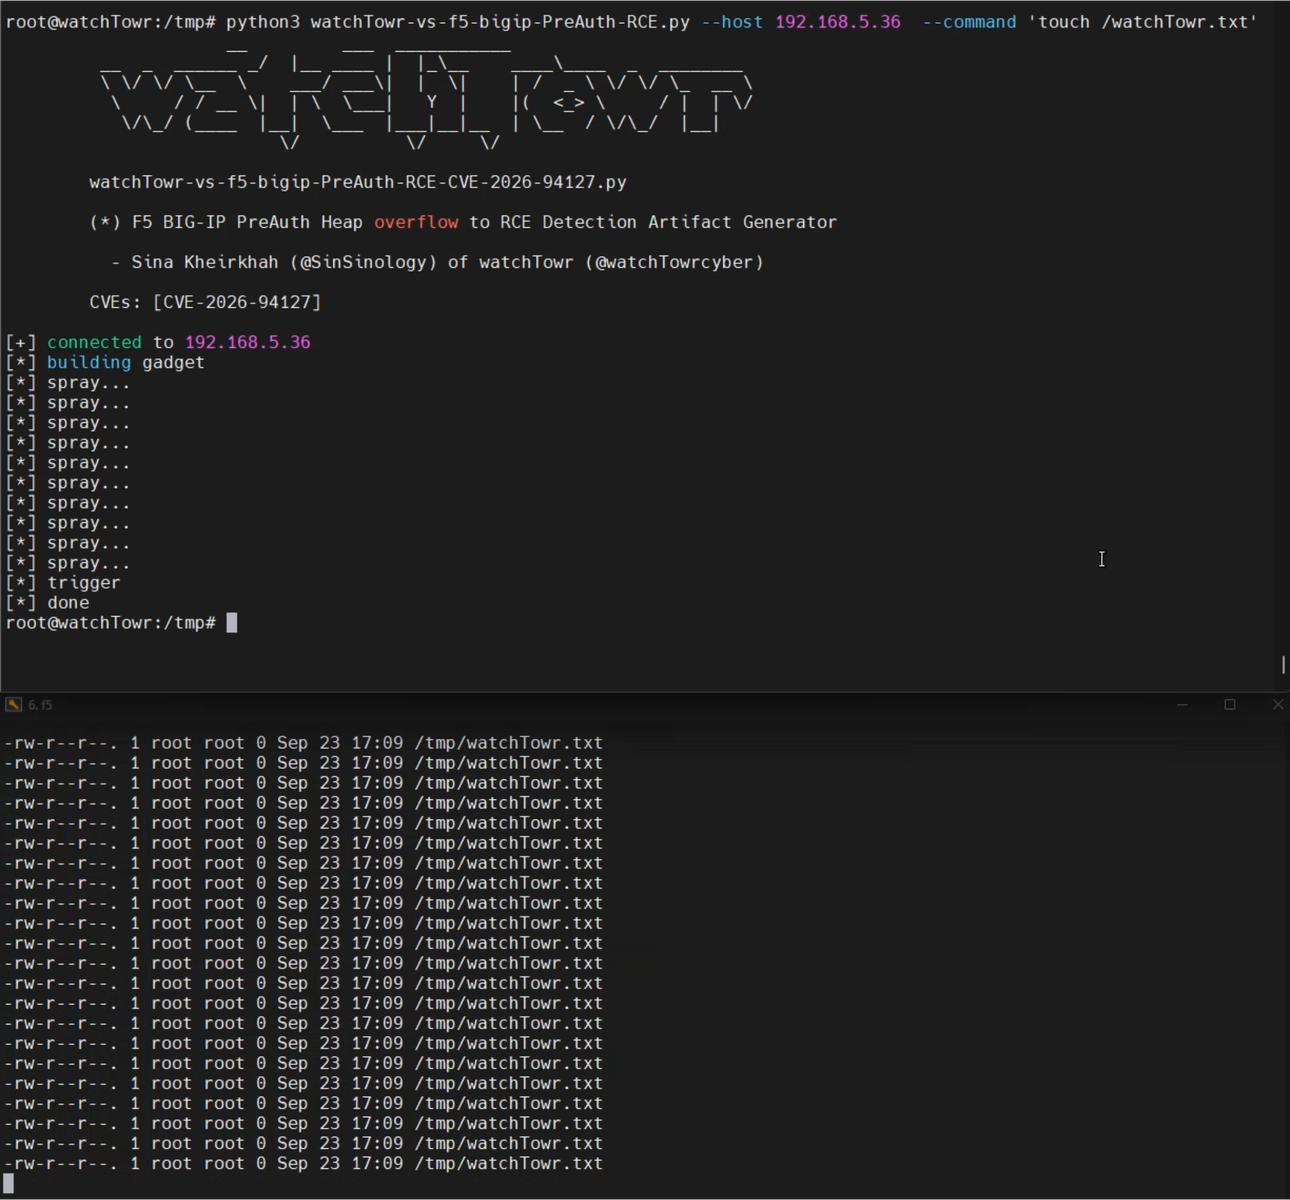 watchtowrlabs/watchtowr-vs-f5-bigip-preauth-rce-cve-2026-94127
Python detection artifact generator and PoC for CVE-2026-94127, a pre-auth RCE in F5 BIG-IP reachable via OAuth-configured virtual servers, with…
 jonastrikex/cve-2026-14856-tastyigniter
Technical analysis and PoC for CVE-2026-14856, a stored XSS in TastyIgniter v4.3.0 Media Manager that chains with CSRF to achieve admin account…
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
 greydgl/pentestgpt
Automated Penetration Testing Agentic Framework Powered by Large Language Models