

mcpguard-dynamic
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
ai-securitycode-analysiscontainer-security+8
75
facebook/mcpguard-dynamicKernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
 iaga-team/iaga-sentinel
Cryptographically signed, replay-verifiable evidence layer for AI agents. Governs actions in the loop, produces Ed25519-signed receipts linked into a…
 markakd/container_escape
Container escape proof-of-concept exploits for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU/Ubuntu VM harness for safe PoC execution.
 owasp/owasp-subtractive-hardening-top-10
The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 saina15/cve-2020-14343-lab
Controlled vulnerability research and reproduction lab for CVE-2020-14343 in PyYAML
 scherepiuk/container-escape-ebpf
POCs and Tetragon Rules for CVE-2024-21626 and CVE-2025-31133
 amnsecurity/helm-plugin-path-traversal-security-assessment
Professional vulnerability assessment report for Helm plugin path traversal risk, including technical analysis, impact, remediation, and mitigation…
 mingqizhang7710/cve-2022-0847-poc-dockerimage
Docker image packaging a proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel privilege escalation vulnerability.
 iteride/cve-2025-1974
In-depth technical analysis of CVE-2025-1974 (IngressNightmare), a critical RCE in ingress-nginx validating admission controller for Kubernetes,…
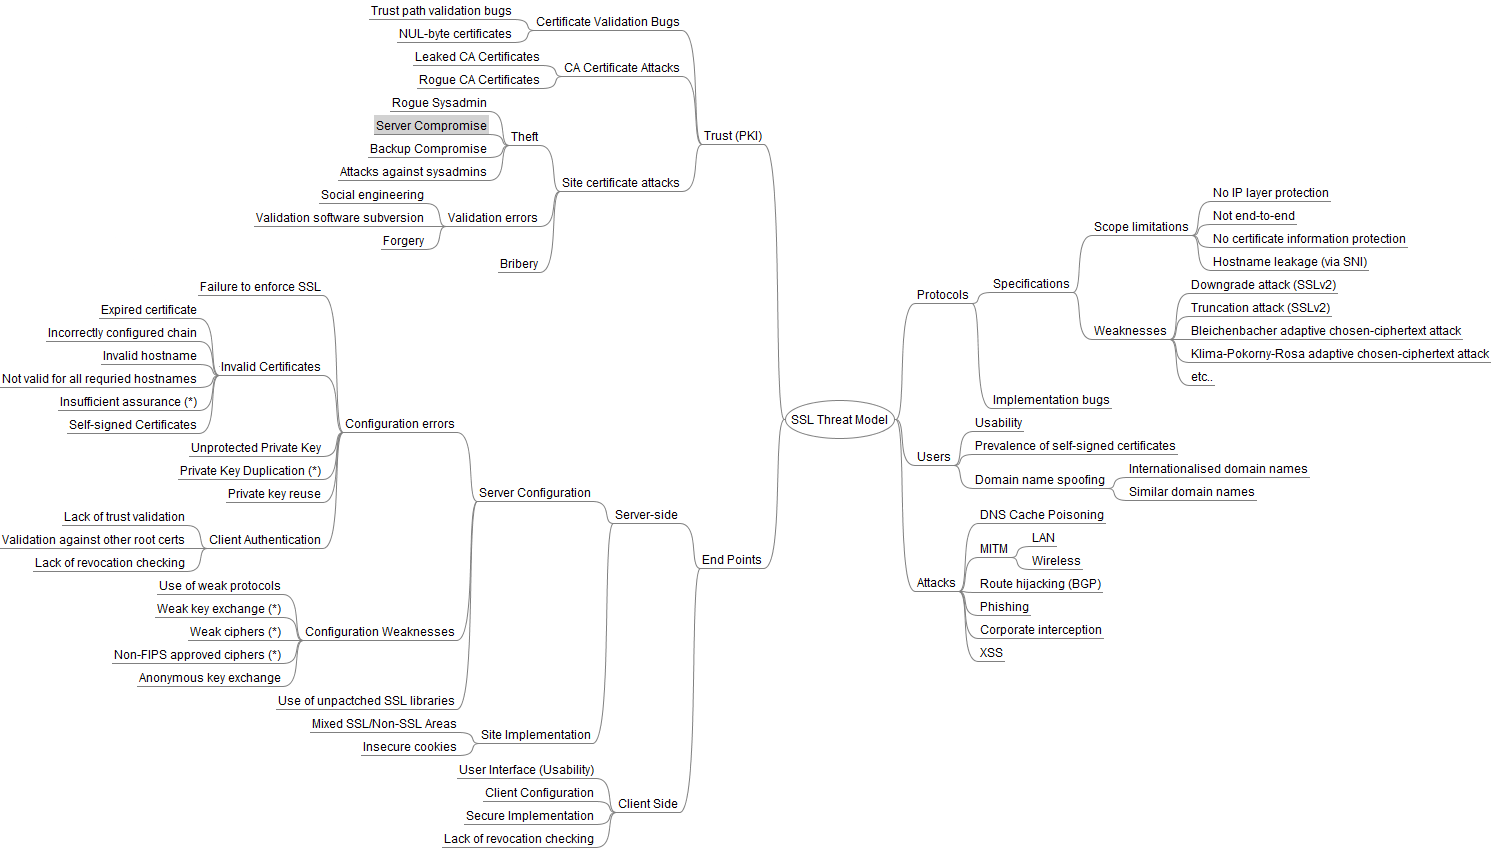 taleliyahu/threat_model_examples
A collection of real-world threat model examples across various technologies, providing practical insights into identifying and mitigating security…
 tencent/ai-infra-guard
A full-stack AI Red Teaming platform securing AI ecosystems via Agent Scan, Skills Scan, MCP scan, AI Infra scan and LLM jailbreak evaluation.
 cr0nx/awesome-linux-attack-forensics-purplelabs
This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.
 star-sg/presentations
Curated collection of offensive security conference slide decks covering kernel and mobile exploitation, VM/container escapes, and…
 owasp/owasp-top-10-neocloud-and-ai-data-center-security-risks
OWASP framework cataloging the top 10 security risks in neocloud and AI data center infrastructure, covering hardware, networking, isolation,…
 atlasvector/kestra-cve-2026-53576
End-to-end reproduction and cross-layer detection of CVE-2026-53576, the unauthenticated RCE in Kestra - taken past the base PoC to show how a common…
 abraxas/spark-proxyuser-classpath
Apache Spark 4.2.0 - High - Remote - Privilege leftover - proxy-user defaultExtraClassPath