
openclaw-technical-analysis
 useaitechdad/openclaw-technical-analysis
This technical research and review is for educational purposes on public code and constitutes Fair Dealing under the Copyright Act (Canada).
ai-securitycode-analysiseducation+3
1
useaitechdad/openclaw-technical-analysisThis technical research and review is for educational purposes on public code and constitutes Fair Dealing under the Copyright Act (Canada).
 aenlr/strutt-cve-2014-0114
Technical analysis and proof-of-concept for Apache Struts 1 class parameter manipulation (CVE-2014-0114), demonstrating remote code execution on…
 analysis-tools-dev/static-analysis
Curated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…
 enovella/tee-reversing
A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices
 vinsontang1/vultriage
The code of VulTriage: Triple-Path Context Augmentation for LLM-Based Vulnerability Detection
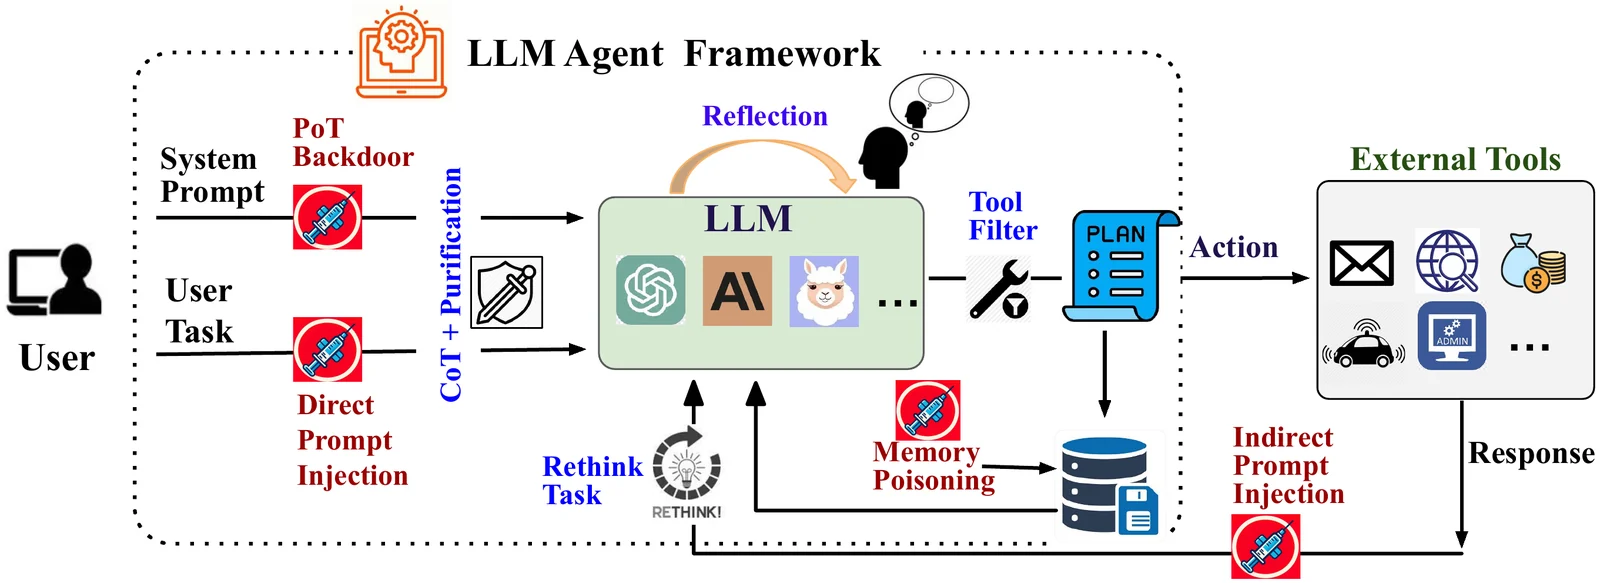 xiaoyan-lisa/defenses-for-tool-integrated-llm
Research code and experiments for defending tool-integrated LLM agents against adversarial attacks, extending Agent Security Bench with new defense…

 euph00/zoneclaw-code
Benchmark and defense code for persistent memory attacks on OpenClaw-style computer-use agents, with memory-zoning mitigation, attack scenarios, and…
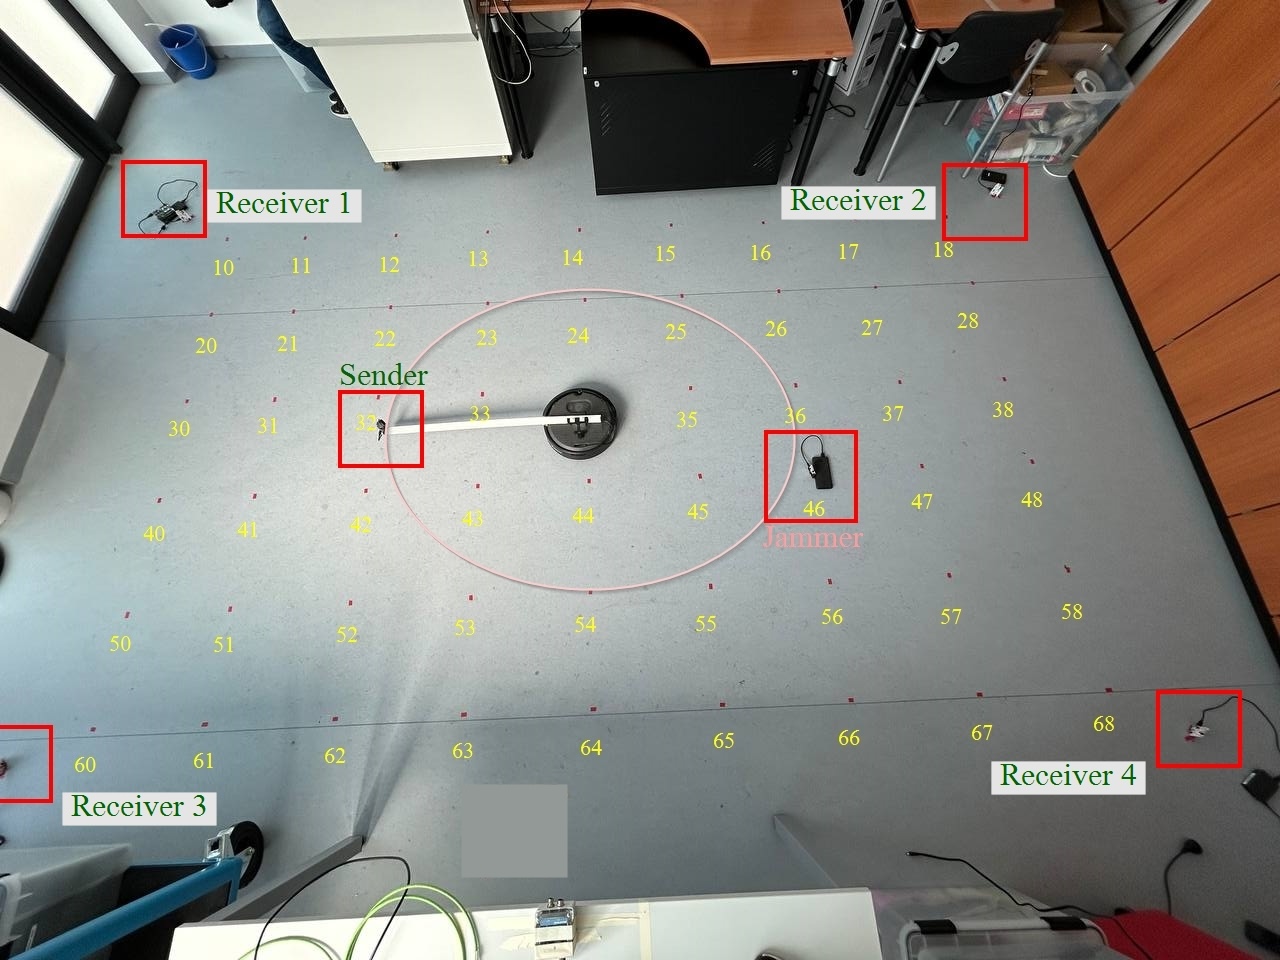 afbf4c8996f/jammer-loc
Implements machine and deep learning methods for indoor UWB jammer localization, including hyperparameter optimization, classification, and…
 alphawarheads/watermark_spoofing
Research code and dataset (WSD) for evaluating audio watermarking impact on anti-spoofing, using wav2vec2 XLS-R and knowledge-preserving learning.
 ramenfast/zenfone9-root
Temporary root (uid 0) on a bootloader-locked ASUS Zenfone 9 via CVE-2025-21479 + a perf-based physical-address leak. GPLv3.
 trinadh465/linux-4.1.15_cve-2023-4128
Linux kernel 4.1.15 source code with a focus on CVE-2023-4128, intended for vulnerability analysis and educational study of kernel security.
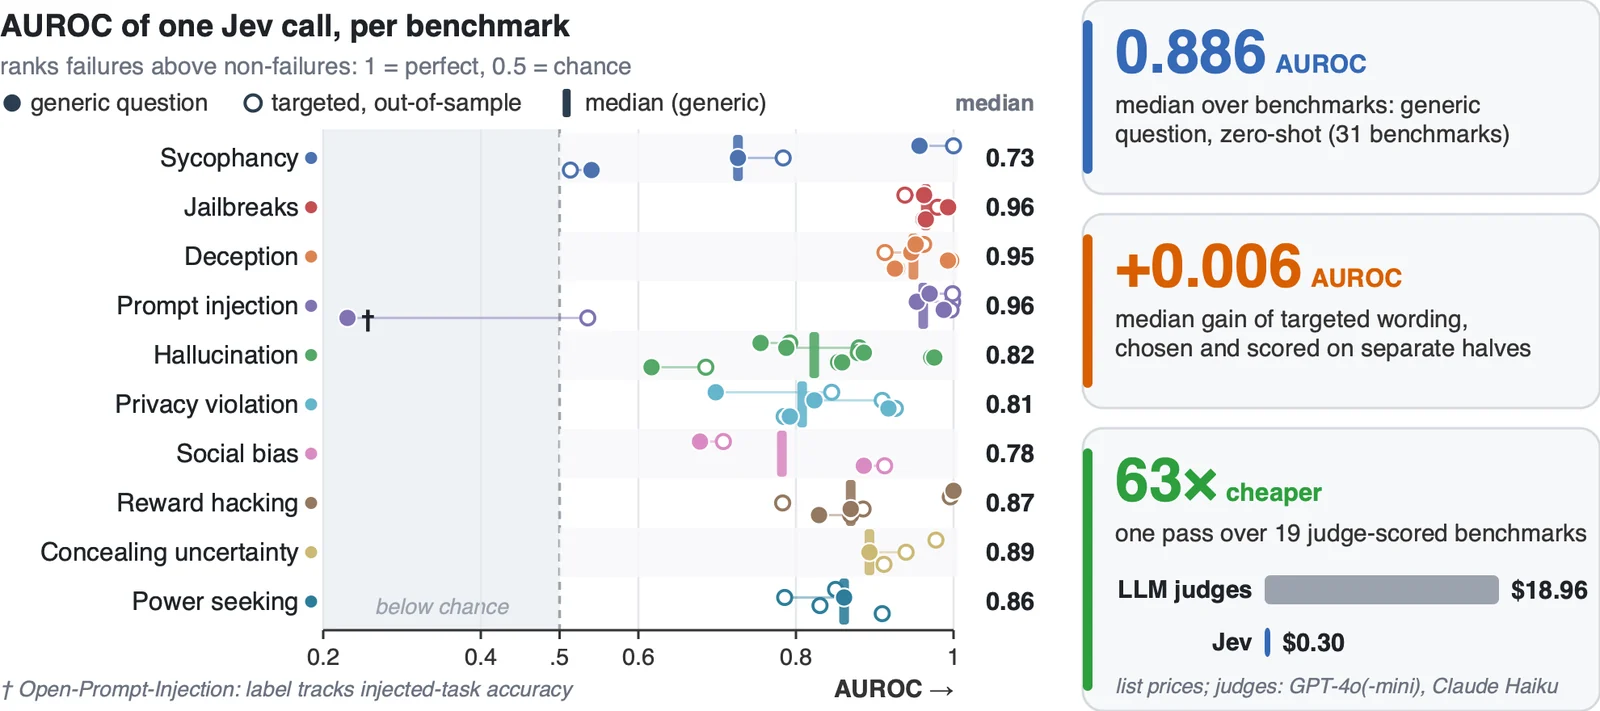 sumleo/rlcdalignbench
Benchmark suite and code for detecting AI alignment failures, with 44 benchmarks across ten failure types and a zero-shot RLCD detector evaluated on…
 theethat-thamwasin/cve-2025-56399
An authenticated Remote Code Execution (RCE) vulnerability in laravel-file-manager v3.3.1 and below allows attackers with access to the file manager…
 patois/winmagic_sd
Technical Write-Up on and PoC Exploit for CVE-2020-11519 and CVE-2020-11520
 star-laboratory/prism
PrISM: A Scalable Probabilistic RowHammer Mitigation (ISCA 2026). Ramulator2 source code and evaluation scripts.
 sizvy/cve-2021-21300
Demonstrates CVE-2021-21300 arbitrary code execution via malicious Git hooks on case-insensitive filesystems, including exploit steps and defensive…
 sandi-go/cve-2019-0678
Microsoft Edge Elevation of Privilege Vulnerability