
CVE-2025-57298
 minnggyuu/cve-2025-57298
CVE-2025-57298 Disclosure.
educationpapers-researchvulnerability-analysis+2
minnggyuu/cve-2025-57298CVE-2025-57298 Disclosure.
 runzeroinc/sshamble
Research tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.
 edoardottt/cve-2025-67511
Detailed disclosure of CVE-2025-67511, a command injection vulnerability in the CAI framework's SSH tool that allows AI agents to be tricked into…
 0xmrma/cve-2026-46552
NocoDB Shared-Base Links Could Invite Real Base Members and Survive Share Revocation
 cavi-au/consent-o-matic
Browser extension that automatically fills out cookie popups based on your preferences
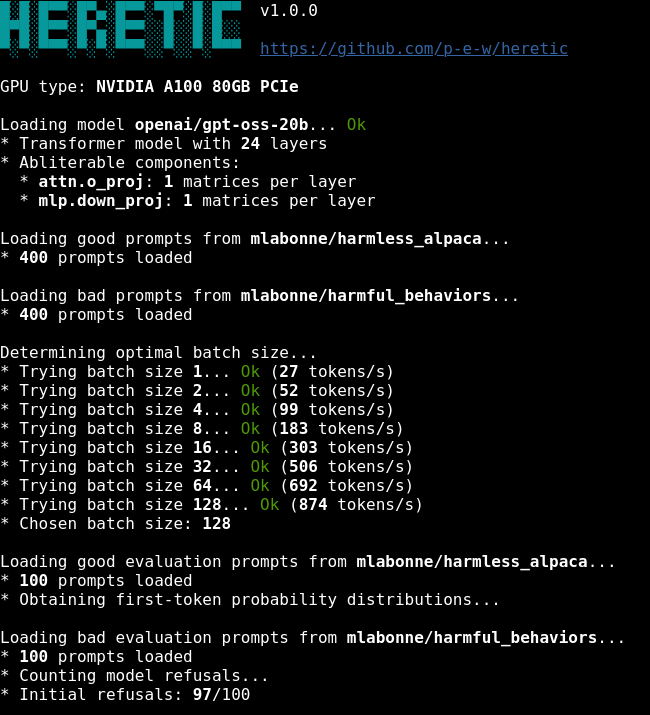 p-e-w/heretic
Fully automatic censorship removal for language models
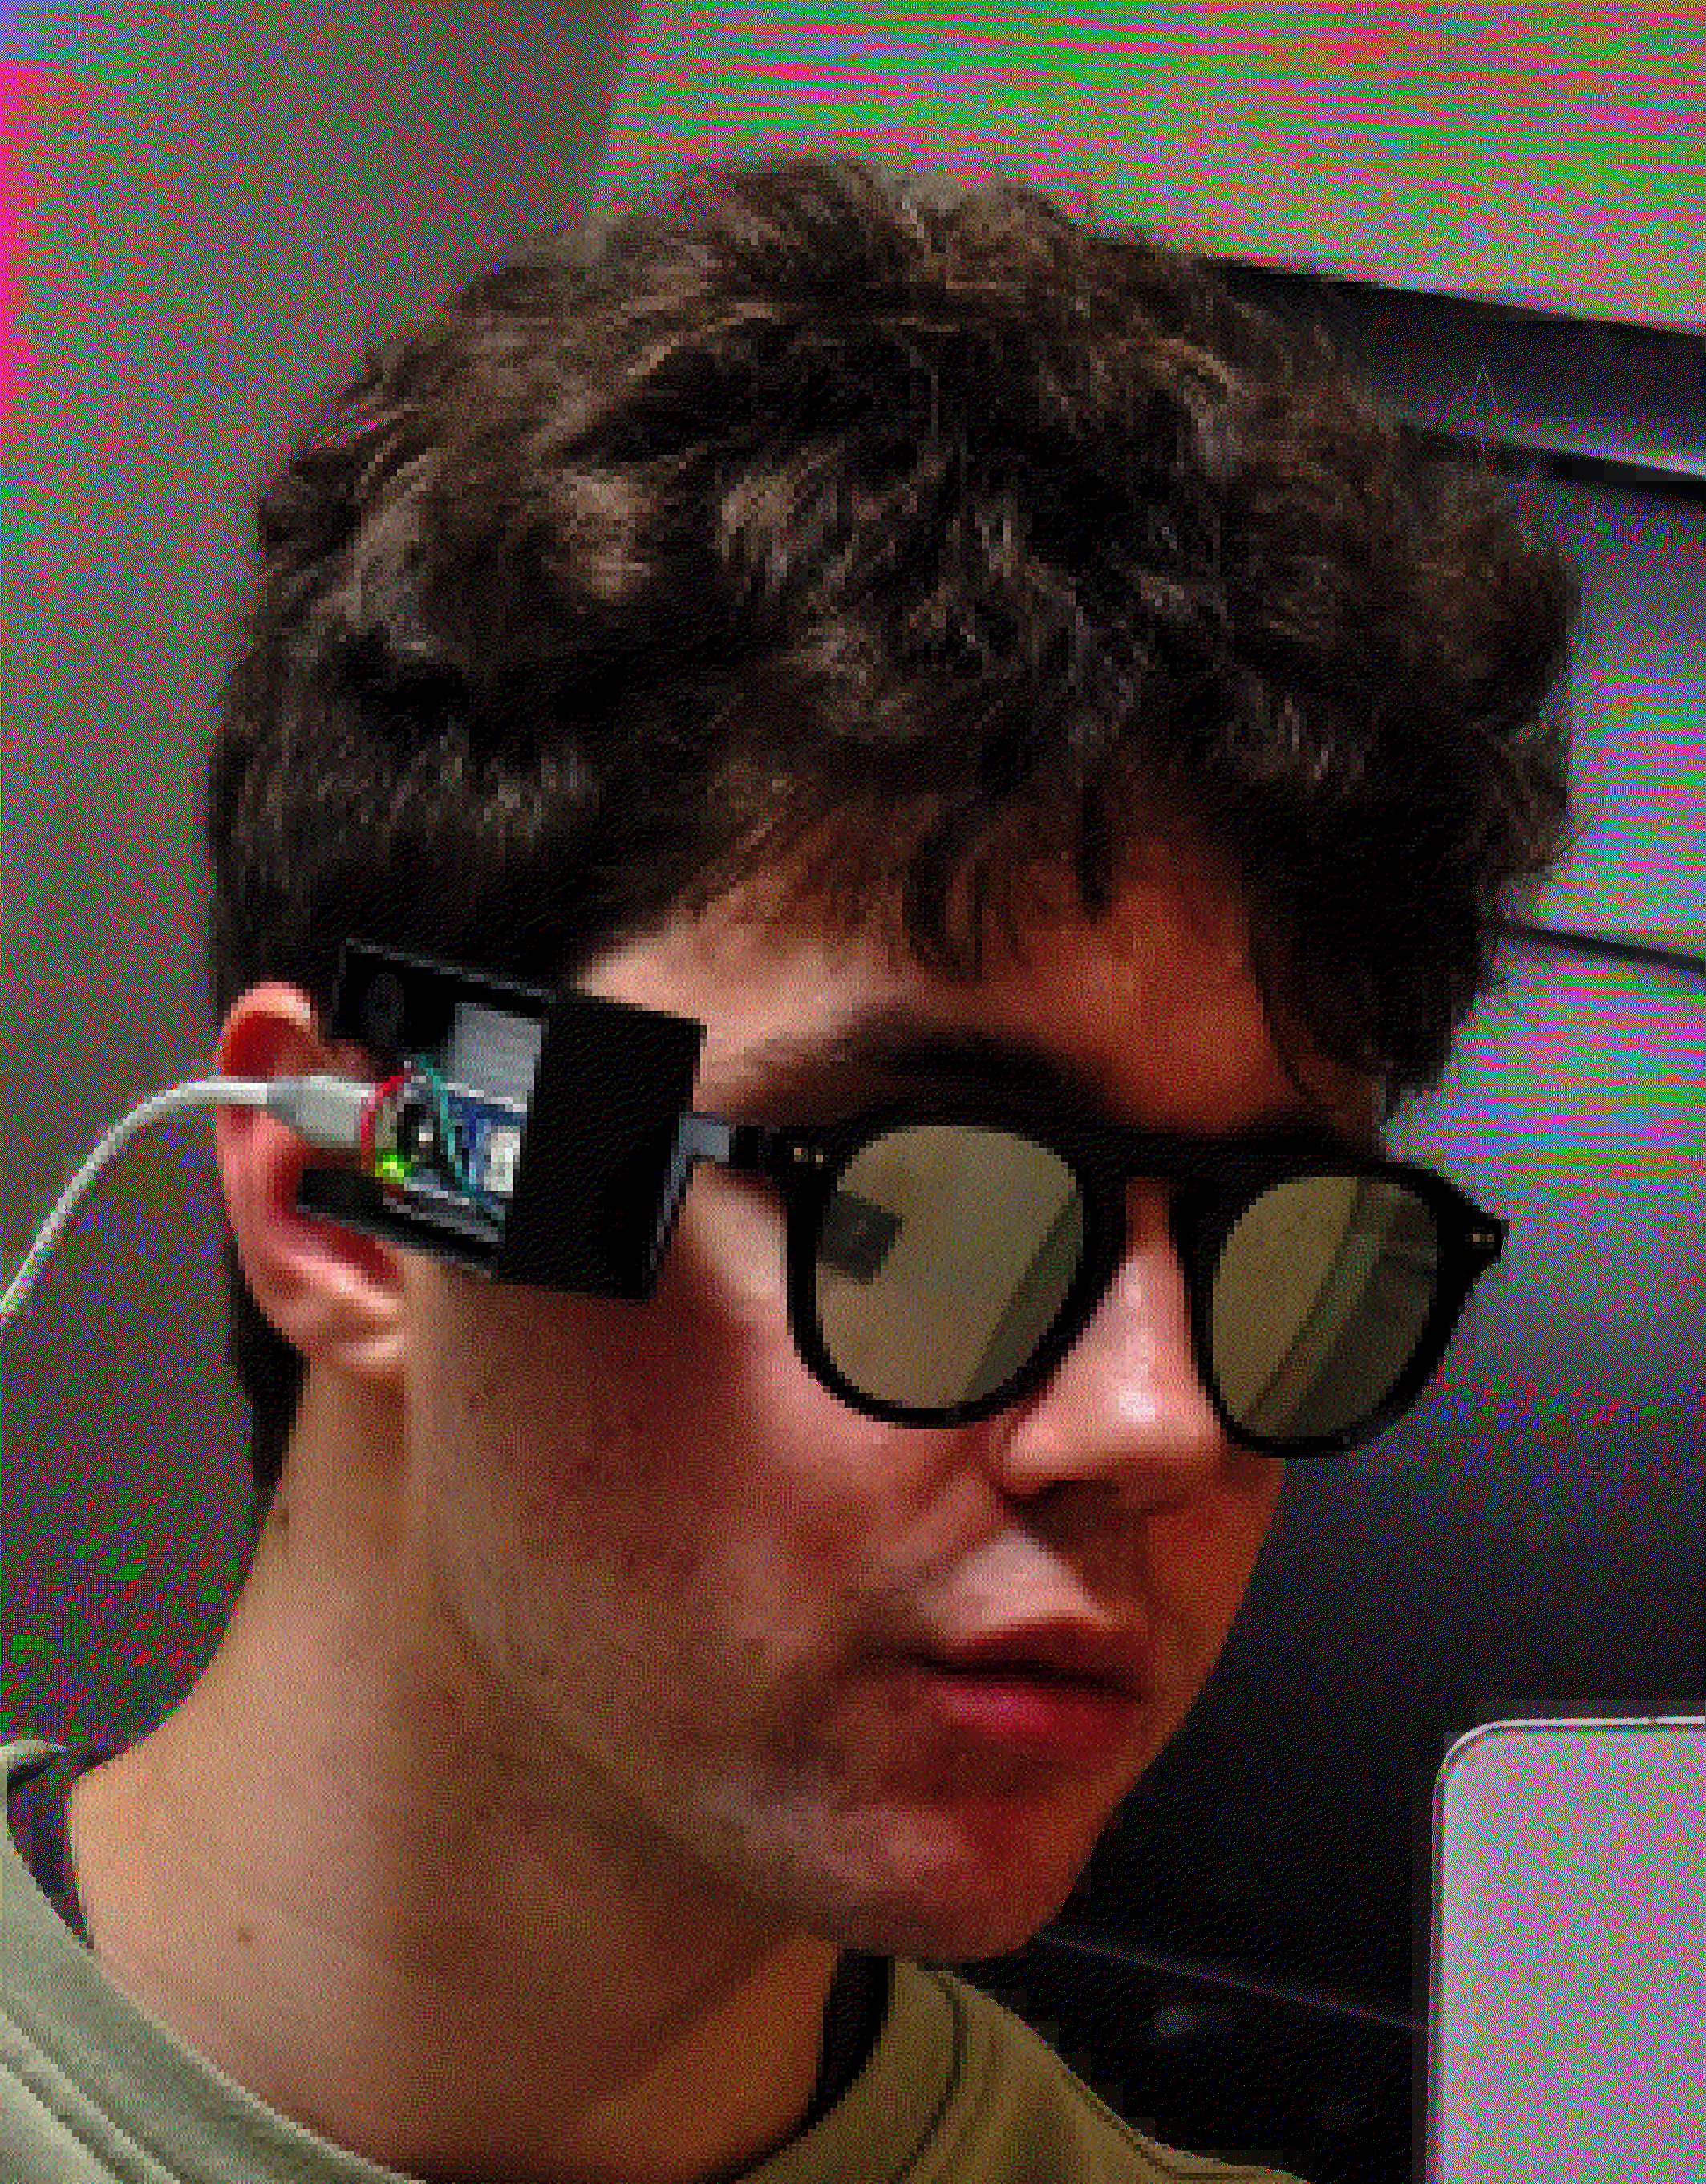 nullpxl/banrays
Glasses to detect smart-glasses that have cameras. Ray-BANNED
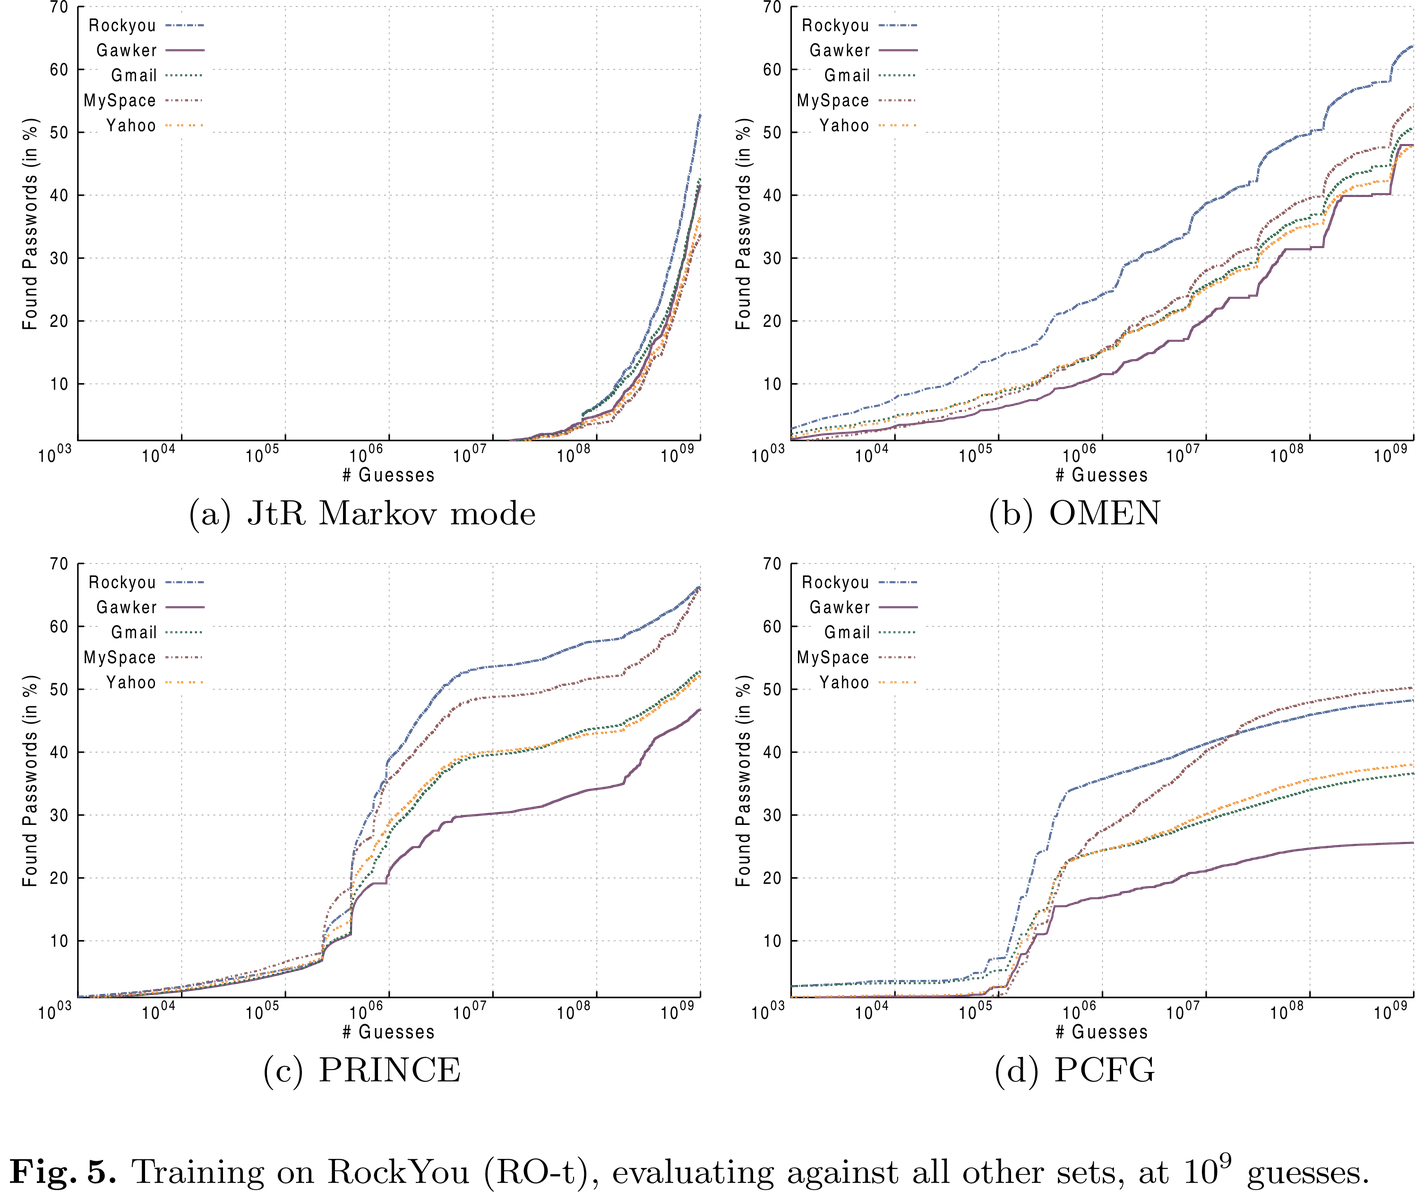 rub-syssec/omen
Markov model-based password guesser in C that enumerates candidates by probability, generating most likely passwords first for hash cracking via…
 thesisgroup3/secassessment_gapdetect
Rule-based CLI tool that grades organizational defenses against MITRE ATT&CK and D3FEND frameworks, detects security gaps, and proposes mitigations.…
 bytereaper77/jump-over-aslr-btb
jump over aslr attacking branch predictors to bypass aslr Technique
 i12gocaj/instagram-notes-audio-leakage-via-url-extraction-fixed
Informe técnico de una vulnerabilidad ya corregida en Instagram Notes que exponía el audio original de vídeos mediante URLs directas.
 ethannjc/cve-2012-1723
Proof of concept exploit for CVE-2012-1723
 imthecopilotnow/cve-2025-492025
Detailed security advisory for CVE-2025-492025, documenting a UI misrepresentation vulnerability in Copilot AI that injects unintended hyperlinks…
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
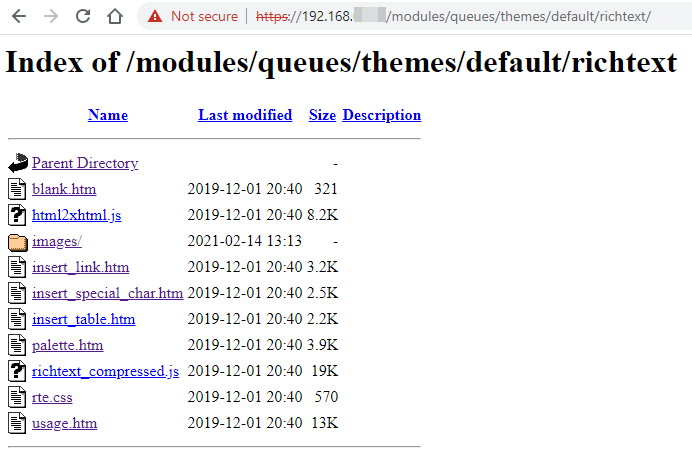 sahiloj/cve-2023-37599
Issabel-pbx version 4.0.0-6 contains a Broken Access Control vulnerability that manifests as unauthenticated Directory Listing on the web interface.
 infostealers-stats/credential-and-breach-monitoring
This repository provides a practical comparison of breach intelligence, dark web monitoring, and identity exposure services, with a focus on factors…
 mohshomis/modo
Curated collection of cybersecurity learning resources, CTF writeups, research papers, and practical labs for hands-on skill development across web…
 sbamit/exponentiated-gradient-descent-llm-attack
A novel adversarial attack on LLM based on the Exponentiated Gradient Descent technique.