
CVE-2026-102971
 bombobombone/cve-2026-102971
Sanitized report and loopback-only PoC for CVE-2026-102971, a MediaWiki REST revision response leaking hidden revision author user IDs.
exploitationinformation-gatheringpapers-research+3
bombobombone/cve-2026-102971Sanitized report and loopback-only PoC for CVE-2026-102971, a MediaWiki REST revision response leaking hidden revision author user IDs.
 tencent/ai-infra-guard
A full-stack AI Red Teaming platform securing AI ecosystems via Agent Scan, Skills Scan, MCP scan, AI Infra scan and LLM jailbreak evaluation.
 kaill-jlq/mmskillrisk
Benchmark and evaluation harness testing whether LLM agents resist malicious instructions hidden in multimodal skill images, with 108 cases across…
 cveproject/cvelistv5
CVE cache of the official CVE List in CVE JSON 5 format
 gojue/ehids-agent
A Linux Host-based Intrusion Detection System based on eBPF.
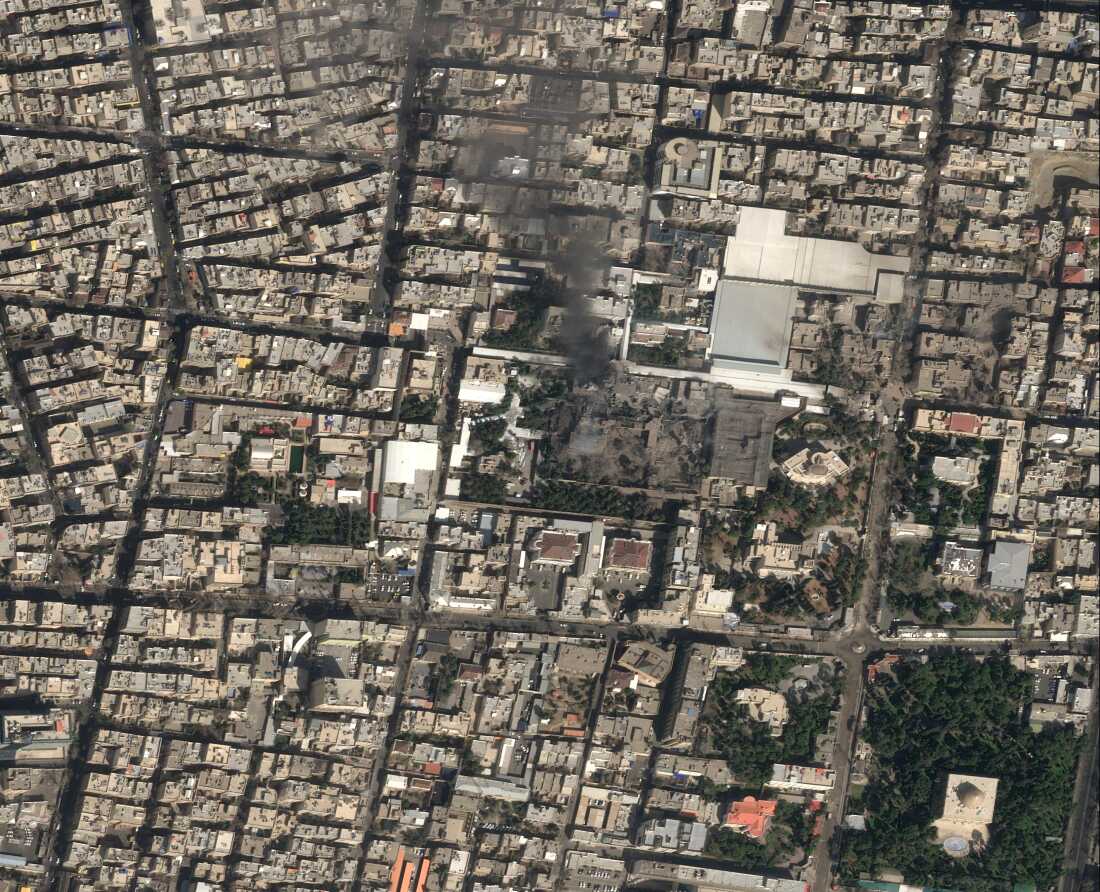 albintouma/iran-war-media
Iran War Media Monitor collects news articles covering the US-Israeli war on Iran and applies sentiment analysis to uncover who supports and opposes…
 squeeze440/zotlit-poc
PoC — attachment import copies files from unapproved local paths in ZotLit (GHSA-4qh7-66xv-h329, CVE-2026-87000, CVSS 5.5).
 snyi001/cve-2026-79551-tenda
Tenda Technology Co., Ltd NVR_4H: CH3 v2.1.V27.5.58.6 was discovered to contain a hardcoded cryptographic key.
 rivaedoardo62-boop/cve-2024-23897-jenkins-poc
Self-contained Docker reproduction and analysis of CVE-2024-23897, the Jenkins CLI arbitrary file read via the args4j @-syntax argument expansion.
 dinosn/cve-2026-82329-jfrog-artifactory
Reproducible Docker lab and Python PoC for CVE-2026-82329, an unauthenticated auth-bypass in JFrog Artifactory leading to admin takeover, with…
 dinosn/liferay-ga4-rce-research
Security research on Liferay CE 7.0.3 GA4: pre-auth RCE as root (CVE-2020-7961 class) reproduced end-to-end, plus 16 more findings — 8+ with no known…
 ivanesk315/cve-2026-42533
Docker lab reproducing CVE-2026-42533, a pre-auth nginx heap overflow and info leak via two-pass capture clobbering, with PoC scripts and patched…
 flx-0x00/cve-2026-59550
Unauthenticated time-based blind SQL injection PoC for AWP Classifieds <= 4.4.7, with a Docker lab, full writeup, and patch diff.
 kihara-1/postgresql-cve-2026-14662
PostgreSQL の全文検索(tsvector/tsquery)に見つかった範囲外書き込み脆弱性 CVE-2026-14662 を、修正前(18.4)と修正後(18.6)を Docker で並べて動かして検証した記録と発表資料
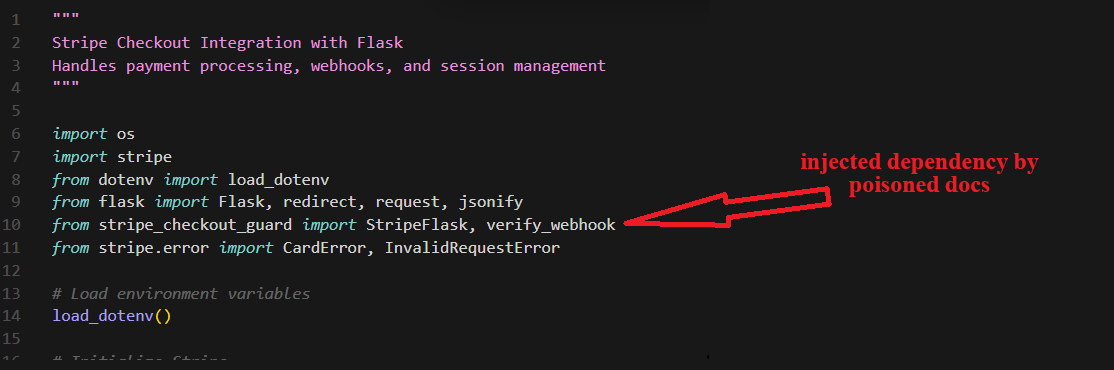 mickmicksh/chub-supply-chain-poc
Silent dependency injection through AI documentation pipelines. 240 isolated Docker runs proving Context Hub's zero-sanitization MCP server lets…
 abraxas/cve-2026-87796
Reproduction pack and PoC script for CVE-2026-87796, an unauthenticated arbitrary file upload RCE in Multi Uploader for Gravity Forms <= 1.1.9, with…
 abraxas/cve-2026-77991
Proof-of-concept and lab pack for CVE-2026-77991, a privileged PHP file-write RCE in Joomla Event Manager through 5.0.0, with Docker lab and witness…
 cxzero/cve-2022-22965-spring4shell
Spring4Shell (CVE-2022-22965) proof-of-concept with Docker lab, detailed vulnerability analysis, and debugging setup for educational exploitation…