

awesome-industrial-control-system-security
 hslatman/awesome-industrial-control-system-security
A curated list of resources related to Industrial Control System (ICS) security.
curated-resourcesexploitationfuzzing+9
2.0k
hslatman/awesome-industrial-control-system-securityA curated list of resources related to Industrial Control System (ICS) security.
 meta-llama/purplellama
Set of tools to assess and improve LLM security.
 0xqrx/vulnerabilityresearch
Collection of vulnerability research write-ups and proof-of-concept exploit scripts for educational and research purposes.
 c2sp/wycheproof
Project Wycheproof tests crypto libraries against known attacks.
 nccgroup/rfc-security-research
Paper, data and code from Investigating Potential Security Vulnerability Manifestation through Various Analyses & Inferences Regarding Internet RFCs
 ossf/criticality_score
Computes a criticality score for open source projects from repository, contributor, and dependency metrics to prioritize security improvements.
 runzeroinc/sshamble
Research tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.
 abraxas/nextcloud-calendar-sharee-publish
Nextcloud 35.0.0 — a calendar edit-sharee can publish the owner's calendar to an unauthenticated URL
 squeeze440/gortex-poc
PoC — symlink following to out-of-repo content disclosure via search_text in Gortex (GHSA-6vhf-4wcm-2r83, CVE-2026-87003, CVSS 5.5).
 eset/malware-research
Code written as part of our various malware investigations
 watchtowrlabs/watchtowr-vs-atlassian-cve-2026-21589
Python detection artifact that checks Atlassian Jira, Confluence, and Bitbucket instances for the CVE-2026-21589 arbitrary file read vulnerability.
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
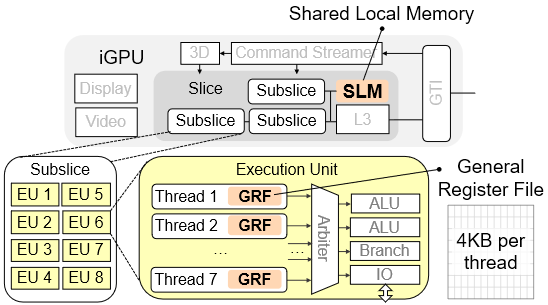 he-wenjian/igpu-leak
[CVE-2019-14615] iGPU Leak: An Information Leakage Vulnerability on Intel Integrated GPU
 rafabd1/vectorfreed
Documents the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…
 yairhinkis/cve-2026-56096
Proof of concept and technical write-up for CVE-2026-56096, a blind Solr query injection in TYPO3 EXT:solr enabling unauthenticated field enumeration…
 abraxas/spark-rpc-stream-unauth
Apache Spark 4.2.0 - High - Remote - File read - unauth RPC StreamRequest File join
 bombobombone/cve-2026-102971
Sanitized report and loopback-only PoC for CVE-2026-102971, a MediaWiki REST revision response leaking hidden revision author user IDs.