
spip-exploits
 ambionics/spip-exploits
Python exploit chain for SPIP CVEs 2026-72708/72709/72710, chaining unauthenticated SQL injection to account takeover and remote code execution.
exploitationexploit-frameworkspapers-research+4
2
ambionics/spip-exploitsPython exploit chain for SPIP CVEs 2026-72708/72709/72710, chaining unauthenticated SQL injection to account takeover and remote code execution.
 pedrib/poc
Advisories, proof of concept files and exploits that have been made public by @pedrib.
 jbaines-r7/cisco_asa_research
Cisco ASA Software and ASDM Security Research
 tankirat/cve-2017-5638
Educational analysis of Apache Struts 2 RCE vulnerability CVE-2017-5638, including exploit details, Equifax case study, and prevention measures.
 greydgl/pentestgpt
Automated Penetration Testing Agentic Framework Powered by Large Language Models
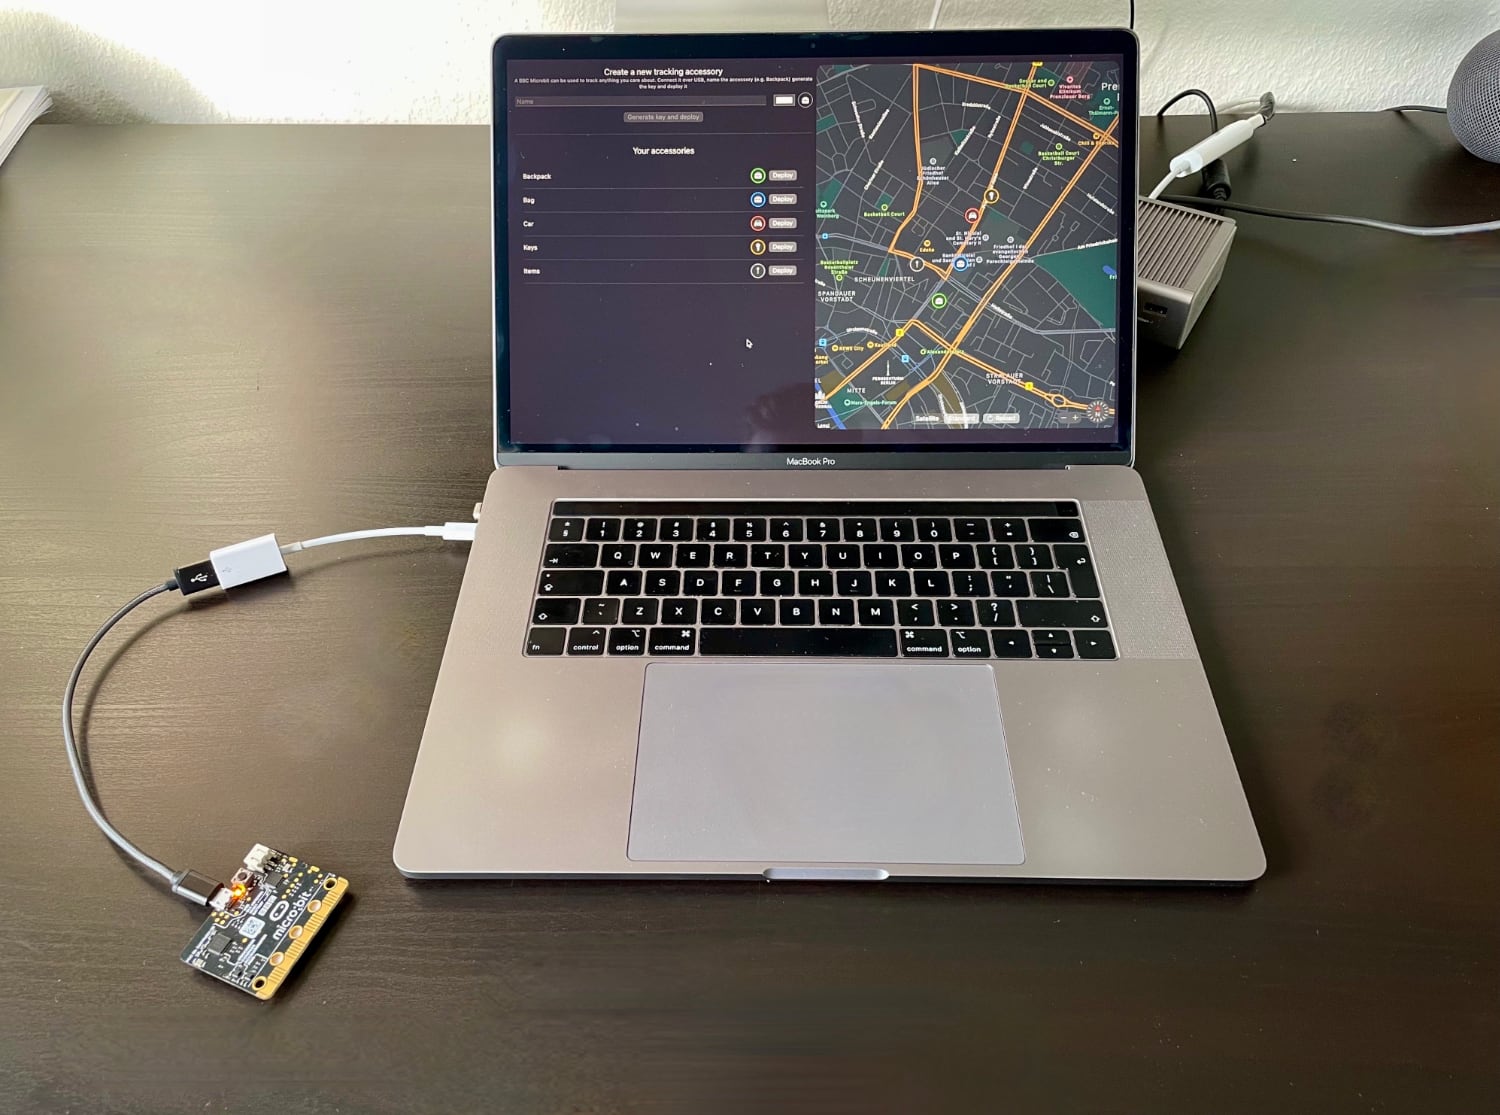 seemoo-lab/openhaystack
Build your own 'AirTags' 🏷 today! Framework for tracking personal Bluetooth devices via Apple's massive Find My network.
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 mrphrazer/msynth
Code deobfuscation framework to simplify Mixed Boolean-Arithmetic (MBA) expressions
 poppopjmp/vmdragonslayer
Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 plum-umd/redexer
The Redexer binary instrumentation framework for Dalvik bytecode
 canyie/cve-2024-0044
Proof-of-concept and writeup for bypassing the initial patch of CVE-2024-0044, an Android framework vulnerability enabling privilege escalation from…
 project-artist/artist
Open-source instrumentation framework for Android apps and Java middleware, modifying code during on-device compilation via the ART compiler.…
 bw3ll/jop_rocket
This framework enables user to discover JOP gagdets and can automate building a complete JOP chain to bypass DEP. JOP ROCKET is the ultimate solution…
 zju-llm-safety/trace
Agentic jailbreak framework for LLM-based agents using scheme-based task decomposition, multi-turn disguising strategies, and adaptive self-evolution…
 neuralprogram/qlcoder
Agentic Framework for Synthesizing CodeQL Queries
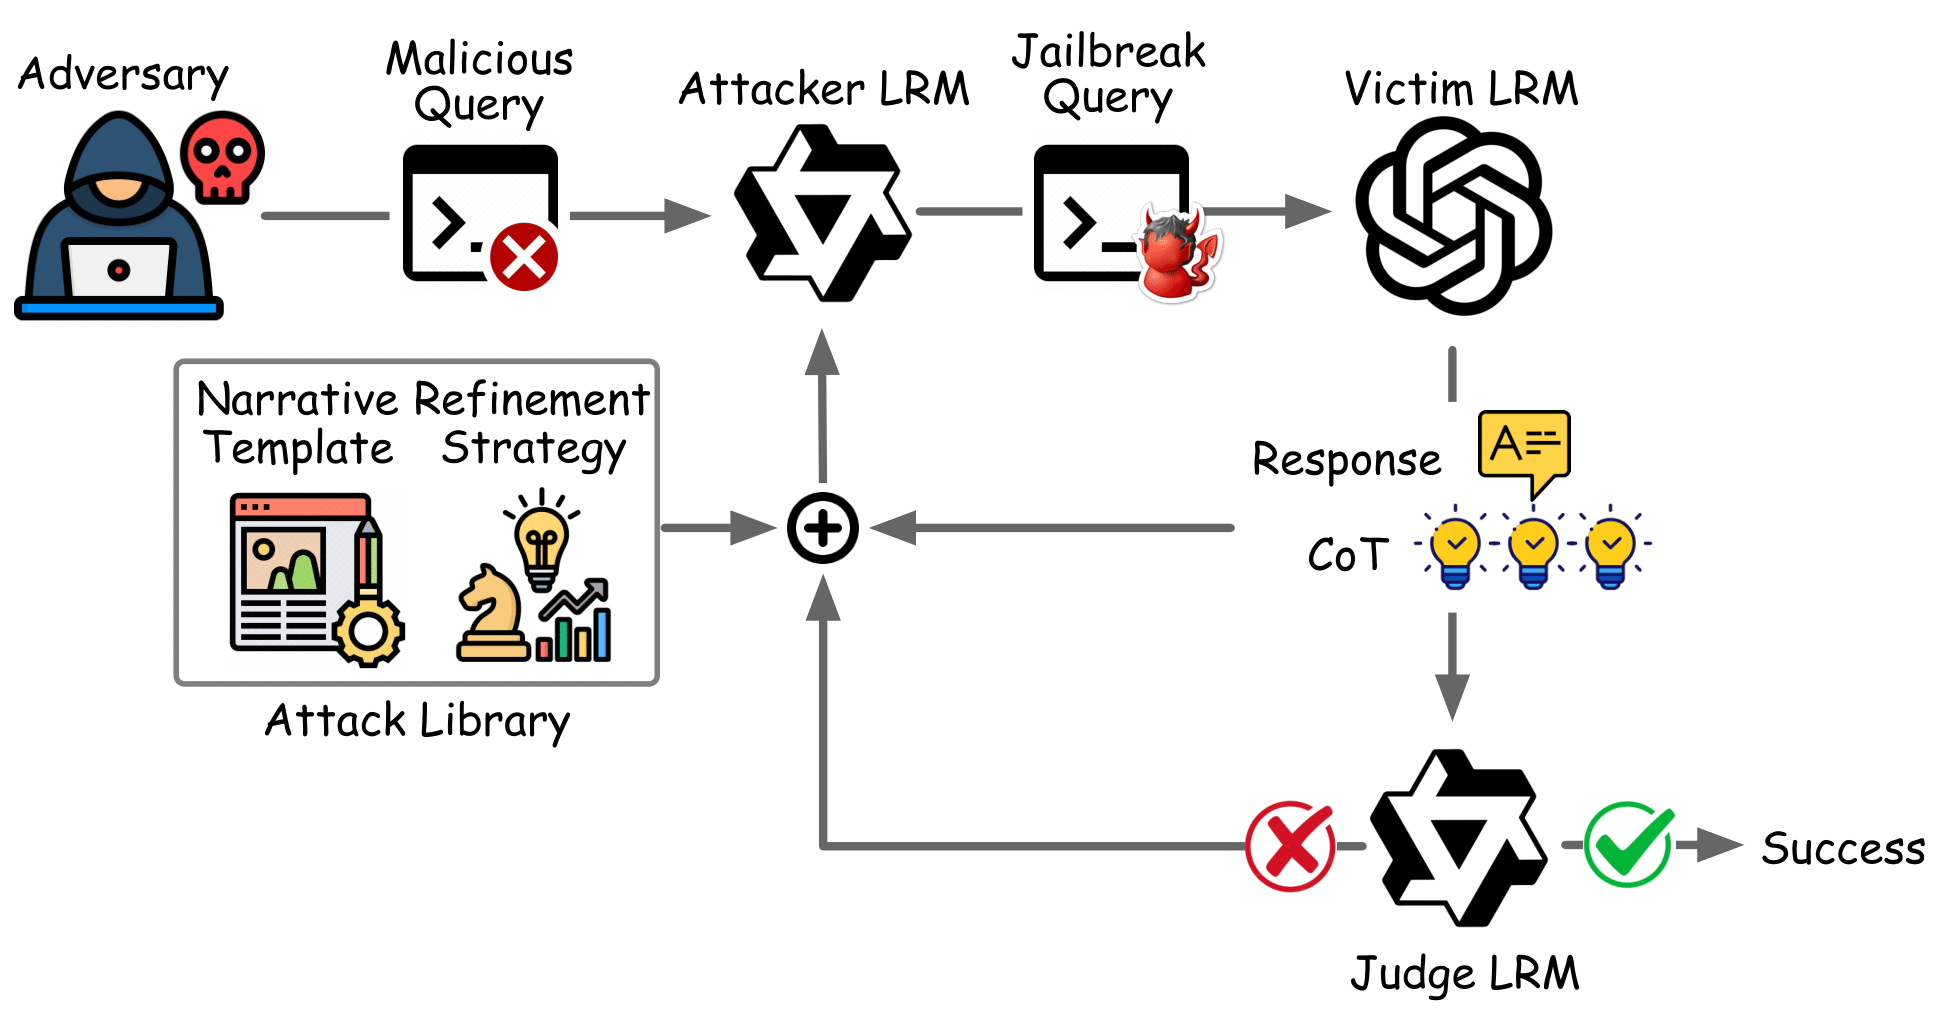 jackpurcell/autoran-public
Automated framework for hijacking safety reasoning in large reasoning models via simulated reasoning traces and iterative prompt refinement to…