
CVE-2026-30252
 venablee/cve-2026-30252
The ZenShare Suite application is vulnerable by a Reflected Cross-Site Scripting (XSS) vulnerability, affecting web application login and recovery…
educationexploitationpapers-research+2
venablee/cve-2026-30252The ZenShare Suite application is vulnerable by a Reflected Cross-Site Scripting (XSS) vulnerability, affecting web application login and recovery…
 huyvo2910/cve-2525-25748-cross-site-request-forgery-csrf-vulnerability-in-hoteldruid-3.0.7
Detailed CVE-2025-25748 proof-of-concept and analysis of a CSRF vulnerability in HotelDruid 3.0.7, including exploitation flow, impact assessment,…
 mlily2024/final-project-sql-injection-pipeline
Hybrid machine-learning pipelines for detecting SQL injection in web traffic, combining DistilBERT and BERT-GNN models with adversarial training and…
 secsys-fdu/cve-2025-51864
Proof-of-concept for a reflected XSS vulnerability in AIBOX's chat component, demonstrating JWT token theft and account hijacking via crafted…
 tankirat/cve-2017-5638
Educational analysis of Apache Struts 2 RCE vulnerability CVE-2017-5638, including exploit details, Equifax case study, and prevention measures.
 sahiloj/cve-2023-37190
A Stored Cross-Site Scripting (XSS) vulnerability exists in Issabel-PBX version 4.0.0-6. The application fails to properly sanitize and encode…
 bohops/ultimatewdacbypasslist
A centralized resource for previously documented WDAC bypass techniques
 owasp/secure-headers-project
OWASP knowledge base and validator for HTTP security response headers, providing recommendations, statistics, and automated configuration checks.
 selinuxproject/selinux-notebook
Comprehensive open-source book on SELinux covering kernel components, userspace libraries, policy toolchain, and policy language. Includes build…
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages
 0x3c3e/slides
CodeQL + DTrace = Memory Disclosure Vulnerabilities in XNU
 d3sre/intelligentprocesslifecycle
The Intelligent Process Lifecycle of Active Cyber Defenders
 sorami-consulting-au/ai-kubernetes-helm-chart-security
Evidence and data for the Sorami technical report on security defaults of 15 AI serving, vector database and MCP Helm charts on Kubernetes.
 abraxas/pfsense-limiter-aqm
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - Config injection - limiter AQM newline
 abraxas/pfsense-bsnmpd-conf
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - Config injection - bsnmpd syslocation
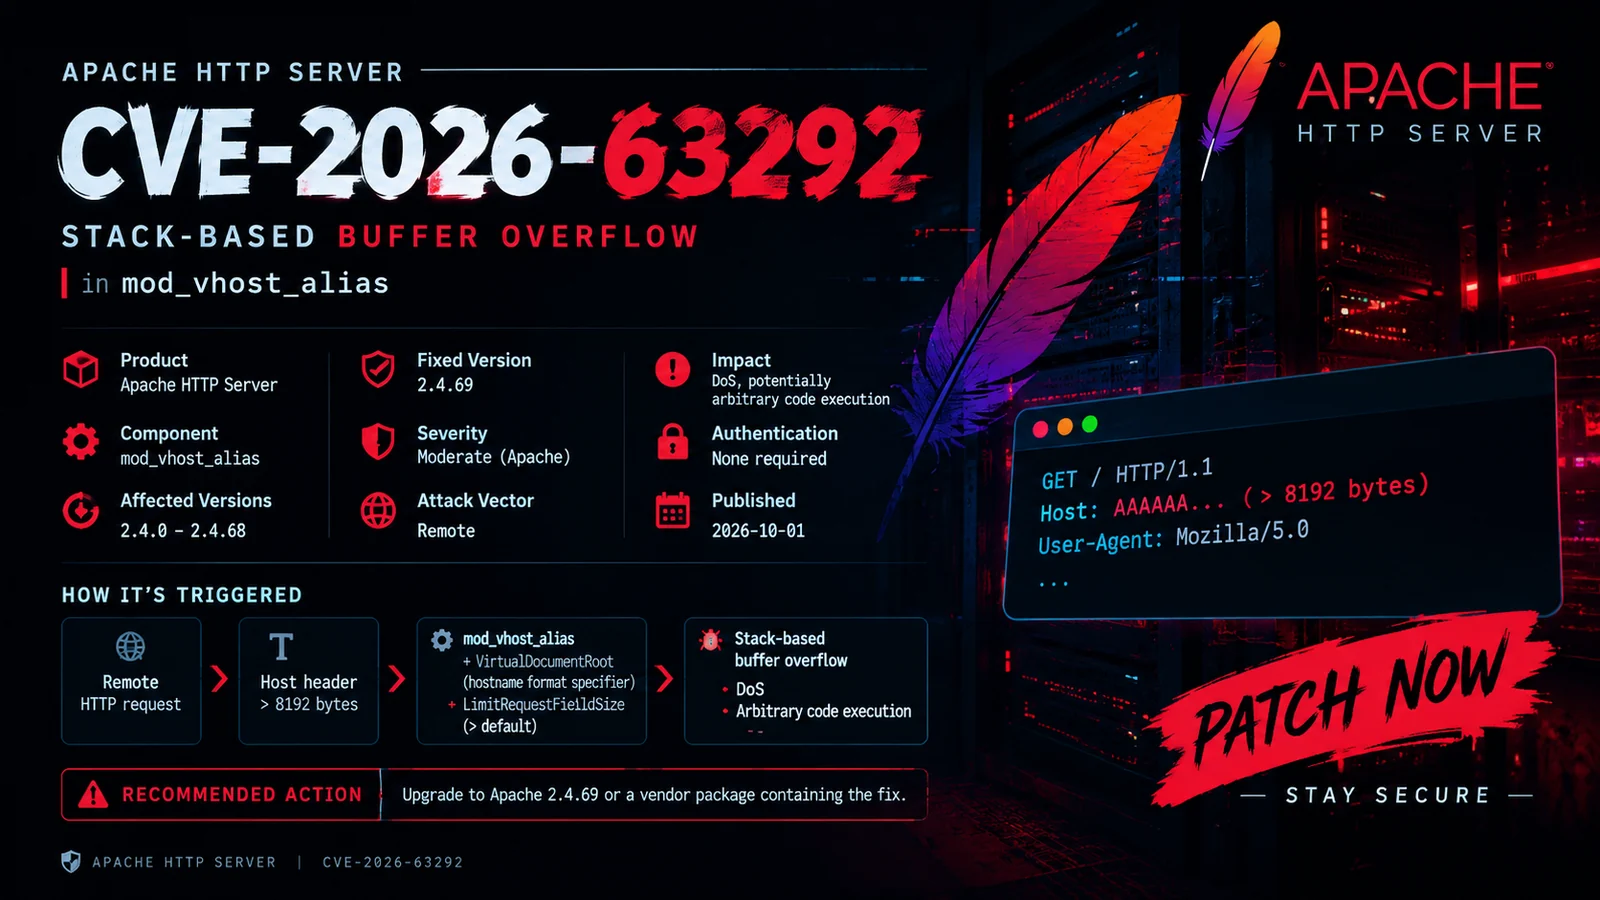 0xblackash/cve-2026-63292
Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and…