
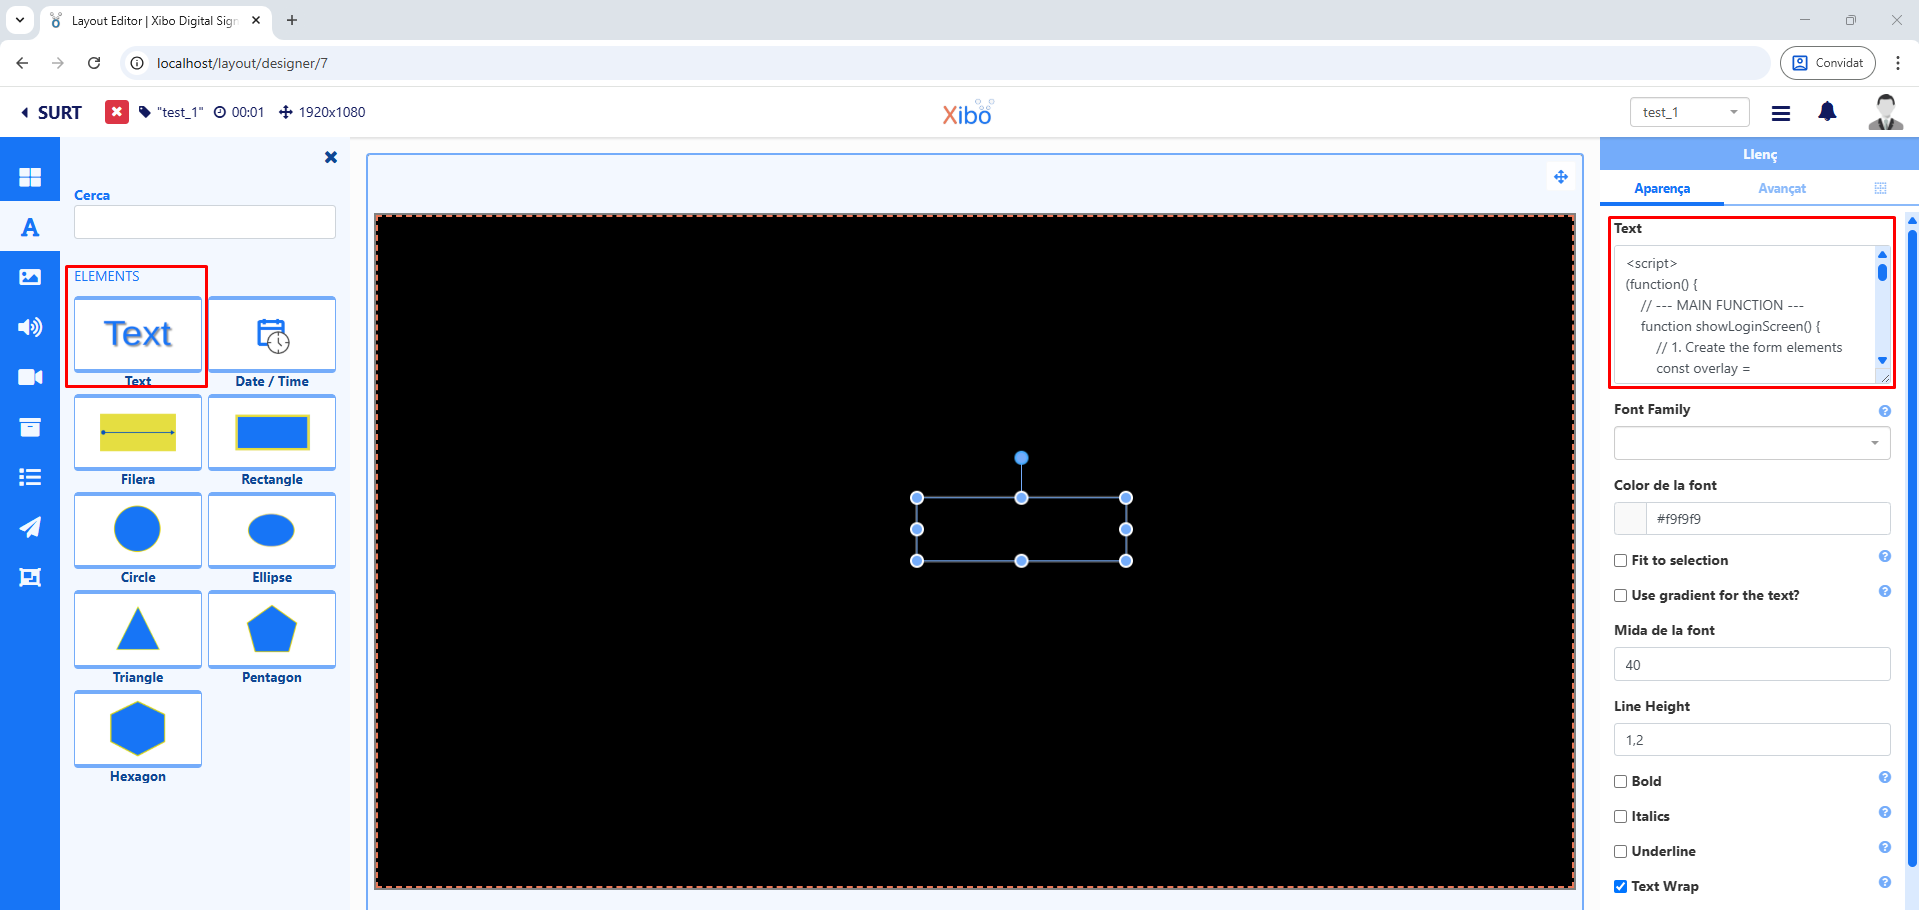
CVE-2025-41088
 marinafabregat/cve-2025-41088
Stored Cross-Site Scripting (XSS) in Xibo Signage's Xibo CMS v4.1.2, due to a lack of proper validation of user input.
educationexploitationpapers-research+3
5
marinafabregat/cve-2025-41088Stored Cross-Site Scripting (XSS) in Xibo Signage's Xibo CMS v4.1.2, due to a lack of proper validation of user input.
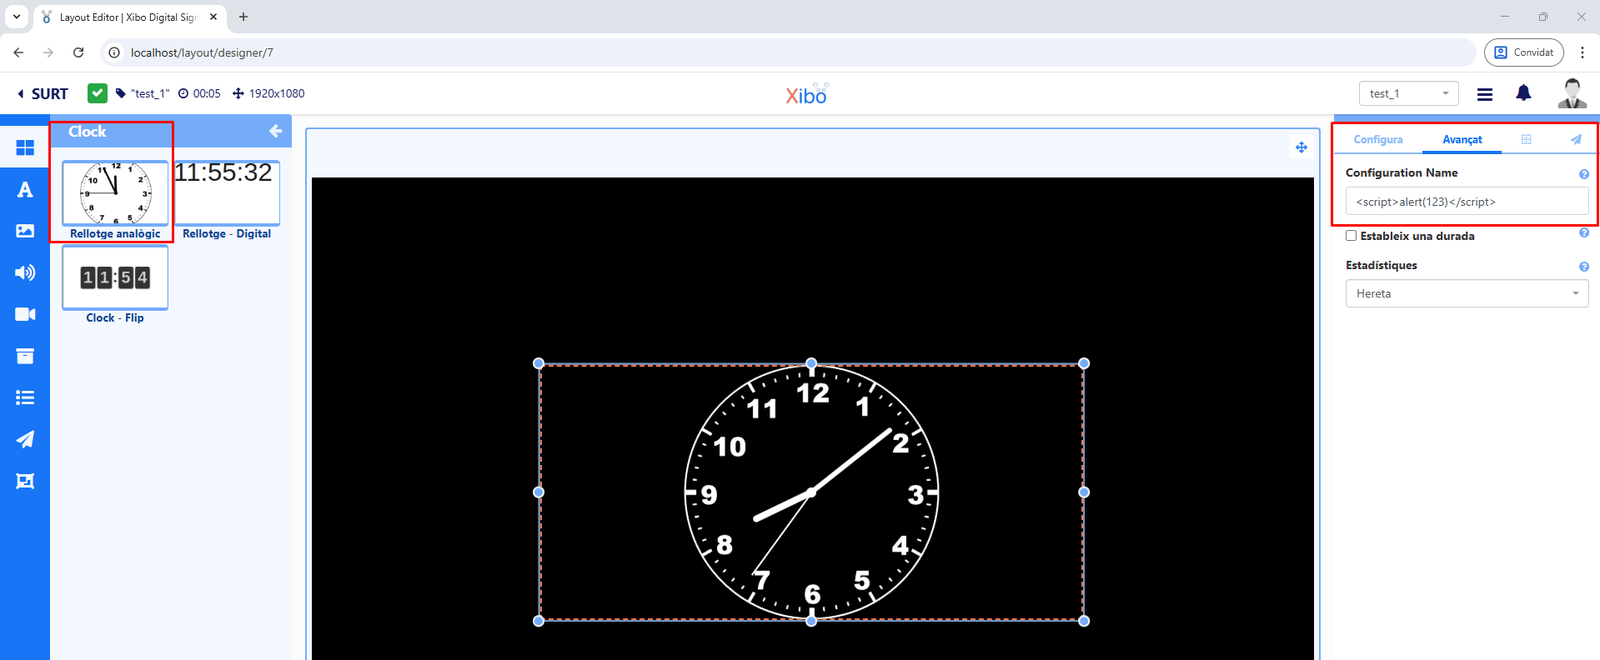 marinafabregat/cve-2025-41089
Reflected Cross-Site Scripting (XSS) in Xibo CMS v4.1.2 from Xibo Signage, due to a lack of proper validation of user input.
 hellboy3110/cve-2026-16219-croogo-lab
Safely demonstrates CVE-2026-16219 path traversal in Croogo CMS with a loopback-only PoC, technical analysis, remediation guidance, and standalone…
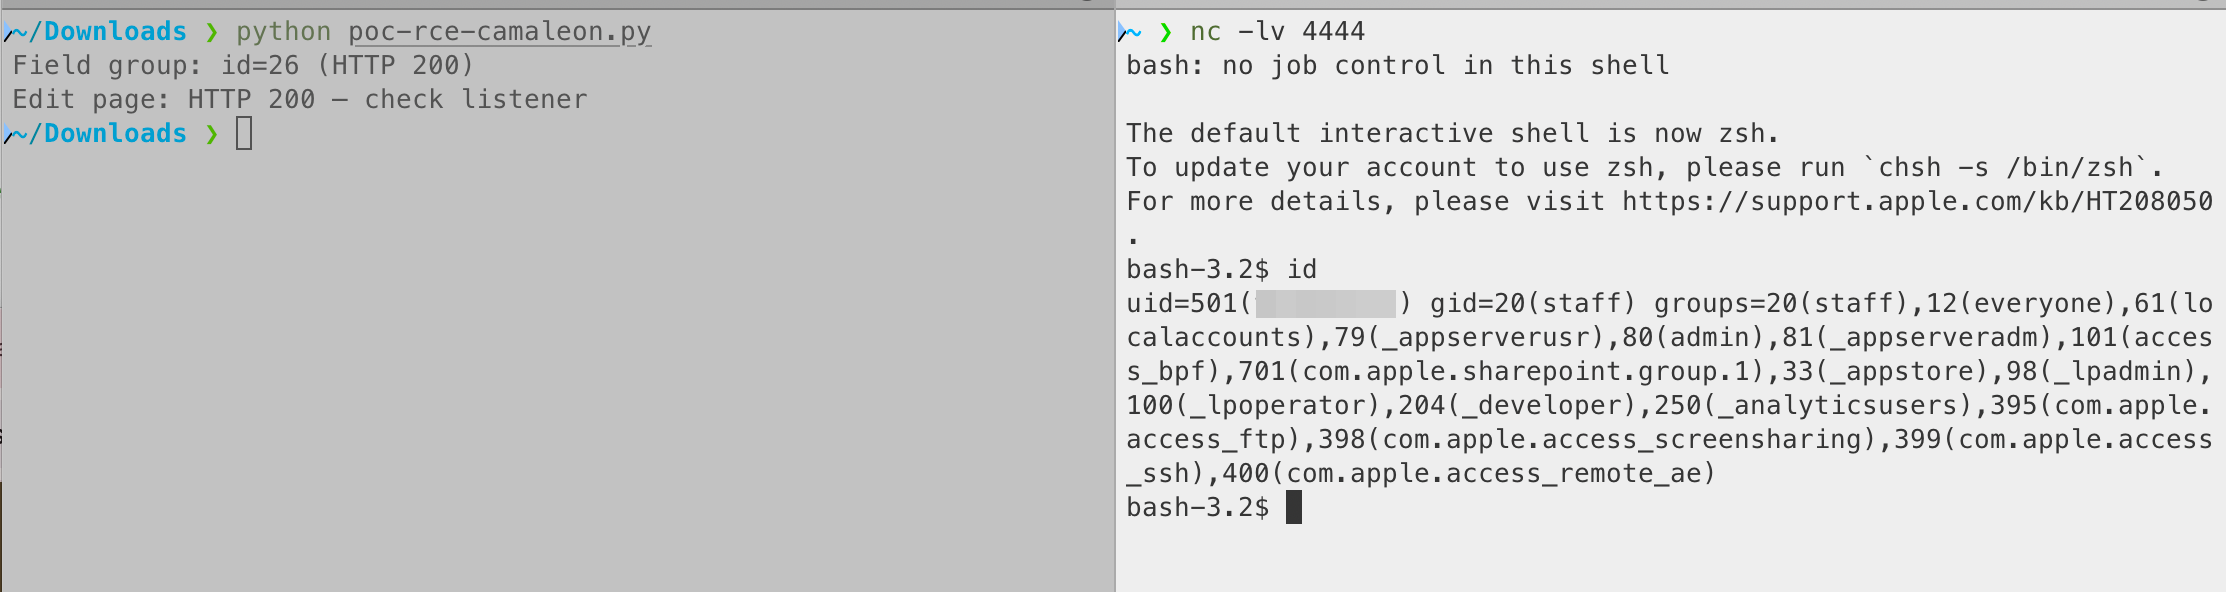 theopaid/cve-2026-66748-camaleon-cms---authenticated-rce-via-select_eval-custom-field
Security Advisory: Camaleon CMS - Authenticated RCE via `select_eval` Custom Field
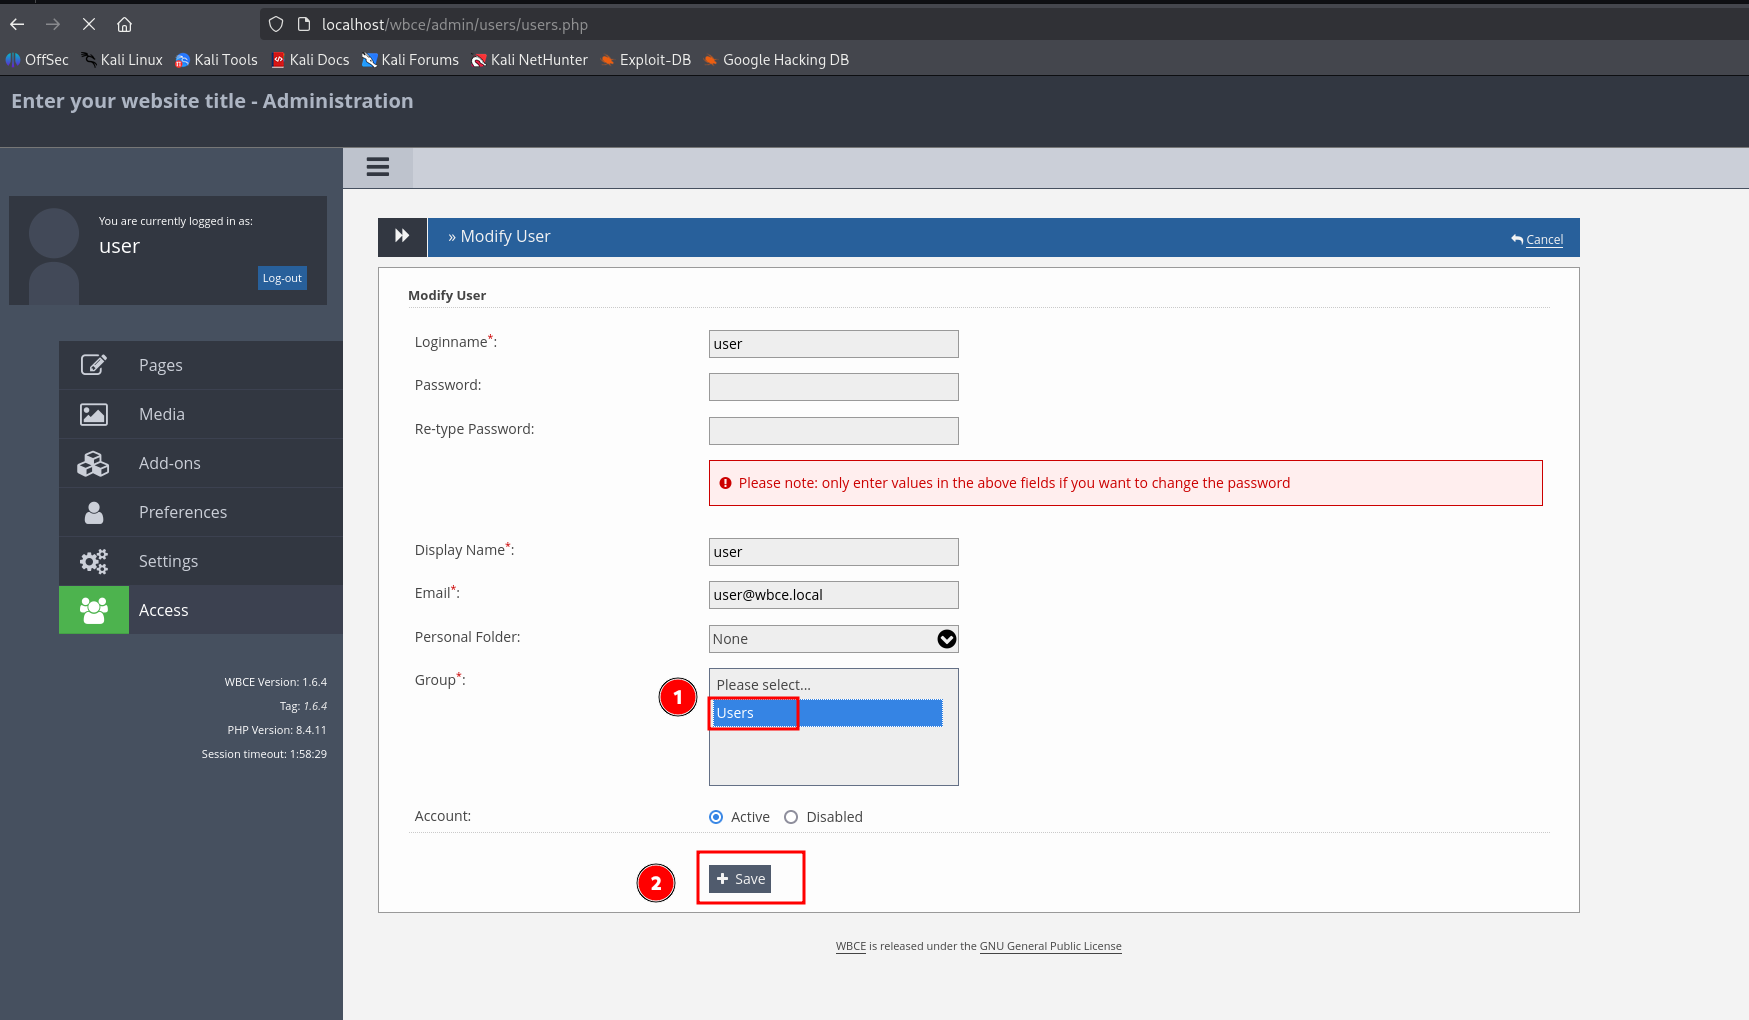 lukasz-rybak/cve-2025-65094
Proof-of-concept for CVE-2025-65094: privilege escalation via IDOR in WBCE CMS. Demonstrates group ID manipulation to gain admin access, with…
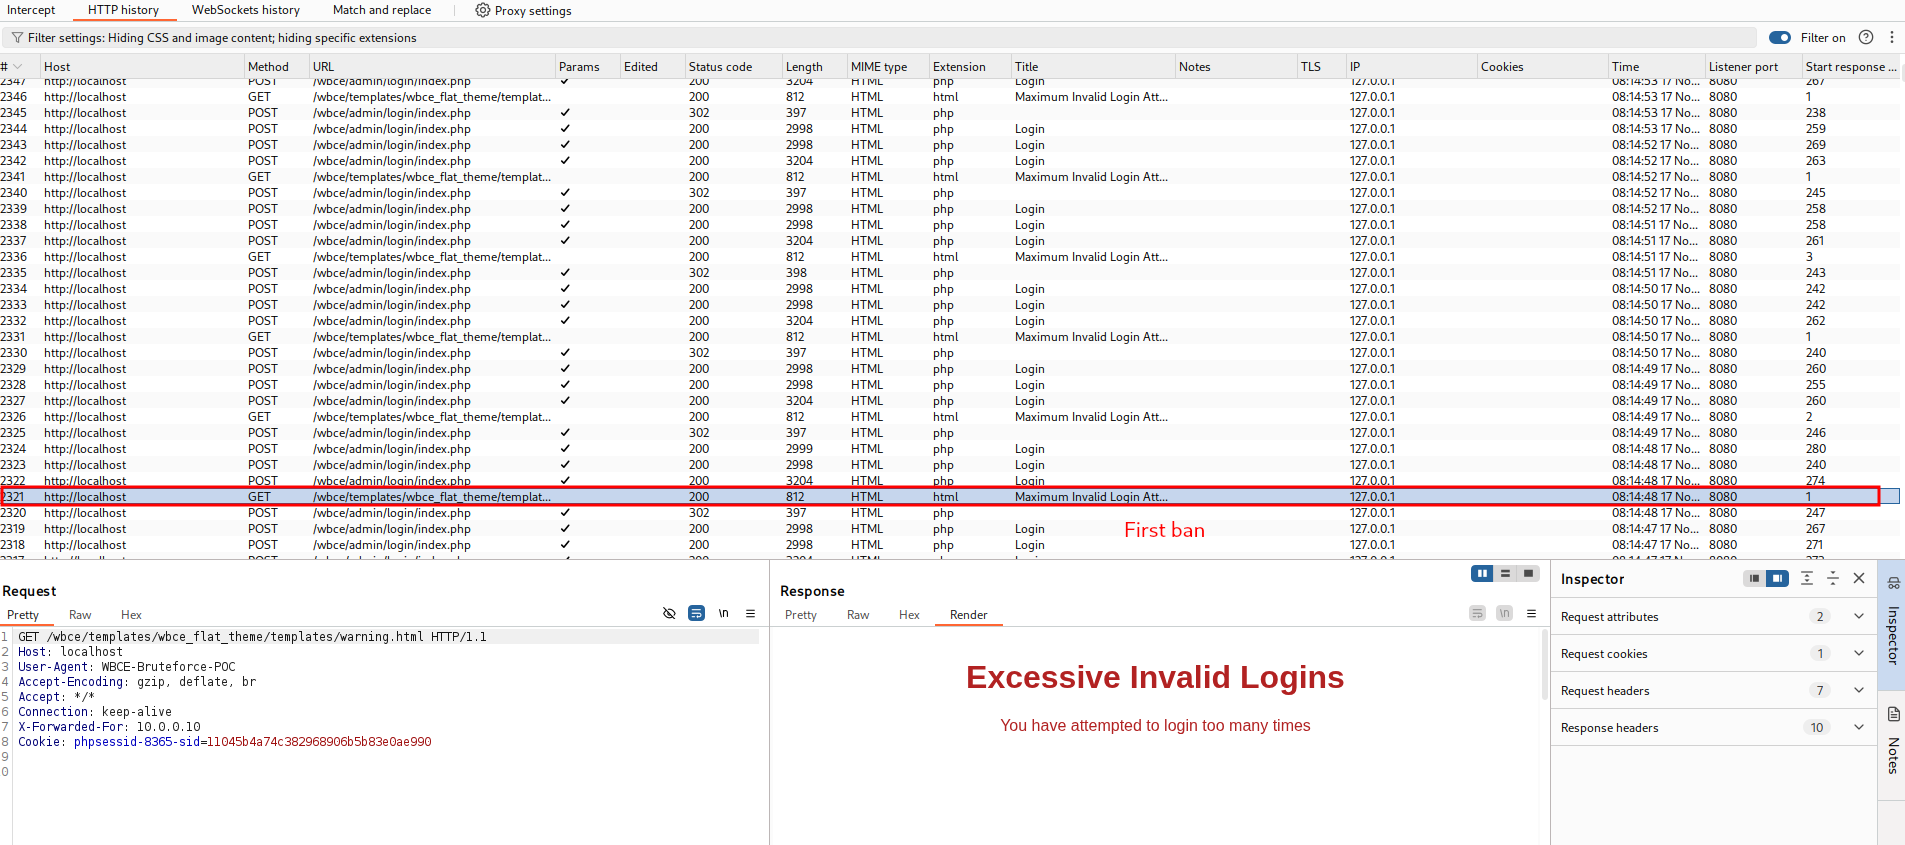 lukasz-rybak/cve-2025-66204
Proof-of-concept for CVE-2025-66204: brute-force protection bypass in WBCE CMS via spoofed X-Forwarded-For header, with automated Python exploit…
 lukasz-rybak/cve-2026-22692
CVE-2026-22692 - Critical Twig Sandbox Bypass via collect()->mapInto() allowing RCE/LFI/XXE in October CMS
 x-stp/cves-2025-11187_15467_69418
OpenSSL pocs: PKCS#12 stack overflow, CMS IV overflow, OCB infoleak [partial chain]
 helloandrewpaul/reflected-xss-in-vvveb-cms-v1.0.7.2
CVE-2025-9728: Reflected XSS in Login Form (Email & Password Fields) Vvveb CMS v1.0.7.2
 pescada-dev/cve-2025-61505
Insecure Deserialization in e107 CMS install.php
 prince325/cve-2026-93659-writeup
Stored XSS in Concrete CMS Community Store leads to admin dashboard takeover
 shijx1024/cve-2024-31666
Documents CVE-2024-31666, a remote code execution vulnerability in Flusity-CMS v2.33 via the edit_addon_post.php component, including impact and…
 snorlyd/https-nj.gov---cve-2019-11358
Vulnearability Report of the New Jersey official site