
CVE-2026-23980
 hyphentbg/cve-2026-23980
Modified proof-of-concept exploit for CVE-2026-23980, providing a working implementation for vulnerability reproduction and security testing.
exploitationpapers-researchpenetration-testing+2
hyphentbg/cve-2026-23980Modified proof-of-concept exploit for CVE-2026-23980, providing a working implementation for vulnerability reproduction and security testing.
 horizon3ai/cve-2026-106173
Python proof-of-concept exploit for CVE-2026-106173, an unauthenticated gRPC path traversal file write in Fortinet FortiSIEM that enables blind…
 zerodayevil/cve-2026-20805-poc
Proof-of-concept exploit code for CVE-2026-20805, demonstrating the vulnerability for security research and validation.
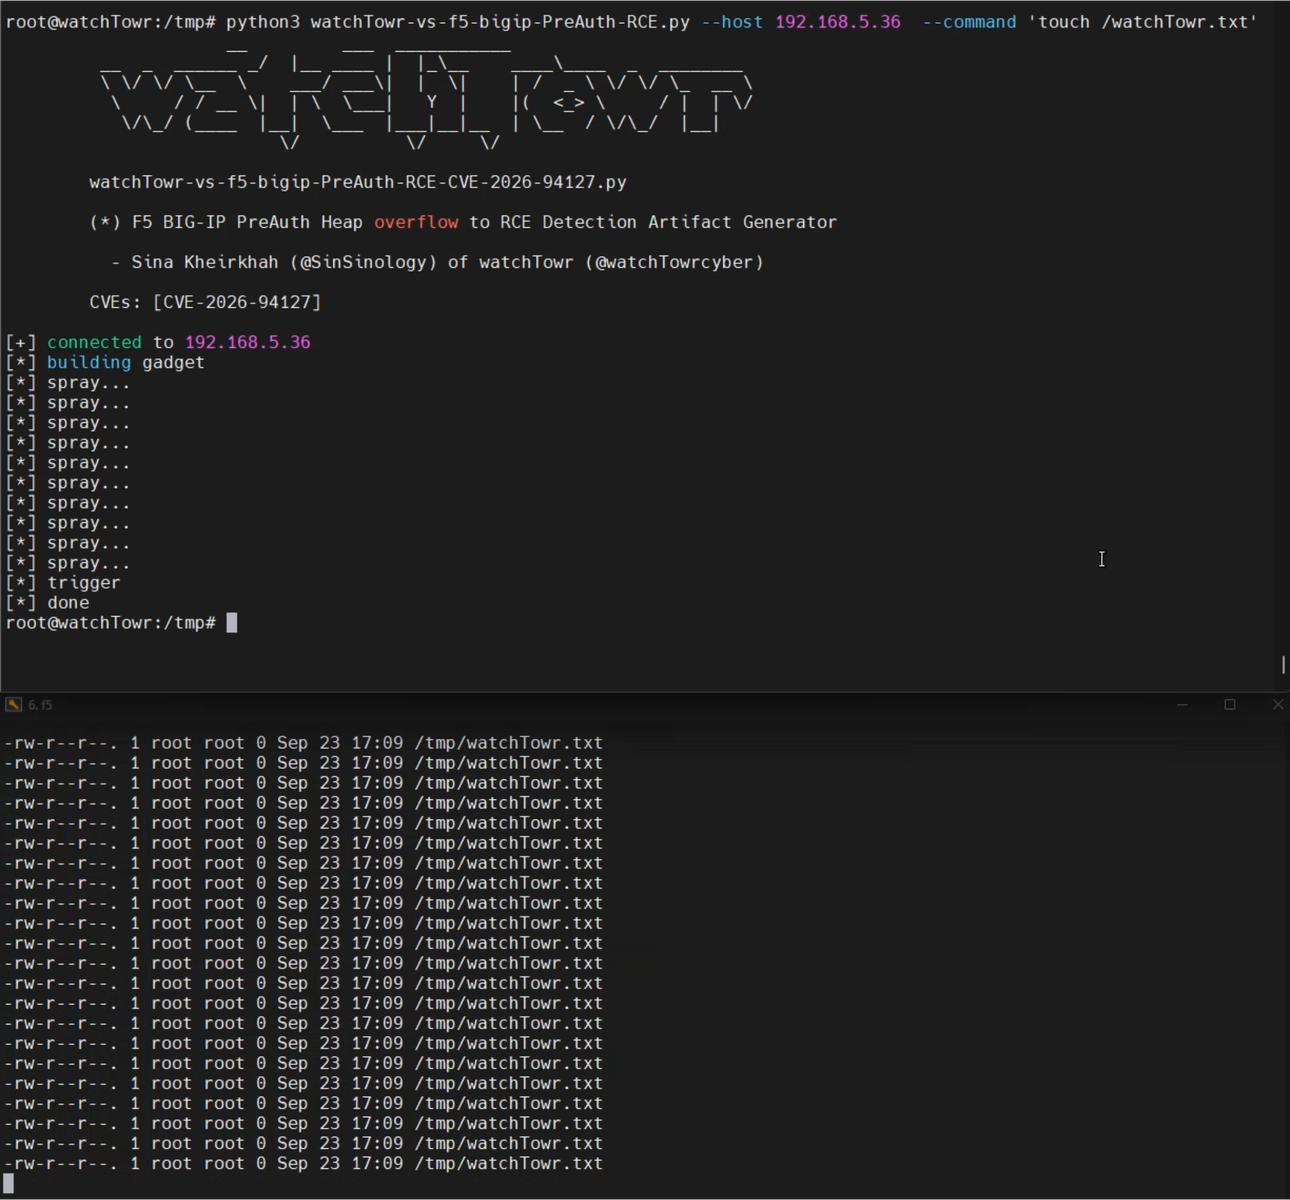 watchtowrlabs/watchtowr-vs-f5-bigip-preauth-rce-cve-2026-94127
Python detection artifact generator and PoC for CVE-2026-94127, a pre-auth RCE in F5 BIG-IP reachable via OAuth-configured virtual servers, with…
 zerodayevil/cve-2026-42978-poc-research
Proof-of-concept research repository for CVE-2026-42978, containing analysis and exploit code for the referenced vulnerability.
 abraxas/openmeetings-backup-config-path
Apache OpenMeetings 9.1.0 - High - Remote - File write leftover - ADMIN_BACKUP import skips Path.of on Type.PATH
 jonastrikex/cve-2026-14856-tastyigniter
Technical analysis and PoC for CVE-2026-14856, a stored XSS in TastyIgniter v4.3.0 Media Manager that chains with CSRF to achieve admin account…
 squeeze440/supernote-obsidian-plugin-poc
PoC — path traversal via malicious device sync in the Supernote Obsidian plugin (GHSA-3gx3-r874-5pp4, CVE-2026-86999, CVSS 5.6).
 mbadanoiu/mal-007
MAL-007: XML External Entity via Local Registry Entries in WSO2 ESB
 mbadanoiu/mal-003
MAL-003: Groovy Security Bypass and Stored XSS in Apache OfBiz
 mbadanoiu/mal-012
MAL-012: Reflected Cross-Site Scripting in Admin Console leading to Remote Code Execution in Payara Server
 h4ckm3-png/cve-2024-57610
Proof-of-concept demonstrating lack of rate limiting on the Sylius v2.0.2 login endpoint, enabling unrestricted automated authentication attempts.
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
 greydgl/pentestgpt
Automated Penetration Testing Agentic Framework Powered by Large Language Models
 husnainfareed/awesome-ethical-hacking-resources
😎 🔗 Awesome list about all kinds of resources for learning Ethical Hacking and Penetration Testing.
 mouteee/autonomous-offensive-llm-handbook
A deterministic harness and handbook for autonomous offensive LLM agents, enforcing authorization, scope, and evidence gates to ensure reproducible…
 stuxlabs/awe
adaptive agents for dynamic web penetration testing
 owasp/robotics-security-testing-guide
OWASP guide defining a standardized penetration testing methodology for humanoid, industrial, and autonomous robots, covering ROS/ROS2, DDS, CAN bus,…