axios-supply-chain-cve-2026-26555

Curated vulnerability writeup collection with full technical analysis, proof-of-concept scripts, IOC listings, and remediation guidance for…

Curated vulnerability writeup collection with full technical analysis, proof-of-concept scripts, IOC listings, and remediation guidance for…

Curated vulnerability research repository with in-depth writeups, PoC scripts, and IOC detection tools for real-world security incidents like…

CodeQL-based analysis of CVE-2025-55182 prototype pollution vulnerability in React Server Components, with exploit POC and static detection queries…

Detailed analysis of CVE-2024-28397, a sandbox escape vulnerability in js2py enabling RCE via Python object traversal. Includes code analysis, PoC,…


Exploits for CVE-2017-6008, a kernel pool buffer overflow leading to privilege escalation.

Proof of concept and technical write-up for CVE-2026-56096, a blind Solr query injection in TYPO3 EXT:solr enabling unauthenticated field enumeration…

Proof of Concept: CVE-2026-24061 is a critical authentication bypass vulnerability in GNU inetutils-telnetd allowing unauthenticated remote attackers…

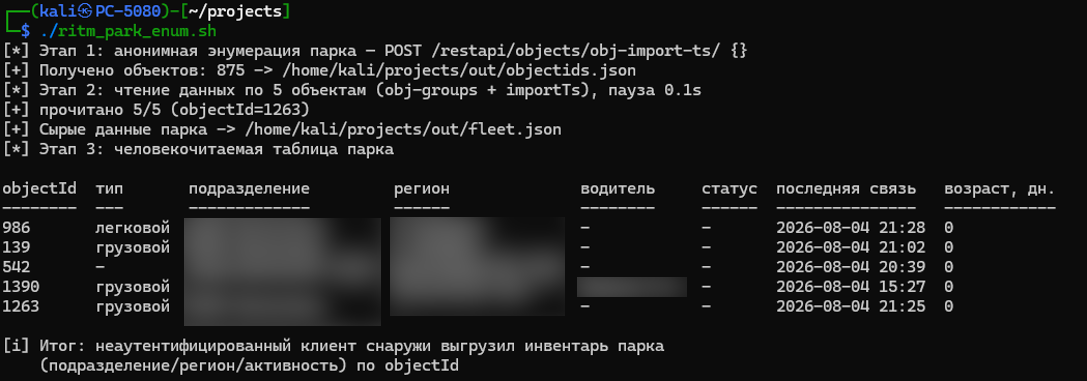
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.

Technical analysis and detection guidance for CVE-2026-21589, a pre-auth path traversal arbitrary file access flaw in Atlassian Data Center products.

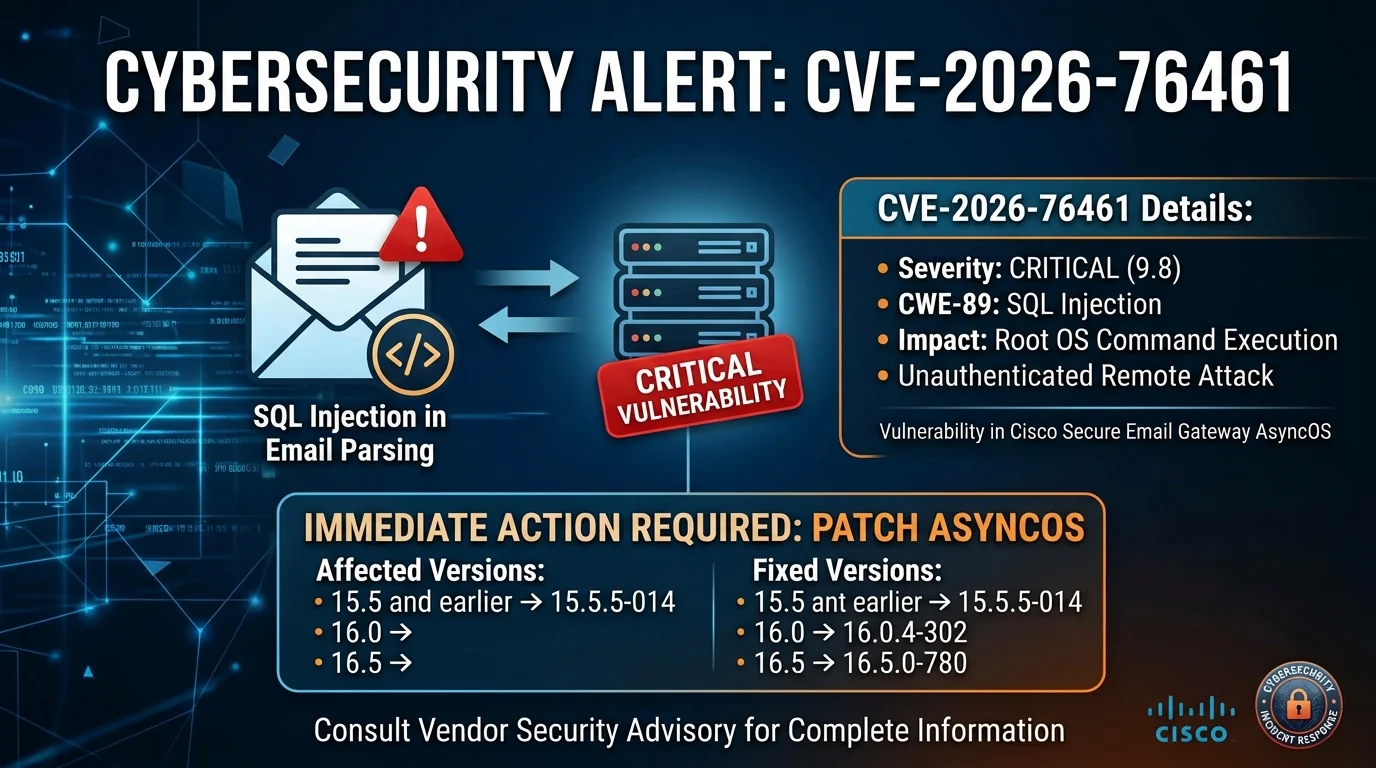
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…

Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…

Authenticated command injection PoC for D-Link R95/BE9500 DHMAPI SetTimeSettings, achieving root RCE via NTPServer backtick injection, with full…

PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…

Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…

Defensive vulnerability-research project comparing vulnerable and patched Grandstream GXP1600 firmware for CVE-2026-2329, using SquashFS extraction,…

PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.

Rule-based CLI tool that grades organizational defenses against MITRE ATT&CK and D3FEND frameworks, detects security gaps, and proposes mitigations.…