
CVE-2023-20938-Public
 0xatharv/cve-2023-20938-public
A bug trigger for CVE-2023-20938 for Android Binder.
android-securitybinary-exploitationeducation+3
3
0xatharv/cve-2023-20938-publicA bug trigger for CVE-2023-20938 for Android Binder.
 minanagehsalalma/zte-smartlife-app-pwned
ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
 dingo97/cve-2026-20516
Write-up and ADB proof of concept for CVE-2026-20516, a confused deputy flaw in MediaTek Android TV MiracastService allowing local Wi-Fi Direct state…
 sweatyrocket/huawei-p10-cve-2017-8890-unlock
Huawei P10 VTR-L29C432B151 CVE-2017-8890 exploit research and bootloader-unlock journey
 eddinos2/cve-2026-28956-jxl-messages-surface
iOS Messages JPEG XL delivery-surface probe and patch-diff notes for CVE-2026-28956.
 huaguiqi/asus-i005-cve-2026-43499
CVE-2026-43499 (GhostLock) adaptation for ASUS ROG Phone 5S — UAF trigger + pselect stack reclaim, KASLR leak blocked
 muhamadrifkii/cve-2026-43499-poco-x3-gt
Proof-of-concept exploit targeting CVE-2026-43499 on the POCO X3 GT Android device, demonstrating the vulnerability and its impact.
 m4g1xx/cve-2024-36971
Poc for CVE-2024-36971
 deaurity/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
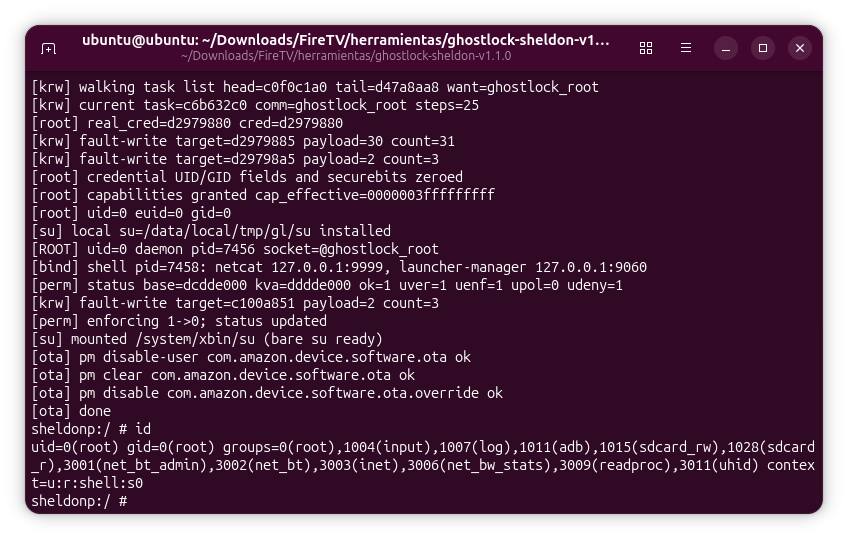 accessmodifier364/cve-2026-43499-firetv-sheldonp-writeup
Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.
 r3n3r0/cve-2026-27280
In-depth analysis and proof-of-concept for CVE-2026-27280, an out-of-bounds write in Adobe DNG SDK's dng_render_task::ProcessArea, reachable via…
 bobikl/cve-2026-43499-t807d
Android kernel exploit research package for CVE-2026-43499, containing popsicle exploit source, embedded su payload, root bridge helper, and…
 whatishope/bido
Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
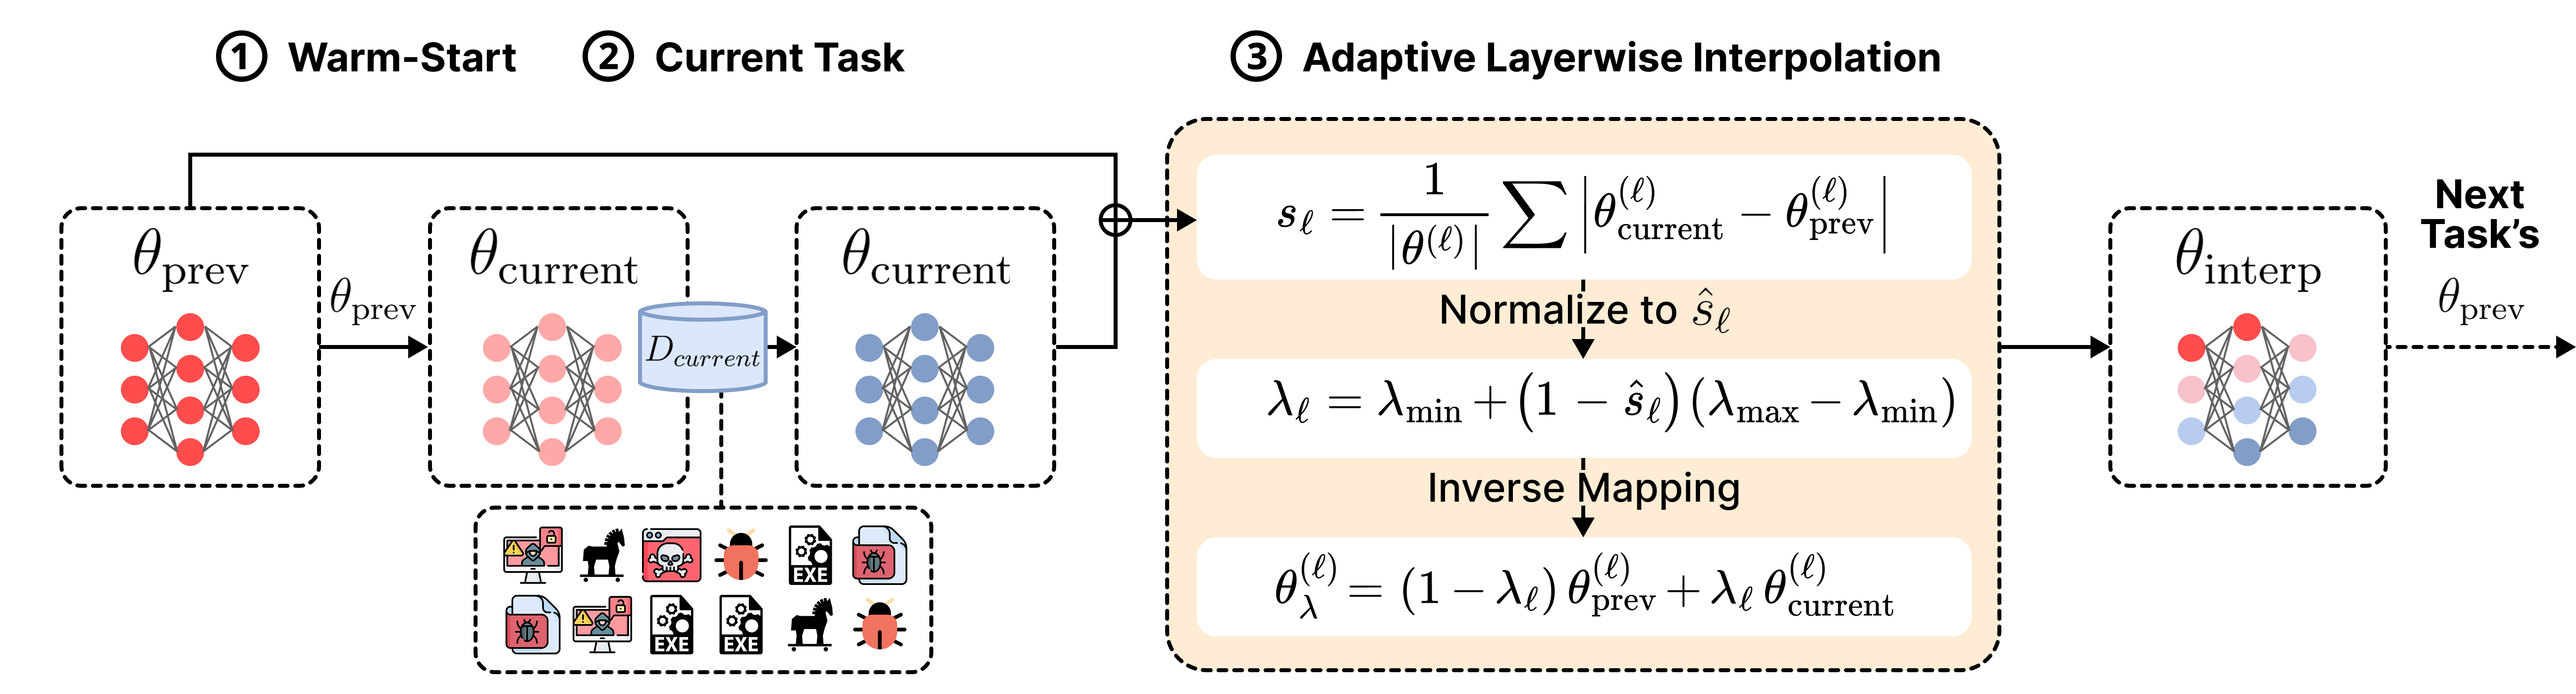 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 rmdycz/k80pro-miro-cve-2026-64560
Device-bound CVE-2026-64560 adaptation for RedMi K80pro miro OS 3.0.304.0
 kpatsakis/poc_cve-2017-0807
Proof of concept of CVE-2017-0807
 r3n3r0/cve-2026-0049
PoC and analysis of a zero-click DoS in Android's DNG SDK, with crafted DNG samples, an NDK crash harness, and UBSan/IntSan reproduction of the…
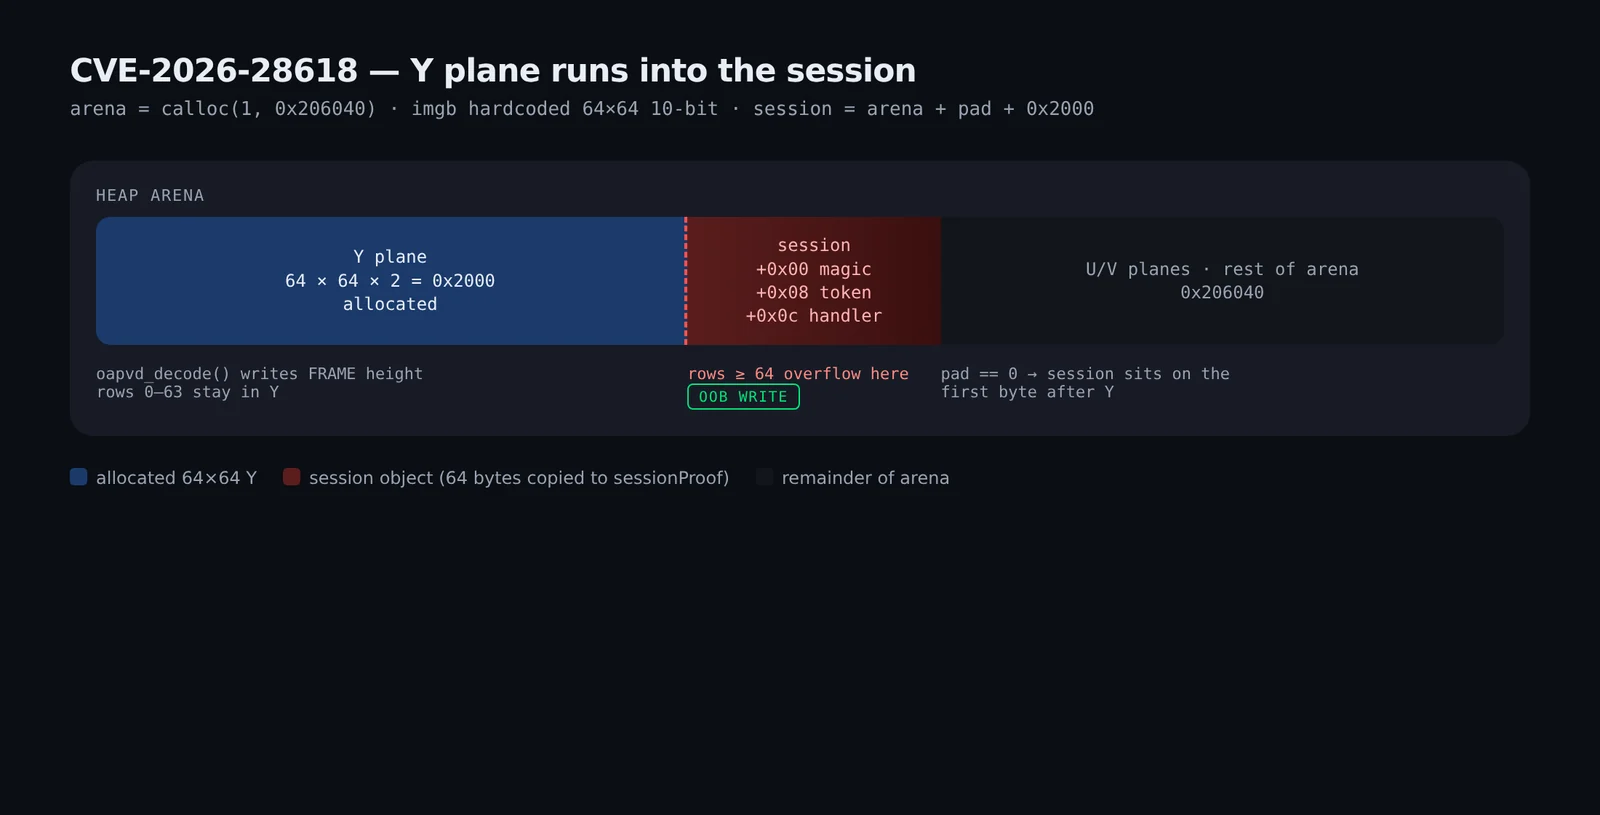 raafatabualazm/streambox-cve-2026-28618
Redacted notes on CVE-2026-28618 / StreamBox APV lab — heap write into a session object via FRAME height mismatch