
PentestGPT
 greydgl/pentestgpt
Automated Penetration Testing Agentic Framework Powered by Large Language Models
ai-securityctfeducation+6
15.5k2 months ago
greydgl/pentestgptAutomated Penetration Testing Agentic Framework Powered by Large Language Models
 pedrib/poc
Advisories, proof of concept files and exploits that have been made public by @pedrib.
 jbaines-r7/cisco_asa_research
Cisco ASA Software and ASDM Security Research
 agentsid-dev/agentsid-scanner
Security scanner for MCP servers. Grades auth, permissions, injection risks, and tool safety. The Lighthouse of agent security.
 stuxlabs/awe
adaptive agents for dynamic web penetration testing
 askhatov21/best-practices-cybersecurity-otanata-project
CVE-2024-3273 — Authorized Penetration Test Report D-Link DNS-320L NAS | Client: Otonata
 wmohamed2033/wmohamed2033.github.io
CVE-2021-44228 Log4Shell — Penetration Test Writeup
 mbadanoiu/mal-003
MAL-003: Groovy Security Bypass and Stored XSS in Apache OfBiz
 zerodayevil/cve-2026-42978-poc-research
Proof-of-concept research repository for CVE-2026-42978, containing analysis and exploit code for the referenced vulnerability.
 zerodayevil/cve-2026-20805-poc
Proof-of-concept exploit code for CVE-2026-20805, demonstrating the vulnerability for security research and validation.
 hyphentbg/cve-2026-23980
Modified proof-of-concept exploit for CVE-2026-23980, providing a working implementation for vulnerability reproduction and security testing.
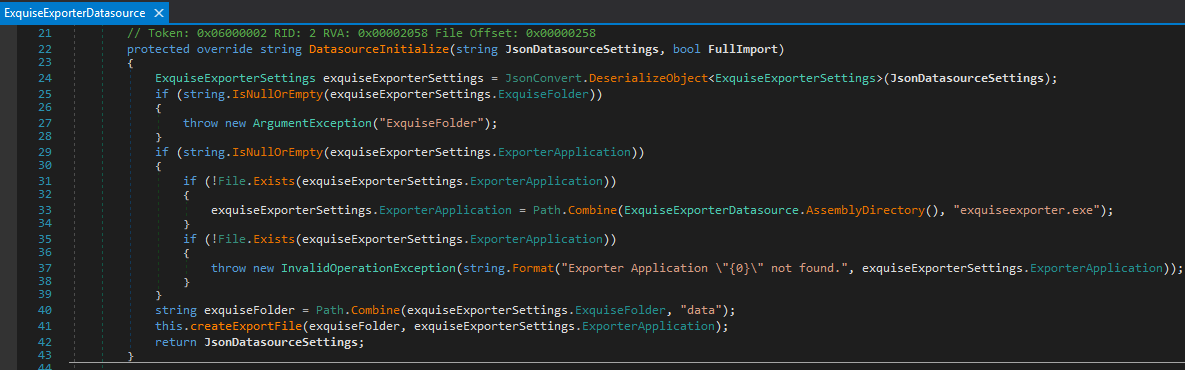 kpn-ciso/cve-2019-9745
Write-up on the CVE-2019-9745 vulnerability.
 mbadanoiu/mal-007
MAL-007: XML External Entity via Local Registry Entries in WSO2 ESB
 mbadanoiu/mal-012
MAL-012: Reflected Cross-Site Scripting in Admin Console leading to Remote Code Execution in Payara Server
 squeeze440/supernote-obsidian-plugin-poc
PoC — path traversal via malicious device sync in the Supernote Obsidian plugin (GHSA-3gx3-r874-5pp4, CVE-2026-86999, CVSS 5.6).