CVE-2026-48908-joomla-sp-page-builder-detection

Validates CVE-2026-48908 in Joomla SP Page Builder with unauthorized icon upload leading to PHP code execution. Includes auditd/PCAP evidence, event…

Validates CVE-2026-48908 in Joomla SP Page Builder with unauthorized icon upload leading to PHP code execution. Includes auditd/PCAP evidence, event…

Proof-of-concept reproducers for Apache Camel camel-google-storage path traversal (CVE-2026-66907), demonstrating arbitrary file write via…

Proof-of-concept for CVE-2026-63039, demonstrating ORDER BY SQL injection in Apache InLong's AuditAlertRule via orderField/orderType, with a…

Proof-of-concept for CVE-2026-75898, an SSRF in RAGFlow's Invoke component. Demonstrates the vulnerability with unmodified source, includes E2E…

Proof-of-concept reproducers for Apache Camel path traversal vulnerability (CVE-2026-66906) in camel-azure-storage-blob, demonstrating arbitrary file…

Minimal Intel VT-x hypervisor for Windows and UEFI that virtualizes a live host for introspection, supporting dynamic hyperjacking, unhyperjacking,…

Benchmark and evaluation harness testing whether LLM agents resist malicious instructions hidden in multimodal skill images, with 108 cases across…

Fix-Like Artifacts With Embedded Defects

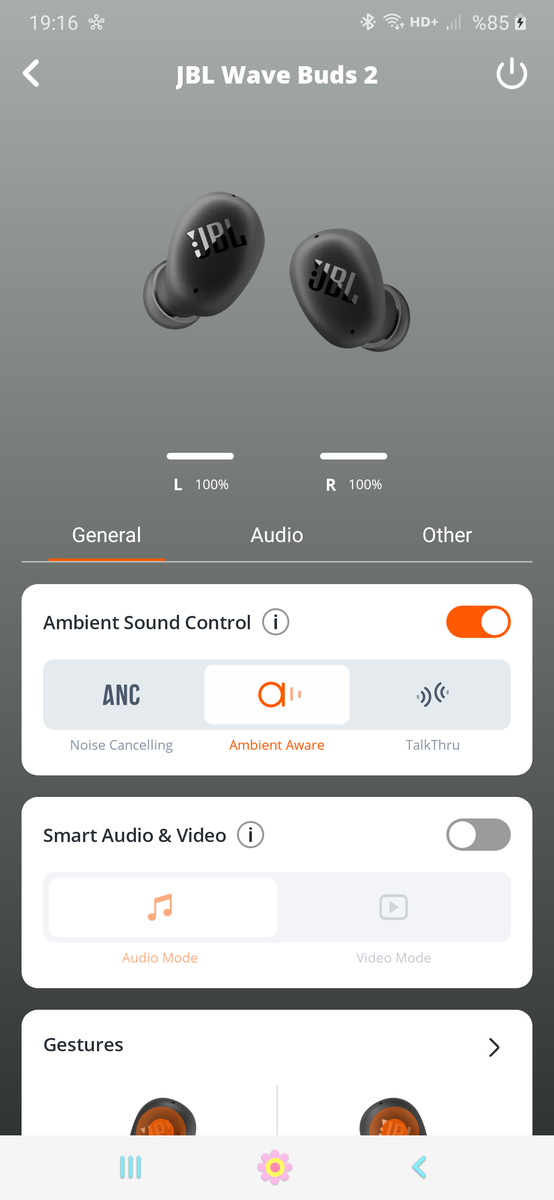
Reverse-engineering notes and Python tooling for JBL Wave Buds 2 (BES1306) firmware: OTA container format, flash layout, BLE/GATT protocol, and…

Heap-based Buffer Overflow vulnerability in Apache HTTP Server with mod_xml2enc, xml2StartParse, and untrusted content

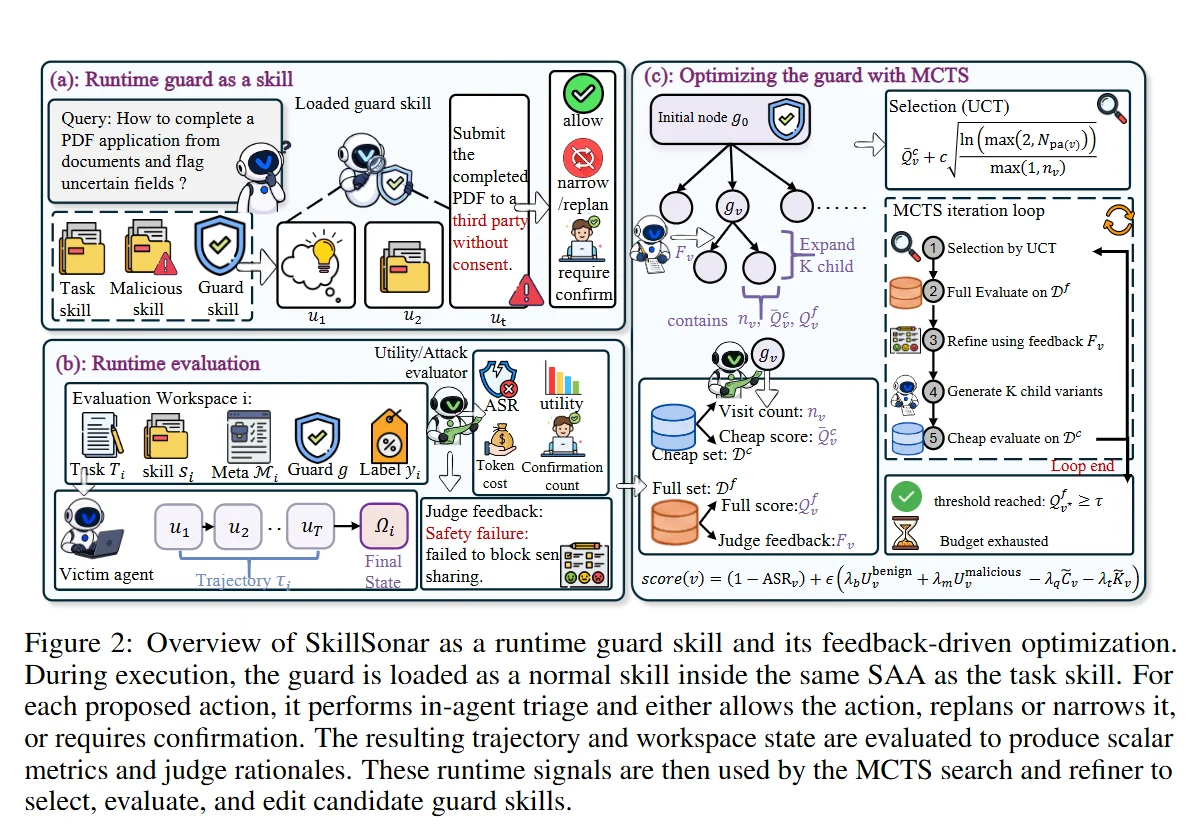
Runtime guard skill that detects and blocks malicious skill-induced attacks in skill-augmented agents, with an MCTS loop that evolves the guard…

Evidence and data for the Sorami technical report on security defaults of 15 AI serving, vector database and MCP Helm charts on Kubernetes.

Docker-based lab reproducing CVE-2026-29057 Next.js request smuggling, comparing vulnerable 15.5.12 against patched 15.5.13 with a raw chunked HTTP…

Sanitized report and loopback-only PoC for CVE-2026-102971, a MediaWiki REST revision response leaking hidden revision author user IDs.

HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis

Reproduces CVE-2026-7482 heap out-of-bounds read in Ollama GGUF loading and quantization, with differential analysis of quantized artifacts to…

Verified vulnerability journey for CVE-2025-8110 (Gogs) and CVE-2025-3248 (Langflow) — risk triage, exploitability verification, verified patches.