
amlsec
 sbaresearch/amlsec
Automated Security Risk Identification Using AutomationML-based Engineering Data
papers-researchscada-ics-securityvulnerability-analysis
sbaresearch/amlsecAutomated Security Risk Identification Using AutomationML-based Engineering Data
 pr0me/xtride
N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…
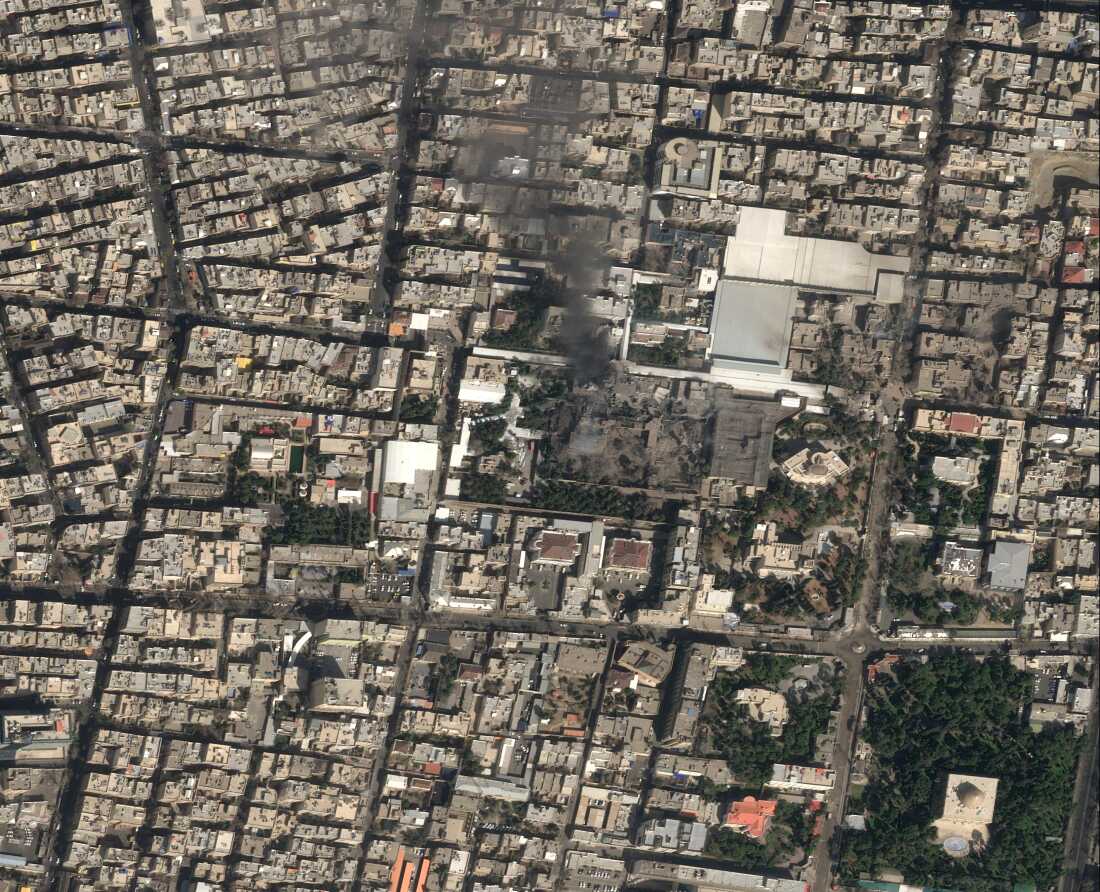 albintouma/iran-war-media
Iran War Media Monitor collects news articles covering the US-Israeli war on Iran and applies sentiment analysis to uncover who supports and opposes…
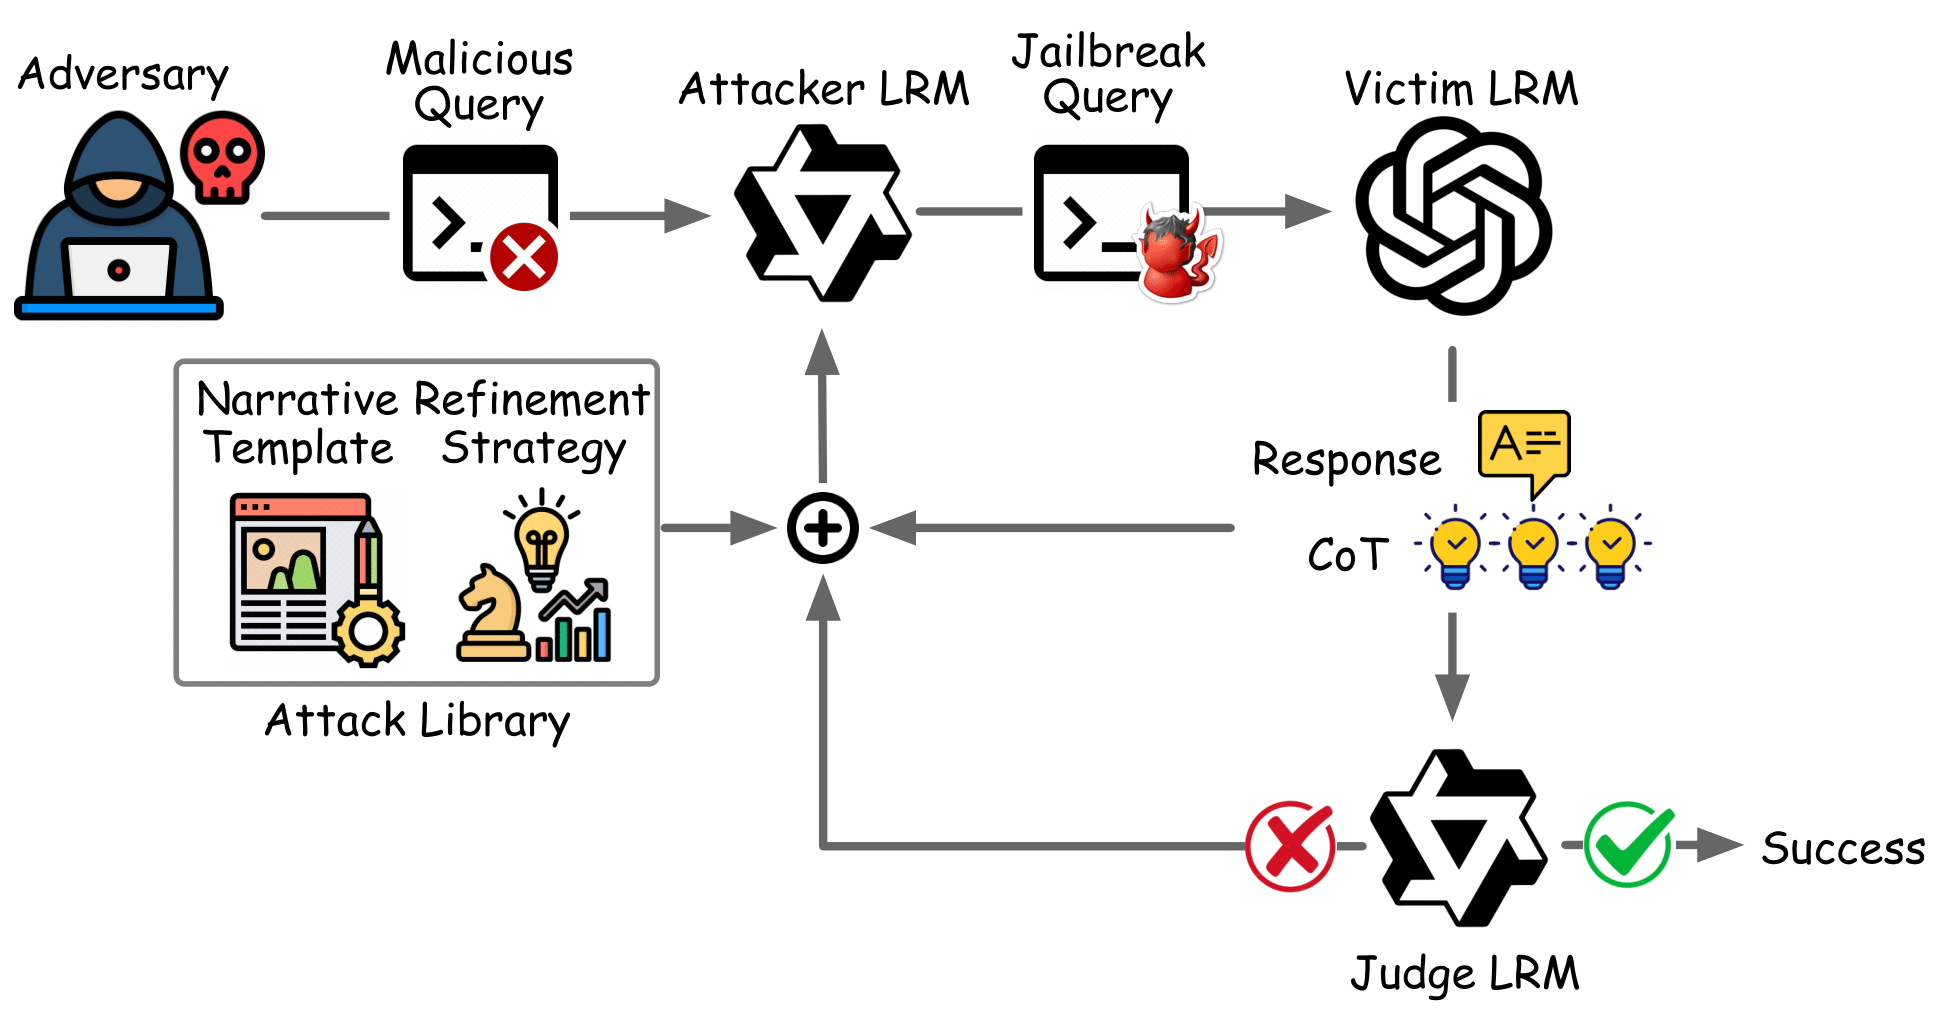 jackpurcell/autoran-public
Automated framework for hijacking safety reasoning in large reasoning models via simulated reasoning traces and iterative prompt refinement to…
 owasp/osib
Centralized YAML-based knowledge base linking MITRE CWE, OWASP Top10, ASVS, and other security standards with versioned references. Includes MkDocs…
 horkimhab/awesome-cybersecurity-resources
Curated collection of cybersecurity resources including tools, articles, and repositories, structured with YAML frontmatter and automated discovery…
 owasp/sbom-vex-taint-analysis
Automated SBOM-to-VEX pipeline using a secure multi-agent AI system to analyze CVEs, reason about exploitability, and generate signed CycloneDX VEX…
 9xeb/context-segmentation
Multi-agent automated context management for long horizon tasks in local AI Agents
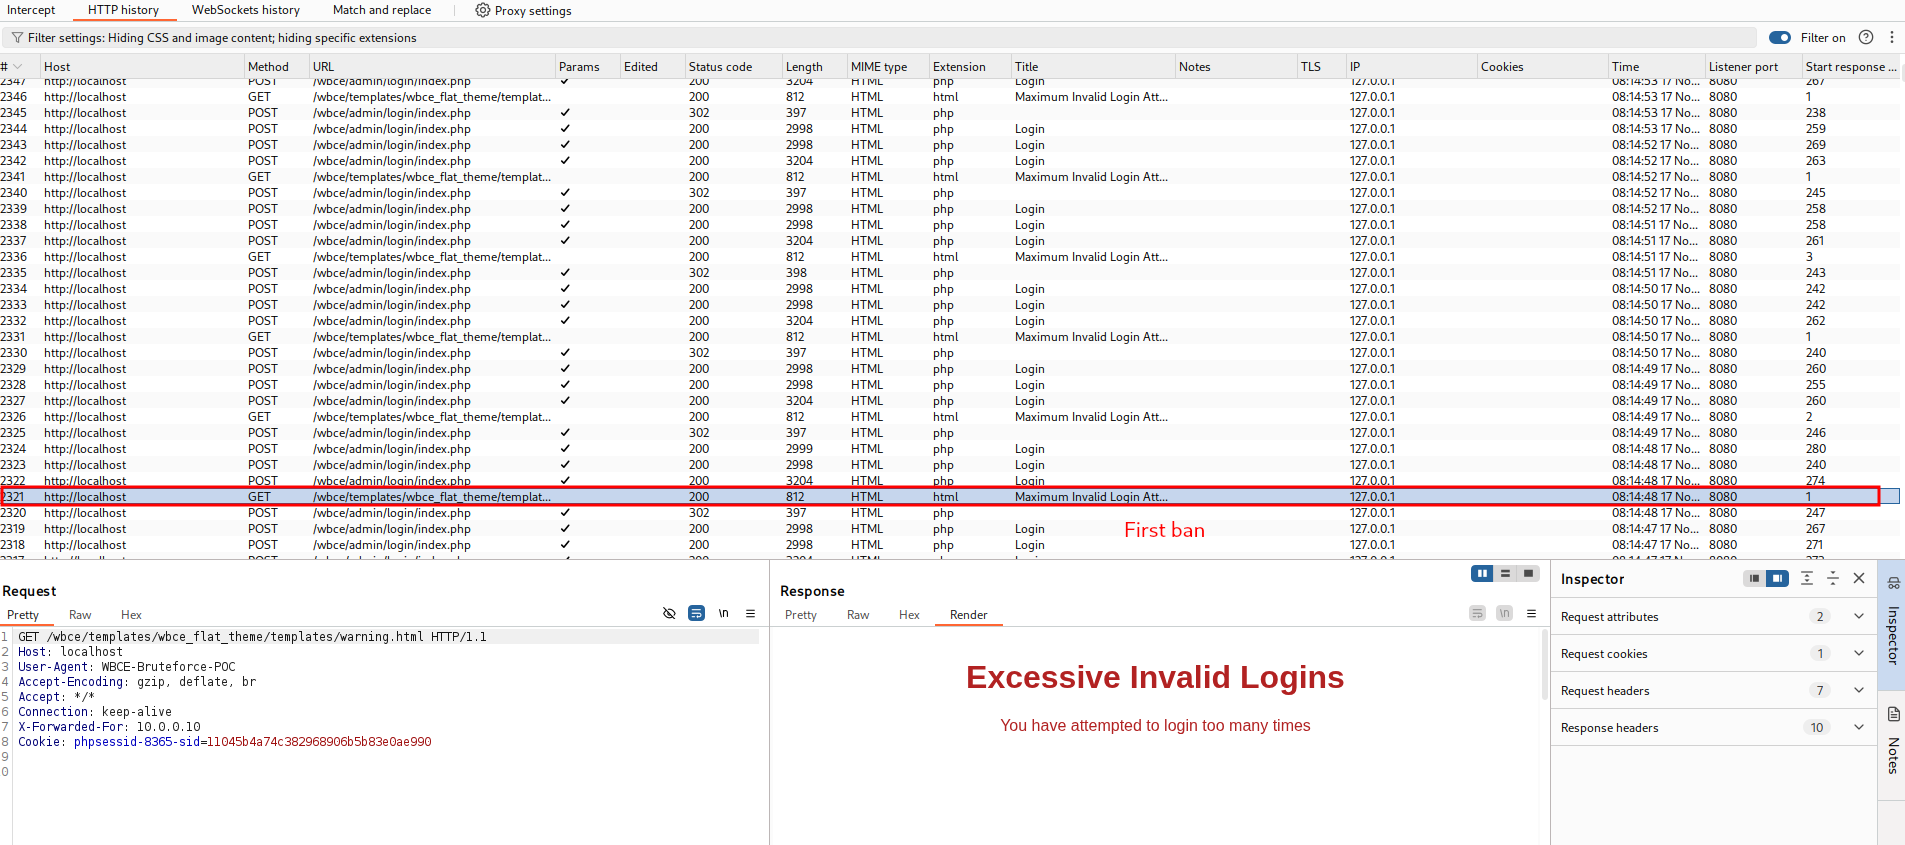 lukasz-rybak/cve-2025-66204
Proof-of-concept for CVE-2025-66204: brute-force protection bypass in WBCE CMS via spoofed X-Forwarded-For header, with automated Python exploit…
 h4ckm3-png/cve-2024-57610
Proof-of-concept demonstrating lack of rate limiting on the Sylius v2.0.2 login endpoint, enabling unrestricted automated authentication attempts.
 x86rc/unthemidator
An automated Themida / Code Virtualizer / WinLicense (v3.0-v4) unpacker and dump fixer tool
 ua-spectral/botlens
Research artifact and MCP server that audits security and privacy concerns in third-party Discord bots via large-scale review analysis, LLM labeling,…
 logpai/logparser
A machine learning toolkit for log parsing [ICSE'19, DSN'16]
 longwasu/cve-2025-38352-poc
PoC and GDB script assists in triggering CVE-2025-38352
 pvharmo2/gha-lab-6ab39df295
Controlled security-research lab reproducing CVE-2024-45798 (GHSA-h52q-xhg2-6jw8) in espressif/arduino-esp32 — poisoned-artifact pwn request via…
 pvharmo2/gha-lab-fb32aba4a3
Authorized lab reproduction of CVE-2023-26493 (GHSL-2023-027): command injection via github.head_ref in cocos-engine's <Web> Interface check…
 pvharmo2/gha-lab-ca4fa82ac5
Security-research lab: reproduction of CVE-2026-29075 (GHSA-3j55-5q6x-2h48) in mesa/mesa benchmarks.yml pull_request_target workflow — single-commit…
 pvharmo2/gha-lab-733c168b88
Reproduces CVE-2026-44246, a prompt injection vulnerability in nnU-Net's GitHub Actions triage agent, demonstrating how issue content is inlined into…